Netfilter internal packet flow
Dear list,
thanks to googling and RTFMing and some very instructive graphics, I think I have understood the netfilter packet flow in principle.
But all material I have found only seems to describe the journey of packets which really come from the "outside" or go to the "outside". I would be strongly interested in some documentation describing what happens to packets that are internally generated and absorbed.
For example, even with one NIC and one IP address, there are packets going from the IP address to loopback and vice versa, so the packets are generated locally and received locally.
According to my testing so far (linux kernel 2.6.26 / debian lenny), the behaviour of these packets seems to contradict the documents and graphics I have seen. Such packets seem to go through the INPUT and OUTPUT chains of the FILTER table and through one or two chains of the NAT table (I just can't remember exactly at the moment), but not through the PREROUTING chain of the NAT table. This is confusing ...
I would be grateful if somebody could give a comprehensive explanation of that or a hint regarding further documentation.
By the way, the graphics I have mentioned are:
http://jengelh.medozas.de/images/nf-packet-flow.png
http://dmiessler.com/images/DM_NF.PNG
http://linux-ip.net/nf/nfk-traversal.png
http://ebtables.sourceforge.net/br_fw_ia/PacketFlow.png
http://xkr47.outerspace.dyndns.org/netfilter/packet_flow/packet_flow10.png
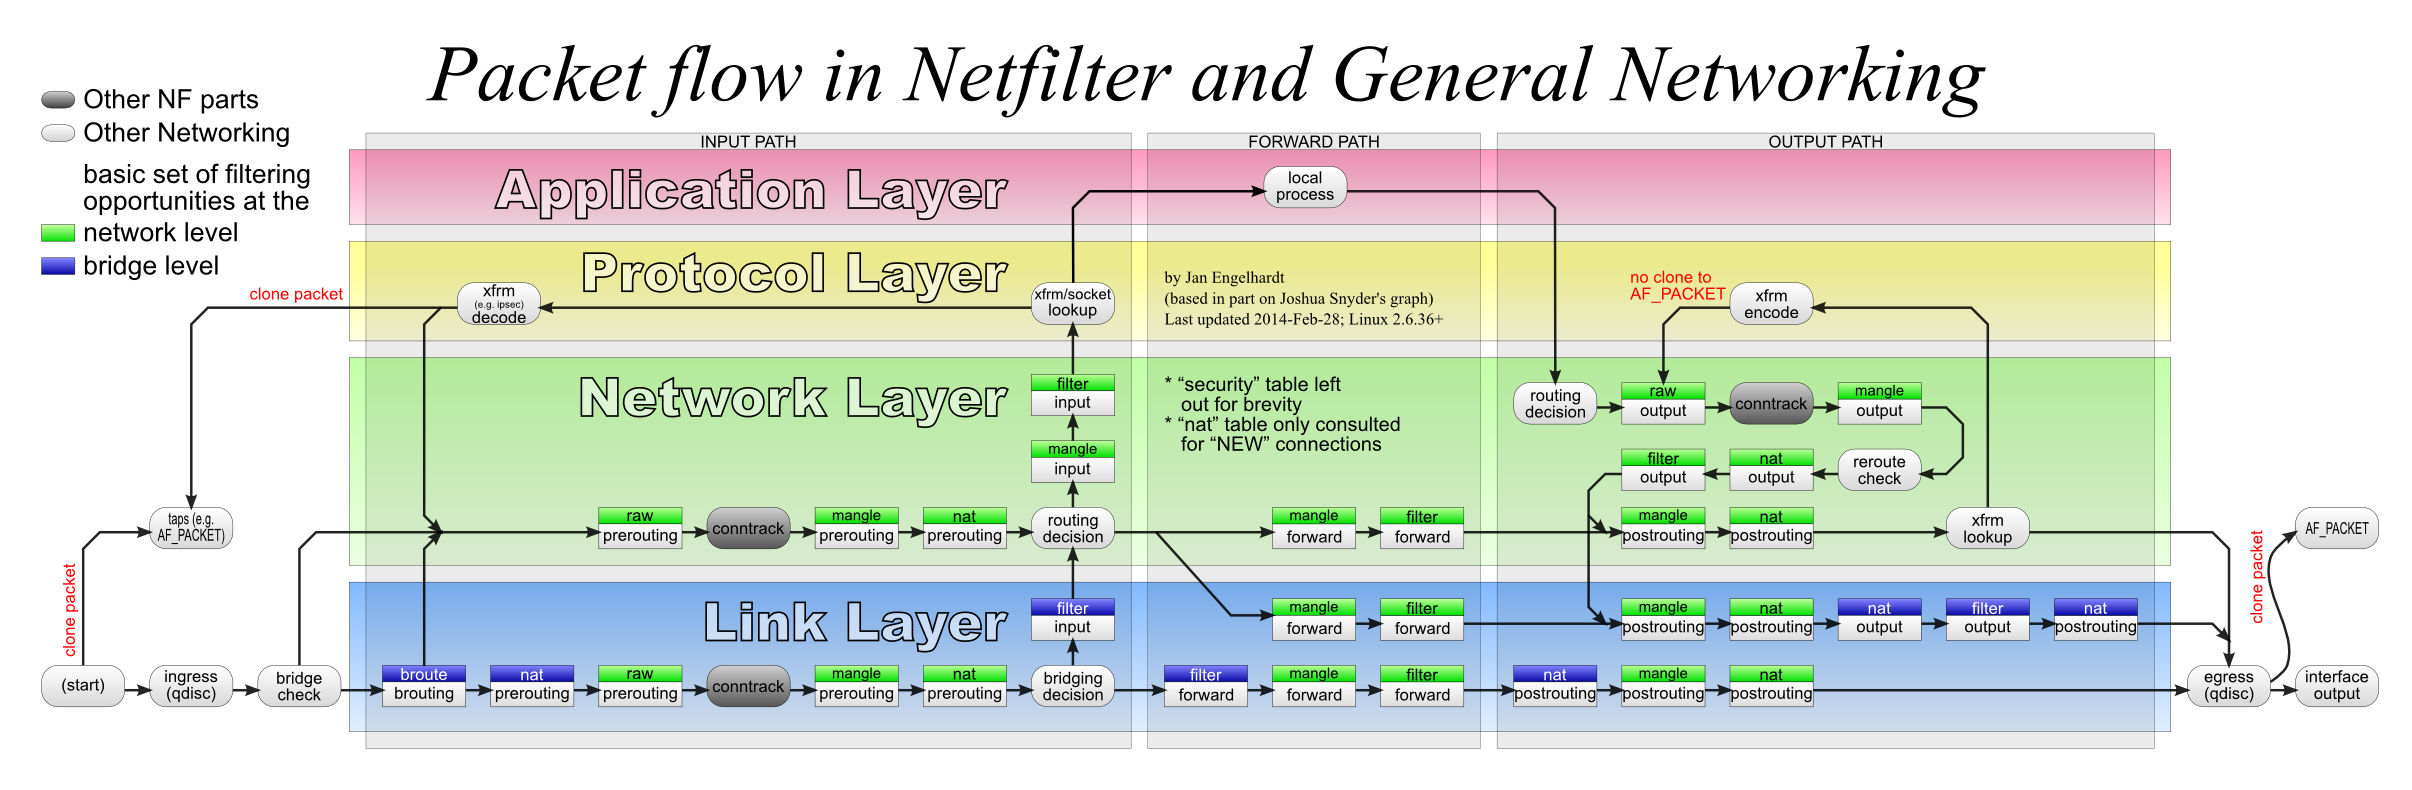

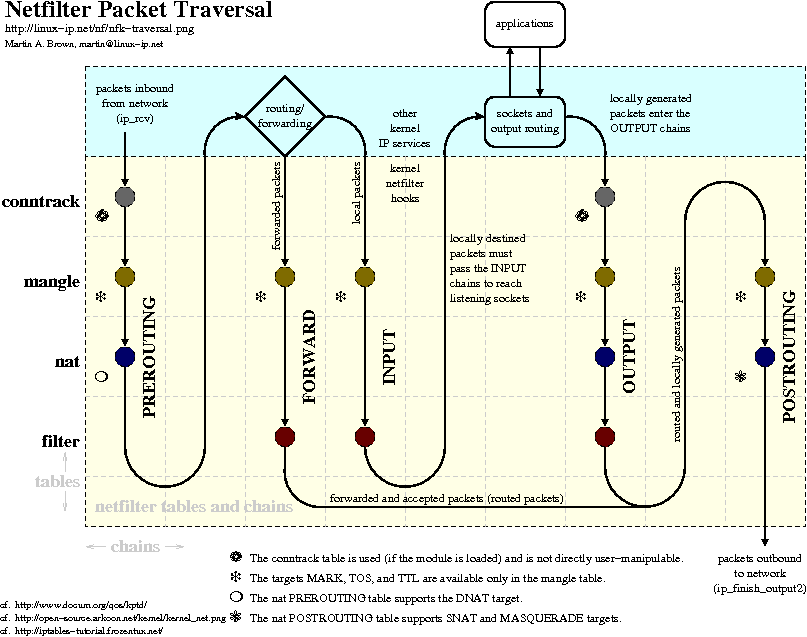

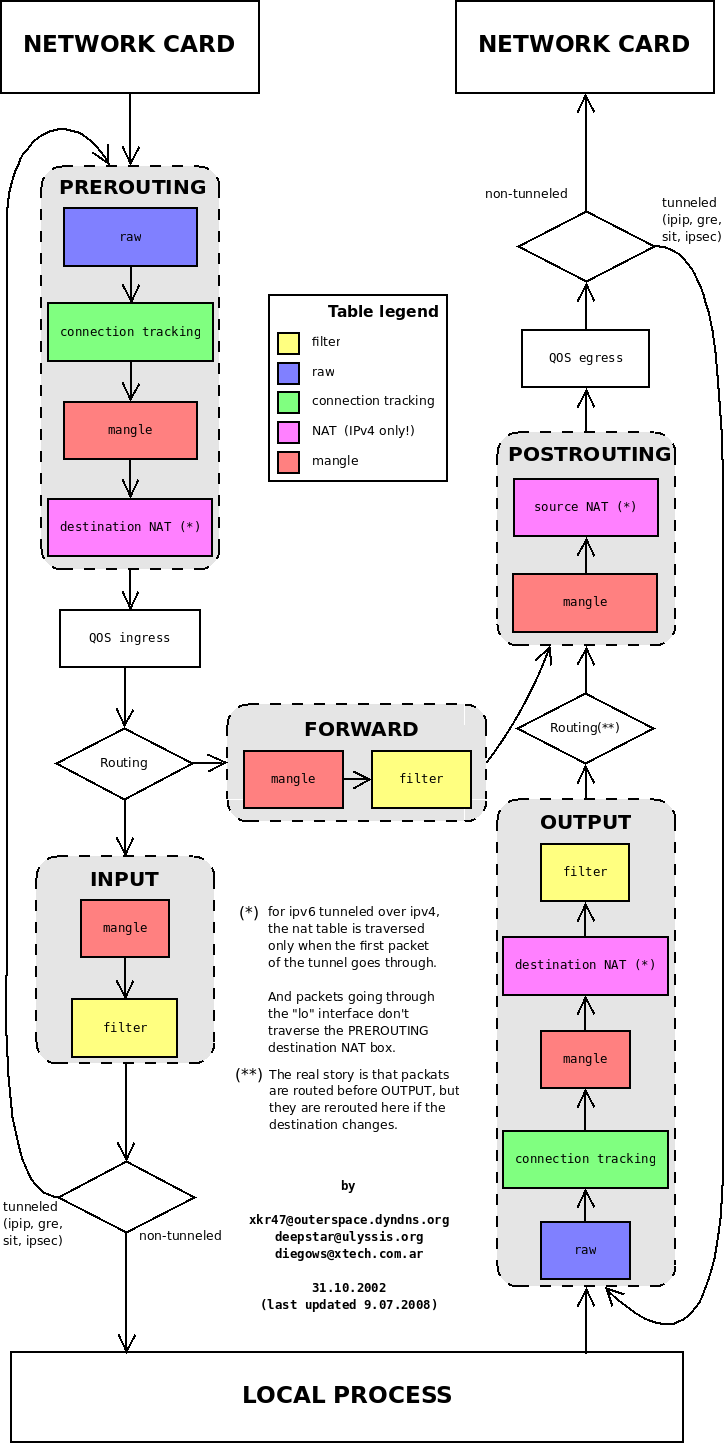
Perhaps it would be sufficient for understanding if somebody, refering to the first of these graphics, could just explain which part of the graph "purely internal" packets have to travel through.
Thank you very much,
Peter
Signature · 2 lines
GMX.at - Österreichs FreeMail-Dienst mit über 2 Mio Mitgliedern
E-Mail, SMS & mehr! Kostenlos: http://portal.gmx.net/de/go/atfreemail
Hello,
Quoted 7 lines · [email protected] a écrit :
According to my testing so far (linux kernel 2.6.26 / debian lenny), the behaviour of these packets seems to contradict the documents and graphics I have seen. Such packets seem to go through the INPUT and OUTPUT chains of the FILTER table and through one or two chains of the NAT table (I just can't remember exactly at the moment), but not through the PREROUTING chain of the NAT table. This is confusing ...
In most graphics a part is missing after the POSTROUTING and INPUT chains : the "conntrack confirm", which confirms the creation of a new conntrack entry for a NEW packet only when the packet reaches that step. So if the packet is dropped before, the new conntrack entry is not confirmed. IIUC, a packet can go through the nat *chains* (not to be confused with the nat *table*) only when its conntrack entry is not confirmed yet. That's why only the first packet of a new connection enters the nat chains.
When a packet is looped back, it reaches the conntrack confirm after POSTROUTING, so it skips the nat PREROUTING chain. Anyway that makes sense : if the destination could be changed in PREROUTING, the packet may need to be re-routed through another interface but I don't think there is a routing decision after PREROUTING for the loopback (routing decision already took place on output). If you need DNAT on loopback, you can do it in OUTPUT.
-------- Original-Nachricht --------
Quoted 12 lines
Datum: Thu, 25 Mar 2010 11:14:18 +0100
Von: Pascal Hambourg <[email protected]>
An: [email protected]
Betreff: Re: Netfilter internal packet flowQuoted 6 lines
According to my testing so far (linux kernel 2.6.26 / debian lenny), the behaviour of these packets seems to contradict the documents and graphics I have seen. Such packets seem to go through the INPUT and OUTPUT chains of the FILTER table and through one or two chains of the NAT table (I just can't remember exactly at the moment), but not through the PREROUTING chain of the NAT table. This is confusing ...
[...]
Quoted 7 lines
When a packet is looped back, it reaches the conntrack confirm after POSTROUTING, so it skips the nat PREROUTING chain. Anyway that makes sense : if the destination could be changed in PREROUTING, the packet may need to be re-routed through another interface but I don't think there is a routing decision after PREROUTING for the loopback (routing decision already took place on output). If you need DNAT on loopback, you can do it in OUTPUT.
Pascal,
thank you very much for your valuable time and the comprehensive explanation. I think I have got it now. Nevertheless, it would be nice to have some sort of graphics comprising really all of the packet flow for future reference and for showing to others.
I have seen many kinds of such pictures, from obviously wrong to (what I would consider) high quality. But none of these pictures seems to originate from the netfilter / iptables developers, and I am still not sure if the graphics I have mentioned in my original post are correct in every aspect.
So does anyone know about "official" graphics or an "official" complete explanation of the packet flow in netfilter? Or a good book? The reference material which is mentioned on the netfilter homepage doesn't help me; it seems to be mostly outdated and incomplete.
Thank you very much,
Peter
Signature · 2 lines
GRATIS für alle GMX-Mitglieder: Die maxdome Movie-FLAT!
Jetzt freischalten unter http://portal.gmx.net/de/go/maxdome01