3.2.34-stable review
Subsystems (50)
cover 3.2.34-stable review
This is the start of the stable review cycle for the 3.2.34 release. There are 82 patches in this series, which will be posted as responses to this one. If anyone has any issues with these being applied, please let me know.
Responses should be made by Fri Nov 16 12:00:00 UTC 2012. Anything received after that time might be too late.
A combined patch relative to 3.2.33 will be posted as an additional response to this. A shortlog and diffstat can be found below.
Ben.
-------------
Alex Deucher (1):
drm/radeon: fix typo in evergreen_mc_resume()
[695ddeb457584a602f2ba117d08ce37cf6ec1589]
Alexander Stein (1):
ALSA: hda: Cirrus: Fix coefficient index for beep configuration
[5a83b4b5a391f07141b157ac9daa51c409e71ab5]
Antonio Quartulli (1):
mac80211: fix SSID copy on IBSS JOIN
[badecb001a310408d3473b1fc2ed5aefd0bc92a9]
Ben Hutchings (1):
      nfs: Show original device name verbatim in /proc/*/mount{s,info}
         [97a54868262da1629a3e65121e65b8e8c4419d9f]
Ben Skeggs (3):
      drm/nouveau: fix suspend/resume when in headless mode
         [9430738d80223a1cd791a2baa74fa170d3df1262]
      drm/nouveau: headless mode by default if pci class != vga display
         [e412e95a268fa8544858ebfe066826b290430d51]
      drm/nouveau: silence modesetting spam on pre-gf8 chipsets
         [cee59f15a60cc6269a25e3f6fbf1a577d6ab8115]
Bo Shen (1):
ARM: at91/i2c: change id to let i2c-gpio work
[7840487cd6298f9f931103b558290d8d98d41c49]
Bryan Schumaker (1):
NFS: Wait for session recovery to finish before returning
[399f11c3d872bd748e1575574de265a6304c7c43]
Cyril Brulebois (1):
      r8169: Fix WoL on RTL8168d/8111d.
         [b00e69dee4ccbb3a19989e3d4f1385bc2e3406cd]
Dan Carpenter (1):
gpio-timberdale: fix a potential wrapping issue
[d79550a7bc35c16476ebdc27c78378d8093390ec]
Daniel J Blueman (1):
      ALSA: HDA: Fix digital microphone on CS420x
         [16337e028a6dae9fbdd718c0d42161540a668ff3]
Daniel Vetter (3):
      drm/i915: clear the entire sdvo infoframe buffer
         [b6e0e543f75729f207b9c72b0162ae61170635b2]
      drm/i915: fix overlay on i830M
         [a9193983f4f292a82a00c72971c17ec0ee8c6c15]
      drm/i915: fixup infoframe support for sdvo
         [81014b9d0b55fb0b48f26cd2a943359750d532db]
Dave Chinner (1):
xfs: fix reading of wrapped log data
[6ce377afd1755eae5c93410ca9a1121dfead7b87]
David Vrabel (1):
xen/gntdev: don't leak memory from IOCTL_GNTDEV_MAP_GRANT_REF
[a67baeb77375199bbd842fa308cb565164dd1f19]
Egbert Eich (1):
DRM/Radeon: Fix Load Detection on legacy primary DAC.
[83325d072185899b706de2956170b246585aaec9]
Eric Dumazet (3):
netlink: use kfree_rcu() in netlink_release()
[6d772ac5578f711d1ce7b03535d1c95bffb21dff]
rtnetlink: fix rtnl_calcit() and rtnl_dump_ifinfo()
[a4b64fbe482c7766f7925f03067fc637716bfa3f]
tcp: fix FIONREAD/SIOCINQ
[a3374c42aa5f7237e87ff3b0622018636b0c847e]
Eric Leblond (1):
af-packet: fix oops when socket is not present
[a3d744e995d2b936c500585ae39d99ee251c89b4]
Eric Paris (1):
fanotify: fix missing break
[848561d368751a1c0f679b9f045a02944506a801]
Felix Fietkau (2):
ath9k: fix stale pointers potentially causing access to free'd skbs
[8c6e30936a7893a85f6222084f0f26aceb81137a]
cfg80211: fix antenna gain handling
[c4a9fafc77a5318f5ed26c509bbcddf03e18c201]
Greg Rose (1):
rtnetlink: Fix problem with buffer allocation
[115c9b81928360d769a76c632bae62d15206a94a]
Hannes Frederic Sowa (1):
ipv6: send unsolicited neighbour advertisements to all-nodes
[60713a0ca7fd6651b951cc1b4dbd528d1fc0281b]
Hemant Kumar (1):
net: usb: Fix memory leak on Tx data path
[39707c2a3ba5011038b363f84d37c8a98d2d9db1]
Herton Ronaldo Krzesinski (2):
floppy: do put_disk on current dr if blk_init_queue fails
[238ab78469c6ab7845b43d5061cd3c92331b2452]
floppy: properly handle failure on add_disk loop
[d60e7ec18c3fb2cbf90969ccd42889eb2d03aef9]
Ilija Hadzic (1):
drm: restore open_count if drm_setup fails
[0f1cb1bd94a9c967cd4ad3de51cfdabe61eb5dcc]
Ivan Shugov (1):
ARM: at91: at91sam9g10: fix SOC type detection
[3d9a0183dd3423353e9e363bcc261c1220d05f9f]
J. Bruce Fields (1):
nfsd: add get_uint for u32's
[a007c4c3e943ecc054a806c259d95420a188754b]
Javier Cardona (2):
mac80211: Only process mesh config header on frames that RA_MATCH
[555cb715be8ef98b8ec362b23dfc254d432a35b1]
mac80211: don't inspect Sequence Control field on control frames
[f7fbf70ee9db6da6033ae50d100e017ac1f26555]
Jean Delvare (1):
hwmon: (w83627ehf) Force initial bank selection
[3300fb4f88688029fff8dfb9ec0734f6e4cba3e7]
Jeff Layton (1):
cifs: fix potential buffer overrun in cifs.idmap handling code
[36960e440ccf94349c09fb944930d3bfe4bc473f]
Jesper Dangaard Brouer (1):
net: fix divide by zero in tcp algorithm illinois
[8f363b77ee4fbf7c3bbcf5ec2c5ca482d396d664]
Jiri Slaby (1):
HID: microsoft: fix invalid rdesc for 3k kbd
[3ccc60f9d8c39180c205dba1a020735bda1b2491]
Johan Hovold (1):
USB: mos7840: remove unused variable
[a tiny part of 80c00750f0c9867a65b30a17880939b6bc660a77]
Johannes Berg (4):
mac80211: check management frame header length
[4a4f1a5808c8bb0b72a4f6e5904c53fb8c9cd966]
mac80211: make sure data is accessible in EAPOL check
[6dbda2d00d466225f9db1dc695ff852443f28832]
mac80211: verify that skb data is present
[9b395bc3be1cebf0144a127c7e67d56dbdac0930]
wireless: drop invalid mesh address extension frames
[7dd111e8ee10cc6816669eabcad3334447673236]
Jussi Kivilinna (1):
crypto: cryptd - disable softirqs in cryptd_queue_worker to prevent data corruption
[9efade1b3e981f5064f9db9ca971b4dc7557ae42]
Kailang Yang (1):
ALSA: hda - Add new codec ALC668 and ALC900 (default name ALC1150)
[19a62823eae453619604636082085812c14ee391]
Konrad Rzeszutek Wilk (1):
xen/mmu: Use Xen specific TLB flush instead of the generic one.
[95a7d76897c1e7243d4137037c66d15cbf2cce76]
Len Brown (1):
x86: Remove the ancient and deprecated disable_hlt() and enable_hlt() facility
[f6365201d8a21fb347260f89d6e9b3e718d63c70]
Li RongQing (1):
ipv6: Set default hoplimit as zero.
[14edd87dc67311556f1254a8f29cf4dd6cb5b7d1]
Mathias Nyman (1):
gpiolib: Don't return -EPROBE_DEFER to sysfs, or for invalid gpios
[ad2fab36d7922401c4576fb7ea9b21a47a29a17f]
Michal Schmidt (1):
r8169: use unlimited DMA burst for TX
[aee77e4accbeb2c86b1d294cd84fec4a12dde3bd]
Mirko Lindner (1):
sky2: Fix for interrupt handler
[d663d181b9e92d80c2455e460e932d34e7a2a7ae]
Nathan Walp (1):
r8169: allow multicast packets on sub-8168f chipset.
[0481776b7a70f09acf7d9d97c288c3a8403fbfe4]
NeilBrown (1):
NFS: fix bug in legacy DNS resolver.
[8d96b10639fb402357b75b055b1e82a65ff95050]
Roland Dreier (3):
iscsi-target: Fix missed wakeup race in TX thread
[d5627acba9ae584cf4928af19f7ddf5f6837de32]
target: Avoid integer overflow in se_dev_align_max_sectors()
[3e03989b5868acf69a391a424dc71fcd6cc48167]
target: Don't return success from module_init() if setup fails
[0d0f9dfb31e0a6c92063e235417b42df185b3275]
Rolf Eike Beer (1):
Input: tsc40 - remove wrong announcement of pressure support
[32ed1911fc79908d704023317d4ddeb3883fd07e]
Rusty Russell (1):
module: fix out-by-one error in kallsyms
[59ef28b1f14899b10d6b2682c7057ca00a9a3f47]
Scott Mayhew (1):
nfsv3: Make v3 mounts fail with ETIMEDOUTs instead EIO on mountd timeouts
[acce94e68a0f346115fd41cdc298197d2d5a59ad]
Stanislaw Gruszka (1):
rt2800: validate step value for temperature compensation
[bf7e1abe434ba9e22e8dc04a4cba4ab504b788b8]
Sven Eckelmann (1):
ath9k: Test for TID only in BlockAcks while checking tx status
[6fe7cc71bbf3a0bc28c9cec3c00bc11e81344412]
Takamori Yamaguchi (1):
      mm: bugfix: set current->reclaim_state to NULL while returning from kswapd()
         [b0a8cc58e6b9aaae3045752059e5e6260c0b94bc]
Takashi Iwai (10):
ALSA: Add a reference counter to card instance
[a0830dbd4e42b38aefdf3fb61ba5019a1a99ea85]
ALSA: Avoid endless sleep after disconnect
[0914f7961babbf28aaa2f19b453951fb4841c03f]
ALSA: Fix card refcount unbalance
[8bb4d9ce08b0a92ca174e41d92c180328f86173f]
ALSA: PCM: Fix some races at disconnection
[9b0573c07f278e9888c352aa9724035c75784ea0]
ALSA: hda - Fix empty DAC filling in patch_via.c
[5b3761954dac2d1393beef8210eb8cee81d16b8d]
ALSA: hda - Fix invalid connections in VT1802 codec
[ef4da45828603df57e5e21b8aa21a66ce309f79b]
ALSA: hda - Force to reset IEC958 status bits for AD codecs
[ae24c3191ba2ab03ec6b4be323e730e00404b4b6]
ALSA: usb-audio: Fix races at disconnection
[978520b75f0a1ce82b17e1e8186417250de6d545]
ALSA: usb-audio: Fix races at disconnection in mixer_quirks.c
[888ea7d5ac6815ba16b3b3a20f665a92c7af6724]
ALSA: usb-audio: Use rwsem for disconnect protection
[34f3c89fda4fba9fe689db22253ca8db2f5e6386]
Thomas Hellstrom (2):
drm/vmwgfx: Fix a case where the code would BUG when trying to pin GMR memory
[afcc87aa6a233e52df73552dc1dc9ae3881b7cc8]
drm/vmwgfx: Fix hibernation device reset
[95e8f6a21996c4cc2c4574b231c6e858b749dce3]
Tim Sally (1):
eCryptfs: check for eCryptfs cipher support at mount
[5f5b331d5c21228a6519dcb793fc1629646c51a6]
Tom Parkin (1):
l2tp: fix oops in l2tp_eth_create() error path
[789336360e0a2aeb9750c16ab704a02cbe035e9e]
Trond Myklebust (2):
NFSv4.1: We must release the sequence id when we fail to get a session slot
[2240a9e2d013d8269ea425b73e1d7a54c7bc141f]
NFSv4: nfs4_locku_done must release the sequence id
[2b1bc308f492589f7d49012ed24561534ea2be8c]
Tyler Hicks (1):
eCryptfs: Copy up POSIX ACL and read-only flags from lower mount
[069ddcda37b2cf5bb4b6031a944c0e9359213262]
Ulisses Furquim (1):
Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
[f1e91e1640d808d332498a6b09b2bcd01462eff9]
Zijie Pan (1):
sctp: fix call to SCTP_CMD_PROCESS_SACK in sctp_cmd_interpreter()
[f6e80abeab928b7c47cc1fbf53df13b4398a2bec]
 Documentation/feature-removal-schedule.txt      |    8 ---
 Makefile                                        |    4 +-
 arch/arm/mach-at91/at91rm9200_devices.c         |    2 +-
 arch/arm/mach-at91/at91sam9260_devices.c        |    2 +-
 arch/arm/mach-at91/at91sam9261_devices.c        |    2 +-
 arch/arm/mach-at91/at91sam9263_devices.c        |    2 +-
 arch/arm/mach-at91/at91sam9rl_devices.c         |    2 +-
 arch/arm/mach-at91/setup.c                      |    2 +-
 arch/x86/include/asm/system.h                   |    7 --
 arch/x86/kernel/process.c                       |   24 -------
 arch/x86/xen/mmu.c                              |   21 +++++-
 crypto/cryptd.c                                 |   11 +++-
 drivers/block/floppy.c                          |   48 ++++----------
 drivers/gpio/gpio-timberdale.c                  |    4 +-
 drivers/gpio/gpiolib.c                          |   10 ++-
 drivers/gpu/drm/drm_fops.c                      |    5 +-
 drivers/gpu/drm/i915/intel_drv.h                |    4 +-
 drivers/gpu/drm/i915/intel_overlay.c            |   14 +++-
 drivers/gpu/drm/i915/intel_sdvo.c               |   59 ++++++++++++-----
 drivers/gpu/drm/i915/intel_sdvo_regs.h          |    2 +
 drivers/gpu/drm/nouveau/nouveau_drv.c           |   34 ++++++----
 drivers/gpu/drm/nouveau/nouveau_state.c         |    4 +-
 drivers/gpu/drm/nouveau/nv04_dac.c              |    8 +--
 drivers/gpu/drm/nouveau/nv04_dfp.c              |    6 +-
 drivers/gpu/drm/nouveau/nv04_tv.c               |    4 +-
 drivers/gpu/drm/radeon/evergreen.c              |    2 +-
 drivers/gpu/drm/radeon/radeon_legacy_encoders.c |    1 +
 drivers/gpu/drm/vmwgfx/vmwgfx_dmabuf.c          |    2 +-
 drivers/gpu/drm/vmwgfx/vmwgfx_drv.c             |    5 ++
 drivers/hid/hid-microsoft.c                     |   18 ++++--
 drivers/hwmon/w83627ehf.c                       |    1 +
 drivers/input/touchscreen/tsc40.c               |    1 -
 drivers/net/ethernet/marvell/sky2.c             |    4 +-
 drivers/net/ethernet/realtek/r8169.c            |    7 +-
 drivers/net/usb/usbnet.c                        |    3 +
 drivers/net/wireless/ath/ath9k/xmit.c           |   10 ++-
 drivers/net/wireless/rt2x00/rt2800lib.c         |    2 +-
 drivers/target/iscsi/iscsi_target.c             |    4 +-
 drivers/target/iscsi/iscsi_target_core.h        |    1 +
 drivers/target/iscsi/iscsi_target_login.c       |    1 +
 drivers/target/iscsi/iscsi_target_util.c        |   22 ++++++-
 drivers/target/iscsi/iscsi_target_util.h        |    1 +
 drivers/target/target_core_configfs.c           |    3 +-
 drivers/target/target_core_device.c             |   18 +++---
 drivers/usb/serial/mos7840.c                    |    1 -
 drivers/xen/gntdev.c                            |   36 ++++++-----
 fs/cifs/cifsacl.c                               |   49 ++++++--------
 fs/ecryptfs/main.c                              |   23 ++++++-
 fs/nfs/dns_resolve.c                            |    5 +-
 fs/nfs/internal.h                               |    5 +-
 fs/nfs/mount_clnt.c                             |    2 +-
 fs/nfs/namespace.c                              |   19 ++++--
 fs/nfs/nfs4namespace.c                          |    3 +-
 fs/nfs/nfs4proc.c                               |   40 +++++++-----
 fs/nfs/super.c                                  |    2 +-
 fs/nfsd/export.c                                |    6 +-
 fs/notify/fanotify/fanotify.c                   |    1 +
 fs/xfs/xfs_log_recover.c                        |    2 +-
 include/linux/if_link.h                         |    1 +
 include/linux/rtnetlink.h                       |    3 +
 include/linux/sunrpc/cache.h                    |   16 +++++
 include/net/bluetooth/bluetooth.h               |   22 -------
 include/net/cfg80211.h                          |    9 +++
 include/net/rtnetlink.h                         |    2 +-
 include/sound/core.h                            |    3 +
 include/trace/events/xen.h                      |    8 +++
 kernel/module.c                                 |   24 +++----
 mm/vmscan.c                                     |    2 +
 net/bluetooth/Kconfig                           |   37 +++--------
 net/bluetooth/Makefile                          |    5 +-
 net/bluetooth/bnep/Kconfig                      |    2 +-
 net/bluetooth/cmtp/Kconfig                      |    2 +-
 net/bluetooth/hidp/Kconfig                      |    2 +-
 net/bluetooth/rfcomm/Kconfig                    |    2 +-
 net/core/dev.c                                  |    2 +-
 net/core/rtnetlink.c                            |   78 +++++++++++++++++------
 net/ipv4/tcp.c                                  |    8 +--
 net/ipv4/tcp_illinois.c                         |    8 ++-
 net/ipv6/ndisc.c                                |    3 +-
 net/ipv6/route.c                                |    4 +-
 net/l2tp/l2tp_eth.c                             |    1 +
 net/mac80211/ibss.c                             |    2 +-
 net/mac80211/rx.c                               |   71 ++++++++++++++++-----
 net/netlink/af_netlink.c                        |   19 ++++--
 net/sctp/sm_sideeffect.c                        |    3 +-
 net/wireless/core.c                             |    3 +-
 net/wireless/util.c                             |   14 ++--
 sound/core/control.c                            |    5 ++
 sound/core/hwdep.c                              |   12 +++-
 sound/core/init.c                               |   50 +++++++++------
 sound/core/oss/mixer_oss.c                      |   11 +++-
 sound/core/oss/pcm_oss.c                        |    7 ++
 sound/core/pcm.c                                |   13 +++-
 sound/core/pcm_native.c                         |   35 ++++++++--
 sound/core/rawmidi.c                            |   26 +++++++-
 sound/core/sound.c                              |   11 +++-
 sound/core/sound_oss.c                          |   10 ++-
 sound/pci/hda/patch_analog.c                    |    1 +
 sound/pci/hda/patch_cirrus.c                    |   16 +++--
 sound/pci/hda/patch_realtek.c                   |    2 +
 sound/pci/hda/patch_via.c                       |   25 ++++++--
 sound/usb/card.c                                |   12 ++--
 sound/usb/card.h                                |    1 +
 sound/usb/endpoint.c                            |    9 ++-
 sound/usb/mixer.c                               |   65 ++++++++++++-------
 sound/usb/mixer_quirks.c                        |   37 +++++++++--
 sound/usb/pcm.c                                 |   35 +++++++---
 sound/usb/proc.c                                |    4 +-
 sound/usb/usbaudio.h                            |    2 +-
 109 files changed, 867 insertions(+), 467 deletions(-)
Signature · 2 lines
Ben Hutchings
friends: People who know you well, but like you anyway.
PATCH 1/82 Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit f1e91e1640d808d332498a6b09b2bcd01462eff9 upstream.
The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
---
 include/net/bluetooth/bluetooth.h |   22 ----------------------
 net/bluetooth/Kconfig             |   37 +++++++++----------------------------
 net/bluetooth/Makefile            |    5 ++---
 net/bluetooth/bnep/Kconfig        |    2 +-
 net/bluetooth/cmtp/Kconfig        |    2 +-
 net/bluetooth/hidp/Kconfig        |    2 +-
 net/bluetooth/rfcomm/Kconfig      |    2 +-
 7 files changed, 15 insertions(+), 57 deletions(-)
include/net/bluetooth/bluetooth.h +0 -22
@@ -250,32 +250,10 @@ extern void bt_sysfs_cleanup(void);extern struct dentry *bt_debugfs; -#ifdef CONFIG_BT_L2CAP int l2cap_init (void );void l2cap_exit (void ); -#else -static inline int l2cap_init (void ) -{ -return 0 ; -} - -static inline void l2cap_exit (void ) -{ -} -#endif -#ifdef CONFIG_BT_SCO int sco_init (void );void sco_exit (void ); -#else -static inline int sco_init (void ) -{ -return 0 ; -} - -static inline void sco_exit (void ) -{ -} -#endif #endif /* __BLUETOOTH_H */
net/bluetooth/Kconfig +9 -28
@@ -6,7 +6,11 @@ menuconfig BT tristate "Bluetooth subsystem support" depends on NET && !S390 depends on RFKILL || !RFKILL + select CRC16 select CRYPTO + select CRYPTO_BLKCIPHER + select CRYPTO_AES + select CRYPTO_ECB help Bluetooth is low-cost, low-power, short-range wireless technology. It was designed as a replacement for cables and other short-range
@@ -15,10 +19,12 @@ menuconfig BT
 	  Bluetooth can be found at <http://www.bluetooth.com/>.

 	  Linux Bluetooth subsystem consist of several layers:
-	     Bluetooth Core (HCI device and connection manager, scheduler)
+	     Bluetooth Core
+		HCI device and connection manager, scheduler
+		SCO audio links
+		L2CAP (Logical Link Control and Adaptation Protocol)
+		SMP (Security Manager Protocol) on LE (Low Energy) links
 	     HCI Device drivers (Interface to the hardware)
-	     SCO Module (SCO audio links)
-	     L2CAP Module (Logical Link Control and Adaptation Protocol)
 	     RFCOMM Module (RFCOMM Protocol)
 	     BNEP Module (Bluetooth Network Encapsulation Protocol)
 	     CMTP Module (CAPI Message Transport Protocol)
@@ -33,31 +39,6 @@ menuconfig BT
 	  to Bluetooth kernel modules are provided in the BlueZ packages.  For
 	  more information, see <http://www.bluez.org/>.

-if BT != n
-
-config BT_L2CAP
-	bool "L2CAP protocol support"
-	select CRC16
-	select CRYPTO
-	select CRYPTO_BLKCIPHER
-	select CRYPTO_AES
-	select CRYPTO_ECB
-	help
-	  L2CAP (Logical Link Control and Adaptation Protocol) provides
-	  connection oriented and connection-less data transport.  L2CAP
-	  support is required for most Bluetooth applications.
-
-	  Also included is support for SMP (Security Manager Protocol) which
-	  is the security layer on top of LE (Low Energy) links.
-
-config BT_SCO
-	bool "SCO links support"
-	help
-	  SCO link provides voice transport over Bluetooth.  SCO support is
-	  required for voice applications like Headset and Audio.
-
-endif
-
 source "net/bluetooth/rfcomm/Kconfig"

 source "net/bluetooth/bnep/Kconfig"
net/bluetooth/Makefile +2 -3
@@ -8,6 +8,5 @@ obj-$(CONFIG_BT_BNEP) += bnep/ obj-$(CONFIG_BT_CMTP) += cmtp/ obj-$(CONFIG_BT_HIDP) += hidp/ -bluetooth-y := af_bluetooth.o hci_core.o hci_conn.o hci_event.o mgmt.o hci_sock.o hci_sysfs.o lib.o -bluetooth-$(CONFIG_BT_L2CAP) += l2cap_core.o l2cap_sock.o smp.o -bluetooth-$(CONFIG_BT_SCO) += sco.o +bluetooth-y := af_bluetooth.o hci_core.o hci_conn.o hci_event.o mgmt.o \ + hci_sock.o hci_sysfs.o l2cap_core.o l2cap_sock.o smp.o sco.o lib.o
net/bluetooth/bnep/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_BNEP tristate "BNEP protocol support" - depends on BT && BT_L2CAP + depends on BT select CRC32 help BNEP (Bluetooth Network Encapsulation Protocol) is Ethernet
net/bluetooth/cmtp/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_CMTP tristate "CMTP protocol support" - depends on BT && BT_L2CAP && ISDN_CAPI + depends on BT && ISDN_CAPI help CMTP (CAPI Message Transport Protocol) is a transport layer for CAPI messages. CMTP is required for the Bluetooth Common
net/bluetooth/hidp/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_HIDP tristate "HIDP protocol support" - depends on BT && BT_L2CAP && INPUT && HID_SUPPORT + depends on BT && INPUT && HID_SUPPORT select HID help HIDP (Human Interface Device Protocol) is a transport layer
net/bluetooth/rfcomm/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_RFCOMM tristate "RFCOMM protocol support" - depends on BT && BT_L2CAP + depends on BT help RFCOMM provides connection oriented stream transport. RFCOMM support is required for Dialup Networking, OBEX and other Bluetooth
Re: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
Hi Ben,
Quoted 10 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Gustavo
David Miller
maintainerRe: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
From: Gustavo Padovan <[email protected]>
Date: Wed, 14 Nov 2012 19:24:26 -0200
Quoted 10 lines
Hi Ben,
Quoted 6 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
Quoted 8 lines
Quoted 4 lines
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Agreed, I wish this had not been merged into -stable, I would have never submitted a patch like this myself.
Re: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
Quoted 18 lines · David Miller
From: Gustavo Padovan <[email protected]>
Date: Wed, 14 Nov 2012 19:24:26 -0200Quoted 15 lines
Hi Ben,
Quoted 10 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
Quoted 6 lines
Quoted 3 lines
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Agreed, I wish this had not been merged into -stable, I would have never submitted a patch like this myself.
This is required by:
commit ff03261adc8b4bdd8291f1783c079b53a892b429
Author: Vinicius Costa Gomes <[email protected]>
Date:   Thu Aug 23 21:32:44 2012 -0300
Bluetooth: Fix sending a HCI Authorization Request over LE links
commit d8343f125710fb596f7a88cd756679f14f4e77b9 upstream.
which was already applied.
Ben.
Signature · 3 lines
Ben Hutchings
We get into the habit of living before acquiring the habit of thinking.
- Albert CamusRe: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
Quoted 29 lines · Ben Hutchings
Quoted 18 lines · David Miller
From: Gustavo Padovan <[email protected]>
Date: Wed, 14 Nov 2012 19:24:26 -0200Quoted 15 lines
Hi Ben,
Quoted 10 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
Quoted 6 lines
Quoted 3 lines
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Agreed, I wish this had not been merged into -stable, I would have never submitted a patch like this myself.
This is required by:
commit
ff03261adc8b4bdd8291f1783c079b53a892b429
Quoted 8 lines
Author: Vinicius Costa Gomes <[email protected]>
Date:   Thu Aug 23 21:32:44 2012 -0300
Bluetooth: Fix sending a HCI Authorization Request over LE links
commit
d8343f125710fb596f7a88cd756679f14f4e77b9upstream.which was already applied.
So, do you think it's better to revert that in 3.2, or to go ahead with this?
Ben.
Signature · 2 lines
Ben Hutchings
friends: People who know you well, but like you anyway.
David Miller
maintainerRe: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
From: Ben Hutchings <[email protected]>
Date: Thu, 15 Nov 2012 20:04:32 +0000
Quoted 33 lines · Ben Hutchings
Quoted 32 lines · David Miller
Quoted 18 lines
From: Gustavo Padovan <[email protected]>
Date: Wed, 14 Nov 2012 19:24:26 -0200Quoted 15 lines
Hi Ben,
Quoted 10 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
Quoted 6 lines
Quoted 3 lines
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Agreed, I wish this had not been merged into -stable, I would have never submitted a patch like this myself.
This is required by:
commit
ff03261adc8b4bdd8291f1783c079b53a892b429Author: Vinicius Costa Gomes <[email protected]> Date: Thu Aug 23 21:32:44 2012 -0300
Quoted 8 lines
Quoted 5 lines
Bluetooth: Fix sending a HCI Authorization Request over LE links
commit
d8343f125710fb596f7a88cd756679f14f4e77b9upstream.which was already applied.
So, do you think it's better to revert that in 3.2, or to go ahead with this?
I can't believe that just turning on bluetooth is going to force enable these sub-protocols too, that's simply rediculous. That change should have never gone into the tree.
Do I _REALLY_ have to go back to validating all the bluetooth stuff by hand when John Linville sends me pull requests? Seriously?
I thought we were beyond that kind of bullshit after the coding style fiasco.
Actually I have a better idea, how about John stops pulling the bluetooth stuff into his tree, and instead the bluetooth folks have to submit their changes individually to the netdev list. I like that scheme better.
Because I don't want John's wireless work held back by the garbage these bluetooth guys keep submitting.
Re: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
Hi David,
Quoted 40 lines · David Miller
From: Ben Hutchings <[email protected]>
Date: Thu, 15 Nov 2012 20:04:32 +0000Quoted 37 lines · Ben Hutchings
Quoted 36 lines · David Miller
Quoted 18 lines
From: Gustavo Padovan <[email protected]>
Date: Wed, 14 Nov 2012 19:24:26 -0200Quoted 15 lines
Hi Ben,
Quoted 10 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
Quoted 6 lines
Quoted 3 lines
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Agreed, I wish this had not been merged into -stable, I would have never submitted a patch like this myself.
This is required by:
commit
ff03261adc8b4bdd8291f1783c079b53a892b429Author: Vinicius Costa Gomes <[email protected]> Date: Thu Aug 23 21:32:44 2012 -0300Bluetooth: Fix sending a HCI Authorization Request over LE links
commit
d8343f125710fb596f7a88cd756679f14f4e77b9upstream.
Quoted 8 lines
Quoted 4 lines
Quoted 1 line
which was already applied.
So, do you think it's better to revert that in 3.2, or to go ahead with this?
I can't believe that just turning on bluetooth is going to force enable these sub-protocols too, that's simply rediculous. That change should have never gone into the tree.
I think you should go and try to understand our subsystem better, if one wants use bluetooth on linux he/she needs HCI core, L2CAP and SCO. Those were three different modules in the past, but at some point we concluded it does not makes sense to have the split. L2CAP for example is needed for every bluetooth usage out there, it is really part of the core. It useless to load the bluetooth core module without l2cap and sco. There is a technical decision behind this that we, the bluetooth folk, think it is better this way.
Quoted 10 lines
Do I _REALLY_ have to go back to validating all the bluetooth stuff by hand when John Linville sends me pull requests? Seriously?
I thought we were beyond that kind of bullshit after the coding style fiasco.
Actually I have a better idea, how about John stops pulling the bluetooth stuff into his tree, and instead the bluetooth folks have to submit their changes individually to the netdev list. I like that scheme better.
We will no put our stuff in netdev. I'll keep pushing patches to bluetooth-next, our community needs this tree.
Gustavo
David Miller
maintainerRe: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
From: Gustavo Padovan <[email protected]>
Date: Thu, 15 Nov 2012 19:04:37 -0200
Quoted 1 line
We will no put our stuff in netdev.
You very much better post your work there for review purposes or else I'm not even going to consider pulling from your tree, and I'm going to tell John to not pull your GIT tree in either.
Re: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
In reply to Gustavo PadovanQuoted 4 lines · Gustavo Padovan
if one
wants use bluetooth on linux he/she needs HCI core, L2CAP and SCO. Those were three different modules in the past, but at some point we concluded it does not makes sense to have the split.
You could remove the unused CONFIG_ remnants
$ git grep CONFIG_BT_L2CAP
(unused but for defconfigs)
$ git grep CONFIG_BT_SCO
(unused but for defconfigs)
Re: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
In reply to Ben HutchingsHi Ben,
Quoted 33 lines · Ben Hutchings
Quoted 32 lines · Ben Hutchings
Quoted 18 lines · David Miller
From: Gustavo Padovan <[email protected]>
Date: Wed, 14 Nov 2012 19:24:26 -0200Quoted 15 lines
Hi Ben,
Quoted 10 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
Quoted 6 lines
Quoted 3 lines
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Agreed, I wish this had not been merged into -stable, I would have never submitted a patch like this myself.
This is required by:
commit
ff03261adc8b4bdd8291f1783c079b53a892b429Author: Vinicius Costa Gomes <[email protected]> Date: Thu Aug 23 21:32:44 2012 -0300
Quoted 8 lines
Quoted 5 lines
Bluetooth: Fix sending a HCI Authorization Request over LE links
commit
d8343f125710fb596f7a88cd756679f14f4e77b9upstream.which was already applied.
So, do you think it's better to revert that in 3.2, or to go ahead with this?
I suggest you to revert it. There is a much simpler solution if revert, fix the patch and apply it again. No need to push this module merge patch here.
The problem seems to be only a missing EXPORT_SYMBOL of the smp.c method. That should fix it. If you want me to fix that just ask me.
Gustavo
Re: [ 01/82] Bluetooth: Always compile SCO and L2CAP in Bluetooth Core
Quoted 43 lines · Gustavo Padovan
Hi Ben,
Quoted 39 lines · Ben Hutchings
Quoted 37 lines · Ben Hutchings
Quoted 18 lines · David Miller
From: Gustavo Padovan <[email protected]>
Date: Wed, 14 Nov 2012 19:24:26 -0200Quoted 15 lines
Hi Ben,
Quoted 10 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ulisses Furquim <[email protected]>
commit
f1e91e1640d808d332498a6b09b2bcd01462eff9upstream.The handling of SCO audio links and the L2CAP protocol are essential to any system with Bluetooth thus are always compiled in from now on.
Quoted 6 lines
Quoted 3 lines
I wonder if this could not break any kind of script or code people have that refer directly to the sco and l2cap modules. Also I don't see this change as really necessary for 3.2.
Agreed, I wish this had not been merged into -stable, I would have never submitted a patch like this myself.
This is required by:
commit
ff03261adc8b4bdd8291f1783c079b53a892b429Author: Vinicius Costa Gomes <[email protected]> Date: Thu Aug 23 21:32:44 2012 -0300Bluetooth: Fix sending a HCI Authorization Request over LE links
commit
d8343f125710fb596f7a88cd756679f14f4e77b9upstream.which was already applied.
Quoted 8 lines
Quoted 2 lines
So, do you think it's better to revert that in 3.2, or to go ahead with this?
I suggest you to revert it. There is a much simpler solution if revert, fix the patch and apply it again. No need to push this module merge patch here.
The problem seems to be only a missing
EXPORT_SYMBOLof thesmp.cmethod. That should fix it. If you want me to fix that just ask me.
smp_conn_security() is either in the same module or not defined at all. I'll add an #ifdef CONFIG_BT_L2CAP instead of this patch.
Ben.
Signature · 3 lines
Ben Hutchings
Theory and practice are closer in theory than in practice.
- John Levine, moderator of comp.compilersPATCH 2/82 x86: Remove the ancient and deprecated disable_hlt() and enable_hlt() facility
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Len Brown <[email protected]>
commit f6365201d8a21fb347260f89d6e9b3e718d63c70 upstream.
The X86_32-only disable_hlt/enable_hlt mechanism was used by the 32-bit floppy driver. Its effect was to replace the use of the HLT instruction inside default_idle() with cpu_relax() - essentially it turned off the use of HLT.
This workaround was commented in the code as:
"disable hlt during certain critical i/o operations"
"This halt magic was a workaround for ancient floppy DMA
wreckage. It should be safe to remove."
H. Peter Anvin additionally adds:
"To the best of my knowledge, no-hlt only existed because of
flaky power distributions on 386/486 systems which were sold to run DOS. Since DOS did no power management of any kind, including HLT, the power draw was fairly uniform; when exposed to the much hhigher noise levels you got when Linux used HLT caused some of these systems to fail.
They were by far in the minority even back then."
Alan Cox further says:
"Also for the Cyrix 5510 which tended to go castors up if a HLT
occurred during a DMA cycle and on a few other boxes HLT during DMA tended to go astray.
Do we care ? I doubt it. The 5510 was pretty obscure, the 5520 fixed it, the 5530 is probably the oldest still in any kind of use."
So, let's finally drop this.
[ If anyone cares then alternative instruction patching could be
used to replace HLT with a one-byte NOP instruction. Much simpler. ]
---
Documentation/feature-removal-schedule.txt +0 -8
@@ -6,14 +6,6 @@ be removed from this file.

 ---------------------------

-What:	x86 floppy disable_hlt
-When:	2012
-Why:	ancient workaround of dubious utility clutters the
-	code used by everybody else.
-Who:	Len Brown <[email protected]>
-
----------------------------
-
 What:	CONFIG_APM_CPU_IDLE, and its ability to call APM BIOS in idle
 When:	2012
 Why:	This optional sub-feature of APM is of dubious reliability,
arch/x86/include/asm/system.h +0 -7
@@ -93,10 +93,6 @@ do { \ "memory"); \ } while (0) -/* -* disable hlt during certain critical i/o operations - */ -#define HAVE_DISABLE_HLT #else /* frame pointer must be last for get_wchan */
@@ -392,9 +388,6 @@ static inline void clflush(volatile void#define nop () asm volatile ("nop") -void disable_hlt (void ); -void enable_hlt (void ); -void cpu_idle_wait (void );extern unsigned long arch_align_stack (unsigned long sp);
arch/x86/kernel/process.c +0 -24
@@ -341,34 +341,10 @@ void (*pm_idle)(void);EXPORT_SYMBOL (pm_idle);#endif -#ifdef CONFIG_X86_32 -/* -* This halt magic was a workaround for ancient floppy DMA -* wreckage. It should be safe to remove. -*/ -static int hlt_counter; -void disable_hlt (void ) -{ - hlt_counter++; -} -EXPORT_SYMBOL (disable_hlt); - -void enable_hlt (void ) -{ - hlt_counter--; -} -EXPORT_SYMBOL (enable_hlt); - -static inline int hlt_use_halt (void ) -{ -return (!hlt_counter && boot_cpu_data.hlt_works_ok); -} -#else static inline int hlt_use_halt (void ) {return 1 ; } -#endif /* * We use this if we don't have any better
drivers/block/floppy.c +0 -36
@@ -1032,37 +1032,6 @@ static int fd_wait_for_completion(unsignreturn 0 ; } -static DEFINE_SPINLOCK (floppy_hlt_lock); -static int hlt_disabled; -static void floppy_disable_hlt (void ) -{ -unsigned long flags; - -WARN_ONCE (1 ,"floppy_disable_hlt() scheduled for removal in 2012" ); -spin_lock_irqsave (&floppy_hlt_lock, flags); -if (!hlt_disabled) { - hlt_disabled =1 ; -#ifdef HAVE_DISABLE_HLT -disable_hlt (); -#endif - } -spin_unlock_irqrestore (&floppy_hlt_lock, flags); -} - -static void floppy_enable_hlt (void ) -{ -unsigned long flags; - -spin_lock_irqsave (&floppy_hlt_lock, flags); -if (hlt_disabled) { - hlt_disabled =0 ; -#ifdef HAVE_DISABLE_HLT -enable_hlt (); -#endif - } -spin_unlock_irqrestore (&floppy_hlt_lock, flags); -} -static void setup_DMA (void ) {unsigned long f;
@@ -1107,7 +1076,6 @@ static void setup_DMA(void)fd_enable_dma ();release_dma_lock (f);#endif -floppy_disable_hlt (); }static void show_floppy (void );
@@ -1709,7 +1677,6 @@ irqreturn_t floppy_interrupt(int irq, vofd_disable_dma ();release_dma_lock (f); -floppy_enable_hlt (); do_floppy =NULL ;if (fdc >=N_FDC ||FDCS ->address ==-1 ) {/* we don't even know which FDC is the culprit */
@@ -1858,8 +1825,6 @@ static void floppy_shutdown(unsigned lonshow_floppy ();cancel_activity (); -floppy_enable_hlt (); - flags =claim_dma_lock ();fd_disable_dma ();release_dma_lock (flags);
@@ -4510,7 +4475,6 @@ static void floppy_release_irq_and_dma(v#if N_FDC >1 set_dor (1 , ~8 ,0 );#endif -floppy_enable_hlt ();if (floppy_track_buffer && max_buffer_sectors) { tmpsize = max_buffer_sectors *1024 ;
PATCH 3/82 drm/nouveau: silence modesetting spam on pre-gf8 chipsets
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ben Skeggs <[email protected]>
commit cee59f15a60cc6269a25e3f6fbf1a577d6ab8115 upstream.
---
 drivers/gpu/drm/nouveau/nv04_dac.c | 8 ++++----
 drivers/gpu/drm/nouveau/nv04_dfp.c | 6 +++---
 drivers/gpu/drm/nouveau/nv04_tv.c  | 4 ++--
 3 files changed, 9 insertions(+), 9 deletions(-)
drivers/gpu/drm/nouveau/nv04_dac.c +4 -4
@@ -210,7 +210,7 @@ out:NVWriteVgaCrtc (dev,0 ,NV_CIO_CR_MODE_INDEX , saved_cr_mode);if (blue ==0x18 ) { -NV_INFO (dev,"Load detected on head A\n" ); +NV_DEBUG (dev,"Load detected on head A\n" );return connector_status_connected; }
@@ -323,7 +323,7 @@ nv17_dac_detect(struct drm_encoder *encoder, struct drm_connector *connector)if (nv17_dac_sample_load (encoder) &NV_PRAMDAC_TEST_CONTROL_SENSEB_ALLHI ) { -NV_INFO (dev,"Load detected on output %c\n" , +NV_DEBUG (dev,"Load detected on output %c\n" ,'@' +ffs (dcb->or));return connector_status_connected; }else {
@@ -398,7 +398,7 @@ static void nv04_dac_commit(struct drm_encoder *encoder) helper->dpms (encoder,DRM_MODE_DPMS_ON ); -NV_INFO (dev,"Output %s is running on CRTC %d using output %c\n" , +NV_DEBUG (dev,"Output %s is running on CRTC %d using output %c\n" ,drm_get_connector_name (&nouveau_encoder_connector_get (nv_encoder)->base), nv_crtc->index,'@' +ffs (nv_encoder->dcb->or)); }
@@ -447,7 +447,7 @@ static void nv04_dac_dpms(struct drm_encoder *encoder, int mode)return ; nv_encoder->last_dpms = mode; -NV_INFO (dev,"Setting dpms mode %d on vga encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on vga encoder (output %d)\n" , mode, nv_encoder->dcb->index);nv04_dac_update_dacclk (encoder, mode ==DRM_MODE_DPMS_ON );
drivers/gpu/drm/nouveau/nv04_dfp.c +3 -3
@@ -476,7 +476,7 @@ static void nv04_dfp_commit(struct drm_encoder *encoder) helper->dpms (encoder,DRM_MODE_DPMS_ON ); -NV_INFO (dev,"Output %s is running on CRTC %d using output %c\n" , +NV_DEBUG (dev,"Output %s is running on CRTC %d using output %c\n" ,drm_get_connector_name (&nouveau_encoder_connector_get (nv_encoder)->base), nv_crtc->index,'@' +ffs (nv_encoder->dcb->or)); }
@@ -519,7 +519,7 @@ static void nv04_lvds_dpms(struct drm_encoder *encoder, int mode)return ; nv_encoder->last_dpms = mode; -NV_INFO (dev,"Setting dpms mode %d on lvds encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on lvds encoder (output %d)\n" , mode, nv_encoder->dcb->index);if (was_powersaving &&is_powersaving_dpms (mode))
@@ -564,7 +564,7 @@ static void nv04_tmds_dpms(struct drm_encoder *encoder, int mode)return ; nv_encoder->last_dpms = mode; -NV_INFO (dev,"Setting dpms mode %d on tmds encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on tmds encoder (output %d)\n" , mode, nv_encoder->dcb->index);nv04_dfp_update_backlight (encoder, mode);
drivers/gpu/drm/nouveau/nv04_tv.c +2 -2
@@ -69,7 +69,7 @@ static void nv04_tv_dpms(struct drm_encoder *encoder, int mode)struct nv04_mode_state *state = &dev_priv->mode_reg;uint8_t crtc1A; -NV_INFO (dev,"Setting dpms mode %d on TV encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on TV encoder (output %d)\n" , mode, nv_encoder->dcb->index); state->pllsel &= ~(PLLSEL_TV_CRTC1_MASK |PLLSEL_TV_CRTC2_MASK );
@@ -162,7 +162,7 @@ static void nv04_tv_commit(struct drm_encoder *encoder) helper->dpms (encoder,DRM_MODE_DPMS_ON ); -NV_INFO (dev,"Output %s is running on CRTC %d using output %c\n" , +NV_DEBUG (dev,"Output %s is running on CRTC %d using output %c\n" ,drm_get_connector_name (&nouveau_encoder_connector_get (nv_encoder)->base), nv_crtc->index,'@' +ffs (nv_encoder->dcb->or)); }
PATCH 4/82 drm/nouveau: fix suspend/resume when in headless mode
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ben Skeggs <[email protected]>
commit 9430738d80223a1cd791a2baa74fa170d3df1262 upstream.
[[email protected]: backport to 3.2: make fbcon suspend/resume
handling conditional in a vague hope that this will approximate what the original does for 3.3+]
---
 drivers/gpu/drm/nouveau/nouveau_drv.c | 32 ++++++++++++++++++++------------
 1 file changed, 20 insertions(+), 12 deletions(-)
drivers/gpu/drm/nouveau/nouveau_drv.c +20 -12
@@ -178,8 +178,10 @@ nouveau_pci_suspend(struct pci_dev *pdev, pm_message_t pm_state)if (dev->switch_power_state ==DRM_SWITCH_POWER_OFF )return 0 ; -NV_INFO (dev,"Disabling fbcon acceleration...\n" ); -nouveau_fbcon_save_disable_accel (dev); +if (dev->mode_config.num_crtc) { +NV_INFO (dev,"Disabling fbcon acceleration...\n" ); +nouveau_fbcon_save_disable_accel (dev); + }NV_INFO (dev,"Unpinning framebuffer(s)...\n" );list_for_each_entry (crtc, &dev->mode_config.crtc_list, head) {
@@ -246,10 +248,12 @@ nouveau_pci_suspend(struct pci_dev *pdev, pm_message_t pm_state)pci_set_power_state (pdev, PCI_D3hot); } -console_lock (); -nouveau_fbcon_set_suspend (dev,1 ); -console_unlock (); -nouveau_fbcon_restore_accel (dev); +if (dev->mode_config.num_crtc) { +console_lock (); +nouveau_fbcon_set_suspend (dev,1 ); +console_unlock (); +nouveau_fbcon_restore_accel (dev); + }return 0 ; out_abort:
@@ -275,7 +279,8 @@ nouveau_pci_resume(struct pci_dev *pdev)if (dev->switch_power_state ==DRM_SWITCH_POWER_OFF )return 0 ; -nouveau_fbcon_save_disable_accel (dev); +if (dev->mode_config.num_crtc) +nouveau_fbcon_save_disable_accel (dev);NV_INFO (dev,"We're back, enabling device...\n" );pci_set_power_state (pdev,PCI_D0 );
@@ -376,15 +381,18 @@ nouveau_pci_resume(struct pci_dev *pdev) nv_crtc->lut.depth =0 ; } -console_lock (); -nouveau_fbcon_set_suspend (dev,0 ); -console_unlock (); +if (dev->mode_config.num_crtc) { +console_lock (); +nouveau_fbcon_set_suspend (dev,0 ); +console_unlock (); -nouveau_fbcon_zfill_all (dev); +nouveau_fbcon_zfill_all (dev); + }drm_helper_resume_force_mode (dev); -nouveau_fbcon_restore_accel (dev); +if (dev->mode_config.num_crtc) +nouveau_fbcon_restore_accel (dev);return 0 ; }
PATCH 5/82 drm/nouveau: headless mode by default if pci class != vga display
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ben Skeggs <[email protected]>
commit e412e95a268fa8544858ebfe066826b290430d51 upstream.
This is to prevent nouveau from taking over the console on headless boards such as Tesla.
---
 drivers/gpu/drm/nouveau/nouveau_drv.c   | 2 --
 drivers/gpu/drm/nouveau/nouveau_state.c | 4 +++-
 2 files changed, 3 insertions(+), 3 deletions(-)
drivers/gpu/drm/nouveau/nouveau_drv.c +0 -2
@@ -488,9 +488,7 @@ static int __init nouveau_init(void)#ifdef CONFIG_VGA_CONSOLE if (vgacon_text_force ()) nouveau_modeset =0 ; - else#endif - nouveau_modeset =1 ; }if (!nouveau_modeset)
drivers/gpu/drm/nouveau/nouveau_state.c +3 -1
@@ -50,6 +50,7 @@ static int nouveau_init_engine_ptrs(struct drm_device *dev) {struct drm_nouveau_private *dev_priv = dev->dev_private;struct nouveau_engine *engine = &dev_priv->engine; +u32 pclass = dev->pdev->class >>8 ;switch (dev_priv->chipset &0xf0 ) {case 0x00 :
@@ -428,7 +429,8 @@ static int nouveau_init_engine_ptrs(struct drm_device *dev) }/* headless mode */ -if (nouveau_modeset ==2 ) { +if (nouveau_modeset ==2 || + (nouveau_modeset <0 && pclass !=PCI_CLASS_DISPLAY_VGA )) { engine->display.early_init = nouveau_stub_init; engine->display.late_takedown = nouveau_stub_takedown; engine->display.create = nouveau_stub_init;
PATCH 6/82 nfsd: add get_uint for u32s
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: "J. Bruce Fields" <[email protected]>
commit a007c4c3e943ecc054a806c259d95420a188754b upstream.
I don't think there's a practical difference for the range of values these interfaces should see, but it would be safer to be unambiguous.
---
 fs/nfsd/export.c             |    6 +++---
 include/linux/sunrpc/cache.h |   16 ++++++++++++++++
 2 files changed, 19 insertions(+), 3 deletions(-)
fs/nfsd/export.c +3 -3
@@ -398,7 +398,7 @@ fsloc_parse(char **mesg, char *buf, struct nfsd4_fs_locations *fsloc)int migrated, i, err;/* listsize */ - err =get_int (mesg, &fsloc->locations_count); + err =get_uint (mesg, &fsloc->locations_count);if (err)return err;if (fsloc->locations_count >MAX_FS_LOCATIONS )
@@ -456,7 +456,7 @@ static int secinfo_parse(char **mesg, char *buf, struct svc_export *exp)return -EINVAL ;for (f = exp->ex_flavors; f < exp->ex_flavors + listsize; f++) { - err =get_int (mesg, &f->pseudoflavor); + err =get_uint (mesg, &f->pseudoflavor);if (err)return err;/*
@@ -465,7 +465,7 @@ static int secinfo_parse(char **mesg, char *buf, struct svc_export *exp)* problem at export time instead of when a client fails * to authenticate. */ - err =get_int (mesg, &f->flags); + err =get_uint (mesg, &f->flags);if (err)return err;/* Only some flags are allowed to differ between flavors: */
include/linux/sunrpc/cache.h +16 -0
@@ -230,6 +230,22 @@ static inline int get_int(char **bpp, int *anint)return 0 ; } +static inline int get_uint (char **bpp,unsigned int *anint) +{ +char buf[50 ]; +int len =qword_get (bpp, buf,sizeof (buf)); + +if (len <0 ) +return -EINVAL ; +if (len ==0 ) +return -ENOENT ; + +if (kstrtouint (buf,0 , anint)) +return -EINVAL ; + +return 0 ; +} +/* * timestamps kept in the cache are expressed in seconds * since boot. This is the best for measuring differences in
PATCH 7/82 ALSA: PCM: Fix some races at disconnection
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit 9b0573c07f278e9888c352aa9724035c75784ea0 upstream.
Fix races at PCM disconnection:
- while a PCM device is being opened or closed
- while the PCM state is being changed without lock in prepare, hw_params, hw_free ops
---
 sound/core/pcm.c        |  7 ++++++-
 sound/core/pcm_native.c | 16 ++++++++++++----
 2 files changed, 18 insertions(+), 5 deletions(-)
sound/core/pcm.c +6 -1
@@ -1046,11 +1046,15 @@ static int snd_pcm_dev_disconnect(struct snd_device *device)if (list_empty (&pcm->list)) goto unlock; +mutex_lock (&pcm->open_mutex);list_del_init (&pcm->list);for (cidx =0 ; cidx <2 ; cidx++) -for (substream = pcm->streams[cidx].substream; substream; substream = substream->next) +for (substream = pcm->streams[cidx].substream; substream; substream = substream->next) { +snd_pcm_stream_lock_irq (substream);if (substream->runtime) substream->runtime->status->state =SNDRV_PCM_STATE_DISCONNECTED ; +snd_pcm_stream_unlock_irq (substream); + }list_for_each_entry (notify, &snd_pcm_notify_list, list) { notify->n_disconnect (pcm); }
@@ -1066,6 +1070,7 @@ static int snd_pcm_dev_disconnect(struct snd_device *device) }snd_unregister_device (devtype, pcm->card, pcm->device); } +mutex_unlock (&pcm->open_mutex); unlock:mutex_unlock (®ister_mutex);return 0 ;
sound/core/pcm_native.c +12 -4
@@ -369,6 +369,14 @@ static int period_to_usecs(struct snd_pcm_runtime *runtime)return usecs; } +static void snd_pcm_set_state (struct snd_pcm_substream *substream,int state) +{ +snd_pcm_stream_lock_irq (substream); +if (substream->runtime->status->state !=SNDRV_PCM_STATE_DISCONNECTED ) + substream->runtime->status->state = state; +snd_pcm_stream_unlock_irq (substream); +} +static int snd_pcm_hw_params (struct snd_pcm_substream *substream,struct snd_pcm_hw_params *params) {
@@ -452,7 +460,7 @@ static int snd_pcm_hw_params(struct snd_pcm_substream *substream, runtime->boundary *=2 ;snd_pcm_timer_resolution_change (substream); - runtime->status->state =SNDRV_PCM_STATE_SETUP ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_SETUP );if (pm_qos_request_active (&substream->latency_pm_qos_req))pm_qos_remove_request (&substream->latency_pm_qos_req);
@@ -464,7 +472,7 @@ static int snd_pcm_hw_params(struct snd_pcm_substream *substream,/* hardware might be unusable from this time, so we force application to retry to set the correct hardware parameter settings */ - runtime->status->state =SNDRV_PCM_STATE_OPEN ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_OPEN );if (substream->ops->hw_free !=NULL ) substream->ops->hw_free (substream);return err;
@@ -512,7 +520,7 @@ static int snd_pcm_hw_free(struct snd_pcm_substream *substream)return -EBADFD ;if (substream->ops->hw_free) result = substream->ops->hw_free (substream); - runtime->status->state =SNDRV_PCM_STATE_OPEN ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_OPEN );pm_qos_remove_request (&substream->latency_pm_qos_req);return result; }
@@ -1320,7 +1328,7 @@ static void snd_pcm_post_prepare(struct snd_pcm_substream *substream, int state) {struct snd_pcm_runtime *runtime = substream->runtime; runtime->control->appl_ptr = runtime->status->hw_ptr; - runtime->status->state =SNDRV_PCM_STATE_PREPARED ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_PREPARED ); }static struct action_ops snd_pcm_action_prepare = {
PATCH 8/82 ALSA: usb-audio: Fix races at disconnection
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit 978520b75f0a1ce82b17e1e8186417250de6d545 upstream.
Close some races at disconnection of a USB audio device by adding the chip->shutdown_mutex and chip->shutdown check at appropriate places.
The spots to put bandaids are:
- PCM prepare, hw_params and hw_free
- where the usb device is accessed for communication or get speed, in mixer.c and others; the device speed is now cached in subs->speed instead of accessing to chip->dev
The accesses in PCM open and close don't need the mutex protection because these are already handled in the core PCM disconnection code.
The autosuspend/autoresume codes are still uncovered by this patch because of possible mutex deadlocks. They'll be covered by the upcoming change to rwsem.
Also the mixer codes are untouched, too. These will be fixed in another patch, too.
---
 sound/usb/card.h     |  1 +
 sound/usb/endpoint.c |  9 +++++---
 sound/usb/mixer.c    | 65 ++++++++++++++++++++++++++++++++++------------------
 sound/usb/pcm.c      | 31 +++++++++++++++++++------
 sound/usb/proc.c     |  4 ++--
 5 files changed, 76 insertions(+), 34 deletions(-)
sound/usb/card.h +1 -0
@@ -86,6 +86,7 @@ struct snd_usb_substream {struct snd_urb_ctx syncurb[SYNC_URBS ];/* sync urb table */ char *syncbuf;/* sync buffer for all sync URBs */ dma_addr_t sync_dma;/* DMA address of syncbuf */ +unsigned int speed;/* USB_SPEED_XXX */ u64 formats;/* format bitmasks (all or'ed) */ unsigned int num_formats;/* number of supported audio formats (list) */
sound/usb/endpoint.c +6 -3
@@ -148,8 +148,10 @@ void snd_usb_release_substream_urbs(struct snd_usb_substream *subs, int force)int i;/* stop urbs (to be sure) */ -deactivate_urbs (subs, force,1 ); -wait_clear_urbs (subs); +if (!subs->stream->chip->shutdown) { +deactivate_urbs (subs, force,1 ); +wait_clear_urbs (subs); + }for (i =0 ; i <MAX_URBS ; i++)release_urb_ctx (&subs->dataurb[i]);
@@ -895,7 +897,8 @@ void snd_usb_init_substream(struct snd_usb_stream *as, subs->dev = as->chip->dev; subs->txfr_quirk = as->chip->txfr_quirk; subs->ops = audio_urb_ops[stream]; -if (snd_usb_get_speed (subs->dev) >=USB_SPEED_HIGH ) + subs->speed =snd_usb_get_speed (subs->dev); +if (subs->speed >=USB_SPEED_HIGH ) subs->ops.prepare_sync = prepare_capture_sync_urb_hs;snd_usb_set_pcm_ops (as->pcm, stream);
sound/usb/mixer.c +43 -22
117 lines not on this page · raw message
sound/usb/pcm.c +24 -7
@@ -67,6 +67,8 @@ static snd_pcm_uframes_t snd_usb_pcm_pointer(struct snd_pcm_substream *substreamunsigned int hwptr_done; subs = (struct snd_usb_substream *)substream->runtime->private_data; +if (subs->stream->chip->shutdown) +return SNDRV_PCM_POS_XRUN ;spin_lock (&subs->lock); hwptr_done = subs->hwptr_done; substream->runtime->delay = snd_usb_pcm_delay(subs,
@@ -373,8 +375,14 @@ static int snd_usb_hw_params(struct snd_pcm_substream *substream, changed = subs->cur_audiofmt != fmt || subs->period_bytes !=params_period_bytes (hw_params) || subs->cur_rate != rate; + +mutex_lock (&subs->stream->chip->shutdown_mutex); +if (subs->stream->chip->shutdown) { + ret = -ENODEV ; + goto unlock; + }if ((ret =set_format (subs, fmt)) <0 ) -return ret; + goto unlock;if (subs->cur_rate != rate) {struct usb_host_interface *alts;
@@ -383,12 +391,11 @@ static int snd_usb_hw_params(struct snd_pcm_substream *substream, alts = &iface->altsetting[fmt->altset_idx]; ret =snd_usb_init_sample_rate (subs->stream->chip, subs->interface, alts, fmt, rate);if (ret <0 ) -return ret; + goto unlock; subs->cur_rate = rate; }if (changed) { -mutex_lock (&subs->stream->chip->shutdown_mutex);/* format changed */ snd_usb_release_substream_urbs (subs,0 );/* influenced: period_bytes, channels, rate, format, */
@@ -396,9 +403,10 @@ static int snd_usb_hw_params(struct snd_pcm_substream *substream,params_rate (hw_params),snd_pcm_format_physical_width (params_format (hw_params)) * params_channels(hw_params)); -mutex_unlock (&subs->stream->chip->shutdown_mutex); } +unlock: +mutex_unlock (&subs->stream->chip->shutdown_mutex);return ret; }
@@ -429,12 +437,18 @@ static int snd_usb_pcm_prepare(struct snd_pcm_substream *substream) {struct snd_pcm_runtime *runtime = substream->runtime;struct snd_usb_substream *subs = runtime->private_data; +int ret =0 ;if (! subs->cur_audiofmt) {snd_printk (KERN_ERR "usbaudio: no format is specified!\n" );return -ENXIO ; } +mutex_lock (&subs->stream->chip->shutdown_mutex); +if (subs->stream->chip->shutdown) { + ret = -ENODEV ; + goto unlock; + }/* some unit conversions in runtime */ subs->maxframesize =bytes_to_frames (runtime, subs->maxpacksize); subs->curframesize =bytes_to_frames (runtime, subs->curpacksize);
@@ -447,7 +461,10 @@ static int snd_usb_pcm_prepare(struct snd_pcm_substream *substream) subs->last_frame_number =0 ; runtime->delay =0 ; -return snd_usb_substream_prepare (subs, runtime); + ret =snd_usb_substream_prepare (subs, runtime); + unlock: +mutex_unlock (&subs->stream->chip->shutdown_mutex); +return ret; } static struct snd_pcm_hardware snd_usb_hardware =
@@ -500,7 +517,7 @@ static int hw_check_valid_format(struct snd_usb_substream *subs,return 0 ; }/* check whether the period time is >= the data packet interval */ -if (snd_usb_get_speed (subs->dev) !=USB_SPEED_FULL ) { +if (subs->speed !=USB_SPEED_FULL ) { ptime =125 * (1 << fp->datainterval);if (ptime > pt->max || (ptime == pt->max && pt->openmax)) {hwc_debug (" > check: ptime %u > max %u\n" , ptime, pt->max);
@@ -776,7 +793,7 @@ static int setup_hw_info(struct snd_pcm_runtime *runtime, struct snd_usb_substrereturn err; param_period_time_if_needed =SNDRV_PCM_HW_PARAM_PERIOD_TIME ; -if (snd_usb_get_speed (subs->dev) ==USB_SPEED_FULL ) +if (subs->speed ==USB_SPEED_FULL )/* full speed devices have fixed data packet interval */ ptmin =1000 ;if (ptmin ==1000 )
sound/usb/proc.c +2 -2
@@ -107,7 +107,7 @@ static void proc_dump_substream_formats(struct snd_usb_substream *subs, struct s }snd_iprintf (buffer,"\n" ); } -if (snd_usb_get_speed (subs->dev) !=USB_SPEED_FULL ) +if (subs->speed !=USB_SPEED_FULL )snd_iprintf (buffer," Data packet interval: %d us\n" ,125 * (1 << fp->datainterval));// snd_iprintf(buffer, " Max Packet Size = %d\n", fp->maxpacksize);
@@ -128,7 +128,7 @@ static void proc_dump_substream_status(struct snd_usb_substream *subs, struct snsnd_iprintf (buffer,"]\n" );snd_iprintf (buffer," Packet Size = %d\n" , subs->curpacksize);snd_iprintf (buffer," Momentary freq = %u Hz (%#x.%04x)\n" , -snd_usb_get_speed (subs->dev) ==USB_SPEED_FULL + subs->speed ==USB_SPEED_FULL ?get_full_speed_hz (subs->freqm) :get_high_speed_hz (subs->freqm), subs->freqm >>16 , subs->freqm &0xffff );
PATCH 9/82 ALSA: usb-audio: Use rwsem for disconnect protection
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit 34f3c89fda4fba9fe689db22253ca8db2f5e6386 upstream.
Replace mutex with rwsem for codec->shutdown protection so that concurrent accesses are allowed.
Also add the protection to snd_usb_autosuspend() and snd_usb_autoresume(), too.
---
 sound/usb/card.c     | 12 ++++++++----
 sound/usb/mixer.c    | 12 ++++++------
 sound/usb/pcm.c      | 12 ++++++------
 sound/usb/usbaudio.h |  2 +-
 4 files changed, 21 insertions(+), 17 deletions(-)
sound/usb/card.c +8 -4
@@ -336,7 +336,7 @@ static int snd_usb_audio_create(struct usb_device *dev, int idx,return -ENOMEM ; } -mutex_init (&chip->shutdown_mutex); +init_rwsem (&chip->shutdown_rwsem); chip->index = idx; chip->dev = dev; chip->card = card;
@@ -556,7 +556,7 @@ static void snd_usb_audio_disconnect(struct usb_device *dev, card = chip->card;mutex_lock (®ister_mutex); -mutex_lock (&chip->shutdown_mutex); +down_write (&chip->shutdown_rwsem); chip->shutdown =1 ; chip->num_interfaces--;if (chip->num_interfaces <=0 ) {
@@ -574,11 +574,11 @@ static void snd_usb_audio_disconnect(struct usb_device *dev,snd_usb_mixer_disconnect (p); } usb_chip[chip->index] =NULL ; -mutex_unlock (&chip->shutdown_mutex); +up_write (&chip->shutdown_rwsem);mutex_unlock (®ister_mutex);snd_card_free_when_closed (card); }else { -mutex_unlock (&chip->shutdown_mutex); +up_write (&chip->shutdown_rwsem);mutex_unlock (®ister_mutex); } }
@@ -610,16 +610,20 @@ int snd_usb_autoresume(struct snd_usb_audio *chip) {int err = -ENODEV ; +down_read (&chip->shutdown_rwsem);if (!chip->shutdown && !chip->probing) err =usb_autopm_get_interface (chip->pm_intf); +up_read (&chip->shutdown_rwsem);return err; }void snd_usb_autosuspend (struct snd_usb_audio *chip) { +down_read (&chip->shutdown_rwsem);if (!chip->shutdown && !chip->probing)usb_autopm_put_interface (chip->pm_intf); +up_read (&chip->shutdown_rwsem); }static int usb_audio_suspend (struct usb_interface *intf,pm_message_t message)
sound/usb/mixer.c +6 -6
@@ -292,7 +292,7 @@ static int get_ctl_value_v1(struct usb_mixer_elem_info *cval, int request, int v err =snd_usb_autoresume (cval->mixer->chip);if (err <0 )return -EIO ; -mutex_lock (&chip->shutdown_mutex); +down_read (&chip->shutdown_rwsem);while (timeout-- >0 ) {if (chip->shutdown)break ;
@@ -310,7 +310,7 @@ static int get_ctl_value_v1(struct usb_mixer_elem_info *cval, int request, int v err = -EINVAL ; out: -mutex_unlock (&chip->shutdown_mutex); +up_read (&chip->shutdown_rwsem);snd_usb_autosuspend (cval->mixer->chip);return err; }
@@ -337,7 +337,7 @@ static int get_ctl_value_v2(struct usb_mixer_elem_info *cval, int request, int vif (ret) goto error; -mutex_lock (&chip->shutdown_mutex); +down_read (&chip->shutdown_rwsem);if (chip->shutdown) ret = -ENODEV ;else {
@@ -346,7 +346,7 @@ static int get_ctl_value_v2(struct usb_mixer_elem_info *cval, int request, int vUSB_RECIP_INTERFACE |USB_TYPE_CLASS |USB_DIR_IN , validx, idx, buf, size); } -mutex_unlock (&chip->shutdown_mutex); +up_read (&chip->shutdown_rwsem);snd_usb_autosuspend (chip);if (ret <0 ) {
@@ -453,7 +453,7 @@ int snd_usb_mixer_set_ctl_value(struct usb_mixer_elem_info *cval, err =snd_usb_autoresume (chip);if (err <0 )return -EIO ; -mutex_lock (&chip->shutdown_mutex); +down_read (&chip->shutdown_rwsem);while (timeout-- >0 ) {if (chip->shutdown)break ;
@@ -471,7 +471,7 @@ int snd_usb_mixer_set_ctl_value(struct usb_mixer_elem_info *cval, err = -EINVAL ; out: -mutex_unlock (&chip->shutdown_mutex); +up_read (&chip->shutdown_rwsem);snd_usb_autosuspend (chip);return err; }
sound/usb/pcm.c +6 -6
@@ -376,7 +376,7 @@ static int snd_usb_hw_params(struct snd_pcm_substream *substream, subs->period_bytes !=params_period_bytes (hw_params) || subs->cur_rate != rate; -mutex_lock (&subs->stream->chip->shutdown_mutex); +down_read (&subs->stream->chip->shutdown_rwsem);if (subs->stream->chip->shutdown) { ret = -ENODEV ; goto unlock;
@@ -406,7 +406,7 @@ static int snd_usb_hw_params(struct snd_pcm_substream *substream, } unlock: -mutex_unlock (&subs->stream->chip->shutdown_mutex); +up_read (&subs->stream->chip->shutdown_rwsem);return ret; }
@@ -422,9 +422,9 @@ static int snd_usb_hw_free(struct snd_pcm_substream *substream) subs->cur_audiofmt =NULL ; subs->cur_rate =0 ; subs->period_bytes =0 ; -mutex_lock (&subs->stream->chip->shutdown_mutex); +down_read (&subs->stream->chip->shutdown_rwsem);snd_usb_release_substream_urbs (subs,0 ); -mutex_unlock (&subs->stream->chip->shutdown_mutex); +up_read (&subs->stream->chip->shutdown_rwsem);return snd_pcm_lib_free_vmalloc_buffer (substream); }
@@ -444,7 +444,7 @@ static int snd_usb_pcm_prepare(struct snd_pcm_substream *substream)return -ENXIO ; } -mutex_lock (&subs->stream->chip->shutdown_mutex); +down_read (&subs->stream->chip->shutdown_rwsem);if (subs->stream->chip->shutdown) { ret = -ENODEV ; goto unlock;
@@ -463,7 +463,7 @@ static int snd_usb_pcm_prepare(struct snd_pcm_substream *substream) ret =snd_usb_substream_prepare (subs, runtime); unlock: -mutex_unlock (&subs->stream->chip->shutdown_mutex); +up_read (&subs->stream->chip->shutdown_rwsem);return ret; }
sound/usb/usbaudio.h +1 -1
@@ -36,7 +36,7 @@ struct snd_usb_audio {struct snd_card *card;struct usb_interface *pm_intf;u32 usb_id; -struct mutex shutdown_mutex; +struct rw_semaphore shutdown_rwsem; unsigned int shutdown:1; unsigned int probing:1; unsigned int autosuspended:1;
PATCH 10/82 ALSA: usb-audio: Fix races at disconnection in mixer_quirks.c
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit 888ea7d5ac6815ba16b3b3a20f665a92c7af6724 upstream.
Similar like the previous commit, cover with chip->shutdown_rwsem and chip->shutdown checks.
---
 sound/usb/mixer_quirks.c | 37 +++++++++++++++++++++++++++++++++----
 1 file changed, 33 insertions(+), 4 deletions(-)
sound/usb/mixer_quirks.c +33 -4
@@ -186,6 +186,11 @@ static int snd_audigy2nx_led_put(struct snd_kcontrol *kcontrol, struct snd_ctl_eif (value >1 )return -EINVAL ; changed = value != mixer->audigy2nx_leds[index]; +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) { + err = -ENODEV ; + goto out; + }if (mixer->chip->usb_id ==USB_ID (0x041e ,0x3042 )) err = snd_usb_ctl_msg(mixer->chip->dev, usb_sndctrlpipe(mixer->chip->dev, 0), 0x24,
@@ -202,6 +207,8 @@ static int snd_audigy2nx_led_put(struct snd_kcontrol *kcontrol, struct snd_ctl_eusb_sndctrlpipe (mixer->chip->dev,0 ),0x24 ,USB_DIR_OUT |USB_TYPE_VENDOR |USB_RECIP_OTHER , value, index + 2, NULL, 0); + out: +up_read (&mixer->chip->shutdown_rwsem);if (err <0 )return err; mixer->audigy2nx_leds[index] = value;
@@ -295,11 +302,16 @@ static void snd_audigy2nx_proc_read(struct snd_info_entry *entry,for (i =0 ; jacks[i].name; ++i) {snd_iprintf (buffer,"%s: " , jacks[i].name); - err =snd_usb_ctl_msg (mixer->chip->dev, +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) + err =0 ; +else + err =snd_usb_ctl_msg (mixer->chip->dev,usb_rcvctrlpipe (mixer->chip->dev,0 ),UAC_GET_MEM ,USB_DIR_IN |USB_TYPE_CLASS |USB_RECIP_INTERFACE ,0 , jacks[i].unitid <<8 , buf,3 ); +up_read (&mixer->chip->shutdown_rwsem);if (err ==3 && (buf[0 ] ==3 || buf[0 ] ==6 ))snd_iprintf (buffer,"%02x %02x\n" , buf[1 ], buf[2 ]);else
@@ -329,10 +341,15 @@ static int snd_xonar_u1_switch_put(struct snd_kcontrol *kcontrol,else new_status = old_status & ~0x02 ; changed = new_status != old_status; - err =snd_usb_ctl_msg (mixer->chip->dev, +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) + err = -ENODEV ; +else + err =snd_usb_ctl_msg (mixer->chip->dev,usb_sndctrlpipe (mixer->chip->dev,0 ),0x08 ,USB_DIR_OUT |USB_TYPE_VENDOR |USB_RECIP_OTHER ,50 ,0 , &new_status,1 ); +up_read (&mixer->chip->shutdown_rwsem);if (err <0 )return err; mixer->xonar_u1_status = new_status;
@@ -371,11 +388,17 @@ static int snd_nativeinstruments_control_get(struct snd_kcontrol *kcontrol,u8 bRequest = (kcontrol->private_value >>16 ) &0xff ;u16 wIndex = kcontrol->private_value &0xffff ;u8 tmp; +int ret; -int ret =usb_control_msg (dev,usb_rcvctrlpipe (dev,0 ), bRequest, +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) + ret = -ENODEV ; +else + ret =usb_control_msg (dev,usb_rcvctrlpipe (dev,0 ), bRequest,USB_TYPE_VENDOR |USB_RECIP_DEVICE |USB_DIR_IN ,0 ,cpu_to_le16 (wIndex), &tmp,sizeof (tmp),1000 ); +up_read (&mixer->chip->shutdown_rwsem);if (ret <0 ) { snd_printk(KERN_ERR
@@ -396,11 +419,17 @@ static int snd_nativeinstruments_control_put(struct snd_kcontrol *kcontrol,u8 bRequest = (kcontrol->private_value >>16 ) &0xff ;u16 wIndex = kcontrol->private_value &0xffff ;u16 wValue = ucontrol->value.integer.value[0 ]; +int ret; -int ret =usb_control_msg (dev,usb_sndctrlpipe (dev,0 ), bRequest, +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) + ret = -ENODEV ; +else + ret =usb_control_msg (dev,usb_sndctrlpipe (dev,0 ), bRequest,USB_TYPE_VENDOR |USB_RECIP_DEVICE |USB_DIR_OUT ,cpu_to_le16 (wValue),cpu_to_le16 (wIndex),NULL ,0 ,1000 ); +up_read (&mixer->chip->shutdown_rwsem);if (ret <0 ) { snd_printk(KERN_ERR
PATCH 11/82 ALSA: Add a reference counter to card instance
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit a0830dbd4e42b38aefdf3fb61ba5019a1a99ea85 upstream.
For more strict protection for wild disconnections, a refcount is introduced to the card instance, and let it up/down when an object is referred via snd_lookup_*() in the open ops.
The free-after-last-close check is also changed to check this refcount instead of the empty list, too.
---
 include/sound/core.h       |  3 +++
 sound/core/control.c       |  3 +++
 sound/core/hwdep.c         |  5 ++++-
 sound/core/init.c          | 50 +++++++++++++++++++++++++++-------------------
 sound/core/oss/mixer_oss.c | 10 ++++++++--
 sound/core/oss/pcm_oss.c   |  2 ++
 sound/core/pcm_native.c    |  9 +++++++--
 sound/core/rawmidi.c       |  6 +++++-
 sound/core/sound.c         | 11 ++++++++--
 sound/core/sound_oss.c     | 10 ++++++++--
 10 files changed, 79 insertions(+), 30 deletions(-)
include/sound/core.h +3 -0
@@ -132,6 +132,7 @@ struct snd_card {int shutdown;/* this card is going down */ int free_on_last_close;/* free in context of file_release */ wait_queue_head_t shutdown_sleep; +atomic_t refcount;/* refcount for disconnection */ struct device *dev;/* device assigned to this card */ struct device *card_dev;/* cardX object for sysfs */
@@ -189,6 +190,7 @@ struct snd_minor {const struct file_operations *f_ops;/* file operations */ void *private_data;/* private data for f_ops->open */ struct device *dev;/* device for sysfs */ +struct snd_card *card_ptr;/* assigned card instance */ };/* return a device pointer linked to each sound device as a parent */
@@ -295,6 +297,7 @@ int snd_card_info_done(void);int snd_component_add (struct snd_card *card,const char *component);int snd_card_file_add (struct snd_card *card,struct file *file);int snd_card_file_remove (struct snd_card *card,struct file *file); +void snd_card_unref (struct snd_card *card);#define snd_card_set_dev (card, devptr) ((card)->dev = (devptr))
sound/core/control.c +3 -0
@@ -86,6 +86,7 @@ static int snd_ctl_open(struct inode *inode, struct file *file)write_lock_irqsave (&card->ctl_files_rwlock, flags);list_add_tail (&ctl->list, &card->ctl_files);write_unlock_irqrestore (&card->ctl_files_rwlock, flags); +snd_card_unref (card);return 0 ; __error:
@@ -93,6 +94,8 @@ static int snd_ctl_open(struct inode *inode, struct file *file) __error2:snd_card_file_remove (card, file); __error1: +if (card) +snd_card_unref (card);return err; }
sound/core/hwdep.c +4 -1
@@ -100,8 +100,10 @@ static int snd_hwdep_open(struct inode *inode, struct file * file)if (hw ==NULL )return -ENODEV ; -if (!try_module_get (hw->card->module)) +if (!try_module_get (hw->card->module)) { +snd_card_unref (hw->card);return -EFAULT ; + }init_waitqueue_entry (&wait, current);add_wait_queue (&hw->open_wait, &wait);
@@ -148,6 +150,7 @@ static int snd_hwdep_open(struct inode *inode, struct file * file)mutex_unlock (&hw->open_mutex);if (err <0 )module_put (hw->card->module); +snd_card_unref (hw->card);return err; }
sound/core/init.c +30 -20
96 lines not on this page · raw message
sound/core/oss/mixer_oss.c +8 -2
@@ -52,14 +52,19 @@ static int snd_mixer_oss_open(struct inode *inode, struct file *file) SNDRV_OSS_DEVICE_TYPE_MIXER);if (card ==NULL )return -ENODEV ; -if (card->mixer_oss ==NULL ) +if (card->mixer_oss ==NULL ) { +snd_card_unref (card);return -ENODEV ; + } err =snd_card_file_add (card, file); -if (err <0 ) +if (err <0 ) { +snd_card_unref (card);return err; + } fmixer =kzalloc (sizeof (*fmixer),GFP_KERNEL );if (fmixer ==NULL ) {snd_card_file_remove (card, file); +snd_card_unref (card);return -ENOMEM ; } fmixer->card = card;
@@ -68,6 +73,7 @@ static int snd_mixer_oss_open(struct inode *inode, struct file *file)if (!try_module_get (card->module)) {kfree (fmixer);snd_card_file_remove (card, file); +snd_card_unref (card);return -EFAULT ; }return 0 ;
sound/core/oss/pcm_oss.c +2 -0
@@ -2457,6 +2457,8 @@ static int snd_pcm_oss_open(struct inode *inode, struct file *file) __error2:snd_card_file_remove (pcm->card, file); __error1: +if (pcm) +snd_card_unref (pcm->card);return err; }
sound/core/pcm_native.c +7 -2
@@ -1628,6 +1628,7 @@ static int snd_pcm_link(struct snd_pcm_substream *substream, int fd) _end:write_unlock_irq (&snd_pcm_link_rwlock);up_write (&snd_pcm_link_rwsem); +snd_card_unref (substream1->pcm->card);fput (file);return res; }
@@ -2100,7 +2101,9 @@ static int snd_pcm_playback_open(struct inode *inode, struct file *file)return err; pcm =snd_lookup_minor_data (iminor (inode),SNDRV_DEVICE_TYPE_PCM_PLAYBACK ); -return snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_PLAYBACK ); + err =snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_PLAYBACK ); +snd_card_unref (pcm->card); +return err; }static int snd_pcm_capture_open (struct inode *inode,struct file *file)
@@ -2111,7 +2114,9 @@ static int snd_pcm_capture_open(struct inode *inode, struct file *file)return err; pcm =snd_lookup_minor_data (iminor (inode),SNDRV_DEVICE_TYPE_PCM_CAPTURE ); -return snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_CAPTURE ); + err =snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_CAPTURE ); +snd_card_unref (pcm->card); +return err; }static int snd_pcm_open (struct file *file,struct snd_pcm *pcm,int stream)
sound/core/rawmidi.c +5 -1
@@ -379,8 +379,10 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file)if (rmidi ==NULL )return -ENODEV ; -if (!try_module_get (rmidi->card->module)) +if (!try_module_get (rmidi->card->module)) { +snd_card_unref (rmidi->card);return -ENXIO ; + }mutex_lock (&rmidi->open_mutex); card = rmidi->card;
@@ -440,6 +442,7 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file)#endif file->private_data = rawmidi_file;mutex_unlock (&rmidi->open_mutex); +snd_card_unref (rmidi->card);return 0 ; __error:
@@ -447,6 +450,7 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file) __error_card:mutex_unlock (&rmidi->open_mutex);module_put (rmidi->card->module); +snd_card_unref (rmidi->card);return err; }
sound/core/sound.c +9 -2
@@ -99,6 +99,10 @@ static void snd_request_other(int minor)* * Checks that a minor device with the specified type is registered, and returns * its user data pointer. +* +* This function increments the reference counter of the card instance +* if an associated instance with the given minor number and type is found. +* The caller must call snd_card_unref() appropriately later. */ void *snd_lookup_minor_data (unsigned int minor,int type) {
@@ -109,9 +113,11 @@ void *snd_lookup_minor_data(unsigned int minor, int type)return NULL ;mutex_lock (&sound_mutex); mreg = snd_minors[minor]; -if (mreg && mreg->type == type) +if (mreg && mreg->type == type) { private_data = mreg->private_data; -else +if (mreg->card_ptr) +atomic_inc (&mreg->card_ptr->refcount); + }else private_data =NULL ;mutex_unlock (&sound_mutex);return private_data;
@@ -275,6 +281,7 @@ int snd_register_device_for_dev(int type, struct snd_card *card, int dev, preg->device = dev; preg->f_ops = f_ops; preg->private_data = private_data; + preg->card_ptr = card;mutex_lock (&sound_mutex);#ifdef CONFIG_SND_DYNAMIC_MINORS minor =snd_find_free_minor (type);
sound/core/sound_oss.c +8 -2
@@ -40,6 +40,9 @@static struct snd_minor *snd_oss_minors[SNDRV_OSS_MINORS ];static DEFINE_MUTEX (sound_oss_mutex); +/* NOTE: This function increments the refcount of the associated card like +* snd_lookup_minor_data(); the caller must call snd_card_unref() appropriately +*/ void *snd_lookup_oss_minor_data (unsigned int minor,int type) {struct snd_minor *mreg;
@@ -49,9 +52,11 @@ void *snd_lookup_oss_minor_data(unsigned int minor, int type)return NULL ;mutex_lock (&sound_oss_mutex); mreg = snd_oss_minors[minor]; -if (mreg && mreg->type == type) +if (mreg && mreg->type == type) { private_data = mreg->private_data; -else +if (mreg->card_ptr) +atomic_inc (&mreg->card_ptr->refcount); + }else private_data =NULL ;mutex_unlock (&sound_oss_mutex);return private_data;
@@ -123,6 +128,7 @@ int snd_register_oss_device(int type, struct snd_card *card, int dev, preg->device = dev; preg->f_ops = f_ops; preg->private_data = private_data; + preg->card_ptr = card;mutex_lock (&sound_oss_mutex); snd_oss_minors[minor] = preg; minor_unit =SNDRV_MINOR_OSS_DEVICE (minor);
PATCH 12/82 ALSA: Avoid endless sleep after disconnect
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit 0914f7961babbf28aaa2f19b453951fb4841c03f upstream.
When disconnect callback is called, each component should wake up sleepers and check card->shutdown flag for avoiding the endless sleep blocking the proper resource release.
---
 sound/core/control.c     |  2 ++
 sound/core/hwdep.c       |  7 +++++++
 sound/core/oss/pcm_oss.c |  4 ++++
 sound/core/pcm.c         |  6 +++++-
 sound/core/pcm_native.c  |  8 ++++++++
 sound/core/rawmidi.c     | 20 ++++++++++++++++++++
 6 files changed, 46 insertions(+), 1 deletion(-)
sound/core/control.c +2 -0
@@ -1436,6 +1436,8 @@ static ssize_t snd_ctl_read(struct file *file, char __user *buffer,spin_unlock_irq (&ctl->read_lock);schedule ();remove_wait_queue (&ctl->change_sleep, &wait); +if (ctl->card->shutdown) +return -ENODEV ;if (signal_pending (current))return -ERESTARTSYS ;spin_lock_irq (&ctl->read_lock);
sound/core/hwdep.c +7 -0
@@ -131,6 +131,10 @@ static int snd_hwdep_open(struct inode *inode, struct file * file)mutex_unlock (&hw->open_mutex);schedule ();mutex_lock (&hw->open_mutex); +if (hw->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
@@ -462,12 +466,15 @@ static int snd_hwdep_dev_disconnect(struct snd_device *device)mutex_unlock (®ister_mutex);return -EINVAL ; } +mutex_lock (&hwdep->open_mutex); +wake_up (&hwdep->open_wait);#ifdef CONFIG_SND_OSSEMUL if (hwdep->ossreg)snd_unregister_oss_device (hwdep->oss_type, hwdep->card, hwdep->device);#endif snd_unregister_device (SNDRV_DEVICE_TYPE_HWDEP , hwdep->card, hwdep->device);list_del_init (&hwdep->list); +mutex_unlock (&hwdep->open_mutex);mutex_unlock (®ister_mutex);return 0 ; }
sound/core/oss/pcm_oss.c +4 -0
@@ -2441,6 +2441,10 @@ static int snd_pcm_oss_open(struct inode *inode, struct file *file)mutex_unlock (&pcm->open_mutex);schedule ();mutex_lock (&pcm->open_mutex); +if (pcm->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
sound/core/pcm.c +5 -1
@@ -1047,12 +1047,16 @@ static int snd_pcm_dev_disconnect(struct snd_device *device) goto unlock;mutex_lock (&pcm->open_mutex); +wake_up (&pcm->open_wait);list_del_init (&pcm->list);for (cidx =0 ; cidx <2 ; cidx++)for (substream = pcm->streams[cidx].substream; substream; substream = substream->next) {snd_pcm_stream_lock_irq (substream); -if (substream->runtime) +if (substream->runtime) { substream->runtime->status->state =SNDRV_PCM_STATE_DISCONNECTED ; +wake_up (&substream->runtime->sleep); +wake_up (&substream->runtime->tsleep); + }snd_pcm_stream_unlock_irq (substream); }list_for_each_entry (notify, &snd_pcm_notify_list, list) {
sound/core/pcm_native.c +8 -0
@@ -1508,6 +1508,10 @@ static int snd_pcm_drain(struct snd_pcm_substream *substream,down_read (&snd_pcm_link_rwsem);snd_pcm_stream_lock_irq (substream);remove_wait_queue (&to_check->sleep, &wait); +if (card->shutdown) { + result = -ENODEV ; +break ; + }if (tout ==0 ) {if (substream->runtime->status->state ==SNDRV_PCM_STATE_SUSPENDED ) result = -ESTRPIPE ;
@@ -2153,6 +2157,10 @@ static int snd_pcm_open(struct file *file, struct snd_pcm *pcm, int stream)mutex_unlock (&pcm->open_mutex);schedule ();mutex_lock (&pcm->open_mutex); +if (pcm->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
sound/core/rawmidi.c +20 -0
@@ -424,6 +424,10 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file)mutex_unlock (&rmidi->open_mutex);schedule ();mutex_lock (&rmidi->open_mutex); +if (rmidi->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
@@ -995,6 +999,8 @@ static ssize_t snd_rawmidi_read(struct file *file, char __user *buf, size_t counspin_unlock_irq (&runtime->lock);schedule ();remove_wait_queue (&runtime->sleep, &wait); +if (rfile->rmidi->card->shutdown) +return -ENODEV ;if (signal_pending (current))return result >0 ? result : -ERESTARTSYS ;if (!runtime->avail)
@@ -1238,6 +1244,8 @@ static ssize_t snd_rawmidi_write(struct file *file, const char __user *buf,spin_unlock_irq (&runtime->lock); timeout =schedule_timeout (30 *HZ );remove_wait_queue (&runtime->sleep, &wait); +if (rfile->rmidi->card->shutdown) +return -ENODEV ;if (signal_pending (current))return result >0 ? result : -ERESTARTSYS ;if (!runtime->avail && !timeout)
@@ -1613,9 +1621,20 @@ static int snd_rawmidi_dev_register(struct snd_device *device)static int snd_rawmidi_dev_disconnect (struct snd_device *device) {struct snd_rawmidi *rmidi = device->device_data; +int dir;mutex_lock (®ister_mutex); +mutex_lock (&rmidi->open_mutex); +wake_up (&rmidi->open_wait);list_del_init (&rmidi->list); +for (dir =0 ; dir <2 ; dir++) { +struct snd_rawmidi_substream *s; +list_for_each_entry (s, &rmidi->streams[dir].substreams, list) { +if (s->runtime) +wake_up (&s->runtime->sleep); + } + } +#ifdef CONFIG_SND_OSSEMUL if (rmidi->ossreg) {if ((int )rmidi->device == midi_map[rmidi->card->number]) {
@@ -1630,6 +1649,7 @@ static int snd_rawmidi_dev_disconnect(struct snd_device *device) }#endif /* CONFIG_SND_OSSEMUL */ snd_unregister_device (SNDRV_DEVICE_TYPE_RAWMIDI , rmidi->card, rmidi->device); +mutex_unlock (&rmidi->open_mutex);mutex_unlock (®ister_mutex);return 0 ; }
PATCH 13/82 drm/radeon: fix typo in evergreen_mc_resume()
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Alex Deucher <[email protected]>
commit 695ddeb457584a602f2ba117d08ce37cf6ec1589 upstream.
Add missing index that may have led us to enabling more crtcs than necessary.
May also fix:
https://bugs.freedesktop.org/show_bug.cgi?id=56139
---
 drivers/gpu/drm/radeon/evergreen.c |    2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/gpu/drm/radeon/evergreen.c +1 -1
@@ -1164,7 +1164,7 @@ void evergreen_mc_resume(struct radeon_dWREG32 (BIF_FB_EN ,FB_READ_EN |FB_WRITE_EN );for (i =0 ; i < rdev->num_crtc; i++) { -if (save->crtc_enabled) { +if (save->crtc_enabled[i]) { tmp =RREG32 (EVERGREEN_CRTC_CONTROL + crtc_offsets[i]); tmp &= ~EVERGREEN_CRTC_DISP_READ_REQUEST_DISABLE ;WREG32 (EVERGREEN_CRTC_CONTROL + crtc_offsets[i], tmp);
PATCH 14/82 USB: mos7840: remove unused variable
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Johan Hovold <[email protected]>
Fix warning about unused variable introduced by commit e681b66f2e19fa ("USB: mos7840: remove invalid disconnect handling") upstream.
A subsequent fix which removed the disconnect function got rid of the warning but that one was only backported to v3.6.
---
 drivers/usb/serial/mos7840.c | 1 -
 1 file changed, 1 deletion(-)
drivers/usb/serial/mos7840.c +0 -1
@@ -2581,7 +2581,6 @@ error:static void mos7840_disconnect (struct usb_serial *serial) {int i; -unsigned long flags;struct moschip_port *mos7840_port;dbg ("%s" ," disconnect :entering.........." );
PATCH 15/82 rtnetlink: Fix problem with buffer allocation
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Greg Rose <[email protected]>
commit 115c9b81928360d769a76c632bae62d15206a94a upstream.
Implement a new netlink attribute type IFLA_EXT_MASK. The mask is a 32 bit value that can be used to indicate to the kernel that certain extended ifinfo values are requested by the user application. At this time the only mask value defined is RTEXT_FILTER_VF to indicate that the user wants the ifinfo dump to send information about the VFs belonging to the interface.
This patch fixes a bug in which certain applications do not have large enough buffers to accommodate the extra information returned by the kernel with large numbers of SR-IOV virtual functions. Those applications will not send the new netlink attribute with the interface info dump request netlink messages so they will not get unexpectedly large request buffers returned by the kernel.
Modifies the rtnl_calcit function to traverse the list of net devices and compute the minimum buffer size that can hold the info dumps of all matching devices based upon the filter passed in via the new netlink attribute filter mask. If no filter mask is sent then the buffer allocation defaults to NLMSG_GOODSIZE.
With this change it is possible to add yet to be defined netlink attributes to the dump request which should make it fairly extensible in the future.
[bwh: Backported to 3.2: drop the change in do_setlink() that reverts
commit f18da14565819ba43b8321237e2426a2914cc2ef, which we never applied]
---
 include/linux/if_link.h   |    1 +
 include/linux/rtnetlink.h |    3 ++
 include/net/rtnetlink.h   |    2 +-
 net/core/rtnetlink.c      |   78 +++++++++++++++++++++++++++++++++------------
 4 files changed, 62 insertions(+), 22 deletions(-)
include/linux/if_link.h +1 -0
@@ -137,6 +137,7 @@ enum {IFLA_AF_SPEC ,IFLA_GROUP ,/* Group the device belongs to */ IFLA_NET_NS_FD , +IFLA_EXT_MASK ,/* Extended info mask, VFs, etc */ __IFLA_MAX };
include/linux/rtnetlink.h +3 -0
@@ -602,6 +602,9 @@ struct tcamsg {#define TCA_ACT_TAB 1/* attr type must be >=1 */ #define TCAA_MAX 1 +/* New extended info filters for IFLA_EXT_MASK */ +#define RTEXT_FILTER_VF (1 << 0) +/* End of information exported to user level */ #ifdef __KERNEL__
include/net/rtnetlink.h +1 -1
@@ -6,7 +6,7 @@typedef int (*rtnl_doit_func )(struct sk_buff *,struct nlmsghdr *,void *);typedef int (*rtnl_dumpit_func )(struct sk_buff *,struct netlink_callback *); -typedef u16 (*rtnl_calcit_func )(struct sk_buff *); +typedef u16 (*rtnl_calcit_func )(struct sk_buff *,struct nlmsghdr *); extern int __rtnl_register(int protocol, int msgtype, rtnl_doit_func, rtnl_dumpit_func,
net/core/rtnetlink.c +57 -19
183 lines not on this page · raw message
PATCH 16/82 rtnetlink: fix rtnl_calcit() and rtnl_dump_ifinfo()
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Eric Dumazet <[email protected]>
commit a4b64fbe482c7766f7925f03067fc637716bfa3f upstream.
nlmsg_parse() might return an error, so test its return value before potential random memory accesses.
Errors introduced in commit 115c9b81928 (rtnetlink: Fix problem with buffer allocation)
---
 net/core/rtnetlink.c |   18 ++++++++++--------
 1 file changed, 10 insertions(+), 8 deletions(-)
net/core/rtnetlink.c +10 -8
@@ -1060,11 +1060,12 @@ static int rtnl_dump_ifinfo(struct sk_buff *skb, struct netlink_callback *cb)rcu_read_lock (); cb->seq = net->dev_base_seq; -nlmsg_parse (cb->nlh,sizeof (struct rtgenmsg ), tb,IFLA_MAX , - ifla_policy); +if (nlmsg_parse (cb->nlh,sizeof (struct rtgenmsg ), tb,IFLA_MAX , + ifla_policy) >=0 ) { -if (tb[IFLA_EXT_MASK ]) - ext_filter_mask =nla_get_u32 (tb[IFLA_EXT_MASK ]); +if (tb[IFLA_EXT_MASK ]) + ext_filter_mask =nla_get_u32 (tb[IFLA_EXT_MASK ]); + }for (h = s_h; h <NETDEV_HASHENTRIES ; h++, s_idx =0 ) { idx =0 ;
@@ -1900,10 +1901,11 @@ static u16 rtnl_calcit(struct sk_buff *skb, struct nlmsghdr *nlh)u32 ext_filter_mask =0 ;u16 min_ifinfo_dump_size =0 ; -nlmsg_parse (nlh,sizeof (struct rtgenmsg ), tb,IFLA_MAX , ifla_policy); - -if (tb[IFLA_EXT_MASK ]) - ext_filter_mask =nla_get_u32 (tb[IFLA_EXT_MASK ]); +if (nlmsg_parse (nlh,sizeof (struct rtgenmsg ), tb,IFLA_MAX , + ifla_policy) >=0 ) { +if (tb[IFLA_EXT_MASK ]) + ext_filter_mask =nla_get_u32 (tb[IFLA_EXT_MASK ]); + }if (!ext_filter_mask)return NLMSG_GOODSIZE ;
PATCH 17/82 gpio-timberdale: fix a potential wrapping issue
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Dan Carpenter <[email protected]>
commit d79550a7bc35c16476ebdc27c78378d8093390ec upstream.
->last_ier is an unsigned long but the high bits can't be used int the original code because the shift wraps.
---
 drivers/gpio/gpio-timberdale.c |    4 ++--
 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/gpio/gpio-timberdale.c +2 -2
@@ -116,7 +116,7 @@ static void timbgpio_irq_disable(struct irq_data *d)unsigned long flags;spin_lock_irqsave (&tgpio->lock, flags); - tgpio->last_ier &= ~(1 << offset); + tgpio->last_ier &= ~(1UL << offset);iowrite32 (tgpio->last_ier, tgpio->membase +TGPIO_IER );spin_unlock_irqrestore (&tgpio->lock, flags); }
@@ -128,7 +128,7 @@ static void timbgpio_irq_enable(struct irq_data *d)unsigned long flags;spin_lock_irqsave (&tgpio->lock, flags); - tgpio->last_ier |=1 << offset; + tgpio->last_ier |=1UL << offset;iowrite32 (tgpio->last_ier, tgpio->membase +TGPIO_IER );spin_unlock_irqrestore (&tgpio->lock, flags); }
PATCH 18/82 cfg80211: fix antenna gain handling
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Felix Fietkau <[email protected]>
commit c4a9fafc77a5318f5ed26c509bbcddf03e18c201 upstream.
No driver initializes chan->max_antenna_gain to something sensible, and the only place where it is being used right now is inside ath9k. This leads to ath9k potentially using less tx power than it can use, which can decrease performance/range in some rare cases.
Rather than going through every single driver, this patch initializes chan->orig_mag in wiphy_register(), ignoring whatever value the driver left in there. If a driver for some reason wishes to limit it independent from regulatory rulesets, it can do so internally.
---
 net/wireless/core.c |    3 +--
 1 file changed, 1 insertion(+), 2 deletions(-)
net/wireless/core.c +1 -2
@@ -526,8 +526,7 @@ int wiphy_register(struct wiphy *wiphy)for (i =0 ; i < sband->n_channels; i++) { sband->channels[i].orig_flags = sband->channels[i].flags; - sband->channels[i].orig_mag = - sband->channels[i].max_antenna_gain; + sband->channels[i].orig_mag =INT_MAX ; sband->channels[i].orig_mpwr = sband->channels[i].max_power; sband->channels[i].band = band;
PATCH 19/82 drm/i915: fix overlay on i830M
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Daniel Vetter <[email protected]>
commit a9193983f4f292a82a00c72971c17ec0ee8c6c15 upstream.
The overlay on the i830M has a peculiar failure mode: It works the first time around after boot-up, but consistenly hangs the second time it's used.
Chris Wilson has dug out a nice errata:
"1.5.12 Clock Gating Disable for Display Register
Address Offset: 06200h–06203h
"Bit 3
Ovrunit Clock Gating Disable.
0 = Clock gating controlled by unit enabling logic
1 = Disable clock gating function
DevALM Errata ALM049: Overlay Clock Gating Must be Disabled: Overlay & L2 Cache clock gating must be disabled in order to prevent device hangs when turning off overlay.SW must turn off Ovrunit clock gating (6200h) and L2 Cache clock gating (C8h)."
Now I've nowhere found that 0xc8 register and hence couldn't apply the l2 cache workaround. But I've remembered that part of the magic that the OVERLAY_ON/OFF commands are supposed to do is to rearrange cache allocations so that the overlay scaler has some scratch space.
And while pondering how that could explain the hang the 2nd time we enable the overlay, I've remembered that the old ums overlay code did _not_ issue the OVERLAY_OFF cmd.
And indeed, disabling the OFF cmd results in the overlay working flawlessly, so I guess we can workaround the lack of the above workaround by simply never disabling the overlay engine once it's enabled.
Note that we have the first part of the above w/a already implemented in i830_init_clock_gating - leave that as-is to avoid surprises.
v2: Add a comment in the code.
Bugzilla: https://bugs.freedesktop.org/show_bug.cgi?id=47827
[bwh: Backported to 3.2:
- Adjust context
- s/intel_ring_emit(ring, /OUT_RING(/]
---
 drivers/gpu/drm/i915/intel_overlay.c |   14 +++++++++++---
 1 file changed, 11 insertions(+), 3 deletions(-)
drivers/gpu/drm/i915/intel_overlay.c +11 -3
@@ -428,9 +428,17 @@ static int intel_overlay_off(struct inteOUT_RING (flip_addr);OUT_RING (MI_WAIT_FOR_EVENT |MI_WAIT_FOR_OVERLAY_FLIP );/* turn overlay off */ -OUT_RING (MI_OVERLAY_FLIP |MI_OVERLAY_OFF ); -OUT_RING (flip_addr); -OUT_RING (MI_WAIT_FOR_EVENT |MI_WAIT_FOR_OVERLAY_FLIP ); +if (IS_I830 (dev)) { +/* Workaround: Don't disable the overlay fully, since otherwise +* it dies on the next OVERLAY_ON cmd. */ +OUT_RING (MI_NOOP ); +OUT_RING (MI_NOOP ); +OUT_RING (MI_NOOP ); + }else { +OUT_RING (MI_OVERLAY_FLIP |MI_OVERLAY_OFF ); +OUT_RING (flip_addr); +OUT_RING (MI_WAIT_FOR_EVENT |MI_WAIT_FOR_OVERLAY_FLIP ); + }ADVANCE_LP_RING (); return intel_overlay_do_wait_request(overlay, request,
PATCH 20/82 drm/i915: fixup infoframe support for sdvo
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Daniel Vetter <[email protected]>
commit 81014b9d0b55fb0b48f26cd2a943359750d532db upstream.
At least the worst offenders:
- SDVO specifies that the encoder should compute the ecc. Testing also shows that we must not send the ecc field, so copy the dip_infoframe struct to a temporay place and avoid the ecc field. This way the avi infoframe is exactly 17 bytes long, which agrees with what the spec mandates as a minimal storage capacity (with the ecc field it would be 18 bytes).
- Only 17 when sending the avi infoframe. The SDVO spec explicitly says that sending more data than what the device announces results in undefined behaviour.
- Add __attribute__((packed)) to the avi and spd infoframes, for otherwise they're wrongly aligned. Noticed because the avi infoframe ended up being 18 bytes large instead of 17. We haven't noticed this yet because we don't use the uint16_t fields yet (which are the only ones that would be wrongly aligned).
This regression has been introduce by
3c17fe4b8f40a112a85758a9ab2aebf772bdd647 is the first bad commit commit 3c17fe4b8f40a112a85758a9ab2aebf772bdd647
Author: David Härdeman <[email protected]>
Date:   Fri Sep 24 21:44:32 2010 +0200
i915: enable AVI infoframe for intel_hdmi.c [v4]
Patch tested on my g33 with a sdvo hdmi adaptor.
Bugzilla: https://bugzilla.kernel.org/show_bug.cgi?id=25732
---
 drivers/gpu/drm/i915/intel_drv.h  |    4 ++--
 drivers/gpu/drm/i915/intel_sdvo.c |   11 +++++++++--
 2 files changed, 11 insertions(+), 4 deletions(-)
drivers/gpu/drm/i915/intel_drv.h +2 -2
@@ -280,12 +280,12 @@ struct dip_infoframe {uint16_t bottom_bar_start;uint16_t left_bar_end;uint16_t right_bar_start; - } avi; + } __attribute__ ((packed)) avi;struct {uint8_t vn[8 ];uint8_t pd[16 ];uint8_t sdi; - } spd; + } __attribute__ ((packed)) spd;uint8_t payload[27 ]; } __attribute__ ((packed)) body; } __attribute__((packed));
drivers/gpu/drm/i915/intel_sdvo.c +9 -2
@@ -887,17 +887,24 @@ static bool intel_sdvo_set_avi_infoframe(struct intel_sdvo *intel_sdvo) };uint8_t tx_rate =SDVO_HBUF_TX_VSYNC ;uint8_t set_buf_index[2 ] = {1 ,0 }; -uint64_t *data = (uint64_t *)&avi_if; +uint8_t sdvo_data[4 +sizeof (avi_if.body.avi)]; +uint64_t *data = (uint64_t *)sdvo_data;unsigned i;intel_dip_infoframe_csum (&avi_if); +/* sdvo spec says that the ecc is handled by the hw, and it looks like +* we must not send the ecc field, either. */ +memcpy (sdvo_data, &avi_if,3 ); + sdvo_data[3 ] = avi_if.checksum; +memcpy (&sdvo_data[4 ], &avi_if.body,sizeof (avi_if.body.avi)); +if (!intel_sdvo_set_value (intel_sdvo,SDVO_CMD_SET_HBUF_INDEX , set_buf_index,2 ))return false; -for (i =0 ; i <sizeof (avi_if); i +=8 ) { +for (i =0 ; i <sizeof (sdvo_data); i +=8 ) {if (!intel_sdvo_set_value (intel_sdvo,SDVO_CMD_SET_HBUF_DATA , data,8 ))
PATCH 21/82 drm/i915: clear the entire sdvo infoframe buffer
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Daniel Vetter <[email protected]>
commit b6e0e543f75729f207b9c72b0162ae61170635b2 upstream.
Like in the case of native hdmi, which is fixed already in
commit adf00b26d18e1b3570451296e03bcb20e4798cdd
Author: Paulo Zanoni <[email protected]>
Date:   Tue Sep 25 13:23:34 2012 -0300
drm/i915: make sure we write all the DIP data bytes
we need to clear the entire sdvo buffer to avoid upsetting the display.
Since infoframe buffer writing is now a bit more elaborate, extract it into it's own function. This will be useful if we ever get around to properly update the ELD for sdvo. Also #define proper names for the two buffer indexes with fixed usage.
v2: Cite the right commit above, spotted by Paulo Zanoni.
v3: I'm too stupid to paste the right commit.
v4: Ben Hutchings noticed that I've failed to handle an underflow in my loop logic, breaking it for i >= length + 8. Since I've just lost C programmer license, use his solution. Also, make the frustrated 0-base buffer size a notch more clear.
Bugzilla: https://bugzilla.kernel.org/show_bug.cgi?id=25732
---
 drivers/gpu/drm/i915/intel_sdvo.c      |   62 +++++++++++++++++++++-----------
 drivers/gpu/drm/i915/intel_sdvo_regs.h |    2 ++
 2 files changed, 44 insertions(+), 20 deletions(-)
drivers/gpu/drm/i915/intel_sdvo.c +42 -20
@@ -894,6 +894,45 @@ static void intel_sdvo_dump_hdmi_buf(struct intel_sdvo *intel_sdvo) }#endif +static bool intel_sdvo_write_infoframe (struct intel_sdvo *intel_sdvo, +unsigned if_index,uint8_t tx_rate, +uint8_t *data,unsigned length) +{ +uint8_t set_buf_index[2 ] = { if_index,0 }; +uint8_t hbuf_size, tmp[8 ]; +int i; + +if (!intel_sdvo_set_value (intel_sdvo, +SDVO_CMD_SET_HBUF_INDEX , + set_buf_index,2 )) +return false; + +if (!intel_sdvo_get_value (intel_sdvo,SDVO_CMD_GET_HBUF_INFO , + &hbuf_size,1 )) +return false; + +/* Buffer size is 0 based, hooray! */ + hbuf_size++; + +DRM_DEBUG_KMS ("writing sdvo hbuf: %i, hbuf_size %i, hbuf_size: %i\n" , + if_index, length, hbuf_size); + +for (i =0 ; i < hbuf_size; i +=8 ) { +memset (tmp,0 ,8 ); +if (i < length) +memcpy (tmp, data + i,min_t (unsigned,8 , length - i)); + +if (!intel_sdvo_set_value (intel_sdvo, +SDVO_CMD_SET_HBUF_DATA , + tmp,8 )) +return false; + } + +return intel_sdvo_set_value (intel_sdvo, +SDVO_CMD_SET_HBUF_TXRATE , + &tx_rate,1 ); +} +static bool intel_sdvo_set_avi_infoframe (struct intel_sdvo *intel_sdvo) {struct dip_infoframe avi_if = {
@@ -901,11 +940,7 @@ static bool intel_sdvo_set_avi_infoframe(struct intel_sdvo *intel_sdvo) .ver = DIP_VERSION_AVI, .len = DIP_LEN_AVI, }; -uint8_t tx_rate =SDVO_HBUF_TX_VSYNC ; -uint8_t set_buf_index[2 ] = {1 ,0 };uint8_t sdvo_data[4 +sizeof (avi_if.body.avi)]; -uint64_t *data = (uint64_t *)sdvo_data; -unsigned i;intel_dip_infoframe_csum (&avi_if);
@@ -915,22 +950,9 @@ static bool intel_sdvo_set_avi_infoframe(struct intel_sdvo *intel_sdvo) sdvo_data[3 ] = avi_if.checksum;memcpy (&sdvo_data[4 ], &avi_if.body,sizeof (avi_if.body.avi)); -if (!intel_sdvo_set_value (intel_sdvo, -SDVO_CMD_SET_HBUF_INDEX , - set_buf_index,2 )) -return false; - -for (i =0 ; i <sizeof (sdvo_data); i +=8 ) { -if (!intel_sdvo_set_value (intel_sdvo, -SDVO_CMD_SET_HBUF_DATA , - data,8 )) -return false; - data++; - } - -return intel_sdvo_set_value (intel_sdvo, -SDVO_CMD_SET_HBUF_TXRATE , - &tx_rate,1 ); +return intel_sdvo_write_infoframe (intel_sdvo,SDVO_HBUF_INDEX_AVI_IF , +SDVO_HBUF_TX_VSYNC , + sdvo_data,sizeof (sdvo_data)); }static bool intel_sdvo_set_tv_format (struct intel_sdvo *intel_sdvo)
drivers/gpu/drm/i915/intel_sdvo_regs.h +2 -0
@@ -708,6 +708,8 @@ struct intel_sdvo_enhancements_arg {#define SDVO_CMD_SET_AUDIO_STAT 0x91#define SDVO_CMD_GET_AUDIO_STAT 0x92#define SDVO_CMD_SET_HBUF_INDEX 0x93 +#define SDVO_HBUF_INDEX_ELD 0 +#define SDVO_HBUF_INDEX_AVI_IF 1#define SDVO_CMD_GET_HBUF_INDEX 0x94#define SDVO_CMD_GET_HBUF_INFO 0x95#define SDVO_CMD_SET_HBUF_AV_SPLIT 0x96
PATCH 22/82 crypto: cryptd - disable softirqs in cryptd_queue_worker to prevent data corruption
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Jussi Kivilinna <[email protected]>
commit 9efade1b3e981f5064f9db9ca971b4dc7557ae42 upstream.
cryptd_queue_worker attempts to prevent simultaneous accesses to crypto workqueue by cryptd_enqueue_request using preempt_disable/preempt_enable. However cryptd_enqueue_request might be called from softirq context, so add local_bh_disable/local_bh_enable to prevent data corruption and panics.
Bug report at http://marc.info/?l=linux-crypto-vger&m=134858649616319&w=2
v2:
- Disable software interrupts instead of hardware interrupts
---
 crypto/cryptd.c |   11 ++++++++---
 1 file changed, 8 insertions(+), 3 deletions(-)
crypto/cryptd.c +8 -3
@@ -137,13 +137,18 @@ static void cryptd_queue_worker(struct work_struct *work)struct crypto_async_request *req, *backlog; cpu_queue = container_of(work, struct cryptd_cpu_queue, work); -/* Only handle one request at a time to avoid hogging crypto -* workqueue. preempt_disable/enable is used to prevent -* being preempted by cryptd_enqueue_request() */ +/* +* Only handle one request at a time to avoid hogging crypto workqueue. +* preempt_disable/enable is used to prevent being preempted by +* cryptd_enqueue_request(). local_bh_disable/enable is used to prevent +* cryptd_enqueue_request() being accessed from software interrupts. +*/ +local_bh_disable ();preempt_disable (); backlog =crypto_get_backlog (&cpu_queue->queue); req =crypto_dequeue_request (&cpu_queue->queue);preempt_enable (); +local_bh_enable ();if (!req)return ;
PATCH 23/82 ARM: at91: at91sam9g10: fix SOC type detection
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ivan Shugov <[email protected]>
commit 3d9a0183dd3423353e9e363bcc261c1220d05f9f upstream.
Newer at91sam9g10 SoC revision can't be detected, so the kernel can't boot with this kind of kernel panic:
"AT91: Impossible to detect the SOC type"
CPU: ARM926EJ-S [41069265] revision 5 (ARMv5TEJ), cr=00053177
CPU: VIVT data cache, VIVT instruction cache
Machine: Atmel AT91SAM9G10-EK
Ignoring tag cmdline (using the default kernel command line) bootconsole [earlycon0] enabled
Memory policy: ECC disabled, Data cache writeback
Kernel panic - not syncing: AT91: Impossible to detect the SOC type
[<c00133d4>] (unwind_backtrace+0x0/0xe0) from [<c02366dc>] (panic+0x78/0x1cc)
[<c02366dc>] (panic+0x78/0x1cc) from [<c02fa35c>] (at91_map_io+0x90/0xc8)
[<c02fa35c>] (at91_map_io+0x90/0xc8) from [<c02f9860>] (paging_init+0x564/0x6d0)
[<c02f9860>] (paging_init+0x564/0x6d0) from [<c02f7914>] (setup_arch+0x464/0x704)
[<c02f7914>] (setup_arch+0x464/0x704) from [<c02f44f8>] (start_kernel+0x6c/0x2d4)
[<c02f44f8>] (start_kernel+0x6c/0x2d4) from [<20008040>] (0x20008040)
The reason for this is that the Debug Unit Chip ID Register has changed between Engineering Sample and definitive revision of the SoC. Changing the check of cidr to socid will address the problem. We do not integrate this check to the list just above because we also have to make sure that the extended id is disregarded.
---
 arch/arm/mach-at91/setup.c |    2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
arch/arm/mach-at91/setup.c +1 -1
@@ -151,7 +151,7 @@ static void __init soc_detect(u32 dbgu_base) }/* at91sam9g10 */ -if ((cidr & ~AT91_CIDR_EXT ) ==ARCH_ID_AT91SAM9G10 ) { +if ((socid & ~AT91_CIDR_EXT ) ==ARCH_ID_AT91SAM9G10 ) { at91_soc_initdata.type =AT91_SOC_SAM9G10 ; at91_boot_soc = at91sam9261_soc; }
PATCH 24/82 ARM: at91/i2c: change id to let i2c-gpio work
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Bo Shen <[email protected]>
commit 7840487cd6298f9f931103b558290d8d98d41c49 upstream.
The i2c core driver will turn the platform device ID to busnum When using platfrom device ID as -1, it means dynamically assigned the busnum. When writing code, we need to make sure the busnum, and call i2c_register_board_info(int busnum, ...) to register device if using -1, we do not know the value of busnum
In order to solve this issue, set the platform device ID as a fix number Here using 0 to match the busnum used in i2c_regsiter_board_info()
---
 arch/arm/mach-at91/at91rm9200_devices.c  |    2 +-
 arch/arm/mach-at91/at91sam9260_devices.c |    2 +-
 arch/arm/mach-at91/at91sam9261_devices.c |    2 +-
 arch/arm/mach-at91/at91sam9263_devices.c |    2 +-
 arch/arm/mach-at91/at91sam9rl_devices.c  |    2 +-
 5 files changed, 5 insertions(+), 5 deletions(-)
arch/arm/mach-at91/at91rm9200_devices.c +1 -1
@@ -479,7 +479,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91rm9200_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9260_devices.c +1 -1
@@ -389,7 +389,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9260_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9261_devices.c +1 -1
@@ -285,7 +285,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9261_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9263_devices.c +1 -1
@@ -567,7 +567,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9263_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9rl_devices.c +1 -1
@@ -314,7 +314,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9rl_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
PATCH 25/82 mac80211: Only process mesh config header on frames that RA_MATCH
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Javier Cardona <[email protected]>
commit 555cb715be8ef98b8ec362b23dfc254d432a35b1 upstream.
Doing otherwise is wrong, and may wreak havoc on the mpp tables, specially if the frame is encrypted.
[bwh: Backported to 3.2: we have a large block conditional on
IEEE80211_RX_RA_MATCH rather than a goto conditional on the opposite, so delete the condition]
---
net/mac80211/rx.c +3 -2
@@ -1895,7 +1895,8 @@ ieee80211_rx_h_mesh_fwding(struct ieee80 mesh_rmc_check(hdr->addr3, mesh_hdr, rx->sdata))return RX_DROP_MONITOR ; -if (!ieee80211_is_data (hdr->frame_control)) +if (!ieee80211_is_data (hdr->frame_control) || + !(status->rx_flags &IEEE80211_RX_RA_MATCH ))return RX_CONTINUE ;if (!mesh_hdr->ttl)
@@ -1941,7 +1942,7 @@ ieee80211_rx_h_mesh_fwding(struct ieee80 mesh_hdr->ttl--; -if (status->rx_flags &IEEE80211_RX_RA_MATCH ) { + {if (!mesh_hdr->ttl)IEEE80211_IFSTA_MESH_CTR_INC (&rx->sdata->u.mesh, dropped_frames_ttl);
PATCH 26/82 mac80211: dont inspect Sequence Control field on control frames
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Javier Cardona <[email protected]>
commit f7fbf70ee9db6da6033ae50d100e017ac1f26555 upstream.
Per IEEE Std. 802.11-2012, Sec 8.2.4.4.1, the sequence Control field is not present in control frames. We noticed this problem when processing Block Ack Requests.
---
 net/mac80211/rx.c |    4 ++++
 1 file changed, 4 insertions(+)
net/mac80211/rx.c +4 -0
@@ -1462,6 +1462,10 @@ ieee80211_rx_h_defragment(struct ieee80211_rx_data *rx) hdr = (struct ieee80211_hdr *)rx->skb->data; fc = hdr->frame_control; + +if (ieee80211_is_ctl (fc)) +return RX_CONTINUE ; + sc =le16_to_cpu (hdr->seq_ctrl); frag = sc &IEEE80211_SCTL_FRAG ;
PATCH 27/82 gpiolib: Dont return -EPROBE_DEFER to sysfs, or for invalid gpios
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Mathias Nyman <[email protected]>
commit ad2fab36d7922401c4576fb7ea9b21a47a29a17f upstream.
gpios requested with invalid numbers, or gpios requested from userspace via sysfs should not try to be deferred on failure.
---
 drivers/gpio/gpiolib.c |   10 +++++++---
 1 file changed, 7 insertions(+), 3 deletions(-)
drivers/gpio/gpiolib.c +7 -3
@@ -623,9 +623,11 @@ static ssize_t export_store(struct class *class,*/ status =gpio_request (gpio,"sysfs" ); -if (status <0 ) +if (status <0 ) { +if (status == -EPROBE_DEFER ) + status = -ENODEV ; goto done; - + } status =gpio_export (gpio, true);if (status <0 )gpio_free (gpio);
@@ -1191,8 +1193,10 @@ int gpio_request(unsigned gpio, const char *label)spin_lock_irqsave (&gpio_lock, flags); -if (!gpio_is_valid (gpio)) +if (!gpio_is_valid (gpio)) { + status = -EINVAL ; goto done; + } desc = &gpio_desc[gpio]; chip = desc->chip;if (chip ==NULL )
Re: [ 27/82] gpiolib: Dont return -EPROBE_DEFER to sysfs, or for invalid gpios
Quoted 23 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Mathias Nyman <[email protected]>
commit
ad2fab36d7922401c4576fb7ea9b21a47a29a17fupstream.gpios requested with invalid numbers, or gpios requested from userspace via sysfs should not try to be deferred on failure.
Signed-off-by Mathias Nyman <[email protected]>Signed-off-by Linus Walleij <[email protected]>Signed-off-by Ben Hutchings <[email protected]>--- drivers/gpio/gpiolib.c | 10 +++++++--- 1 file changed, 7 insertions(+), 3 deletions(-)drivers/gpio/gpiolib.c +0
-0
drivers/gpio/gpiolib.c static ssize_t export_store(struct class *class, · line 627
Quoted 6 lines
drivers/gpio/gpiolib.c +2
-1@@ -623,9 +623,11 @@ static ssize_t export_store(struct class *class,*/ status =gpio_request (gpio,"sysfs" ); -if (status <0 ) +if (status <0 ) { +if (status == -EPROBE_DEFER )
This one fails to build here:linux/drivers/gpio/gpiolib.c: In function 'export_store':linux/drivers/gpio/gpiolib.c:625:18: error: 'EPROBE_DEFER' undeclared (first use in this function) linux/drivers/gpio/gpiolib.c:625:18: note: each undeclared identifier is reported only once for each function it appears in
There is no EPROBE_DEFER functionality on 3.2 and in gpio_request, so I think the patch can be safely dropped.
[...]
Signature · 2 lines
[]'s
Herton
Re: [ 27/82] gpiolib: Dont return -EPROBE_DEFER to sysfs, or for invalid gpios
Quoted 36 lines · Herton Ronaldo Krzesinski
Quoted 23 lines · Ben Hutchings
3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Mathias Nyman <[email protected]>
commit
ad2fab36d7922401c4576fb7ea9b21a47a29a17fupstream.gpios requested with invalid numbers, or gpios requested from userspace via sysfs should not try to be deferred on failure.
Signed-off-by Mathias Nyman <[email protected]>Signed-off-by Linus Walleij <[email protected]>Signed-off-by Ben Hutchings <[email protected]>--- drivers/gpio/gpiolib.c | 10 +++++++--- 1 file changed, 7 insertions(+), 3 deletions(-)drivers/gpio/gpiolib.c +0
-0drivers/gpio/gpiolib.c static ssize_t export_store(struct class *class, · line 627
Quoted 6 lines
drivers/gpio/gpiolib.c +2
-1@@ -623,9 +623,11 @@ static ssize_t export_store(struct class *class,*/ status =gpio_request (gpio,"sysfs" ); -if (status <0 ) +if (status <0 ) { +if (status == -EPROBE_DEFER )This one fails to build here:
linux/drivers/gpio/gpiolib.c: In function 'export_store':linux/drivers/gpio/gpiolib.c:625:18: error: 'EPROBE_DEFER' undeclared (first use in this function)linux/drivers/gpio/gpiolib.c:625:18: note: each undeclared identifier is reported only once for each function it appears in
Quoted 4 lines
There is no
EPROBE_DEFERfunctionality on 3.2 and ingpio_request, so I think the patch can be safely dropped.[...]
Right, I'll do that, thanks.
Ben.
Signature · 2 lines
Ben Hutchings
friends: People who know you well, but like you anyway.
PATCH 28/82 mac80211: fix SSID copy on IBSS JOIN
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Antonio Quartulli <[email protected]>
commit badecb001a310408d3473b1fc2ed5aefd0bc92a9 upstream.
The 'ssid' field of the cfg80211_ibss_params is a u8 pointer and its length is likely to be less than IEEE80211_MAX_SSID_LEN most of the time.
This patch fixes the ssid copy in ieee80211_ibss_join() by using the SSID length to prevent it from reading beyond the string.
---
 net/mac80211/ibss.c |    2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
net/mac80211/ibss.c +1 -1
@@ -1108,7 +1108,7 @@ int ieee80211_ibss_join(struct ieee80211_sub_if_data *sdata, sdata->u.ibss.state =IEEE80211_IBSS_MLME_SEARCH ; sdata->u.ibss.ibss_join_req = jiffies; -memcpy (sdata->u.ibss.ssid, params->ssid,IEEE80211_MAX_SSID_LEN ); +memcpy (sdata->u.ibss.ssid, params->ssid, params->ssid_len); sdata->u.ibss.ssid_len = params->ssid_len;mutex_unlock (&sdata->u.ibss.mtx);
PATCH 29/82 wireless: drop invalid mesh address extension frames
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Johannes Berg <[email protected]>
commit 7dd111e8ee10cc6816669eabcad3334447673236 upstream.
The mesh header can have address extension by a 4th or a 5th and 6th address, but never both. Drop such frames in 802.11 -> 802.3 conversion along with any frames that have the wrong extension.
---
 net/wireless/util.c |   11 ++++++-----
 1 file changed, 6 insertions(+), 5 deletions(-)
net/wireless/util.c +6 -5
@@ -312,18 +312,15 @@ EXPORT_SYMBOL(ieee80211_get_hdrlen_from_skb);static int ieee80211_get_mesh_hdrlen (struct ieee80211s_hdr *meshhdr) {int ae = meshhdr->flags &MESH_FLAGS_AE ; -/* 7.1.3.5a.2 */ +/* 802.11-2012, 8.2.4.7.3 */ switch (ae) { +default :case 0 :return 6 ;case MESH_FLAGS_AE_A4 :return 12 ;case MESH_FLAGS_AE_A5_A6 :return 18 ; -case (MESH_FLAGS_AE_A4 |MESH_FLAGS_AE_A5_A6 ): -return 24 ; -default : -return 6 ; } }
@@ -373,6 +370,8 @@ int ieee80211_data_to_8023(struct sk_buff *skb, const u8 *addr,/* make sure meshdr->flags is on the linear part */ if (!pskb_may_pull (skb, hdrlen +1 ))return -1 ; +if (meshdr->flags &MESH_FLAGS_AE_A4 ) +return -1 ;if (meshdr->flags &MESH_FLAGS_AE_A5_A6 ) { skb_copy_bits(skb, hdrlen + offsetof(struct ieee80211s_hdr, eaddr1),
@@ -397,6 +396,8 @@ int ieee80211_data_to_8023(struct sk_buff *skb, const u8 *addr,/* make sure meshdr->flags is on the linear part */ if (!pskb_may_pull (skb, hdrlen +1 ))return -1 ; +if (meshdr->flags &MESH_FLAGS_AE_A5_A6 ) +return -1 ;if (meshdr->flags &MESH_FLAGS_AE_A4 ) skb_copy_bits(skb, hdrlen + offsetof(struct ieee80211s_hdr, eaddr1),
PATCH 30/82 mac80211: check management frame header length
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Johannes Berg <[email protected]>
commit 4a4f1a5808c8bb0b72a4f6e5904c53fb8c9cd966 upstream.
Due to pskb_may_pull() checking the skb length, all non-management frames are checked on input whether their 802.11 header is fully present. Also add that check for management frames and remove a check that is now duplicate. This prevents accessing skb data beyond the frame end.
--- net/mac80211/rx.c | 12 ++++++++---- 1 file changed, 8 insertions(+), 4 deletions(-)
net/mac80211/rx.c +8 -4
@@ -1457,7 +1457,6 @@ ieee80211_rx_h_defragment(struct ieee802 frag = sc &IEEE80211_SCTL_FRAG ;if (likely ((!ieee80211_has_morefrags (fc) && frag ==0 ) || - (rx->skb)->len <24 ||is_multicast_ether_addr (hdr->addr1))) {/* not fragmented */ goto out;
@@ -2875,10 +2874,15 @@ static void __ieee80211_rx_handle_packet test_bit(SCAN_OFF_CHANNEL, &local->scanning))) status->rx_flags |= IEEE80211_RX_IN_SCAN; -if (ieee80211_is_mgmt (fc)) - err =skb_linearize (skb); -else +if (ieee80211_is_mgmt (fc)) { +/* drop frame if too short for header */ +if (skb->len <ieee80211_hdrlen (fc)) + err = -ENOBUFS ; +else + err =skb_linearize (skb); + }else { err = !pskb_may_pull (skb,ieee80211_hdrlen (fc)); + }if (err) {dev_kfree_skb (skb);
PATCH 31/82 mac80211: verify that skb data is present
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Johannes Berg <[email protected]>
commit 9b395bc3be1cebf0144a127c7e67d56dbdac0930 upstream.
A number of places in the mesh code don't check that the frame data is present and in the skb header when trying to access. Add those checks and the necessary pskb_may_pull() calls. This prevents accessing data that doesn't actually exist.
To do this, export ieee80211_get_mesh_hdrlen() to be able to use it in mac80211.
--- include/net/cfg80211.h | 9 +++++++++ net/mac80211/rx.c | 32 +++++++++++++++++++++++++++++++- net/wireless/util.c | 3 ++- 3 files changed, 42 insertions(+), 2 deletions(-)
include/net/cfg80211.h +9 -0
@@ -2652,6 +2652,15 @@ unsigned int ieee80211_get_hdrlen_from_skb(const struct sk_buff *skb); unsigned int __attribute_const__ ieee80211_hdrlen(__le16 fc);/** +* ieee80211_get_mesh_hdrlen - get mesh extension header length +* @meshhdr: the mesh extension header, only the flags field +* (first byte) will be accessed +* Returns the length of the extension header, which is always at +* least 6 bytes and at most 18 if address 5 and 6 are present. +*/ +unsigned int ieee80211_get_mesh_hdrlen (struct ieee80211s_hdr *meshhdr); + +/** * DOC: Data path helpers * * In addition to generic utilities, cfg80211 also offers
net/mac80211/rx.c +31 -1
@@ -531,6 +531,11 @@ ieee80211_rx_mesh_check(struct ieee80211_rx_data *rx)if (ieee80211_is_action (hdr->frame_control)) {u8 category; + +/* make sure category field is present */ +if (rx->skb->len <IEEE80211_MIN_ACTION_SIZE ) +return RX_DROP_MONITOR ; + mgmt = (struct ieee80211_mgmt *)hdr; category = mgmt->u.action.category; if (category != WLAN_CATEGORY_MESH_ACTION &&
@@ -1892,6 +1897,20 @@ ieee80211_rx_h_mesh_fwding(struct ieee80211_rx_data *rx) hdr = (struct ieee80211_hdr *) skb->data; hdrlen =ieee80211_hdrlen (hdr->frame_control); + +/* make sure fixed part of mesh header is there, also checks skb len */ +if (!pskb_may_pull (rx->skb, hdrlen +6 )) +return RX_DROP_MONITOR ; + + mesh_hdr = (struct ieee80211s_hdr *) (skb->data + hdrlen); + +/* make sure full mesh header is there, also checks skb len */ +if (!pskb_may_pull (rx->skb, + hdrlen +ieee80211_get_mesh_hdrlen (mesh_hdr))) +return RX_DROP_MONITOR ; + +/* reload pointers */ + hdr = (struct ieee80211_hdr *) skb->data; mesh_hdr = (struct ieee80211s_hdr *) (skb->data + hdrlen);/* frame is in RMC, don't forward */
@@ -1915,9 +1934,12 @@ ieee80211_rx_h_mesh_fwding(struct ieee80211_rx_data *rx)if (is_multicast_ether_addr (hdr->addr1)) { mpp_addr = hdr->addr3; proxied_addr = mesh_hdr->eaddr1; - }else { + }else if (mesh_hdr->flags &MESH_FLAGS_AE_A5_A6 ) { +/* has_a4 already checked in ieee80211_rx_mesh_check */ mpp_addr = hdr->addr4; proxied_addr = mesh_hdr->eaddr2; + }else { +return RX_DROP_MONITOR ; }rcu_read_lock ();
@@ -2354,6 +2376,10 @@ ieee80211_rx_h_action(struct ieee80211_rx_data *rx) }break ;case WLAN_CATEGORY_SELF_PROTECTED : +if (len < (IEEE80211_MIN_ACTION_SIZE + +sizeof (mgmt->u.action.u.self_prot.action_code))) +break ; +switch (mgmt->u.action.u.self_prot.action_code) {case WLAN_SP_MESH_PEERING_OPEN :case WLAN_SP_MESH_PEERING_CLOSE :
@@ -2372,6 +2398,10 @@ ieee80211_rx_h_action(struct ieee80211_rx_data *rx) }break ;case WLAN_CATEGORY_MESH_ACTION : +if (len < (IEEE80211_MIN_ACTION_SIZE + +sizeof (mgmt->u.action.u.mesh_action.action_code))) +break ; +if (!ieee80211_vif_is_mesh (&sdata->vif))break ; if (mesh_action_is_path_sel(mgmt) &&
net/wireless/util.c +2 -1
@@ -309,7 +309,7 @@ unsigned int ieee80211_get_hdrlen_from_skb(const struct sk_buff *skb) }EXPORT_SYMBOL (ieee80211_get_hdrlen_from_skb); -static int ieee80211_get_mesh_hdrlen (struct ieee80211s_hdr *meshhdr) +unsigned int ieee80211_get_mesh_hdrlen (struct ieee80211s_hdr *meshhdr) {int ae = meshhdr->flags &MESH_FLAGS_AE ;/* 802.11-2012, 8.2.4.7.3 */
@@ -323,6 +323,7 @@ static int ieee80211_get_mesh_hdrlen(struct ieee80211s_hdr *meshhdr)return 18 ; } } +EXPORT_SYMBOL (ieee80211_get_mesh_hdrlen);int ieee80211_data_to_8023 (struct sk_buff *skb,const u8 *addr,enum nl80211_iftype iftype)
PATCH 32/82 mac80211: make sure data is accessible in EAPOL check
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Johannes Berg <[email protected]>
commit 6dbda2d00d466225f9db1dc695ff852443f28832 upstream.
The code to allow EAPOL frames even when the station isn't yet marked associated needs to check that the incoming frame is long enough and due to paged RX it also can't assume skb->data contains the right data, it must use skb_copy_bits(). Fix this to avoid using data that doesn't really exist.
--- net/mac80211/rx.c | 18 ++++++++++-------- 1 file changed, 10 insertions(+), 8 deletions(-)
net/mac80211/rx.c +9 -7
@@ -859,14 +859,16 @@ ieee80211_rx_h_check(struct ieee80211_rx (!rx->sta || !test_sta_flag(rx->sta, WLAN_STA_ASSOC)))) {if (rx->sta && rx->sta->dummy &&ieee80211_is_data_present (hdr->frame_control)) { -u16 ethertype; -u8 *payload; +unsigned int hdrlen; +__be16 ethertype; - payload = rx->skb->data + -ieee80211_hdrlen (hdr->frame_control); - ethertype = (payload[6 ] <<8 ) | payload[7 ]; -if (cpu_to_be16 (ethertype) == - rx->sdata->control_port_protocol) + hdrlen =ieee80211_hdrlen (hdr->frame_control); + +if (rx->skb->len < hdrlen +8 ) +return RX_DROP_MONITOR ; + +skb_copy_bits (rx->skb, hdrlen +6 , ðertype,2 ); +if (ethertype == rx->sdata->control_port_protocol)return RX_CONTINUE ; }return RX_DROP_MONITOR ;
PATCH 33/82 ath9k: fix stale pointers potentially causing access to freed skbs
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Felix Fietkau <[email protected]>
commit 8c6e30936a7893a85f6222084f0f26aceb81137a upstream.
bf->bf_next is only while buffers are chained as part of an A-MPDU in the tx queue. When a tid queue is flushed (e.g. on tearing down an aggregation session), frames can be enqueued again as normal transmission, without bf_next being cleared. This can lead to the old pointer being dereferenced again later.
This patch might fix crashes and "Failed to stop TX DMA!" messages.
--- drivers/net/wireless/ath/ath9k/xmit.c | 2 ++ 1 file changed, 2 insertions(+)
drivers/net/wireless/ath/ath9k/xmit.c +2 -0
@@ -288,6 +288,7 @@ static struct ath_buf *ath_tx_get_buffer } bf = list_first_entry(&sc->tx.txbuf, struct ath_buf, list); + bf->bf_next =NULL ;list_del (&bf->list);spin_unlock_bh (&sc->tx.txbuflock);
@@ -1710,6 +1711,7 @@ static void ath_tx_send_normal(struct atif (tid)INCR (tid->seq_start,IEEE80211_SEQ_MAX ); + bf->bf_next =NULL ; bf->bf_lastbf = bf;ath_tx_fill_desc (sc, bf, txq, fi->framelen);ath_tx_txqaddbuf (sc, txq, &bf_head, false);
PATCH 34/82 floppy: do put_disk on current dr if blk_init_queue fails
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Herton Ronaldo Krzesinski <[email protected]>
commit 238ab78469c6ab7845b43d5061cd3c92331b2452 upstream.
If blk_init_queue fails, we do not call put_disk on the current dr (dr is decremented first in the error handling loop).
--- drivers/block/floppy.c | 1 + 1 file changed, 1 insertion(+)
drivers/block/floppy.c +1 -0
@@ -4150,6 +4150,7 @@ static int __init do_floppy_init(void) disks[dr]->queue =blk_init_queue (do_fd_request, &floppy_lock);if (!disks[dr]->queue) { +put_disk (disks[dr]); err = -ENOMEM ; goto out_put_disk; }
PATCH 35/82 floppy: properly handle failure on add_disk loop
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Herton Ronaldo Krzesinski <[email protected]>
commit d60e7ec18c3fb2cbf90969ccd42889eb2d03aef9 upstream.
On floppy initialization, if something failed inside the loop we call add_disk, there was no cleanup of previous iterations in the error handling.
--- drivers/block/floppy.c | 11 ++++++++++- 1 file changed, 10 insertions(+), 1 deletion(-)
drivers/block/floppy.c +10 -1
@@ -4305,7 +4305,7 @@ static int __init floppy_init(void) err =platform_device_register (&floppy_device[drive]);if (err) - goto out_flush_work; + goto out_remove_drives; err =device_create_file (&floppy_device[drive].dev, &dev_attr_cmos);
@@ -4323,6 +4323,15 @@ static int __init floppy_init(void) out_unreg_platform_dev:platform_device_unregister (&floppy_device[drive]); +out_remove_drives: +while (drive--) { +if ((allowed_drive_mask & (1 << drive)) && + fdc_state[FDC (drive)].version !=FDC_NONE ) { +del_gendisk (disks[drive]); +device_remove_file (&floppy_device[drive].dev, &dev_attr_cmos); +platform_device_unregister (&floppy_device[drive]); + } + } out_flush_work:flush_work_sync (&floppy_work);if (atomic_read (&usage_count))
PATCH 36/82 xen/gntdev: dont leak memory from IOCTL_GNTDEV_MAP_GRANT_REF
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: David Vrabel <[email protected]>
commit a67baeb77375199bbd842fa308cb565164dd1f19 upstream.
map->kmap_ops allocated in gntdev_alloc_map() wasn't freed by gntdev_put_map().
Add a gntdev_free_map() helper function to free everything allocated by gntdev_alloc_map().
--- drivers/xen/gntdev.c | 36 +++++++++++++++++++----------------- 1 file changed, 19 insertions(+), 17 deletions(-)
drivers/xen/gntdev.c +19 -17
@@ -105,6 +105,21 @@ static void gntdev_print_maps(struct gnt#endif } +static void gntdev_free_map (struct grant_map *map) +{ +if (map ==NULL ) +return ; + +if (map->pages) +free_xenballooned_pages (map->count, map->pages); +kfree (map->pages); +kfree (map->grants); +kfree (map->map_ops); +kfree (map->unmap_ops); +kfree (map->kmap_ops); +kfree (map); +} +static struct grant_map *gntdev_alloc_map (struct gntdev_priv *priv,int count) {struct grant_map *add;
@@ -142,12 +157,7 @@ static struct grant_map *gntdev_alloc_mareturn add; err: -kfree (add->pages); -kfree (add->grants); -kfree (add->map_ops); -kfree (add->unmap_ops); -kfree (add->kmap_ops); -kfree (add); +gntdev_free_map (add);return NULL ; }
@@ -196,17 +206,9 @@ static void gntdev_put_map(struct grant_if (map->notify.flags &UNMAP_NOTIFY_SEND_EVENT )notify_remote_via_evtchn (map->notify.event); -if (map->pages) { -if (!use_ptemod) -unmap_grant_pages (map,0 , map->count); - -free_xenballooned_pages (map->count, map->pages); - } -kfree (map->pages); -kfree (map->grants); -kfree (map->map_ops); -kfree (map->unmap_ops); -kfree (map); +if (map->pages && !use_ptemod) +unmap_grant_pages (map,0 , map->count); +gntdev_free_map (map); }/* ------------------------------------------------------------------ */
PATCH 37/82 rt2800: validate step value for temperature compensation
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Stanislaw Gruszka <[email protected]>
commit bf7e1abe434ba9e22e8dc04a4cba4ab504b788b8 upstream.
Some hardware has correct (!= 0xff) value of tssi_bounds[4] in the EEPROM, but step is equal to 0xff. This results on ridiculous delta calculations and completely broke TX power settings.
--- drivers/net/wireless/rt2x00/rt2800lib.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/net/wireless/rt2x00/rt2800lib.c +1 -1
@@ -2449,7 +2449,7 @@ static int rt2800_get_gain_calibration_delta(struct rt2x00_dev *rt2x00dev)/* * Check if temperature compensation is supported. */ -if (tssi_bounds[4 ] ==0xff ) +if (tssi_bounds[4 ] ==0xff || step ==0xff )return 0 ;/*
PATCH 38/82 ath9k: Test for TID only in BlockAcks while checking tx status
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Sven Eckelmann <[email protected]>
commit 6fe7cc71bbf3a0bc28c9cec3c00bc11e81344412 upstream.
The ath9k xmit functions for AMPDUs can send frames as non-aggregate in case only one frame is currently available. The client will then answer using a normal Ack instead of a BlockAck. This acknowledgement has no TID stored and therefore the hardware is not able to provide us the corresponding TID.
The TID set by the hardware in the tx status descriptor has to be seen as undefined and not as a valid TID value for normal acknowledgements. Doing otherwise results in a massive amount of retransmissions and stalls of connections.
Users may experience low bandwidth and complete connection stalls in environments with transfers using multiple TIDs.
This regression was introduced in b11b160defc48e4daa283f785192ea3a23a51f8e ("ath9k: validate the TID in the tx status information").
--- drivers/net/wireless/ath/ath9k/xmit.c | 8 ++++++-- 1 file changed, 6 insertions(+), 2 deletions(-)
drivers/net/wireless/ath/ath9k/xmit.c +6 -2
@@ -370,7 +370,7 @@ static void ath_tx_complete_aggr(structu16 seq_st =0 , acked_cnt =0 , txfail_cnt =0 ;u32 ba[WME_BA_BMP_SIZE >>5 ];int isaggr, txfail, txpending, sendbar =0 , needreset =0 , nbad =0 ; -bool rc_update = true; +bool rc_update = true, isba;struct ieee80211_tx_rate rates[4 ];struct ath_frame_info *fi;int nframes;
@@ -408,13 +408,17 @@ static void ath_tx_complete_aggr(struct an = (struct ath_node *)sta->drv_priv; tidno =ieee80211_get_qos_ctl (hdr)[0 ] &IEEE80211_QOS_CTL_TID_MASK ; tid =ATH_AN_2_TID (an, tidno); + isba = ts->ts_flags &ATH9K_TX_BA ;/* * The hardware occasionally sends a tx status for the wrong TID. * In this case, the BA status cannot be considered valid and all * subframes need to be retransmitted +* +* Only BlockAcks have a TID and therefore normal Acks cannot be +* checked */ -if (tidno != ts->tid) +if (isba && tidno != ts->tid) txok = false; isaggr =bf_isaggr (bf);
PATCH 39/82 module: fix out-by-one error in kallsyms
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Rusty Russell <[email protected]>
commit 59ef28b1f14899b10d6b2682c7057ca00a9a3f47 upstream.
Masaki found and patched a kallsyms issue: the last symbol in a module's symtab wasn't transferred. This is because we manually copy the zero'th entry (which is always empty) then copy the rest in a loop starting at 1, though from src[0]. His fix was minimal, I prefer to rewrite the loops in more standard form.
There are two loops: one to get the size, and one to copy. Make these
identical: always count entry 0 and any defined symbol in an allocated non-init section.
This bug exists since the following commit was introduced.
module: reduce symbol table for loaded modules (v2)
commit: 4a4962263f07d14660849ec134ee42b63e95ea9a
LKML: http://lkml.org/lkml/2012/10/24/27
[bwh: Backported to 3.2: we're still using a bitmap to compress the string
table]
--- kernel/module.c | 27 ++++++++++++++++----------- 1 file changed, 16 insertions(+), 11 deletions(-)
kernel/module.c +13 -11
@@ -2193,15 +2193,17 @@ static void layout_symtab(struct module src = (void *)info->hdr + symsect->sh_offset; nsrc = symsect->sh_size /sizeof (*src); -for (ndst = i =1 ; i < nsrc; ++i, ++src) -if (is_core_symbol (src, info->sechdrs, info->hdr->e_shnum)) { -unsigned int j = src->st_name; +for (ndst = i =0 ; i < nsrc; i++) { +if (i ==0 || +is_core_symbol (src+i, info->sechdrs, info->hdr->e_shnum)) { +unsigned int j = src[i].st_name;while (!__test_and_set_bit (j, info->strmap) && info->strtab[j]) ++j; ++ndst; } + }/* Append room for core symbols at end of core part. */ info->symoffs =ALIGN (mod->core_size, symsect->sh_addralign ?:1 );
@@ -2238,14 +2240,14 @@ static void add_kallsyms(struct module * mod->core_symtab = dst = mod->module_core + info->symoffs; src = mod->symtab; - *dst = *src; -for (ndst = i =1 ; i < mod->num_symtab; ++i, ++src) { -if (!is_core_symbol (src, info->sechdrs, info->hdr->e_shnum)) -continue ; - dst[ndst] = *src; - dst[ndst].st_name =bitmap_weight (info->strmap, - dst[ndst].st_name); - ++ndst; +for (ndst = i =0 ; i < mod->num_symtab; i++) { +if (i ==0 || +is_core_symbol (src+i, info->sechdrs, info->hdr->e_shnum)) { + dst[ndst] = src[i]; + dst[ndst].st_name =bitmap_weight (info->strmap, + dst[ndst].st_name); + ++ndst; + } } mod->core_num_syms = ndst;
PATCH 40/82 Input: tsc40 - remove wrong announcement of pressure support
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Rolf Eike Beer <[email protected]>
commit 32ed1911fc79908d704023317d4ddeb3883fd07e upstream.
The tsc40 driver announces it supports the pressure event, but will never send one. The announcement will cause tslib to wait for such events and sending all touch events with a pressure of 0. Removing the announcement will make tslib fall back to emulating the pressure on touch events so everything works as expected.
--- drivers/input/touchscreen/tsc40.c | 1 - 1 file changed, 1 deletion(-)
drivers/input/touchscreen/tsc40.c +0 -1
@@ -107,7 +107,6 @@ static int tsc_connect(struct serio *serio, struct serio_driver *drv)__set_bit (BTN_TOUCH , input_dev->keybit);input_set_abs_params (ptsc->dev,ABS_X ,0 ,0x3ff ,0 ,0 );input_set_abs_params (ptsc->dev,ABS_Y ,0 ,0x3ff ,0 ,0 ); -input_set_abs_params (ptsc->dev,ABS_PRESSURE ,0 ,0 ,0 ,0 );serio_set_drvdata (serio, ptsc);
PATCH 41/82 HID: microsoft: fix invalid rdesc for 3k kbd
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Jiri Slaby <[email protected]>
commit 3ccc60f9d8c39180c205dba1a020735bda1b2491 upstream.
Microsoft Digital Media Keyboard 3000 has two interfaces, and the second one has a report descriptor with a bug. The second collection says:
05 01 -- global; usage page -- 01 -- Generic Desktop Controls 09 80 -- local; usage -- 80 -- System Control
a1 01 -- main; collection -- 01 -- application
85 03 -- global; report ID -- 03
19 00 -- local; Usage Minimum -- 00
29 ff -- local; Usage Maximum -- ff
15 00 -- global; Logical Minimum -- 0
26 ff 00 -- global; Logical Maximum -- ff
81 00 -- main; input
c0 -- main; End Collection
I.e. it makes us think that there are all kinds of usages of system control. That the keyboard is a not only a keyboard, but also a joystick, mouse, gamepad, keypad, etc. The same as for the Wireless Desktop Receiver, this should be Physical Min/Max. So fix that appropriately.
References: https://bugzilla.novell.com/show_bug.cgi?id=776834
--- drivers/hid/hid-microsoft.c | 18 +++++++++++++----- 1 file changed, 13 insertions(+), 5 deletions(-)
drivers/hid/hid-microsoft.c +13 -5
@@ -28,22 +28,30 @@#define MS_RDESC 0x08#define MS_NOGET 0x10#define MS_DUPLICATE_USAGES 0x20 +#define MS_RDESC_3K 0x40 -/* -* Microsoft Wireless Desktop Receiver (Model 1028) has -* 'Usage Min/Max' where it ought to have 'Physical Min/Max' -*/ static __u8 *ms_report_fixup (struct hid_device *hdev,__u8 *rdesc,unsigned int *rsize) {unsigned long quirks = (unsigned long )hid_get_drvdata (hdev); +/* +* Microsoft Wireless Desktop Receiver (Model 1028) has +* 'Usage Min/Max' where it ought to have 'Physical Min/Max' +*/ if ((quirks &MS_RDESC ) && *rsize ==571 && rdesc[557 ] ==0x19 && rdesc[559 ] ==0x29 ) {hid_info (hdev,"fixing up Microsoft Wireless Receiver Model 1028 report descriptor\n" ); rdesc[557 ] =0x35 ; rdesc[559 ] =0x45 ; } +/* the same as above (s/usage/physical/) */ +if ((quirks &MS_RDESC_3K ) && *rsize ==106 && + !memcmp ((char []){0x19 ,0x00 ,0x29 ,0xff }, + &rdesc[94 ],4 )) { + rdesc[94 ] =0x35 ; + rdesc[96 ] =0x45 ; + }return rdesc; }
@@ -192,7 +200,7 @@ static const struct hid_device_id ms_devices[] = { { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_MS_PRESENTER_8K_USB), .driver_data = MS_PRESENTER }, { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_MS_DIGITAL_MEDIA_3K), - .driver_data = MS_ERGONOMY }, + .driver_data = MS_ERGONOMY | MS_RDESC_3K }, { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_WIRELESS_OPTICAL_DESKTOP_3_0), .driver_data = MS_NOGET }, { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_MS_COMFORT_MOUSE_4500),
PATCH 42/82 xen/mmu: Use Xen specific TLB flush instead of the generic one.
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Konrad Rzeszutek Wilk <[email protected]>
commit 95a7d76897c1e7243d4137037c66d15cbf2cce76 upstream.
As Mukesh explained it, the MMUEXT_TLB_FLUSH_ALL allows the hypervisor to do a TLB flush on all active vCPUs. If instead we were using the generic one (which ends up being xen_flush_tlb) we end up making the MMUEXT_TLB_FLUSH_LOCAL hypercall. But before we make that hypercall the kernel will IPI all of the vCPUs (even those that were asleep from the hypervisor perspective). The end result is that we needlessly wake them up and do a TLB flush when we can just let the hypervisor do it correctly.
This patch gives around 50% speed improvement when migrating idle guest's from one host to another.
Oracle-bug: 14630170
--- arch/x86/xen/mmu.c | 21 ++++++++++++++++++++- include/trace/events/xen.h | 8 ++++++++ 2 files changed, 28 insertions(+), 1 deletion(-)
arch/x86/xen/mmu.c +20 -1
@@ -1203,6 +1203,25 @@ unsigned long xen_read_cr2_direct(void)return percpu_read (xen_vcpu_info.arch.cr2); } +void xen_flush_tlb_all (void ) +{ +struct mmuext_op *op; +struct multicall_space mcs; + +trace_xen_mmu_flush_tlb_all (0 ); + +preempt_disable (); + + mcs =xen_mc_entry (sizeof (*op)); + + op = mcs.args; + op->cmd =MMUEXT_TLB_FLUSH_ALL ; +MULTI_mmuext_op (mcs.mc, op,1 ,NULL ,DOMID_SELF ); + +xen_mc_issue (PARAVIRT_LAZY_MMU ); + +preempt_enable (); +}static void xen_flush_tlb (void ) {struct mmuext_op *op;
@@ -2366,7 +2385,7 @@ int xen_remap_domain_mfn_range(struct vm err =0 ; out: -flush_tlb_all (); +xen_flush_tlb_all ();return err; }
include/trace/events/xen.h +8 -0
@@ -377,6 +377,14 @@ DECLARE_EVENT_CLASS(xen_mmu_pgd,DEFINE_XEN_MMU_PGD_EVENT (xen_mmu_pgd_pin);DEFINE_XEN_MMU_PGD_EVENT (xen_mmu_pgd_unpin); +TRACE_EVENT (xen_mmu_flush_tlb_all, + TP_PROTO(int x), +TP_ARGS (x), +TP_STRUCT__entry (__array (char, x,0 )), +TP_fast_assign ((void )x), +TP_printk ("%s" ,"" ) + ); + TRACE_EVENT(xen_mmu_flush_tlb, TP_PROTO(int x), TP_ARGS(x),
PATCH 43/82 NFS: Wait for session recovery to finish before returning
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Bryan Schumaker <[email protected]>
commit 399f11c3d872bd748e1575574de265a6304c7c43 upstream.
Currently, we will schedule session recovery and then return to the caller of nfs4_handle_exception. This works for most cases, but causes a hang on the following test case:
Client Server
------ ------
Open file over NFS v4.1
Write to file
Expire client
Try to lock file
The server will return NFS4ERR_BADSESSION, prompting the client to schedule recovery. However, the client will continue placing lock attempts and the open recovery never seems to be scheduled. The simplest solution is to wait for session recovery to run before retrying the lock.
--- fs/nfs/nfs4proc.c | 3 +-- 1 file changed, 1 insertion(+), 2 deletions(-)
fs/nfs/nfs4proc.c +1 -2
@@ -303,8 +303,7 @@ static int nfs4_handle_exception(structdprintk ("%s ERROR: %d Reset session\n" , __func__, errorcode);nfs4_schedule_session_recovery (clp->cl_session); - exception->retry =1 ; -break ; + goto wait_on_recovery;#endif /* defined(CONFIG_NFS_V4_1) */ case -NFS4ERR_FILE_OPEN :if (exception->timeout >HZ ) {
PATCH 44/82 NFSv4.1: We must release the sequence id when we fail to get a session slot
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Trond Myklebust <[email protected]>
commit 2240a9e2d013d8269ea425b73e1d7a54c7bc141f upstream.
If we do not release the sequence id in cases where we fail to get a session slot, then we can deadlock if we hit a recovery scenario.
[bwh: Backported to 3.2:
- Adjust context
- nfs4_setup_sequence() has an additional 'cache_reply' parameter]
--- fs/nfs/nfs4proc.c | 36 +++++++++++++++++++++++------------- 1 file changed, 23 insertions(+), 13 deletions(-)
fs/nfs/nfs4proc.c +23 -13
@@ -1463,9 +1463,11 @@ static void nfs4_open_prepare(struct rpc data->timestamp = jiffies;if (nfs4_setup_sequence (data->o_arg.server, &data->o_arg.seq_args, - &data->o_res.seq_res,1 , task)) -return ; -rpc_call_start (task); + &data->o_res.seq_res, +1 , task) !=0 ) +nfs_release_seqid (data->o_arg.seqid); +else +rpc_call_start (task);return ; unlock_no_action:rcu_read_unlock ();
@@ -2045,9 +2047,10 @@ static void nfs4_close_prepare(struct rp calldata->timestamp = jiffies;if (nfs4_setup_sequence (NFS_SERVER (calldata->inode), &calldata->arg.seq_args, &calldata->res.seq_res, -1 , task)) -return ; -rpc_call_start (task); +1 , task) !=0 ) +nfs_release_seqid (calldata->arg.seqid); +else +rpc_call_start (task); }static const struct rpc_call_ops nfs4_close_ops = {
@@ -4163,9 +4166,11 @@ static void nfs4_locku_prepare(struct rp calldata->timestamp = jiffies;if (nfs4_setup_sequence (calldata->server, &calldata->arg.seq_args, - &calldata->res.seq_res,1 , task)) -return ; -rpc_call_start (task); + &calldata->res.seq_res, +1 , task) !=0 ) +nfs_release_seqid (calldata->arg.seqid); +else +rpc_call_start (task); }static const struct rpc_call_ops nfs4_locku_ops = {
@@ -4309,7 +4314,7 @@ static void nfs4_lock_prepare(struct rpc/* Do we need to do an open_to_lock_owner? */ if (!(data->arg.lock_seqid->sequence->flags &NFS_SEQID_CONFIRMED )) {if (nfs_wait_on_sequence (data->arg.open_seqid, task) !=0 ) -return ; + goto out_release_lock_seqid; data->arg.open_stateid = &state->stateid; data->arg.new_lock_owner =1 ; data->res.open_seqid = data->arg.open_seqid;
@@ -4318,10 +4323,15 @@ static void nfs4_lock_prepare(struct rpc data->timestamp = jiffies;if (nfs4_setup_sequence (data->server, &data->arg.seq_args, - &data->res.seq_res,1 , task)) + &data->res.seq_res, +1 , task) ==0 ) { +rpc_call_start (task);return ; -rpc_call_start (task); -dprintk ("%s: done!, ret = %d\n" , __func__, data->rpc_status); + } +nfs_release_seqid (data->arg.open_seqid); +out_release_lock_seqid: +nfs_release_seqid (data->arg.lock_seqid); +dprintk ("%s: done!, ret = %d\n" , __func__, task->tk_status); }static void nfs4_recover_lock_prepare (struct rpc_task *task,void *calldata)
PATCH 45/82 NFSv4: nfs4_locku_done must release the sequence id
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Trond Myklebust <[email protected]>
commit 2b1bc308f492589f7d49012ed24561534ea2be8c upstream.
If the state recovery machinery is triggered by the call to nfs4_async_handle_error() then we can deadlock.
--- fs/nfs/nfs4proc.c | 1 + 1 file changed, 1 insertion(+)
fs/nfs/nfs4proc.c +1 -0
@@ -4531,6 +4531,7 @@ static void nfs4_locku_done(struct rpc_task *task, void *data)if (nfs4_async_handle_error (task, calldata->server,NULL ) == -EAGAIN )rpc_restart_call_prepare (task); } +nfs_release_seqid (calldata->arg.seqid); }static void nfs4_locku_prepare (struct rpc_task *task,void *data)
PATCH 46/82 NFS: fix bug in legacy DNS resolver.
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: NeilBrown <[email protected]>
commit 8d96b10639fb402357b75b055b1e82a65ff95050 upstream.
The DNS resolver's use of the sunrpc cache involves a 'ttl' number (relative) rather that a timeout (absolute). This confused me when I wrote
commit c5b29f885afe890f953f7f23424045cdad31d3e4
"sunrpc: use seconds since boot in expiry cache"
and I managed to break it. The effect is that any TTL is interpreted as 0, and nothing useful gets into the cache.
This patch removes the use of get_expiry() - which really expects an expiry time - and uses get_uint() instead, treating the int correctly as a ttl.
This fixes a regression that has been present since 2.6.37, causing certain NFS accesses in certain environments to incorrectly fail.
--- fs/nfs/dns_resolve.c | 5 +++-- 1 file changed, 3 insertions(+), 2 deletions(-)
fs/nfs/dns_resolve.c +3 -2
@@ -217,7 +217,7 @@ static int nfs_dns_parse(struct cache_detail *cd, char *buf, int buflen) {char buf1[NFS_DNS_HOSTNAME_MAXLEN +1 ];struct nfs_dns_ent key, *item; -unsigned long ttl; +unsigned int ttl;ssize_t len;int ret = -EINVAL ;
@@ -240,7 +240,8 @@ static int nfs_dns_parse(struct cache_detail *cd, char *buf, int buflen) key.namelen = len;memset (&key.h,0 ,sizeof (key.h)); - ttl =get_expiry (&buf); +if (get_uint (&buf, &ttl) <0 ) + goto out;if (ttl ==0 ) goto out; key.h.expiry_time = ttl +seconds_since_boot ();
PATCH 47/82 nfsv3: Make v3 mounts fail with ETIMEDOUTs instead EIO on mountd timeouts
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Scott Mayhew <[email protected]>
commit acce94e68a0f346115fd41cdc298197d2d5a59ad upstream.
In very busy v3 environment, rpc.mountd can respond to the NULL procedure but not the MNT procedure in a timely manner causing the MNT procedure to time out. The problem is the mount system call returns EIO which causes the mount to fail, instead of ETIMEDOUT, which would cause the mount to be retried.
This patch sets the RPC_TASK_SOFT|RPC_TASK_TIMEOUT flags to the rpc_call_sync() call in nfs_mount() which causes ETIMEDOUT to be returned on timed out connections.
--- fs/nfs/mount_clnt.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
fs/nfs/mount_clnt.c +1 -1
@@ -181,7 +181,7 @@ int nfs_mount(struct nfs_mount_request *info)else msg.rpc_proc = &mnt_clnt->cl_procinfo[MOUNTPROC_MNT ]; - status =rpc_call_sync (mnt_clnt, &msg,0 ); + status =rpc_call_sync (mnt_clnt, &msg,RPC_TASK_SOFT |RPC_TASK_TIMEOUT );rpc_shutdown_client (mnt_clnt);if (status <0 )
PATCH 48/82 nfs: Show original device name verbatim in /proc/*/mount{s,info}
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ben Hutchings <[email protected]>
commit 97a54868262da1629a3e65121e65b8e8c4419d9f upstream.
Since commit c7f404b ('vfs: new superblock methods to override /proc/*/mount{s,info}'), nfs_path() is used to generate the mounted device name reported back to userland.
nfs_path() always generates a trailing slash when the given dentry is the root of an NFS mount, but userland may expect the original device name to be returned verbatim (as it used to be). Make this canonicalisation optional and change the callers accordingly.
Reference: http://bugs.debian.org/669314
[bwh: Backported to 3.2:
- Adjust context
- nfs_show_devname() still takes a pointer to struct vfsmount]
--- fs/nfs/internal.h | 5 +++-- fs/nfs/namespace.c | 19 ++++++++++++++----- fs/nfs/nfs4namespace.c | 3 ++- fs/nfs/super.c | 2 +- 4 files changed, 20 insertions(+), 9 deletions(-)
fs/nfs/internal.h +3 -2
@@ -274,8 +274,9 @@ extern void nfs_sb_active(struct super_bextern void nfs_sb_deactive (struct super_block *sb);/* namespace.c */ +#define NFS_PATH_CANONICAL 1extern char *nfs_path (char **p,struct dentry *dentry, -char *buffer,ssize_t buflen); +char *buffer,ssize_t buflen,unsigned flags);extern struct vfsmount *nfs_d_automount (struct path *path);#ifdef CONFIG_NFS_V4 rpc_authflavor_t nfs_find_best_sec (struct nfs4_secinfo_flavors *);
@@ -364,7 +365,7 @@ static inline char *nfs_devname(struct d char *buffer, ssize_t buflen) {char *dummy; -return nfs_path (&dummy, dentry, buffer, buflen); +return nfs_path (&dummy, dentry, buffer, buflen,NFS_PATH_CANONICAL ); }/*
fs/nfs/namespace.c +14 -5
@@ -37,6 +37,7 @@ static struct vfsmount *nfs_do_submount(* @dentry - pointer to dentry * @buffer - result buffer * @buflen - length of buffer +* @flags - options (see below) * * Helper function for constructing the server pathname * by arbitrary hashed dentry.
@@ -44,8 +45,14 @@ static struct vfsmount *nfs_do_submount(* This is mainly for use in figuring out the path on the * server side when automounting on top of an existing partition * and in generating /proc/mounts and friends. +* +* Supported flags: +* NFS_PATH_CANONICAL: ensure there is exactly one slash after +* the original device (export) name +* (if unset, the original name is returned verbatim) */ -char *nfs_path (char **p,struct dentry *dentry,char *buffer,ssize_t buflen) +char *nfs_path (char **p,struct dentry *dentry,char *buffer,ssize_t buflen, +unsigned flags) {char *end;int namelen;
@@ -78,7 +85,7 @@ rename_retry:rcu_read_unlock (); goto rename_retry; } -if (*end !='/' ) { +if ((flags &NFS_PATH_CANONICAL ) && *end !='/' ) {if (--buflen <0 ) {spin_unlock (&dentry->d_lock);rcu_read_unlock ();
@@ -95,9 +102,11 @@ rename_retry:return end; } namelen =strlen (base); -/* Strip off excess slashes in base string */ -while (namelen >0 && base[namelen -1 ] =='/' ) - namelen--; +if (flags &NFS_PATH_CANONICAL ) { +/* Strip off excess slashes in base string */ +while (namelen >0 && base[namelen -1 ] =='/' ) + namelen--; + } buflen -= namelen;if (buflen <0 ) {spin_unlock (&dentry->d_lock);
fs/nfs/nfs4namespace.c +2 -1
@@ -57,7 +57,8 @@ Elong:static char *nfs4_path (struct dentry *dentry,char *buffer,ssize_t buflen) {char *limit; -char *path =nfs_path (&limit, dentry, buffer, buflen); +char *path =nfs_path (&limit, dentry, buffer, buflen, +NFS_PATH_CANONICAL );if (!IS_ERR (path)) {char *colon =strchr (path,':' );if (colon && colon < limit)
fs/nfs/super.c +1 -1
@@ -768,7 +768,7 @@ static int nfs_show_devname(struct seq_fint err =0 ;if (!page)return -ENOMEM ; - devname =nfs_path (&dummy, mnt->mnt_root, page,PAGE_SIZE ); + devname =nfs_path (&dummy, mnt->mnt_root, page,PAGE_SIZE ,0 );if (IS_ERR (devname)) err =PTR_ERR (devname);else
PATCH 49/82 target: Dont return success from module_init() if setup fails
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Roland Dreier <[email protected]>
commit 0d0f9dfb31e0a6c92063e235417b42df185b3275 upstream.
If the call to core_dev_release_virtual_lun0() fails, then nothing sets ret to anything other than 0, so even though everything is torn down and freed, target_core_init_configfs() will seem to succeed and the module will be loaded. Fix this by passing the return value on up the chain.
--- drivers/target/target_core_configfs.c | 3 ++- 1 file changed, 2 insertions(+), 1 deletion(-)
drivers/target/target_core_configfs.c +2 -1
@@ -3206,7 +3206,8 @@ static int __init target_core_init_configfs(void)if (ret <0 ) goto out; -if (core_dev_setup_virtual_lun0 () <0 ) + ret =core_dev_setup_virtual_lun0 (); +if (ret <0 ) goto out;return 0 ;
PATCH 50/82 target: Avoid integer overflow in se_dev_align_max_sectors()
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Roland Dreier <[email protected]>
commit 3e03989b5868acf69a391a424dc71fcd6cc48167 upstream.
The expression (max_sectors * block_size) might overflow a u32 (indeed, since iblock sets max_hw_sectors to UINT_MAX, it is guaranteed to overflow and end up with a much-too-small result in many common cases). Fix this by doing an equivalent calculation that doesn't require multiplication.
While we're touching this code, avoid splitting a printk format across two lines and use pr_info(...) instead of printk(KERN_INFO ...).
--- drivers/target/target_core_device.c | 18 +++++++++--------- 1 file changed, 9 insertions(+), 9 deletions(-)
drivers/target/target_core_device.c +9 -9
@@ -835,20 +835,20 @@ int se_dev_check_shutdown(struct se_deviu32 se_dev_align_max_sectors (u32 max_sectors,u32 block_size) { -u32 tmp, aligned_max_sectors; +u32 aligned_max_sectors; +u32 alignment;/* * Limit max_sectors to a PAGE_SIZE aligned value for modern * transport_allocate_data_tasks() operation. */ - tmp =rounddown ((max_sectors * block_size),PAGE_SIZE ); - aligned_max_sectors = (tmp / block_size); -if (max_sectors != aligned_max_sectors) { -printk (KERN_INFO "Rounding down aligned max_sectors from %u" -" to %u\n" , max_sectors, aligned_max_sectors); -return aligned_max_sectors; - } + alignment =max (1ul ,PAGE_SIZE / block_size); + aligned_max_sectors =rounddown (max_sectors, alignment); -return max_sectors; +if (max_sectors != aligned_max_sectors) +pr_info ("Rounding down aligned max_sectors from %u to %u\n" , + max_sectors, aligned_max_sectors); + +return aligned_max_sectors; } void se_dev_set_default_attribs(
PATCH 51/82 iscsi-target: Fix missed wakeup race in TX thread
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Roland Dreier <[email protected]>
commit d5627acba9ae584cf4928af19f7ddf5f6837de32 upstream.
The sleeping code in iscsi_target_tx_thread() is susceptible to the classic missed wakeup race:
- TX thread finishes handle_immediate_queue() and handle_response_queue(), thinks both queues are empty.
- Another thread adds a queue entry and does wake_up_process(), which does nothing because the TX thread is still awake.
- TX thread does schedule_timeout() and sleeps forever.
In practice this can kill an iSCSI connection if for example an initiator does single-threaded writes and the target misses the wakeup window when queueing an R2T; in this case the connection will be stuck until the initiator loses patience and does some task management operation (or kills the connection entirely).
Fix this by converting to wait_event_interruptible(), which does not suffer from this sort of race.
--- drivers/target/iscsi/iscsi_target.c | 4 +++- drivers/target/iscsi/iscsi_target_core.h | 1 + drivers/target/iscsi/iscsi_target_login.c | 1 + drivers/target/iscsi/iscsi_target_util.c | 22 ++++++++++++++++++++-- drivers/target/iscsi/iscsi_target_util.h | 1 + 5 files changed, 26 insertions(+), 3 deletions(-)
drivers/target/iscsi/iscsi_target.c +3 -1
@@ -3719,7 +3719,9 @@ restart:*/ iscsit_thread_check_cpumask (conn, current,1 ); -schedule_timeout_interruptible (MAX_SCHEDULE_TIMEOUT ); +wait_event_interruptible (conn->queues_wq, + !iscsit_conn_all_queues_empty (conn) || + ts->status ==ISCSI_THREAD_SET_RESET );if ((ts->status ==ISCSI_THREAD_SET_RESET ) ||signal_pending (current))
drivers/target/iscsi/iscsi_target_core.h +1 -0
@@ -486,6 +486,7 @@ struct iscsi_tmr_req { };struct iscsi_conn { +wait_queue_head_t queues_wq;/* Authentication Successful for this connection */ u8 auth_complete;/* State connection is currently in */
drivers/target/iscsi/iscsi_target_login.c +1 -0
@@ -41,6 +41,7 @@static int iscsi_login_init_conn (struct iscsi_conn *conn) { +init_waitqueue_head (&conn->queues_wq);INIT_LIST_HEAD (&conn->conn_list);INIT_LIST_HEAD (&conn->conn_cmd_list);INIT_LIST_HEAD (&conn->immed_queue_list);
drivers/target/iscsi/iscsi_target_util.c +20 -2
@@ -488,7 +488,7 @@ void iscsit_add_cmd_to_immediate_queue(atomic_set (&conn->check_immediate_queue,1 );spin_unlock_bh (&conn->immed_queue_lock); -wake_up_process (conn->thread_set->tx_thread); +wake_up (&conn->queues_wq); }struct iscsi_queue_req *iscsit_get_cmd_from_immediate_queue (struct iscsi_conn *conn)
@@ -562,7 +562,7 @@ void iscsit_add_cmd_to_response_queue(atomic_inc (&cmd->response_queue_count);spin_unlock_bh (&conn->response_queue_lock); -wake_up_process (conn->thread_set->tx_thread); +wake_up (&conn->queues_wq); }struct iscsi_queue_req *iscsit_get_cmd_from_response_queue (struct iscsi_conn *conn)
@@ -616,6 +616,24 @@ static void iscsit_remove_cmd_from_response_queue( } } +bool iscsit_conn_all_queues_empty (struct iscsi_conn *conn) +{ +bool empty; + +spin_lock_bh (&conn->immed_queue_lock); + empty =list_empty (&conn->immed_queue_list); +spin_unlock_bh (&conn->immed_queue_lock); + +if (!empty) +return empty; + +spin_lock_bh (&conn->response_queue_lock); + empty =list_empty (&conn->response_queue_list); +spin_unlock_bh (&conn->response_queue_lock); + +return empty; +} +void iscsit_free_queue_reqs_for_conn (struct iscsi_conn *conn) {struct iscsi_queue_req *qr, *qr_tmp;
drivers/target/iscsi/iscsi_target_util.h +1 -0
@@ -25,6 +25,7 @@ extern struct iscsi_queue_req *iscsit_get_cmd_from_immediate_queue(struct iscsi_extern void iscsit_add_cmd_to_response_queue (struct iscsi_cmd *,struct iscsi_conn *,u8 );extern struct iscsi_queue_req *iscsit_get_cmd_from_response_queue (struct iscsi_conn *);extern void iscsit_remove_cmd_from_tx_queues (struct iscsi_cmd *,struct iscsi_conn *); +extern bool iscsit_conn_all_queues_empty (struct iscsi_conn *);extern void iscsit_free_queue_reqs_for_conn (struct iscsi_conn *);extern void iscsit_release_cmd (struct iscsi_cmd *);extern void iscsit_free_cmd (struct iscsi_cmd *);
PATCH 52/82 DRM/Radeon: Fix Load Detection on legacy primary DAC.
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Egbert Eich <[email protected]>
commit 83325d072185899b706de2956170b246585aaec9 upstream.
An uninitialized variable led to broken load detection.
--- drivers/gpu/drm/radeon/radeon_legacy_encoders.c | 1 + 1 file changed, 1 insertion(+)
drivers/gpu/drm/radeon/radeon_legacy_encoders.c +1 -0
@@ -671,6 +671,7 @@ static enum drm_connector_status radeon_legacy_primary_dac_detect(struct drm_enc tmp |=RADEON_DAC_RANGE_CNTL_PS2 |RADEON_DAC_CMP_EN ;WREG32 (RADEON_DAC_CNTL , tmp); + tmp = dac_macro_cntl; tmp &= ~(RADEON_DAC_PDWN_R |RADEON_DAC_PDWN_G |RADEON_DAC_PDWN_B );
PATCH 53/82 cifs: fix potential buffer overrun in cifs.idmap handling code
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Jeff Layton <[email protected]>
commit 36960e440ccf94349c09fb944930d3bfe4bc473f upstream.
The userspace cifs.idmap program generally works with the wbclient libs to generate binary SIDs in userspace. That program defines the struct that holds these values as having a max of 15 subauthorities. The kernel idmapping code however limits that value to 5.
When the kernel copies those values around though, it doesn't sanity check the num_subauths value handed back from userspace or from the server. It's possible therefore for userspace to hand us back a bogus num_subauths value (or one that's valid, but greater than 5) that could cause the kernel to walk off the end of the cifs_sid->sub_auths array.
Fix this by defining a new routine for copying sids and using that in all of the places that copy it. If we end up with a sid that's longer than expected then this approach will just lop off the "extra" subauths, but that's basically what the code does today already. Better approaches might be to fix this code to reject SIDs with >5 subauths, or fix it to handle the subauths array dynamically.
At the same time, change the kernel to check the length of the data returned by userspace. If it's shorter than struct cifs_sid, reject it and return -EIO. If that happens we'll end up with fields that are basically uninitialized.
Long term, it might make sense to redefine cifs_sid using a flexarray at the end, to allow for variable-length subauth lists, and teach the code to handle the case where the subauths array being passed in from userspace is shorter than 5 elements.
Note too, that I don't consider this a security issue since you'd need a compromised cifs.idmap program. If you have that, you can do all sorts of nefarious stuff. Still, this is probably reasonable for stable.
--- fs/cifs/cifsacl.c | 49 ++++++++++++++++++++----------------------------- 1 file changed, 20 insertions(+), 29 deletions(-)
fs/cifs/cifsacl.c +20 -29
@@ -225,6 +225,13 @@ sid_to_str(struct cifs_sid *sidptr, char *sidstr) }static void +cifs_copy_sid (struct cifs_sid *dst,const struct cifs_sid *src) +{ +memcpy (dst, src,sizeof (*dst)); + dst->num_subauth =min_t (u8, src->num_subauth,NUM_SUBAUTHS ); +} + +static void id_rb_insert (struct rb_root *root,struct cifs_sid *sidptr,struct cifs_sid_id **psidid,char *typestr) {
@@ -248,7 +255,7 @@ id_rb_insert(struct rb_root *root, struct cifs_sid *sidptr, } } -memcpy (&(*psidid)->sid, sidptr,sizeof (struct cifs_sid )); +cifs_copy_sid (&(*psidid)->sid, sidptr); (*psidid)->time = jiffies - (SID_MAP_RETRY +1 ); (*psidid)->refcount =0 ;
@@ -354,7 +361,7 @@ id_to_sid(unsigned long cid, uint sidtype, struct cifs_sid *ssid)* any fields of the node after a reference is put . */ if (test_bit (SID_ID_MAPPED , &psidid->state)) { -memcpy (ssid, &psidid->sid,sizeof (struct cifs_sid )); +cifs_copy_sid (ssid, &psidid->sid); psidid->time = jiffies;/* update ts for accessing */ goto id_sid_out; }
@@ -370,14 +377,14 @@ id_to_sid(unsigned long cid, uint sidtype, struct cifs_sid *ssid)if (IS_ERR (sidkey)) { rc = -EINVAL ;cFYI (1 ,"%s: Can't map and id to a SID" , __func__); + }else if (sidkey->datalen <sizeof (struct cifs_sid )) { + rc = -EIO ; +cFYI (1 ,"%s: Downcall contained malformed key " +"(datalen=%hu)" , __func__, sidkey->datalen); }else { lsid = (struct cifs_sid *)sidkey->payload.data; -memcpy (&psidid->sid, lsid, - sidkey->datalen <sizeof (struct cifs_sid ) ? - sidkey->datalen :sizeof (struct cifs_sid )); -memcpy (ssid, &psidid->sid, - sidkey->datalen <sizeof (struct cifs_sid ) ? - sidkey->datalen :sizeof (struct cifs_sid )); +cifs_copy_sid (&psidid->sid, lsid); +cifs_copy_sid (ssid, &psidid->sid);set_bit (SID_ID_MAPPED , &psidid->state);key_put (sidkey);kfree (psidid->sidstr);
@@ -396,7 +403,7 @@ id_to_sid(unsigned long cid, uint sidtype, struct cifs_sid *ssid)return rc; }if (test_bit (SID_ID_MAPPED , &psidid->state)) -memcpy (ssid, &psidid->sid,sizeof (struct cifs_sid )); +cifs_copy_sid (ssid, &psidid->sid);else rc = -EINVAL ; }
@@ -675,8 +682,6 @@ int compare_sids(const struct cifs_sid *ctsid, const struct cifs_sid *cwsid)static void copy_sec_desc (const struct cifs_ntsd *pntsd,struct cifs_ntsd *pnntsd,__u32 sidsoffset) { -int i; -struct cifs_sid *owner_sid_ptr, *group_sid_ptr;struct cifs_sid *nowner_sid_ptr, *ngroup_sid_ptr;
@@ -692,26 +697,14 @@ static void copy_sec_desc(const struct cifs_ntsd *pntsd, owner_sid_ptr = (struct cifs_sid *)((char *)pntsd +le32_to_cpu (pntsd->osidoffset)); nowner_sid_ptr = (struct cifs_sid *)((char *)pnntsd + sidsoffset); - - nowner_sid_ptr->revision = owner_sid_ptr->revision; - nowner_sid_ptr->num_subauth = owner_sid_ptr->num_subauth; -for (i =0 ; i <6 ; i++) - nowner_sid_ptr->authority[i] = owner_sid_ptr->authority[i]; -for (i =0 ; i <5 ; i++) - nowner_sid_ptr->sub_auth[i] = owner_sid_ptr->sub_auth[i]; +cifs_copy_sid (nowner_sid_ptr, owner_sid_ptr);/* copy group sid */ group_sid_ptr = (struct cifs_sid *)((char *)pntsd +le32_to_cpu (pntsd->gsidoffset)); ngroup_sid_ptr = (struct cifs_sid *)((char *)pnntsd + sidsoffset +sizeof (struct cifs_sid )); - - ngroup_sid_ptr->revision = group_sid_ptr->revision; - ngroup_sid_ptr->num_subauth = group_sid_ptr->num_subauth; -for (i =0 ; i <6 ; i++) - ngroup_sid_ptr->authority[i] = group_sid_ptr->authority[i]; -for (i =0 ; i <5 ; i++) - ngroup_sid_ptr->sub_auth[i] = group_sid_ptr->sub_auth[i]; +cifs_copy_sid (ngroup_sid_ptr, group_sid_ptr);return ; }
@@ -1120,8 +1113,7 @@ static int build_sec_desc(struct cifs_ntsd *pntsd, struct cifs_ntsd *pnntsd,kfree (nowner_sid_ptr);return rc; } -memcpy (owner_sid_ptr, nowner_sid_ptr, -sizeof (struct cifs_sid )); +cifs_copy_sid (owner_sid_ptr, nowner_sid_ptr);kfree (nowner_sid_ptr); *aclflag =CIFS_ACL_OWNER ; }
@@ -1139,8 +1131,7 @@ static int build_sec_desc(struct cifs_ntsd *pntsd, struct cifs_ntsd *pnntsd,kfree (ngroup_sid_ptr);return rc; } -memcpy (group_sid_ptr, ngroup_sid_ptr, -sizeof (struct cifs_sid )); +cifs_copy_sid (group_sid_ptr, ngroup_sid_ptr);kfree (ngroup_sid_ptr); *aclflag =CIFS_ACL_GROUP ; }
PATCH 54/82 ALSA: hda: Cirrus: Fix coefficient index for beep configuration
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Alexander Stein <[email protected]>
commit 5a83b4b5a391f07141b157ac9daa51c409e71ab5 upstream.
--- sound/pci/hda/patch_cirrus.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
sound/pci/hda/patch_cirrus.c +1 -1
@@ -1107,7 +1107,7 @@ static const struct hda_verb cs_coef_init_verbs[] = { | 0x0400 /* Disable Coefficient Auto increment */ )},/* Beep */ - {0x11, AC_VERB_SET_COEF_INDEX, IDX_DAC_CFG}, + {0x11, AC_VERB_SET_COEF_INDEX, IDX_BEEP_CFG}, {0x11, AC_VERB_SET_PROC_COEF, 0x0007}, /* Enable Beep thru DAC1/2/3 */ {} /* terminator */
PATCH 55/82 ALSA: HDA: Fix digital microphone on CS420x
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Daniel J Blueman <[email protected]>
commit 16337e028a6dae9fbdd718c0d42161540a668ff3 upstream.
Correctly enable the digital microphones with the right bits in the right coeffecient registers on Cirrus CS4206/7 codecs. It also prevents misconfiguring ADC1/2.
This fixes the digital mic on the Macbook Pro 10,1/Retina.
--- sound/pci/hda/patch_cirrus.c | 14 +++++++++----- 1 file changed, 9 insertions(+), 5 deletions(-)
sound/pci/hda/patch_cirrus.c +9 -5
@@ -93,8 +93,8 @@ enum {#define CS420X_VENDOR_NID 0x11#define CS_DIG_OUT1_PIN_NID 0x10#define CS_DIG_OUT2_PIN_NID 0x15 -#define CS_DMIC1_PIN_NID 0x12 -#define CS_DMIC2_PIN_NID 0x0e +#define CS_DMIC1_PIN_NID 0x0e +#define CS_DMIC2_PIN_NID 0x12/* coef indices */ #define IDX_SPDIF_STAT 0x0000
@@ -1088,14 +1088,18 @@ static void init_input(struct hda_codeccs_automic (codec); coef =0x000a ;/* ADC1/2 - Digital and Analog Soft Ramp */ +cs_vendor_coef_set (codec,IDX_ADC_CFG , coef); + + coef =cs_vendor_coef_get (codec,IDX_BEEP_CFG );if (is_active_pin (codec,CS_DMIC2_PIN_NID )) - coef |=0x0500 ;/* DMIC2 2 chan on, GPIO1 off */ + coef |=1 <<4 ;/* DMIC2 2 chan on, GPIO1 off */ if (is_active_pin (codec,CS_DMIC1_PIN_NID )) - coef |=0x1800 ;/* DMIC1 2 chan on, GPIO0 off + coef |=1 <<3 ;/* DMIC1 2 chan on, GPIO0 off * No effect if SPDIF_OUT2 is * selected in IDX_SPDIF_CTL. */ -cs_vendor_coef_set (codec,IDX_ADC_CFG , coef); + +cs_vendor_coef_set (codec,IDX_BEEP_CFG , coef); } }
PATCH 56/82 ALSA: hda - Force to reset IEC958 status bits for AD codecs
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit ae24c3191ba2ab03ec6b4be323e730e00404b4b6 upstream.
Several bug reports suggest that the forcibly resetting IEC958 status bits is required for AD codecs to get the SPDIF output working properly after changing streams.
Original fix credit to Javeed Shaikh.
--- sound/pci/hda/patch_analog.c | 1 + 1 file changed, 1 insertion(+)
sound/pci/hda/patch_analog.c +1 -0
@@ -545,6 +545,7 @@ static int ad198x_build_pcms(struct hda_codec *codec)if (spec->multiout.dig_out_nid) { info++; codec->num_pcms++; + codec->spdif_status_reset =1 ; info->name ="AD198x Digital" ; info->pcm_type =HDA_PCM_TYPE_SPDIF ; info->stream[SNDRV_PCM_STREAM_PLAYBACK ] = ad198x_pcm_digital_playback;
PATCH 57/82 hwmon: (w83627ehf) Force initial bank selection
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Jean Delvare <[email protected]>
commit 3300fb4f88688029fff8dfb9ec0734f6e4cba3e7 upstream.
Don't assume bank 0 is selected at device probe time. This may not be the case. Force bank selection at first register access to guarantee that we read the right registers upon driver loading.
--- drivers/hwmon/w83627ehf.c | 1 + 1 file changed, 1 insertion(+)
drivers/hwmon/w83627ehf.c +1 -0
@@ -2083,6 +2083,7 @@ static int __devinit w83627ehf_probe(struct platform_device *pdev)mutex_init (&data->lock);mutex_init (&data->update_lock); data->name = w83627ehf_device_names[sio_data->kind]; + data->bank =0xff ;/* Force initial bank selection */ platform_set_drvdata (pdev, data);/* 627EHG and 627EHF have 10 voltage inputs; 627DHG and 667HG have 9 */
PATCH 58/82 drm: restore open_count if drm_setup fails
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Ilija Hadzic <[email protected]>
commit 0f1cb1bd94a9c967cd4ad3de51cfdabe61eb5dcc upstream.
If drm_setup (called at first open) fails, the whole open call has failed, so we should not keep the open_count incremented.
--- drivers/gpu/drm/drm_fops.c | 5 ++++- 1 file changed, 4 insertions(+), 1 deletion(-)
drivers/gpu/drm/drm_fops.c +4 -1
@@ -135,8 +135,11 @@ int drm_open(struct inode *inode, struct file *filp) retcode =drm_open_helper (inode, filp, dev);if (!retcode) {atomic_inc (&dev->counts[_DRM_STAT_OPENS]); -if (!dev->open_count++) +if (!dev->open_count++) { retcode =drm_setup (dev); +if (retcode) + dev->open_count--; + } }if (!retcode) {mutex_lock (&dev->struct_mutex);
PATCH 59/82 ALSA: hda - Fix empty DAC filling in patch_via.c
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit 5b3761954dac2d1393beef8210eb8cee81d16b8d upstream.
In via_auto_fill_adc_nids(), the parser tries to fill dac_nids[] at the point of the current line-out (i). When no valid path is found for this output, this results in dac = 0, thus it creates a hole in dac_nids[]. This confuses is_empty_dac() and trims the detected DAC in later reference.
This patch fixes the bug by appending DAC properly to dac_nids[] in via_auto_fill_adc_nids().
--- sound/pci/hda/patch_via.c | 11 ++++------- 1 file changed, 4 insertions(+), 7 deletions(-)
sound/pci/hda/patch_via.c +4 -7
@@ -1809,11 +1809,11 @@ static int via_auto_fill_dac_nids(struct hda_codec *codec) {struct via_spec *spec = codec->spec;const struct auto_pin_cfg *cfg = &spec->autocfg; -int i, dac_num; +int i;hda_nid_t nid; + spec->multiout.num_dacs =0 ; spec->multiout.dac_nids = spec->private_dac_nids; - dac_num =0 ;for (i =0 ; i < cfg->line_outs; i++) {hda_nid_t dac =0 ; nid = cfg->line_out_pins[i];
@@ -1824,16 +1824,13 @@ static int via_auto_fill_dac_nids(struct hda_codec *codec)if (!i &&parse_output_path (codec, nid, dac,1 , &spec->out_mix_path)) dac = spec->out_mix_path.path[0 ]; -if (dac) { - spec->private_dac_nids[i] = dac; - dac_num++; - } +if (dac) + spec->private_dac_nids[spec->multiout.num_dacs++] = dac; }if (!spec->out_path[0 ].depth && spec->out_mix_path.depth) { spec->out_path[0 ] = spec->out_mix_path; spec->out_mix_path.depth =0 ; } - spec->multiout.num_dacs = dac_num;return 0 ; }
PATCH 60/82 ALSA: hda - Fix invalid connections in VT1802 codec
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit ef4da45828603df57e5e21b8aa21a66ce309f79b upstream.
VT1802 codec provides the invalid connection lists of NID 0x24 and 0x33 containing the routes to a non-exist widget 0x3e. This confuses the auto-parser. Fix it up in the driver by overriding these connections.
--- sound/pci/hda/patch_via.c | 14 ++++++++++++++ 1 file changed, 14 insertions(+)
sound/pci/hda/patch_via.c +14 -0
@@ -3686,6 +3686,18 @@ static void set_widgets_power_state_vt20 AC_VERB_SET_POWER_STATE, AC_PWRST_D3); } +/* NIDs 0x24 and 0x33 on VT1802 have connections to non-existing NID 0x3e +* Replace this with mixer NID 0x1c +*/ +static void fix_vt1802_connections (struct hda_codec *codec) +{ +static hda_nid_t conn_24[] = {0x14 ,0x1c }; +static hda_nid_t conn_33[] = {0x1c }; + +snd_hda_override_conn_list (codec,0x24 ,ARRAY_SIZE (conn_24), conn_24); +snd_hda_override_conn_list (codec,0x33 ,ARRAY_SIZE (conn_33), conn_33); +} +/* patch for vt2002P */ static int patch_vt2002P (struct hda_codec *codec) {
@@ -3700,6 +3712,8 @@ static int patch_vt2002P(struct hda_code spec->aa_mix_nid =0x21 ;override_mic_boost (codec,0x2b ,0 ,3 ,40 );override_mic_boost (codec,0x29 ,0 ,3 ,40 ); +if (spec->codec_type ==VT1802 ) +fix_vt1802_connections (codec);add_secret_dac_path (codec);/* automatic parse from the BIOS config */
PATCH 61/82 ALSA: hda - Add new codec ALC668 and ALC900 (default name ALC1150)
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Kailang Yang <[email protected]>
commit 19a62823eae453619604636082085812c14ee391 upstream.
--- sound/pci/hda/patch_realtek.c | 2 ++ 1 file changed, 2 insertions(+)
sound/pci/hda/patch_realtek.c +2 -0
@@ -7077,6 +7077,7 @@ static const struct hda_codec_preset snd_hda_preset_realtek[] = { .patch = patch_alc662 }, { .id = 0x10ec0663, .name = "ALC663", .patch = patch_alc662 }, { .id = 0x10ec0665, .name = "ALC665", .patch = patch_alc662 }, + { .id = 0x10ec0668, .name = "ALC668", .patch = patch_alc662 }, { .id = 0x10ec0670, .name = "ALC670", .patch = patch_alc662 }, { .id = 0x10ec0680, .name = "ALC680", .patch = patch_alc680 }, { .id = 0x10ec0880, .name = "ALC880", .patch = patch_alc880 },
@@ -7094,6 +7095,7 @@ static const struct hda_codec_preset snd_hda_preset_realtek[] = { { .id = 0x10ec0889, .name = "ALC889", .patch = patch_alc882 }, { .id = 0x10ec0892, .name = "ALC892", .patch = patch_alc662 }, { .id = 0x10ec0899, .name = "ALC898", .patch = patch_alc882 }, + { .id = 0x10ec0900, .name = "ALC1150", .patch = patch_alc882 }, {}/* terminator */ };
PATCH 62/82 ALSA: Fix card refcount unbalance
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takashi Iwai <[email protected]>
commit 8bb4d9ce08b0a92ca174e41d92c180328f86173f upstream.
There are uncovered cases whether the card refcount introduced by the commit a0830dbd isn't properly increased or decreased:
- OSS PCM and mixer success paths
- When lookup function gets NULL
This patch fixes these places.
Bugzilla: https://bugzilla.kernel.org/show_bug.cgi?id=50251
--- sound/core/oss/mixer_oss.c | 1 + sound/core/oss/pcm_oss.c | 1 + sound/core/pcm_native.c | 6 ++++-- sound/core/sound.c | 2 +- sound/core/sound_oss.c | 2 +- 5 files changed, 8 insertions(+), 4 deletions(-)
sound/core/oss/mixer_oss.c +1 -0
@@ -76,6 +76,7 @@ static int snd_mixer_oss_open(struct inode *inode, struct file *file)snd_card_unref (card);return -EFAULT ; } +snd_card_unref (card);return 0 ; }
sound/core/oss/pcm_oss.c +1 -0
@@ -2454,6 +2454,7 @@ static int snd_pcm_oss_open(struct inode *inode, struct file *file)mutex_unlock (&pcm->open_mutex);if (err <0 ) goto __error; +snd_card_unref (pcm->card);return err; __error:
sound/core/pcm_native.c +4 -2
@@ -2122,7 +2122,8 @@ static int snd_pcm_playback_open(struct inode *inode, struct file *file) pcm =snd_lookup_minor_data (iminor (inode),SNDRV_DEVICE_TYPE_PCM_PLAYBACK ); err =snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_PLAYBACK ); -snd_card_unref (pcm->card); +if (pcm) +snd_card_unref (pcm->card);return err; }
@@ -2135,7 +2136,8 @@ static int snd_pcm_capture_open(struct inode *inode, struct file *file) pcm =snd_lookup_minor_data (iminor (inode),SNDRV_DEVICE_TYPE_PCM_CAPTURE ); err =snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_CAPTURE ); -snd_card_unref (pcm->card); +if (pcm) +snd_card_unref (pcm->card);return err; }
sound/core/sound.c +1 -1
@@ -114,7 +114,7 @@ void *snd_lookup_minor_data(unsigned int minor, int type) mreg = snd_minors[minor];if (mreg && mreg->type == type) { private_data = mreg->private_data; -if (mreg->card_ptr) +if (private_data && mreg->card_ptr)atomic_inc (&mreg->card_ptr->refcount); }else private_data =NULL ;
sound/core/sound_oss.c +1 -1
@@ -54,7 +54,7 @@ void *snd_lookup_oss_minor_data(unsigned int minor, int type) mreg = snd_oss_minors[minor];if (mreg && mreg->type == type) { private_data = mreg->private_data; -if (mreg->card_ptr) +if (private_data && mreg->card_ptr)atomic_inc (&mreg->card_ptr->refcount); }else private_data =NULL ;
PATCH 63/82 xfs: fix reading of wrapped log data
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Dave Chinner <[email protected]>
commit 6ce377afd1755eae5c93410ca9a1121dfead7b87 upstream.
Commit 4439647 ("xfs: reset buffer pointers before freeing them") in 3.0-rc1 introduced a regression when recovering log buffers that wrapped around the end of log. The second part of the log buffer at the start of the physical log was being read into the header buffer rather than the data buffer, and hence recovery was seeing garbage in the data buffer when it got to the region of the log buffer that was incorrectly read.
--- fs/xfs/xfs_log_recover.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
fs/xfs/xfs_log_recover.c +1 -1
@@ -3541,7 +3541,7 @@ xlog_do_recovery_pass(* - order is important. */ error =xlog_bread_offset (log,0 , - bblks - split_bblks, hbp, + bblks - split_bblks, dbp, offset +BBTOB (split_bblks));if (error) goto bread_err2;
PATCH 64/82 fanotify: fix missing break
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Eric Paris <[email protected]>
commit 848561d368751a1c0f679b9f045a02944506a801 upstream.
Anders Blomdell noted in 2010 that Fanotify lost events and provided a test case. Eric Paris confirmed it was a bug and posted a fix to the list
https://groups.google.com/forum/?fromgroups=#!topic/linux.kernel/RrJfTfyW2BE
but never applied it. Repeated attempts over time to actually get him to apply it have never had a reply from anyone who has raised it
So apply it anyway
--- fs/notify/fanotify/fanotify.c | 1 + 1 file changed, 1 insertion(+)
fs/notify/fanotify/fanotify.c +1 -0
@@ -21,6 +21,7 @@ static bool should_merge(struct fsnotify_event *old, struct fsnotify_event *new)if ((old->path.mnt == new->path.mnt) && (old->path.dentry == new->path.dentry))return true; +break ;case (FSNOTIFY_EVENT_NONE ):return true;default :
PATCH 65/82 mm: bugfix: set current->reclaim_state to NULL while returning from kswapd()
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Takamori Yamaguchi <[email protected]>
commit b0a8cc58e6b9aaae3045752059e5e6260c0b94bc upstream.
In kswapd(), set current->reclaim_state to NULL before returning, as current->reclaim_state holds reference to variable on kswapd()'s stack.
In rare cases, while returning from kswapd() during memory offlining, __free_slab() and freepages() can access the dangling pointer of current->reclaim_state.
--- mm/vmscan.c | 2 ++ 1 file changed, 2 insertions(+)
mm/vmscan.c +2 -0
@@ -3017,6 +3017,8 @@ static int kswapd(void *p) &balanced_classzone_idx); } } + + current->reclaim_state =NULL ;return 0 ; }
PATCH 66/82 drm/vmwgfx: Fix hibernation device reset
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Thomas Hellstrom <[email protected]>
commit 95e8f6a21996c4cc2c4574b231c6e858b749dce3 upstream.
The device would not reset properly when resuming from hibernation.
--- drivers/gpu/drm/vmwgfx/vmwgfx_drv.c | 5 +++++ 1 file changed, 5 insertions(+)
drivers/gpu/drm/vmwgfx/vmwgfx_drv.c +5 -0
@@ -1098,6 +1098,11 @@ static void vmw_pm_complete(struct device *kdev)struct drm_device *dev =pci_get_drvdata (pdev);struct vmw_private *dev_priv =vmw_priv (dev); +mutex_lock (&dev_priv->hw_mutex); +vmw_write (dev_priv,SVGA_REG_ID ,SVGA_ID_2 ); + (void )vmw_read (dev_priv,SVGA_REG_ID ); +mutex_unlock (&dev_priv->hw_mutex); +/** * Reclaim 3d reference held by fbdev and potentially * start fifo.
PATCH 67/82 drm/vmwgfx: Fix a case where the code would BUG when trying to pin GMR memory
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Thomas Hellstrom <[email protected]>
commit afcc87aa6a233e52df73552dc1dc9ae3881b7cc8 upstream.
--- drivers/gpu/drm/vmwgfx/vmwgfx_dmabuf.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/gpu/drm/vmwgfx/vmwgfx_dmabuf.c +1 -1
@@ -306,7 +306,7 @@ void vmw_bo_pin(struct ttm_buffer_object *bo, bool pin)BUG_ON (!atomic_read (&bo->reserved));BUG_ON (old_mem_type !=TTM_PL_VRAM && - old_mem_type !=VMW_PL_FLAG_GMR ); + old_mem_type !=VMW_PL_GMR ); pl_flags =TTM_PL_FLAG_VRAM |VMW_PL_FLAG_GMR |TTM_PL_FLAG_CACHED ;if (pin)
PATCH 68/82 sctp: fix call to SCTP_CMD_PROCESS_SACK in sctp_cmd_interpreter()
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Zijie Pan <[email protected]>
[ Upstream commit f6e80abeab928b7c47cc1fbf53df13b4398a2bec ]
Bug introduced by commit edfee0339e681a784ebacec7e8c2dc97dc6d2839 (sctp: check src addr when processing SACK to update transport state)
--- net/sctp/sm_sideeffect.c | 3 ++- 1 file changed, 2 insertions(+), 1 deletion(-)
net/sctp/sm_sideeffect.c +2 -1
@@ -1604,8 +1604,9 @@ static int sctp_cmd_interpreter(sctp_event_t event_type, asoc->outqueue.outstanding_bytes; sackh.num_gap_ack_blocks =0 ; sackh.num_dup_tsns =0 ; + chunk->subh.sack_hdr = &sackh;sctp_add_cmd_sf (commands,SCTP_CMD_PROCESS_SACK , -SCTP_SACKH (&sackh)); +SCTP_CHUNK (chunk));break ;case SCTP_CMD_DISCARD_PACKET :
PATCH 69/82 netlink: use kfree_rcu() in netlink_release()
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Eric Dumazet <[email protected]>
[ Upstream commit 6d772ac5578f711d1ce7b03535d1c95bffb21dff ]
On some suspend/resume operations involving wimax device, we have noticed some intermittent memory corruptions in netlink code.
Stéphane Marchesin tracked this corruption in netlink_update_listeners() and suggested a patch.
It appears netlink_release() should use kfree_rcu() instead of kfree() for the listeners structure as it may be used by other cpus using RCU protection.
netlink_release() must set to NULL the listeners pointer when it is about to be freed.
Also have to protect netlink_update_listeners() and netlink_has_listeners() if listeners is NULL.
Add a nl_deref_protected() lockdep helper to properly document which locks protects us.
--- net/netlink/af_netlink.c | 19 +++++++++++++++---- 1 file changed, 15 insertions(+), 4 deletions(-)
net/netlink/af_netlink.c +15 -4
@@ -137,6 +137,8 @@ static void netlink_destroy_callback(struct netlink_callback *cb);static DEFINE_RWLOCK (nl_table_lock);static atomic_t nl_table_users =ATOMIC_INIT (0 ); +#define nl_deref_protected (X ) rcu_dereference_protected(X, lockdep_is_held(&nl_table_lock)); +static ATOMIC_NOTIFIER_HEAD (netlink_chain);static u32 netlink_group_mask (u32 group)
@@ -331,6 +333,11 @@ netlink_update_listeners(struct sock *sk)struct hlist_node *node;unsigned long mask;unsigned int i; +struct listeners *listeners; + + listeners =nl_deref_protected (tbl->listeners); +if (!listeners) +return ;for (i =0 ; i <NLGRPLONGS (tbl->groups); i++) { mask =0 ;
@@ -338,7 +345,7 @@ netlink_update_listeners(struct sock *sk)if (i <NLGRPLONGS (nlk_sk (sk)->ngroups)) mask |=nlk_sk (sk)->groups[i]; } - tbl->listeners->masks[i] = mask; + listeners->masks[i] = mask; }/* this function is only called with the netlink table "grabbed", which * makes sure updates are visible before bind or setsockopt return. */
@@ -519,7 +526,11 @@ static int netlink_release(struct socket *sock)if (netlink_is_kernel (sk)) {BUG_ON (nl_table[sk->sk_protocol].registered ==0 );if (--nl_table[sk->sk_protocol].registered ==0 ) { -kfree (nl_table[sk->sk_protocol].listeners); +struct listeners *old; + + old =nl_deref_protected (nl_table[sk->sk_protocol].listeners); +RCU_INIT_POINTER (nl_table[sk->sk_protocol].listeners,NULL ); +kfree_rcu (old, rcu); nl_table[sk->sk_protocol].module =NULL ; nl_table[sk->sk_protocol].registered =0 ; }
@@ -950,7 +961,7 @@ int netlink_has_listeners(struct sock *sk, unsigned int group)rcu_read_lock (); listeners =rcu_dereference (nl_table[sk->sk_protocol].listeners); -if (group -1 < nl_table[sk->sk_protocol].groups) +if (listeners && group -1 < nl_table[sk->sk_protocol].groups) res =test_bit (group -1 , listeners->masks);rcu_read_unlock ();
@@ -1584,7 +1595,7 @@ int __netlink_change_ngroups(struct sock *sk, unsigned int groups) new =kzalloc (sizeof (*new) +NLGRPSZ (groups),GFP_ATOMIC );if (!new)return -ENOMEM ; - old =rcu_dereference_protected (tbl->listeners,1 ); + old =nl_deref_protected (tbl->listeners);memcpy (new->masks, old->masks,NLGRPSZ (tbl->groups));rcu_assign_pointer (tbl->listeners, new);
PATCH 70/82 tcp: fix FIONREAD/SIOCINQ
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Eric Dumazet <[email protected]>
[ Upstream commit a3374c42aa5f7237e87ff3b0622018636b0c847e ]
tcp_ioctl() tries to take into account if tcp socket received a FIN to report correct number bytes in receive queue.
But its flaky because if the application ate the last skb, we return 1 instead of 0.
Correct way to detect that FIN was received is to test SOCK_DONE.
--- net/ipv4/tcp.c | 8 +++----- 1 file changed, 3 insertions(+), 5 deletions(-)
net/ipv4/tcp.c +3 -5
@@ -481,14 +481,12 @@ int tcp_ioctl(struct sock *sk, int cmd, unsigned long arg) !tp->urg_data || before(tp->urg_seq, tp->copied_seq) || !before(tp->urg_seq, tp->rcv_nxt)) { -struct sk_buff *skb; answ = tp->rcv_nxt - tp->copied_seq; -/* Subtract 1, if FIN is in queue. */ - skb =skb_peek_tail (&sk->sk_receive_queue); -if (answ && skb) - answ -=tcp_hdr (skb)->fin; +/* Subtract 1, if FIN was received */ +if (answ &&sock_flag (sk,SOCK_DONE )) + answ--; } else answ = tp->urg_seq - tp->copied_seq;release_sock (sk);
PATCH 71/82 ipv6: Set default hoplimit as zero.
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Li RongQing <[email protected]>
[ Upstream commit 14edd87dc67311556f1254a8f29cf4dd6cb5b7d1 ]
Commit a02e4b7dae4551(Demark default hoplimit as zero) only changes the hoplimit checking condition and default value in ip6_dst_hoplimit, not zeros all hoplimit default value.
Keep the zeroing ip6_template_metrics[RTAX_HOPLIMIT - 1] to force it as const, cause as a37e6e344910(net: force dst_default_metrics to const section)
--- net/ipv6/route.c | 4 ++-- 1 file changed, 2 insertions(+), 2 deletions(-)
net/ipv6/route.c +2 -2
@@ -185,7 +185,7 @@ static struct dst_ops ip6_dst_blackhole_ops = { };static const u32 ip6_template_metrics[RTAX_MAX ] = { - [RTAX_HOPLIMIT -1 ] =255 , + [RTAX_HOPLIMIT -1 ] =0 , };static struct rt6_info ip6_null_entry_template = {
@@ -1097,7 +1097,7 @@ struct dst_entry *icmp6_dst_alloc(struct net_device *dev,ipv6_addr_copy (&rt->rt6i_dst.addr, addr); rt->rt6i_dst.plen =128 ; rt->rt6i_idev = idev; -dst_metric_set (&rt->dst,RTAX_HOPLIMIT ,255 ); +dst_metric_set (&rt->dst,RTAX_HOPLIMIT ,0 );spin_lock_bh (&icmp6_dst_lock); rt->dst.next = icmp6_dst_gc_list;
PATCH 72/82 net: usb: Fix memory leak on Tx data path
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Hemant Kumar <[email protected]>
[ Upstream commit 39707c2a3ba5011038b363f84d37c8a98d2d9db1 ]
Driver anchors the tx urbs and defers the urb submission if a transmit request comes when the interface is suspended. Anchoring urb increments the urb reference count. These deferred urbs are later accessed by calling usb_get_from_anchor() for submission during interface resume. usb_get_from_anchor() unanchors the urb but urb reference count remains same. This causes the urb reference count to remain non-zero after usb_free_urb() gets called and urb never gets freed. Hence call usb_put_urb() after anchoring the urb to properly balance the reference count for these deferred urbs. Also, unanchor these deferred urbs during disconnect, to free them up.
--- drivers/net/usb/usbnet.c | 3 +++ 1 file changed, 3 insertions(+)
drivers/net/usb/usbnet.c +3 -0
@@ -1156,6 +1156,7 @@ netdev_tx_t usbnet_start_xmit (struct sk_buff *skb,usb_anchor_urb (urb, &dev->deferred);/* no use to process more packets */ netif_stop_queue (net); +usb_put_urb (urb);spin_unlock_irqrestore (&dev->txq.lock, flags);netdev_dbg (dev->net,"Delaying transmission for resumption\n" ); goto deferred;
@@ -1297,6 +1298,8 @@ void usbnet_disconnect (struct usb_interface *intf)cancel_work_sync (&dev->kevent); +usb_scuttle_anchored_urbs (&dev->deferred); +if (dev->driver_info->unbind) dev->driver_info->unbind (dev, intf);
PATCH 73/82 net: fix divide by zero in tcp algorithm illinois
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Jesper Dangaard Brouer <[email protected]>
[ Upstream commit 8f363b77ee4fbf7c3bbcf5ec2c5ca482d396d664 ]
Reading TCP stats when using TCP Illinois congestion control algorithm can cause a divide by zero kernel oops.
The division by zero occur in tcp_illinois_info() at:
do_div(t, ca->cnt_rtt);
where ca->cnt_rtt can become zero (when rtt_reset is called)
Steps to Reproduce:
1. Register tcp_illinois:
# sysctl -w net.ipv4.tcp_congestion_control=illinois
2. Monitor internal TCP information via command "ss -i"
# watch -d ss -i
3. Establish new TCP conn to machineEither it fails at the initial conn, or else it needs to wait for a loss or a reset.
This is only related to reading stats. The function avg_delay() also performs the same divide, but is guarded with a (ca->cnt_rtt > 0) at its calling point in update_params(). Thus, simply fix tcp_illinois_info().
Function tcp_illinois_info() / get_info() is called without socket lock. Thus, eliminate any race condition on ca->cnt_rtt by using a local stack variable. Simply reuse info.tcpv_rttcnt, as its already set to ca->cnt_rtt.
Function avg_delay() is not affected by this race condition, as its called with the socket lock.
--- net/ipv4/tcp_illinois.c | 8 +++++--- 1 file changed, 5 insertions(+), 3 deletions(-)
net/ipv4/tcp_illinois.c +5 -3
@@ -313,11 +313,13 @@ static void tcp_illinois_info(struct sock *sk, u32 ext, .tcpv_rttcnt = ca->cnt_rtt, .tcpv_minrtt = ca->base_rtt, }; -u64 t = ca->sum_rtt; -do_div (t, ca->cnt_rtt); - info.tcpv_rtt = t; +if (info.tcpv_rttcnt >0 ) { +u64 t = ca->sum_rtt; +do_div (t, info.tcpv_rttcnt); + info.tcpv_rtt = t; + }nla_put (skb,INET_DIAG_VEGASINFO ,sizeof (info), &info); } }
PATCH 74/82 l2tp: fix oops in l2tp_eth_create() error path
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Tom Parkin <[email protected]>
[ Upstream commit 789336360e0a2aeb9750c16ab704a02cbe035e9e ]
When creating an L2TPv3 Ethernet session, if register_netdev() should fail for any reason (for example, automatic naming for "l2tpeth%d" interfaces hits the 32k-interface limit), the netdev is freed in the error path. However, the l2tp_eth_sess structure's dev pointer is left uncleared, and this results in l2tp_eth_delete() then attempting to unregister the same netdev later in the session teardown. This results in an oops.
To avoid this, clear the session dev pointer in the error path.
--- net/l2tp/l2tp_eth.c | 1 + 1 file changed, 1 insertion(+)
net/l2tp/l2tp_eth.c +1 -0
@@ -269,6 +269,7 @@ static int l2tp_eth_create(struct net *net, u32 tunnel_id, u32 session_id, u32 p out_del_dev:free_netdev (dev); + spriv->dev =NULL ; out_del_session:l2tp_session_delete (session); out:
PATCH 75/82 af-packet: fix oops when socket is not present
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Eric Leblond <[email protected]>
[ Upstream commit a3d744e995d2b936c500585ae39d99ee251c89b4 ]
Due to a NULL dereference, the following patch is causing oops in normal trafic condition:
commit c0de08d04215031d68fa13af36f347a6cfa252ca
Author: Eric Leblond <[email protected]>
Date: Thu Aug 16 22:02:58 2012 +0000
af_packet: don't emit packet on orig fanout group
This buggy patch was a feature fix and has reached most stable branches.
When skb->sk is NULL and when packet fanout is used, there is a crash in match_fanout_group where skb->sk is accessed. This patch fixes the issue by returning false as soon as the socket is NULL: this correspond to the wanted behavior because the kernel as to resend the skb to all the listening socket in this case.
--- net/core/dev.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
net/core/dev.c +1 -1
@@ -1633,7 +1633,7 @@ static inline int deliver_skb(struct sk_buff *skb,static inline bool skb_loop_sk (struct packet_type *ptype,struct sk_buff *skb) { -if (ptype->af_packet_priv ==NULL ) +if (!ptype->af_packet_priv || !skb->sk)return false;if (ptype->id_match)
PATCH 76/82 ipv6: send unsolicited neighbour advertisements to all-nodes
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Hannes Frederic Sowa <[email protected]>
[ Upstream commit 60713a0ca7fd6651b951cc1b4dbd528d1fc0281b ]
As documented in RFC4861 (Neighbor Discovery for IP version 6) 7.2.6., unsolicited neighbour advertisements should be sent to the all-nodes multicast address.
--- net/ipv6/ndisc.c | 3 +-- 1 file changed, 1 insertion(+), 2 deletions(-)
net/ipv6/ndisc.c +1 -2
@@ -606,7 +606,7 @@ static void ndisc_send_unsol_na(struct net_device *dev) {struct inet6_dev *idev;struct inet6_ifaddr *ifa; -struct in6_addr mcaddr; +struct in6_addr mcaddr =IN6ADDR_LINKLOCAL_ALLNODES_INIT ; idev =in6_dev_get (dev);if (!idev)
@@ -614,7 +614,6 @@ static void ndisc_send_unsol_na(struct net_device *dev)read_lock_bh (&idev->lock);list_for_each_entry (ifa, &idev->addr_list, if_list) { -addrconf_addr_solict_mult (&ifa->addr, &mcaddr); ndisc_send_na(dev, NULL, &mcaddr, &ifa->addr, /*router=*/ !!idev->cnf.forwarding, /*solicited=*/ false, /*override=*/ true,
PATCH 77/82 eCryptfs: Copy up POSIX ACL and read-only flags from lower mount
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Tyler Hicks <[email protected]>
commit 069ddcda37b2cf5bb4b6031a944c0e9359213262 upstream.
When the eCryptfs mount options do not include '-o acl', but the lower filesystem's mount options do include 'acl', the MS_POSIXACL flag is not flipped on in the eCryptfs super block flags. This flag is what the VFS checks in do_last() when deciding if the current umask should be applied to a newly created inode's mode or not. When a default POSIX ACL mask is set on a directory, the current umask is incorrectly applied to new inodes created in the directory. This patch ignores the MS_POSIXACL flag passed into ecryptfs_mount() and sets the flag on the eCryptfs super block depending on the flag's presence on the lower super block.
Additionally, it is incorrect to allow a writeable eCryptfs mount on top of a read-only lower mount. This missing check did not allow writes to the read-only lower mount because permissions checks are still performed on the lower filesystem's objects but it is best to simply not allow a rw mount on top of ro mount. However, a ro eCryptfs mount on top of a rw mount is valid and still allowed.
https://launchpad.net/bugs/1009207
--- fs/ecryptfs/main.c | 10 +++++++++- 1 file changed, 9 insertions(+), 1 deletion(-)
fs/ecryptfs/main.c +9 -1
@@ -505,7 +505,6 @@ static struct dentry *ecryptfs_mount(struct file_system_type *fs_type, int flags goto out; } - s->s_flags = flags; rc =bdi_setup_and_register (&sbi->bdi,"ecryptfs" ,BDI_CAP_MAP_COPY );if (rc) goto out1;
@@ -541,6 +540,15 @@ static struct dentry *ecryptfs_mount(struct file_system_type *fs_type, int flags }ecryptfs_set_superblock_lower (s, path.dentry->d_sb); + +/** +* Set the POSIX ACL flag based on whether they're enabled in the lower +* mount. Force a read-only eCryptfs mount if the lower mount is ro. +* Allow a ro eCryptfs mount even when the lower mount is rw. +*/ + s->s_flags = flags & ~MS_POSIXACL ; + s->s_flags |= path.dentry->d_sb->s_flags & (MS_RDONLY |MS_POSIXACL ); + s->s_maxbytes = path.dentry->d_sb->s_maxbytes; s->s_blocksize = path.dentry->d_sb->s_blocksize; s->s_magic =ECRYPTFS_SUPER_MAGIC ;
PATCH 78/82 eCryptfs: check for eCryptfs cipher support at mount
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Tim Sally <[email protected]>
commit 5f5b331d5c21228a6519dcb793fc1629646c51a6 upstream.
The issue occurs when eCryptfs is mounted with a cipher supported by the crypto subsystem but not by eCryptfs. The mount succeeds and an error does not occur until a write. This change checks for eCryptfs cipher support at mount time.
Resolves Launchpad issue #338914, reported by Tyler Hicks in 03/2009.
https://bugs.launchpad.net/ecryptfs/+bug/338914
--- fs/ecryptfs/main.c | 13 +++++++++++++ 1 file changed, 13 insertions(+)
fs/ecryptfs/main.c +13 -0
@@ -279,6 +279,7 @@ static int ecryptfs_parse_options(struct ecryptfs_sb_info *sbi, char *options,char *fnek_src;char *cipher_key_bytes_src;char *fn_cipher_key_bytes_src; +u8 cipher_code; *check_ruid =0 ;
@@ -420,6 +421,18 @@ static int ecryptfs_parse_options(struct ecryptfs_sb_info *sbi, char *options, && !fn_cipher_key_bytes_set) mount_crypt_stat->global_default_fn_cipher_key_bytes = mount_crypt_stat->global_default_cipher_key_size; + + cipher_code =ecryptfs_code_for_cipher_string ( + mount_crypt_stat->global_default_cipher_name, + mount_crypt_stat->global_default_cipher_key_size); +if (!cipher_code) { +ecryptfs_printk (KERN_ERR , +"eCryptfs doesn't support cipher: %s" , + mount_crypt_stat->global_default_cipher_name); + rc = -EINVAL ; + goto out; + } +mutex_lock (&key_tfm_list_mutex);if (!ecryptfs_tfm_exists (mount_crypt_stat->global_default_cipher_name,NULL )) {
PATCH 79/82 r8169: allow multicast packets on sub-8168f chipset.
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Nathan Walp <[email protected]>
commit 0481776b7a70f09acf7d9d97c288c3a8403fbfe4 upstream.
RTL_GIGA_MAC_VER_35 includes no multicast hardware filter.
--- drivers/net/ethernet/realtek/r8169.c | 3 +++ 1 file changed, 3 insertions(+)
drivers/net/ethernet/realtek/r8169.c +3 -0
@@ -4521,6 +4521,9 @@ static void rtl_set_rx_mode(struct net_device *dev) mc_filter[1 ] =swab32 (data); } +if (tp->mac_version ==RTL_GIGA_MAC_VER_35 ) + mc_filter[1 ] = mc_filter[0 ] =0xffffffff ; +RTL_W32 (MAR0 +4 , mc_filter[1 ]);RTL_W32 (MAR0 +0 , mc_filter[0 ]);
PATCH 80/82 r8169: Fix WoL on RTL8168d/8111d.
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Cyril Brulebois <[email protected]>
commit b00e69dee4ccbb3a19989e3d4f1385bc2e3406cd upstream.
This regression was spotted between Debian squeeze and Debian wheezy kernels (respectively based on 2.6.32 and 3.2). More info about Wake-on-LAN issues with Realtek's 816x chipsets can be found in the following thread: http://marc.info/?t=132079219400004
Probable regression from d4ed95d796e5126bba51466dc07e287cebc8bd19; more chipsets are likely affected.
Tested on top of a 3.2.23 kernel.
--- drivers/net/ethernet/realtek/r8169.c | 2 ++ 1 file changed, 2 insertions(+)
drivers/net/ethernet/realtek/r8169.c +2 -0
@@ -3827,6 +3827,8 @@ static void rtl_wol_suspend_quirk(struct rtl8169_private *tp)void __iomem *ioaddr = tp->mmio_addr;switch (tp->mac_version) { +case RTL_GIGA_MAC_VER_25 : +case RTL_GIGA_MAC_VER_26 :case RTL_GIGA_MAC_VER_29 :case RTL_GIGA_MAC_VER_30 :case RTL_GIGA_MAC_VER_32 :
PATCH 81/82 r8169: use unlimited DMA burst for TX
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Michal Schmidt <[email protected]>
commit aee77e4accbeb2c86b1d294cd84fec4a12dde3bd upstream.
The r8169 driver currently limits the DMA burst for TX to 1024 bytes. I have a box where this prevents the interface from using the gigabit line to its full potential. This patch solves the problem by setting TX_DMA_BURST to unlimited.
The box has an ASRock B75M motherboard with on-board RTL8168evl/8111evl (XID 0c900880). TSO is enabled.
I used netperf (TCP_STREAM test) to measure the dependency of TX throughput on MTU. I did it for three different values of TX_DMA_BURST ('5'=512, '6'=1024, '7'=unlimited). This chart shows the results:
http://michich.fedorapeople.org/r8169/r8169-effects-of-TX_DMA_BURST.png
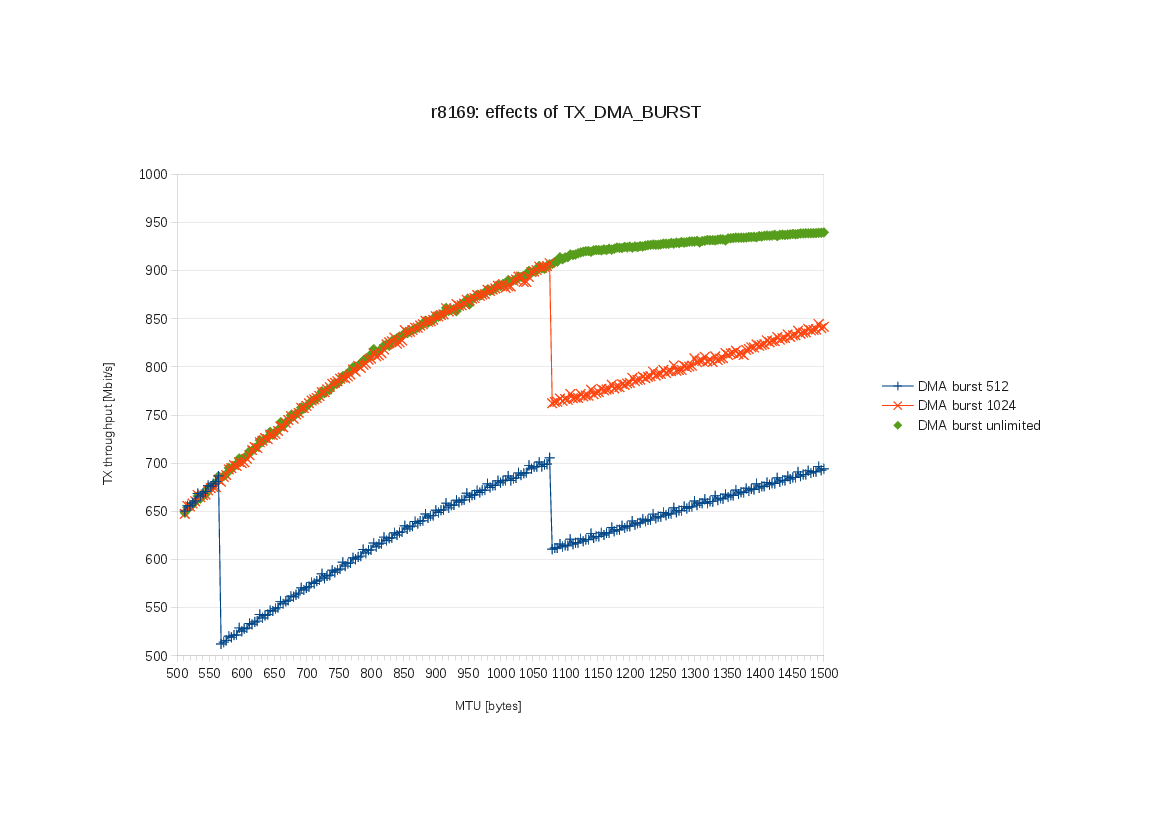
Interesting points:
- With the current DMA burst limit (1024):
- at the default MTU=1500 I get only 842 Mbit/s.
- when going from small MTU, the performance rises monotonically with increasing MTU only up to a peak at MTU=1076 (908 MBit/s). Then there's a sudden drop to 762 MBit/s from which the throughput rises monotonically again with further MTU increases.
- With a smaller DMA burst limit (512):
- there's a similar peak at MTU=1076 and another one at MTU=564.
- With unlimited DMA burst:
- at the default MTU=1500 I get nice 940 Mbit/s.
- the throughput rises monotonically with increasing MTU with no strange peaks.
Notice that the peaks occur at MTU sizes that are multiples of the DMA burst limit plus 52. Why 52? Because:
20 (IP header) + 20 (TCP header) + 12 (TCP options) = 52
The Realtek-provided r8168 driver (v8.032.00) uses unlimited TX DMA burst too, except for CFG_METHOD_1 where the TX DMA burst is set to 512 bytes. CFG_METHOD_1 appears to be the oldest MAC version of "RTL8168B/8111B", i.e. RTL_GIGA_MAC_VER_11 in r8169. Not sure if this MAC version really needs the smaller burst limit, or if any other versions have similar requirements.
--- drivers/net/ethernet/realtek/r8169.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/net/ethernet/realtek/r8169.c +1 -1
@@ -77,7 +77,7 @@ static const int multicast_filter_limit#define MAC_ADDR_LEN 6#define MAX_READ_REQUEST_SHIFT 12 -#define TX_DMA_BURST 6/* Maximum PCI burst, '6' is 1024 */ +#define TX_DMA_BURST 7/* Maximum PCI burst, '7' is unlimited */ #define SafeMtu 0x1c20/* ... actually life sucks beyond ~7k */ #define InterFrameGap 0x03/* 3 means InterFrameGap = the shortest one */
PATCH 82/82 sky2: Fix for interrupt handler
In reply to Ben Hutchings3.2-stable review patch. If anyone has any objections, please let me know.
------------------
From: Mirko Lindner <[email protected]>
commit d663d181b9e92d80c2455e460e932d34e7a2a7ae upstream.
Re-enable interrupts if it is not our interrupt
--- drivers/net/ethernet/marvell/sky2.c | 4 +++- 1 file changed, 3 insertions(+), 1 deletion(-)
drivers/net/ethernet/marvell/sky2.c +3 -1
@@ -3080,8 +3080,10 @@ static irqreturn_t sky2_intr(int irq, void *dev_id)/* Reading this mask interrupts as side effect */ status =sky2_read32 (hw,B0_Y2_SP_ISRC2 ); -if (status ==0 || status == ~0 ) +if (status ==0 || status == ~0 ) { +sky2_write32 (hw,B0_Y2_SP_ICR ,2 );return IRQ_NONE ; + }prefetch (&hw->st_le[hw->st_idx]);
Documentation/feature-removal-schedule.txt +0 -8
@@ -6,14 +6,6 @@ be removed from this file. --------------------------- -What: x86 floppy disable_hlt -When: 2012 -Why: ancient workaround of dubious utility clutters the - code used by everybody else. -Who: Len Brown <[email protected]> - ---------------------------- - What: CONFIG_APM_CPU_IDLE, and its ability to call APM BIOS in idle When: 2012 Why: This optional sub-feature of APM is of dubious reliability,
Makefile +2 -2
@@ -1,7 +1,7 @@ VERSION = 3 PATCHLEVEL = 2 -SUBLEVEL = 33 -EXTRAVERSION = +SUBLEVEL = 34 +EXTRAVERSION = -rc1 NAME = Saber-toothed Squirrel # *DOCUMENTATION*
arch/arm/mach-at91/at91rm9200_devices.c +1 -1
@@ -462,7 +462,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91rm9200_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9260_devices.c +1 -1
@@ -467,7 +467,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9260_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9261_devices.c +1 -1
@@ -284,7 +284,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9261_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9263_devices.c +1 -1
@@ -540,7 +540,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9263_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/at91sam9rl_devices.c +1 -1
@@ -319,7 +319,7 @@ static struct i2c_gpio_platform_data pdata = {static struct platform_device at91sam9rl_twi_device = { .name ="i2c-gpio" , - .id =-1 , + .id =0 , .dev.platform_data = &pdata, };
arch/arm/mach-at91/setup.c +1 -1
@@ -163,7 +163,7 @@ static void __init soc_detect(u32 dbgu_base) }/* at91sam9g10 */ -if ((cidr & ~AT91_CIDR_EXT ) ==ARCH_ID_AT91SAM9G10 ) { +if ((socid & ~AT91_CIDR_EXT ) ==ARCH_ID_AT91SAM9G10 ) { at91_soc_initdata.type =AT91_SOC_SAM9G10 ; at91_boot_soc = at91sam9261_soc; }
arch/x86/include/asm/system.h +0 -7
@@ -93,10 +93,6 @@ do { \ "memory"); \ } while (0) -/* -* disable hlt during certain critical i/o operations - */ -#define HAVE_DISABLE_HLT #else /* frame pointer must be last for get_wchan */
@@ -392,9 +388,6 @@ static inline void clflush(volatile void *__p)#define nop () asm volatile ("nop") -void disable_hlt (void ); -void enable_hlt (void ); -void cpu_idle_wait (void );extern unsigned long arch_align_stack (unsigned long sp);
arch/x86/kernel/process.c +0 -24
@@ -341,34 +341,10 @@ void (*pm_idle)(void);EXPORT_SYMBOL (pm_idle);#endif -#ifdef CONFIG_X86_32 -/* -* This halt magic was a workaround for ancient floppy DMA -* wreckage. It should be safe to remove. -*/ -static int hlt_counter; -void disable_hlt (void ) -{ - hlt_counter++; -} -EXPORT_SYMBOL (disable_hlt); - -void enable_hlt (void ) -{ - hlt_counter--; -} -EXPORT_SYMBOL (enable_hlt); - -static inline int hlt_use_halt (void ) -{ -return (!hlt_counter && boot_cpu_data.hlt_works_ok); -} -#else static inline int hlt_use_halt (void ) {return 1 ; } -#endif /* * We use this if we don't have any better
arch/x86/xen/mmu.c +20 -1
@@ -1203,6 +1203,25 @@ unsigned long xen_read_cr2_direct(void)return percpu_read (xen_vcpu_info.arch.cr2); } +void xen_flush_tlb_all (void ) +{ +struct mmuext_op *op; +struct multicall_space mcs; + +trace_xen_mmu_flush_tlb_all (0 ); + +preempt_disable (); + + mcs =xen_mc_entry (sizeof (*op)); + + op = mcs.args; + op->cmd =MMUEXT_TLB_FLUSH_ALL ; +MULTI_mmuext_op (mcs.mc, op,1 ,NULL ,DOMID_SELF ); + +xen_mc_issue (PARAVIRT_LAZY_MMU ); + +preempt_enable (); +}static void xen_flush_tlb (void ) {struct mmuext_op *op;
@@ -2366,7 +2385,7 @@ int xen_remap_domain_mfn_range(struct vm_area_struct *vma, err =0 ; out: -flush_tlb_all (); +xen_flush_tlb_all ();return err; }
crypto/cryptd.c +8 -3
@@ -137,13 +137,18 @@ static void cryptd_queue_worker(struct work_struct *work)struct crypto_async_request *req, *backlog; cpu_queue = container_of(work, struct cryptd_cpu_queue, work); -/* Only handle one request at a time to avoid hogging crypto -* workqueue. preempt_disable/enable is used to prevent -* being preempted by cryptd_enqueue_request() */ +/* +* Only handle one request at a time to avoid hogging crypto workqueue. +* preempt_disable/enable is used to prevent being preempted by +* cryptd_enqueue_request(). local_bh_disable/enable is used to prevent +* cryptd_enqueue_request() being accessed from software interrupts. +*/ +local_bh_disable ();preempt_disable (); backlog =crypto_get_backlog (&cpu_queue->queue); req =crypto_dequeue_request (&cpu_queue->queue);preempt_enable (); +local_bh_enable ();if (!req)return ;
drivers/block/floppy.c +11 -37
96 lines not on this page · raw message
drivers/gpio/gpio-timberdale.c +2 -2
@@ -116,7 +116,7 @@ static void timbgpio_irq_disable(struct irq_data *d)unsigned long flags;spin_lock_irqsave (&tgpio->lock, flags); - tgpio->last_ier &= ~(1 << offset); + tgpio->last_ier &= ~(1UL << offset);iowrite32 (tgpio->last_ier, tgpio->membase +TGPIO_IER );spin_unlock_irqrestore (&tgpio->lock, flags); }
@@ -128,7 +128,7 @@ static void timbgpio_irq_enable(struct irq_data *d)unsigned long flags;spin_lock_irqsave (&tgpio->lock, flags); - tgpio->last_ier |=1 << offset; + tgpio->last_ier |=1UL << offset;iowrite32 (tgpio->last_ier, tgpio->membase +TGPIO_IER );spin_unlock_irqrestore (&tgpio->lock, flags); }
drivers/gpio/gpiolib.c +7 -3
@@ -621,9 +621,11 @@ static ssize_t export_store(struct class *class,*/ status =gpio_request (gpio,"sysfs" ); -if (status <0 ) +if (status <0 ) { +if (status == -EPROBE_DEFER ) + status = -ENODEV ; goto done; - + } status =gpio_export (gpio, true);if (status <0 )gpio_free (gpio);
@@ -1182,8 +1184,10 @@ int gpio_request(unsigned gpio, const char *label)spin_lock_irqsave (&gpio_lock, flags); -if (!gpio_is_valid (gpio)) +if (!gpio_is_valid (gpio)) { + status = -EINVAL ; goto done; + } desc = &gpio_desc[gpio]; chip = desc->chip;if (chip ==NULL )
drivers/gpu/drm/drm_fops.c +4 -1
@@ -136,8 +136,11 @@ int drm_open(struct inode *inode, struct file *filp) retcode =drm_open_helper (inode, filp, dev);if (!retcode) {atomic_inc (&dev->counts[_DRM_STAT_OPENS]); -if (!dev->open_count++) +if (!dev->open_count++) { retcode =drm_setup (dev); +if (retcode) + dev->open_count--; + } }if (!retcode) {mutex_lock (&dev->struct_mutex);
drivers/gpu/drm/i915/intel_drv.h +2 -2
@@ -227,12 +227,12 @@ struct dip_infoframe {uint16_t bottom_bar_start;uint16_t left_bar_end;uint16_t right_bar_start; - } avi; + } __attribute__ ((packed)) avi;struct {uint8_t vn[8 ];uint8_t pd[16 ];uint8_t sdi; - } spd; + } __attribute__ ((packed)) spd;uint8_t payload[27 ]; } __attribute__ ((packed)) body; } __attribute__((packed));
drivers/gpu/drm/i915/intel_overlay.c +11 -3
@@ -428,9 +428,17 @@ static int intel_overlay_off(struct intel_overlay *overlay)OUT_RING (flip_addr);OUT_RING (MI_WAIT_FOR_EVENT |MI_WAIT_FOR_OVERLAY_FLIP );/* turn overlay off */ -OUT_RING (MI_OVERLAY_FLIP |MI_OVERLAY_OFF ); -OUT_RING (flip_addr); -OUT_RING (MI_WAIT_FOR_EVENT |MI_WAIT_FOR_OVERLAY_FLIP ); +if (IS_I830 (dev)) { +/* Workaround: Don't disable the overlay fully, since otherwise +* it dies on the next OVERLAY_ON cmd. */ +OUT_RING (MI_NOOP ); +OUT_RING (MI_NOOP ); +OUT_RING (MI_NOOP ); + }else { +OUT_RING (MI_OVERLAY_FLIP |MI_OVERLAY_OFF ); +OUT_RING (flip_addr); +OUT_RING (MI_WAIT_FOR_EVENT |MI_WAIT_FOR_OVERLAY_FLIP ); + }ADVANCE_LP_RING (); return intel_overlay_do_wait_request(overlay, request,
drivers/gpu/drm/i915/intel_sdvo.c +44 -15
81 lines not on this page · raw message
drivers/gpu/drm/i915/intel_sdvo_regs.h +2 -0
@@ -708,6 +708,8 @@ struct intel_sdvo_enhancements_arg {#define SDVO_CMD_SET_AUDIO_STAT 0x91#define SDVO_CMD_GET_AUDIO_STAT 0x92#define SDVO_CMD_SET_HBUF_INDEX 0x93 +#define SDVO_HBUF_INDEX_ELD 0 +#define SDVO_HBUF_INDEX_AVI_IF 1#define SDVO_CMD_GET_HBUF_INDEX 0x94#define SDVO_CMD_GET_HBUF_INFO 0x95#define SDVO_CMD_SET_HBUF_AV_SPLIT 0x96
drivers/gpu/drm/nouveau/nouveau_drv.c +20 -14
@@ -178,8 +178,10 @@ nouveau_pci_suspend(struct pci_dev *pdev, pm_message_t pm_state)if (dev->switch_power_state ==DRM_SWITCH_POWER_OFF )return 0 ; -NV_INFO (dev,"Disabling fbcon acceleration...\n" ); -nouveau_fbcon_save_disable_accel (dev); +if (dev->mode_config.num_crtc) { +NV_INFO (dev,"Disabling fbcon acceleration...\n" ); +nouveau_fbcon_save_disable_accel (dev); + }NV_INFO (dev,"Unpinning framebuffer(s)...\n" );list_for_each_entry (crtc, &dev->mode_config.crtc_list, head) {
@@ -246,10 +248,12 @@ nouveau_pci_suspend(struct pci_dev *pdev, pm_message_t pm_state)pci_set_power_state (pdev, PCI_D3hot); } -console_lock (); -nouveau_fbcon_set_suspend (dev,1 ); -console_unlock (); -nouveau_fbcon_restore_accel (dev); +if (dev->mode_config.num_crtc) { +console_lock (); +nouveau_fbcon_set_suspend (dev,1 ); +console_unlock (); +nouveau_fbcon_restore_accel (dev); + }return 0 ; out_abort:
@@ -275,7 +279,8 @@ nouveau_pci_resume(struct pci_dev *pdev)if (dev->switch_power_state ==DRM_SWITCH_POWER_OFF )return 0 ; -nouveau_fbcon_save_disable_accel (dev); +if (dev->mode_config.num_crtc) +nouveau_fbcon_save_disable_accel (dev);NV_INFO (dev,"We're back, enabling device...\n" );pci_set_power_state (pdev,PCI_D0 );
@@ -376,15 +381,18 @@ nouveau_pci_resume(struct pci_dev *pdev) nv_crtc->lut.depth =0 ; } -console_lock (); -nouveau_fbcon_set_suspend (dev,0 ); -console_unlock (); +if (dev->mode_config.num_crtc) { +console_lock (); +nouveau_fbcon_set_suspend (dev,0 ); +console_unlock (); -nouveau_fbcon_zfill_all (dev); +nouveau_fbcon_zfill_all (dev); + }drm_helper_resume_force_mode (dev); -nouveau_fbcon_restore_accel (dev); +if (dev->mode_config.num_crtc) +nouveau_fbcon_restore_accel (dev);return 0 ; }
@@ -466,9 +474,7 @@ static int __init nouveau_init(void)#ifdef CONFIG_VGA_CONSOLE if (vgacon_text_force ()) nouveau_modeset =0 ; - else#endif - nouveau_modeset =1 ; }if (!nouveau_modeset)
drivers/gpu/drm/nouveau/nouveau_state.c +3 -1
@@ -46,6 +46,7 @@ static int nouveau_init_engine_ptrs(struct drm_device *dev) {struct drm_nouveau_private *dev_priv = dev->dev_private;struct nouveau_engine *engine = &dev_priv->engine; +u32 pclass = dev->pdev->class >>8 ;switch (dev_priv->chipset &0xf0 ) {case 0x00 :
@@ -481,7 +482,8 @@ static int nouveau_init_engine_ptrs(struct drm_device *dev) }/* headless mode */ -if (nouveau_modeset ==2 ) { +if (nouveau_modeset ==2 || + (nouveau_modeset <0 && pclass !=PCI_CLASS_DISPLAY_VGA )) { engine->display.early_init = nouveau_stub_init; engine->display.late_takedown = nouveau_stub_takedown; engine->display.create = nouveau_stub_init;
drivers/gpu/drm/nouveau/nv04_dac.c +4 -4
@@ -209,7 +209,7 @@ out:NVWriteVgaCrtc (dev,0 ,NV_CIO_CR_MODE_INDEX , saved_cr_mode);if (blue ==0x18 ) { -NV_INFO (dev,"Load detected on head A\n" ); +NV_DEBUG (dev,"Load detected on head A\n" );return connector_status_connected; }
@@ -323,7 +323,7 @@ nv17_dac_detect(struct drm_encoder *encoder, struct drm_connector *connector)if (nv17_dac_sample_load (encoder) &NV_PRAMDAC_TEST_CONTROL_SENSEB_ALLHI ) { -NV_INFO (dev,"Load detected on output %c\n" , +NV_DEBUG (dev,"Load detected on output %c\n" ,'@' +ffs (dcb->or));return connector_status_connected; }else {
@@ -398,7 +398,7 @@ static void nv04_dac_commit(struct drm_encoder *encoder) helper->dpms (encoder,DRM_MODE_DPMS_ON ); -NV_INFO (dev,"Output %s is running on CRTC %d using output %c\n" , +NV_DEBUG (dev,"Output %s is running on CRTC %d using output %c\n" ,drm_get_connector_name (&nouveau_encoder_connector_get (nv_encoder)->base), nv_crtc->index,'@' +ffs (nv_encoder->dcb->or)); }
@@ -447,7 +447,7 @@ static void nv04_dac_dpms(struct drm_encoder *encoder, int mode)return ; nv_encoder->last_dpms = mode; -NV_INFO (dev,"Setting dpms mode %d on vga encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on vga encoder (output %d)\n" , mode, nv_encoder->dcb->index);nv04_dac_update_dacclk (encoder, mode ==DRM_MODE_DPMS_ON );
drivers/gpu/drm/nouveau/nv04_dfp.c +3 -3
@@ -468,7 +468,7 @@ static void nv04_dfp_commit(struct drm_encoder *encoder) helper->dpms (encoder,DRM_MODE_DPMS_ON ); -NV_INFO (dev,"Output %s is running on CRTC %d using output %c\n" , +NV_DEBUG (dev,"Output %s is running on CRTC %d using output %c\n" ,drm_get_connector_name (&nouveau_encoder_connector_get (nv_encoder)->base), nv_crtc->index,'@' +ffs (nv_encoder->dcb->or)); }
@@ -511,7 +511,7 @@ static void nv04_lvds_dpms(struct drm_encoder *encoder, int mode)return ; nv_encoder->last_dpms = mode; -NV_INFO (dev,"Setting dpms mode %d on lvds encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on lvds encoder (output %d)\n" , mode, nv_encoder->dcb->index);if (was_powersaving &&is_powersaving_dpms (mode))
@@ -556,7 +556,7 @@ static void nv04_tmds_dpms(struct drm_encoder *encoder, int mode)return ; nv_encoder->last_dpms = mode; -NV_INFO (dev,"Setting dpms mode %d on tmds encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on tmds encoder (output %d)\n" , mode, nv_encoder->dcb->index);nv04_dfp_update_backlight (encoder, mode);
drivers/gpu/drm/nouveau/nv04_tv.c +2 -2
@@ -69,7 +69,7 @@ static void nv04_tv_dpms(struct drm_encoder *encoder, int mode)struct nv04_mode_state *state = &dev_priv->mode_reg;uint8_t crtc1A; -NV_INFO (dev,"Setting dpms mode %d on TV encoder (output %d)\n" , +NV_DEBUG (dev,"Setting dpms mode %d on TV encoder (output %d)\n" , mode, nv_encoder->dcb->index); state->pllsel &= ~(PLLSEL_TV_CRTC1_MASK |PLLSEL_TV_CRTC2_MASK );
@@ -162,7 +162,7 @@ static void nv04_tv_commit(struct drm_encoder *encoder) helper->dpms (encoder,DRM_MODE_DPMS_ON ); -NV_INFO (dev,"Output %s is running on CRTC %d using output %c\n" , +NV_DEBUG (dev,"Output %s is running on CRTC %d using output %c\n" ,drm_get_connector_name (&nouveau_encoder_connector_get (nv_encoder)->base), nv_crtc->index,'@' +ffs (nv_encoder->dcb->or)); }
drivers/gpu/drm/radeon/evergreen.c +1 -1
@@ -1164,7 +1164,7 @@ void evergreen_mc_resume(struct radeon_device *rdev, struct evergreen_mc_save *sWREG32 (BIF_FB_EN ,FB_READ_EN |FB_WRITE_EN );for (i =0 ; i < rdev->num_crtc; i++) { -if (save->crtc_enabled) { +if (save->crtc_enabled[i]) { tmp =RREG32 (EVERGREEN_CRTC_CONTROL + crtc_offsets[i]); tmp &= ~EVERGREEN_CRTC_DISP_READ_REQUEST_DISABLE ;WREG32 (EVERGREEN_CRTC_CONTROL + crtc_offsets[i], tmp);
drivers/gpu/drm/radeon/radeon_legacy_encoders.c +1 -0
@@ -650,6 +650,7 @@ static enum drm_connector_status radeon_legacy_primary_dac_detect(struct drm_enc tmp |=RADEON_DAC_RANGE_CNTL_PS2 |RADEON_DAC_CMP_EN ;WREG32 (RADEON_DAC_CNTL , tmp); + tmp = dac_macro_cntl; tmp &= ~(RADEON_DAC_PDWN_R |RADEON_DAC_PDWN_G |RADEON_DAC_PDWN_B );
drivers/gpu/drm/vmwgfx/vmwgfx_dmabuf.c +1 -1
@@ -306,7 +306,7 @@ void vmw_bo_pin(struct ttm_buffer_object *bo, bool pin)BUG_ON (!atomic_read (&bo->reserved));BUG_ON (old_mem_type !=TTM_PL_VRAM && - old_mem_type !=VMW_PL_FLAG_GMR ); + old_mem_type !=VMW_PL_GMR ); pl_flags =TTM_PL_FLAG_VRAM |VMW_PL_FLAG_GMR |TTM_PL_FLAG_CACHED ;if (pin)
drivers/gpu/drm/vmwgfx/vmwgfx_drv.c +5 -0
@@ -1048,6 +1048,11 @@ static void vmw_pm_complete(struct device *kdev)struct drm_device *dev =pci_get_drvdata (pdev);struct vmw_private *dev_priv =vmw_priv (dev); +mutex_lock (&dev_priv->hw_mutex); +vmw_write (dev_priv,SVGA_REG_ID ,SVGA_ID_2 ); + (void )vmw_read (dev_priv,SVGA_REG_ID ); +mutex_unlock (&dev_priv->hw_mutex); +/** * Reclaim 3d reference held by fbdev and potentially * start fifo.
drivers/hid/hid-microsoft.c +13 -5
@@ -29,22 +29,30 @@#define MS_RDESC 0x08#define MS_NOGET 0x10#define MS_DUPLICATE_USAGES 0x20 +#define MS_RDESC_3K 0x40 -/* -* Microsoft Wireless Desktop Receiver (Model 1028) has -* 'Usage Min/Max' where it ought to have 'Physical Min/Max' -*/ static __u8 *ms_report_fixup (struct hid_device *hdev,__u8 *rdesc,unsigned int *rsize) {unsigned long quirks = (unsigned long )hid_get_drvdata (hdev); +/* +* Microsoft Wireless Desktop Receiver (Model 1028) has +* 'Usage Min/Max' where it ought to have 'Physical Min/Max' +*/ if ((quirks &MS_RDESC ) && *rsize ==571 && rdesc[557 ] ==0x19 && rdesc[559 ] ==0x29 ) {hid_info (hdev,"fixing up Microsoft Wireless Receiver Model 1028 report descriptor\n" ); rdesc[557 ] =0x35 ; rdesc[559 ] =0x45 ; } +/* the same as above (s/usage/physical/) */ +if ((quirks &MS_RDESC_3K ) && *rsize ==106 && + !memcmp ((char []){0x19 ,0x00 ,0x29 ,0xff }, + &rdesc[94 ],4 )) { + rdesc[94 ] =0x35 ; + rdesc[96 ] =0x45 ; + }return rdesc; }
@@ -193,7 +201,7 @@ static const struct hid_device_id ms_devices[] = { { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_MS_PRESENTER_8K_USB), .driver_data = MS_PRESENTER }, { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_MS_DIGITAL_MEDIA_3K), - .driver_data = MS_ERGONOMY }, + .driver_data = MS_ERGONOMY | MS_RDESC_3K }, { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_WIRELESS_OPTICAL_DESKTOP_3_0), .driver_data = MS_NOGET }, { HID_USB_DEVICE(USB_VENDOR_ID_MICROSOFT, USB_DEVICE_ID_MS_COMFORT_MOUSE_4500),
drivers/hwmon/w83627ehf.c +1 -0
@@ -2015,6 +2015,7 @@ static int __devinit w83627ehf_probe(struct platform_device *pdev)mutex_init (&data->lock);mutex_init (&data->update_lock); data->name = w83627ehf_device_names[sio_data->kind]; + data->bank =0xff ;/* Force initial bank selection */ platform_set_drvdata (pdev, data);/* 627EHG and 627EHF have 10 voltage inputs; 627DHG and 667HG have 9 */
drivers/input/touchscreen/tsc40.c +0 -1
@@ -107,7 +107,6 @@ static int tsc_connect(struct serio *serio, struct serio_driver *drv)__set_bit (BTN_TOUCH , input_dev->keybit);input_set_abs_params (ptsc->dev,ABS_X ,0 ,0x3ff ,0 ,0 );input_set_abs_params (ptsc->dev,ABS_Y ,0 ,0x3ff ,0 ,0 ); -input_set_abs_params (ptsc->dev,ABS_PRESSURE ,0 ,0 ,0 ,0 );serio_set_drvdata (serio, ptsc);
drivers/net/ethernet/marvell/sky2.c +3 -1
@@ -3060,8 +3060,10 @@ static irqreturn_t sky2_intr(int irq, void *dev_id)/* Reading this mask interrupts as side effect */ status =sky2_read32 (hw,B0_Y2_SP_ISRC2 ); -if (status ==0 || status == ~0 ) +if (status ==0 || status == ~0 ) { +sky2_write32 (hw,B0_Y2_SP_ICR ,2 );return IRQ_NONE ; + }prefetch (&hw->st_le[hw->st_idx]);
drivers/net/ethernet/realtek/r8169.c +6 -1
@@ -77,7 +77,7 @@ static const int multicast_filter_limit = 32;#define MAC_ADDR_LEN 6#define MAX_READ_REQUEST_SHIFT 12 -#define TX_DMA_BURST 6/* Maximum PCI burst, '6' is 1024 */ +#define TX_DMA_BURST 7/* Maximum PCI burst, '7' is unlimited */ #define SafeMtu 0x1c20/* ... actually life sucks beyond ~7k */ #define InterFrameGap 0x03/* 3 means InterFrameGap = the shortest one */
@@ -3521,6 +3521,8 @@ static void rtl_wol_suspend_quirk(struct rtl8169_private *tp)void __iomem *ioaddr = tp->mmio_addr;switch (tp->mac_version) { +case RTL_GIGA_MAC_VER_25 : +case RTL_GIGA_MAC_VER_26 :case RTL_GIGA_MAC_VER_29 :case RTL_GIGA_MAC_VER_30 :case RTL_GIGA_MAC_VER_32 :
@@ -6064,6 +6066,9 @@ static void rtl_set_rx_mode(struct net_device *dev) mc_filter[1 ] =swab32 (data); } +if (tp->mac_version ==RTL_GIGA_MAC_VER_35 ) + mc_filter[1 ] = mc_filter[0 ] =0xffffffff ; +RTL_W32 (MAR0 +4 , mc_filter[1 ]);RTL_W32 (MAR0 +0 , mc_filter[0 ]);
drivers/net/usb/usbnet.c +3 -0
@@ -1156,6 +1156,7 @@ netdev_tx_t usbnet_start_xmit (struct sk_buff *skb,usb_anchor_urb (urb, &dev->deferred);/* no use to process more packets */ netif_stop_queue (net); +usb_put_urb (urb);spin_unlock_irqrestore (&dev->txq.lock, flags);netdev_dbg (dev->net,"Delaying transmission for resumption\n" ); goto deferred;
@@ -1297,6 +1298,8 @@ void usbnet_disconnect (struct usb_interface *intf)cancel_work_sync (&dev->kevent); +usb_scuttle_anchored_urbs (&dev->deferred); +if (dev->driver_info->unbind) dev->driver_info->unbind (dev, intf);
drivers/net/wireless/ath/ath9k/xmit.c +8 -2
@@ -288,6 +288,7 @@ static struct ath_buf *ath_tx_get_buffer(struct ath_softc *sc) } bf = list_first_entry(&sc->tx.txbuf, struct ath_buf, list); + bf->bf_next =NULL ;list_del (&bf->list);spin_unlock_bh (&sc->tx.txbuflock);
@@ -369,7 +370,7 @@ static void ath_tx_complete_aggr(struct ath_softc *sc, struct ath_txq *txq,u16 seq_st =0 , acked_cnt =0 , txfail_cnt =0 ;u32 ba[WME_BA_BMP_SIZE >>5 ];int isaggr, txfail, txpending, sendbar =0 , needreset =0 , nbad =0 ; -bool rc_update = true; +bool rc_update = true, isba;struct ieee80211_tx_rate rates[4 ];struct ath_frame_info *fi;int nframes;
@@ -407,13 +408,17 @@ static void ath_tx_complete_aggr(struct ath_softc *sc, struct ath_txq *txq, an = (struct ath_node *)sta->drv_priv; tidno =ieee80211_get_qos_ctl (hdr)[0 ] &IEEE80211_QOS_CTL_TID_MASK ; tid =ATH_AN_2_TID (an, tidno); + isba = ts->ts_flags &ATH9K_TX_BA ;/* * The hardware occasionally sends a tx status for the wrong TID. * In this case, the BA status cannot be considered valid and all * subframes need to be retransmitted +* +* Only BlockAcks have a TID and therefore normal Acks cannot be +* checked */ -if (tidno != ts->tid) +if (isba && tidno != ts->tid) txok = false; isaggr =bf_isaggr (bf);
@@ -1710,6 +1715,7 @@ static void ath_tx_send_normal(struct ath_softc *sc, struct ath_txq *txq,if (tid)INCR (tid->seq_start,IEEE80211_SEQ_MAX ); + bf->bf_next =NULL ; bf->bf_lastbf = bf;ath_tx_fill_desc (sc, bf, txq, fi->framelen);ath_tx_txqaddbuf (sc, txq, &bf_head, false);
drivers/net/wireless/rt2x00/rt2800lib.c +1 -1
@@ -2141,7 +2141,7 @@ static int rt2800_get_gain_calibration_delta(struct rt2x00_dev *rt2x00dev)/* * Check if temperature compensation is supported. */ -if (tssi_bounds[4 ] ==0xff ) +if (tssi_bounds[4 ] ==0xff || step ==0xff )return 0 ;/*
drivers/target/iscsi/iscsi_target.c +3 -1
@@ -3523,7 +3523,9 @@ restart:*/ iscsit_thread_check_cpumask (conn, current,1 ); -schedule_timeout_interruptible (MAX_SCHEDULE_TIMEOUT ); +wait_event_interruptible (conn->queues_wq, + !iscsit_conn_all_queues_empty (conn) || + ts->status ==ISCSI_THREAD_SET_RESET );if ((ts->status ==ISCSI_THREAD_SET_RESET ) ||signal_pending (current))
drivers/target/iscsi/iscsi_target_core.h +1 -0
@@ -491,6 +491,7 @@ struct iscsi_tmr_req { };struct iscsi_conn { +wait_queue_head_t queues_wq;/* Authentication Successful for this connection */ u8 auth_complete;/* State connection is currently in */
drivers/target/iscsi/iscsi_target_login.c +1 -0
@@ -44,6 +44,7 @@ extern spinlock_t sess_idr_lock;static int iscsi_login_init_conn (struct iscsi_conn *conn) { +init_waitqueue_head (&conn->queues_wq);INIT_LIST_HEAD (&conn->conn_list);INIT_LIST_HEAD (&conn->conn_cmd_list);INIT_LIST_HEAD (&conn->immed_queue_list);
drivers/target/iscsi/iscsi_target_util.c +20 -2
@@ -659,7 +659,7 @@ void iscsit_add_cmd_to_immediate_queue(atomic_set (&conn->check_immediate_queue,1 );spin_unlock_bh (&conn->immed_queue_lock); -wake_up_process (conn->thread_set->tx_thread); +wake_up (&conn->queues_wq); }struct iscsi_queue_req *iscsit_get_cmd_from_immediate_queue (struct iscsi_conn *conn)
@@ -733,7 +733,7 @@ void iscsit_add_cmd_to_response_queue(atomic_inc (&cmd->response_queue_count);spin_unlock_bh (&conn->response_queue_lock); -wake_up_process (conn->thread_set->tx_thread); +wake_up (&conn->queues_wq); }struct iscsi_queue_req *iscsit_get_cmd_from_response_queue (struct iscsi_conn *conn)
@@ -787,6 +787,24 @@ static void iscsit_remove_cmd_from_response_queue( } } +bool iscsit_conn_all_queues_empty (struct iscsi_conn *conn) +{ +bool empty; + +spin_lock_bh (&conn->immed_queue_lock); + empty =list_empty (&conn->immed_queue_list); +spin_unlock_bh (&conn->immed_queue_lock); + +if (!empty) +return empty; + +spin_lock_bh (&conn->response_queue_lock); + empty =list_empty (&conn->response_queue_list); +spin_unlock_bh (&conn->response_queue_lock); + +return empty; +} +void iscsit_free_queue_reqs_for_conn (struct iscsi_conn *conn) {struct iscsi_queue_req *qr, *qr_tmp;
drivers/target/iscsi/iscsi_target_util.h +1 -0
@@ -28,6 +28,7 @@ extern struct iscsi_queue_req *iscsit_get_cmd_from_immediate_queue(struct iscsi_extern void iscsit_add_cmd_to_response_queue (struct iscsi_cmd *,struct iscsi_conn *,u8 );extern struct iscsi_queue_req *iscsit_get_cmd_from_response_queue (struct iscsi_conn *);extern void iscsit_remove_cmd_from_tx_queues (struct iscsi_cmd *,struct iscsi_conn *); +extern bool iscsit_conn_all_queues_empty (struct iscsi_conn *);extern void iscsit_free_queue_reqs_for_conn (struct iscsi_conn *);extern void iscsit_release_cmd (struct iscsi_cmd *);extern void iscsit_free_cmd (struct iscsi_cmd *);
drivers/target/target_core_configfs.c +2 -1
@@ -3205,7 +3205,8 @@ static int __init target_core_init_configfs(void)if (ret <0 ) goto out; -if (core_dev_setup_virtual_lun0 () <0 ) + ret =core_dev_setup_virtual_lun0 (); +if (ret <0 ) goto out;return 0 ;
drivers/target/target_core_device.c +9 -9
@@ -835,20 +835,20 @@ int se_dev_check_shutdown(struct se_device *dev)u32 se_dev_align_max_sectors (u32 max_sectors,u32 block_size) { -u32 tmp, aligned_max_sectors; +u32 aligned_max_sectors; +u32 alignment;/* * Limit max_sectors to a PAGE_SIZE aligned value for modern * transport_allocate_data_tasks() operation. */ - tmp =rounddown ((max_sectors * block_size),PAGE_SIZE ); - aligned_max_sectors = (tmp / block_size); -if (max_sectors != aligned_max_sectors) { -printk (KERN_INFO "Rounding down aligned max_sectors from %u" -" to %u\n" , max_sectors, aligned_max_sectors); -return aligned_max_sectors; - } + alignment =max (1ul ,PAGE_SIZE / block_size); + aligned_max_sectors =rounddown (max_sectors, alignment); + +if (max_sectors != aligned_max_sectors) +pr_info ("Rounding down aligned max_sectors from %u to %u\n" , + max_sectors, aligned_max_sectors); -return max_sectors; +return aligned_max_sectors; } void se_dev_set_default_attribs(
drivers/usb/serial/mos7840.c +0 -1
@@ -2585,7 +2585,6 @@ error:static void mos7840_disconnect (struct usb_serial *serial) {int i; -unsigned long flags;struct moschip_port *mos7840_port;dbg ("%s" ," disconnect :entering.........." );
drivers/xen/gntdev.c +19 -17
@@ -105,6 +105,21 @@ static void gntdev_print_maps(struct gntdev_priv *priv,#endif } +static void gntdev_free_map (struct grant_map *map) +{ +if (map ==NULL ) +return ; + +if (map->pages) +free_xenballooned_pages (map->count, map->pages); +kfree (map->pages); +kfree (map->grants); +kfree (map->map_ops); +kfree (map->unmap_ops); +kfree (map->kmap_ops); +kfree (map); +} +static struct grant_map *gntdev_alloc_map (struct gntdev_priv *priv,int count) {struct grant_map *add;
@@ -142,12 +157,7 @@ static struct grant_map *gntdev_alloc_map(struct gntdev_priv *priv, int count)return add; err: -kfree (add->pages); -kfree (add->grants); -kfree (add->map_ops); -kfree (add->unmap_ops); -kfree (add->kmap_ops); -kfree (add); +gntdev_free_map (add);return NULL ; }
@@ -196,17 +206,9 @@ static void gntdev_put_map(struct grant_map *map)if (map->notify.flags &UNMAP_NOTIFY_SEND_EVENT )notify_remote_via_evtchn (map->notify.event); -if (map->pages) { -if (!use_ptemod) -unmap_grant_pages (map,0 , map->count); - -free_xenballooned_pages (map->count, map->pages); - } -kfree (map->pages); -kfree (map->grants); -kfree (map->map_ops); -kfree (map->unmap_ops); -kfree (map); +if (map->pages && !use_ptemod) +unmap_grant_pages (map,0 , map->count); +gntdev_free_map (map); }/* ------------------------------------------------------------------ */
fs/cifs/cifsacl.c +20 -29
111 lines not on this page · raw message
fs/ecryptfs/main.c +22 -1
@@ -280,6 +280,7 @@ static int ecryptfs_parse_options(struct ecryptfs_sb_info *sbi, char *options,char *fnek_src;char *cipher_key_bytes_src;char *fn_cipher_key_bytes_src; +u8 cipher_code; *check_ruid =0 ;
@@ -421,6 +422,18 @@ static int ecryptfs_parse_options(struct ecryptfs_sb_info *sbi, char *options, && !fn_cipher_key_bytes_set) mount_crypt_stat->global_default_fn_cipher_key_bytes = mount_crypt_stat->global_default_cipher_key_size; + + cipher_code =ecryptfs_code_for_cipher_string ( + mount_crypt_stat->global_default_cipher_name, + mount_crypt_stat->global_default_cipher_key_size); +if (!cipher_code) { +ecryptfs_printk (KERN_ERR , +"eCryptfs doesn't support cipher: %s" , + mount_crypt_stat->global_default_cipher_name); + rc = -EINVAL ; + goto out; + } +mutex_lock (&key_tfm_list_mutex);if (!ecryptfs_tfm_exists (mount_crypt_stat->global_default_cipher_name,NULL )) {
@@ -506,7 +519,6 @@ static struct dentry *ecryptfs_mount(struct file_system_type *fs_type, int flags goto out; } - s->s_flags = flags; rc =bdi_setup_and_register (&sbi->bdi,"ecryptfs" ,BDI_CAP_MAP_COPY );if (rc) goto out1;
@@ -542,6 +554,15 @@ static struct dentry *ecryptfs_mount(struct file_system_type *fs_type, int flags }ecryptfs_set_superblock_lower (s, path.dentry->d_sb); + +/** +* Set the POSIX ACL flag based on whether they're enabled in the lower +* mount. Force a read-only eCryptfs mount if the lower mount is ro. +* Allow a ro eCryptfs mount even when the lower mount is rw. +*/ + s->s_flags = flags & ~MS_POSIXACL ; + s->s_flags |= path.dentry->d_sb->s_flags & (MS_RDONLY |MS_POSIXACL ); + s->s_maxbytes = path.dentry->d_sb->s_maxbytes; s->s_blocksize = path.dentry->d_sb->s_blocksize; s->s_magic =ECRYPTFS_SUPER_MAGIC ;
fs/nfs/dns_resolve.c +3 -2
@@ -213,7 +213,7 @@ static int nfs_dns_parse(struct cache_detail *cd, char *buf, int buflen) {char buf1[NFS_DNS_HOSTNAME_MAXLEN +1 ];struct nfs_dns_ent key, *item; -unsigned long ttl; +unsigned int ttl;ssize_t len;int ret = -EINVAL ;
@@ -236,7 +236,8 @@ static int nfs_dns_parse(struct cache_detail *cd, char *buf, int buflen) key.namelen = len;memset (&key.h,0 ,sizeof (key.h)); - ttl =get_expiry (&buf); +if (get_uint (&buf, &ttl) <0 ) + goto out;if (ttl ==0 ) goto out; key.h.expiry_time = ttl +seconds_since_boot ();
fs/nfs/internal.h +3 -2
@@ -274,8 +274,9 @@ extern void nfs_sb_active(struct super_block *sb);extern void nfs_sb_deactive (struct super_block *sb);/* namespace.c */ +#define NFS_PATH_CANONICAL 1extern char *nfs_path (char **p,struct dentry *dentry, -char *buffer,ssize_t buflen); +char *buffer,ssize_t buflen,unsigned flags);extern struct vfsmount *nfs_d_automount (struct path *path);#ifdef CONFIG_NFS_V4 rpc_authflavor_t nfs_find_best_sec (struct nfs4_secinfo_flavors *);
@@ -364,7 +365,7 @@ static inline char *nfs_devname(struct dentry *dentry, char *buffer, ssize_t buflen) {char *dummy; -return nfs_path (&dummy, dentry, buffer, buflen); +return nfs_path (&dummy, dentry, buffer, buflen,NFS_PATH_CANONICAL ); }/*
fs/nfs/mount_clnt.c +1 -1
@@ -181,7 +181,7 @@ int nfs_mount(struct nfs_mount_request *info)else msg.rpc_proc = &mnt_clnt->cl_procinfo[MOUNTPROC_MNT ]; - status =rpc_call_sync (mnt_clnt, &msg,0 ); + status =rpc_call_sync (mnt_clnt, &msg,RPC_TASK_SOFT |RPC_TASK_TIMEOUT );rpc_shutdown_client (mnt_clnt);if (status <0 )
fs/nfs/namespace.c +14 -5
@@ -37,6 +37,7 @@ static struct vfsmount *nfs_do_submount(struct dentry *dentry,* @dentry - pointer to dentry * @buffer - result buffer * @buflen - length of buffer +* @flags - options (see below) * * Helper function for constructing the server pathname * by arbitrary hashed dentry.
@@ -44,8 +45,14 @@ static struct vfsmount *nfs_do_submount(struct dentry *dentry,* This is mainly for use in figuring out the path on the * server side when automounting on top of an existing partition * and in generating /proc/mounts and friends. +* +* Supported flags: +* NFS_PATH_CANONICAL: ensure there is exactly one slash after +* the original device (export) name +* (if unset, the original name is returned verbatim) */ -char *nfs_path (char **p,struct dentry *dentry,char *buffer,ssize_t buflen) +char *nfs_path (char **p,struct dentry *dentry,char *buffer,ssize_t buflen, +unsigned flags) {char *end;int namelen;
@@ -78,7 +85,7 @@ rename_retry:rcu_read_unlock (); goto rename_retry; } -if (*end !='/' ) { +if ((flags &NFS_PATH_CANONICAL ) && *end !='/' ) {if (--buflen <0 ) {spin_unlock (&dentry->d_lock);rcu_read_unlock ();
@@ -95,9 +102,11 @@ rename_retry:return end; } namelen =strlen (base); -/* Strip off excess slashes in base string */ -while (namelen >0 && base[namelen -1 ] =='/' ) - namelen--; +if (flags &NFS_PATH_CANONICAL ) { +/* Strip off excess slashes in base string */ +while (namelen >0 && base[namelen -1 ] =='/' ) + namelen--; + } buflen -= namelen;if (buflen <0 ) {spin_unlock (&dentry->d_lock);
fs/nfs/nfs4namespace.c +2 -1
@@ -57,7 +57,8 @@ Elong:static char *nfs4_path (struct dentry *dentry,char *buffer,ssize_t buflen) {char *limit; -char *path =nfs_path (&limit, dentry, buffer, buflen); +char *path =nfs_path (&limit, dentry, buffer, buflen, +NFS_PATH_CANONICAL );if (!IS_ERR (path)) {char *colon =strchr (path,':' );if (colon && colon < limit)
fs/nfs/nfs4proc.c +25 -15
@@ -303,8 +303,7 @@ static int nfs4_handle_exception(struct nfs_server *server, int errorcode, strucdprintk ("%s ERROR: %d Reset session\n" , __func__, errorcode);nfs4_schedule_session_recovery (clp->cl_session); - exception->retry =1 ; -break ; + goto wait_on_recovery;#endif /* defined(CONFIG_NFS_V4_1) */ case -NFS4ERR_FILE_OPEN :if (exception->timeout >HZ ) {
@@ -1464,9 +1463,11 @@ static void nfs4_open_prepare(struct rpc_task *task, void *calldata) data->timestamp = jiffies;if (nfs4_setup_sequence (data->o_arg.server, &data->o_arg.seq_args, - &data->o_res.seq_res,1 , task)) -return ; -rpc_call_start (task); + &data->o_res.seq_res, +1 , task) !=0 ) +nfs_release_seqid (data->o_arg.seqid); +else +rpc_call_start (task);return ; unlock_no_action:rcu_read_unlock ();
@@ -2046,9 +2047,10 @@ static void nfs4_close_prepare(struct rpc_task *task, void *data) calldata->timestamp = jiffies;if (nfs4_setup_sequence (NFS_SERVER (calldata->inode), &calldata->arg.seq_args, &calldata->res.seq_res, -1 , task)) -return ; -rpc_call_start (task); +1 , task) !=0 ) +nfs_release_seqid (calldata->arg.seqid); +else +rpc_call_start (task); }static const struct rpc_call_ops nfs4_close_ops = {
@@ -4148,6 +4150,7 @@ static void nfs4_locku_done(struct rpc_task *task, void *data)if (nfs4_async_handle_error (task, calldata->server,NULL ) == -EAGAIN )rpc_restart_call_prepare (task); } +nfs_release_seqid (calldata->arg.seqid); }static void nfs4_locku_prepare (struct rpc_task *task,void *data)
@@ -4164,9 +4167,11 @@ static void nfs4_locku_prepare(struct rpc_task *task, void *data) calldata->timestamp = jiffies;if (nfs4_setup_sequence (calldata->server, &calldata->arg.seq_args, - &calldata->res.seq_res,1 , task)) -return ; -rpc_call_start (task); + &calldata->res.seq_res, +1 , task) !=0 ) +nfs_release_seqid (calldata->arg.seqid); +else +rpc_call_start (task); }static const struct rpc_call_ops nfs4_locku_ops = {
@@ -4310,7 +4315,7 @@ static void nfs4_lock_prepare(struct rpc_task *task, void *calldata)/* Do we need to do an open_to_lock_owner? */ if (!(data->arg.lock_seqid->sequence->flags &NFS_SEQID_CONFIRMED )) {if (nfs_wait_on_sequence (data->arg.open_seqid, task) !=0 ) -return ; + goto out_release_lock_seqid; data->arg.open_stateid = &state->stateid; data->arg.new_lock_owner =1 ; data->res.open_seqid = data->arg.open_seqid;
@@ -4319,10 +4324,15 @@ static void nfs4_lock_prepare(struct rpc_task *task, void *calldata) data->timestamp = jiffies;if (nfs4_setup_sequence (data->server, &data->arg.seq_args, - &data->res.seq_res,1 , task)) + &data->res.seq_res, +1 , task) ==0 ) { +rpc_call_start (task);return ; -rpc_call_start (task); -dprintk ("%s: done!, ret = %d\n" , __func__, data->rpc_status); + } +nfs_release_seqid (data->arg.open_seqid); +out_release_lock_seqid: +nfs_release_seqid (data->arg.lock_seqid); +dprintk ("%s: done!, ret = %d\n" , __func__, task->tk_status); }static void nfs4_recover_lock_prepare (struct rpc_task *task,void *calldata)
fs/nfs/super.c +1 -1
@@ -768,7 +768,7 @@ static int nfs_show_devname(struct seq_file *m, struct vfsmount *mnt)int err =0 ;if (!page)return -ENOMEM ; - devname =nfs_path (&dummy, mnt->mnt_root, page,PAGE_SIZE ); + devname =nfs_path (&dummy, mnt->mnt_root, page,PAGE_SIZE ,0 );if (IS_ERR (devname)) err =PTR_ERR (devname);else
fs/nfsd/export.c +3 -3
@@ -401,7 +401,7 @@ fsloc_parse(char **mesg, char *buf, struct nfsd4_fs_locations *fsloc)int migrated, i, err;/* listsize */ - err =get_int (mesg, &fsloc->locations_count); + err =get_uint (mesg, &fsloc->locations_count);if (err)return err;if (fsloc->locations_count >MAX_FS_LOCATIONS )
@@ -459,7 +459,7 @@ static int secinfo_parse(char **mesg, char *buf, struct svc_export *exp)return -EINVAL ;for (f = exp->ex_flavors; f < exp->ex_flavors + listsize; f++) { - err =get_int (mesg, &f->pseudoflavor); + err =get_uint (mesg, &f->pseudoflavor);if (err)return err;/*
@@ -468,7 +468,7 @@ static int secinfo_parse(char **mesg, char *buf, struct svc_export *exp)* problem at export time instead of when a client fails * to authenticate. */ - err =get_int (mesg, &f->flags); + err =get_uint (mesg, &f->flags);if (err)return err;/* Only some flags are allowed to differ between flavors: */
fs/notify/fanotify/fanotify.c +1 -0
@@ -21,6 +21,7 @@ static bool should_merge(struct fsnotify_event *old, struct fsnotify_event *new)if ((old->path.mnt == new->path.mnt) && (old->path.dentry == new->path.dentry))return true; +break ;case (FSNOTIFY_EVENT_NONE ):return true;default :
fs/xfs/xfs_log_recover.c +1 -1
@@ -3514,7 +3514,7 @@ xlog_do_recovery_pass(* - order is important. */ error =xlog_bread_offset (log,0 , - bblks - split_bblks, hbp, + bblks - split_bblks, dbp, offset +BBTOB (split_bblks));if (error) goto bread_err2;
include/linux/if_link.h +1 -0
@@ -137,6 +137,7 @@ enum {IFLA_AF_SPEC ,IFLA_GROUP ,/* Group the device belongs to */ IFLA_NET_NS_FD , +IFLA_EXT_MASK ,/* Extended info mask, VFs, etc */ __IFLA_MAX };
include/linux/rtnetlink.h +3 -0
@@ -602,6 +602,9 @@ struct tcamsg {#define TCA_ACT_TAB 1/* attr type must be >=1 */ #define TCAA_MAX 1 +/* New extended info filters for IFLA_EXT_MASK */ +#define RTEXT_FILTER_VF (1 << 0) +/* End of information exported to user level */ #ifdef __KERNEL__
include/linux/sunrpc/cache.h +16 -0
@@ -224,6 +224,22 @@ static inline int get_int(char **bpp, int *anint)return 0 ; } +static inline int get_uint (char **bpp,unsigned int *anint) +{ +char buf[50 ]; +int len =qword_get (bpp, buf,sizeof (buf)); + +if (len <0 ) +return -EINVAL ; +if (len ==0 ) +return -ENOENT ; + +if (kstrtouint (buf,0 , anint)) +return -EINVAL ; + +return 0 ; +} +/* * timestamps kept in the cache are expressed in seconds * since boot. This is the best for measuring differences in
include/net/bluetooth/bluetooth.h +0 -22
@@ -218,32 +218,10 @@ extern void bt_sysfs_cleanup(void);extern struct dentry *bt_debugfs; -#ifdef CONFIG_BT_L2CAP int l2cap_init (void );void l2cap_exit (void ); -#else -static inline int l2cap_init (void ) -{ -return 0 ; -} - -static inline void l2cap_exit (void ) -{ -} -#endif -#ifdef CONFIG_BT_SCO int sco_init (void );void sco_exit (void ); -#else -static inline int sco_init (void ) -{ -return 0 ; -} - -static inline void sco_exit (void ) -{ -} -#endif #endif /* __BLUETOOTH_H */
include/net/cfg80211.h +9 -0
@@ -2431,6 +2431,15 @@ unsigned int ieee80211_get_hdrlen_from_skb(const struct sk_buff *skb); unsigned int __attribute_const__ ieee80211_hdrlen(__le16 fc);/** +* ieee80211_get_mesh_hdrlen - get mesh extension header length +* @meshhdr: the mesh extension header, only the flags field +* (first byte) will be accessed +* Returns the length of the extension header, which is always at +* least 6 bytes and at most 18 if address 5 and 6 are present. +*/ +unsigned int ieee80211_get_mesh_hdrlen (struct ieee80211s_hdr *meshhdr); + +/** * DOC: Data path helpers * * In addition to generic utilities, cfg80211 also offers
include/net/rtnetlink.h +1 -1
@@ -6,7 +6,7 @@typedef int (*rtnl_doit_func )(struct sk_buff *,struct nlmsghdr *,void *);typedef int (*rtnl_dumpit_func )(struct sk_buff *,struct netlink_callback *); -typedef u16 (*rtnl_calcit_func )(struct sk_buff *); +typedef u16 (*rtnl_calcit_func )(struct sk_buff *,struct nlmsghdr *); extern int __rtnl_register(int protocol, int msgtype, rtnl_doit_func, rtnl_dumpit_func,
include/sound/core.h +3 -0
@@ -132,6 +132,7 @@ struct snd_card {int shutdown;/* this card is going down */ int free_on_last_close;/* free in context of file_release */ wait_queue_head_t shutdown_sleep; +atomic_t refcount;/* refcount for disconnection */ struct device *dev;/* device assigned to this card */ struct device *card_dev;/* cardX object for sysfs */
@@ -189,6 +190,7 @@ struct snd_minor {const struct file_operations *f_ops;/* file operations */ void *private_data;/* private data for f_ops->open */ struct device *dev;/* device for sysfs */ +struct snd_card *card_ptr;/* assigned card instance */ };/* return a device pointer linked to each sound device as a parent */
@@ -295,6 +297,7 @@ int snd_card_info_done(void);int snd_component_add (struct snd_card *card,const char *component);int snd_card_file_add (struct snd_card *card,struct file *file);int snd_card_file_remove (struct snd_card *card,struct file *file); +void snd_card_unref (struct snd_card *card);#define snd_card_set_dev (card, devptr) ((card)->dev = (devptr))
include/trace/events/xen.h +8 -0
@@ -377,6 +377,14 @@ DECLARE_EVENT_CLASS(xen_mmu_pgd,DEFINE_XEN_MMU_PGD_EVENT (xen_mmu_pgd_pin);DEFINE_XEN_MMU_PGD_EVENT (xen_mmu_pgd_unpin); +TRACE_EVENT (xen_mmu_flush_tlb_all, + TP_PROTO(int x), +TP_ARGS (x), +TP_STRUCT__entry (__array (char, x,0 )), +TP_fast_assign ((void )x), +TP_printk ("%s" ,"" ) + ); + TRACE_EVENT(xen_mmu_flush_tlb, TP_PROTO(int x), TP_ARGS(x),
kernel/module.c +13 -11
@@ -2193,15 +2193,17 @@ static void layout_symtab(struct module *mod, struct load_info *info) src = (void *)info->hdr + symsect->sh_offset; nsrc = symsect->sh_size /sizeof (*src); -for (ndst = i =1 ; i < nsrc; ++i, ++src) -if (is_core_symbol (src, info->sechdrs, info->hdr->e_shnum)) { -unsigned int j = src->st_name; +for (ndst = i =0 ; i < nsrc; i++) { +if (i ==0 || +is_core_symbol (src+i, info->sechdrs, info->hdr->e_shnum)) { +unsigned int j = src[i].st_name;while (!__test_and_set_bit (j, info->strmap) && info->strtab[j]) ++j; ++ndst; } + }/* Append room for core symbols at end of core part. */ info->symoffs =ALIGN (mod->core_size, symsect->sh_addralign ?:1 );
@@ -2238,14 +2240,14 @@ static void add_kallsyms(struct module *mod, const struct load_info *info) mod->core_symtab = dst = mod->module_core + info->symoffs; src = mod->symtab; - *dst = *src; -for (ndst = i =1 ; i < mod->num_symtab; ++i, ++src) { -if (!is_core_symbol (src, info->sechdrs, info->hdr->e_shnum)) -continue ; - dst[ndst] = *src; - dst[ndst].st_name =bitmap_weight (info->strmap, - dst[ndst].st_name); - ++ndst; +for (ndst = i =0 ; i < mod->num_symtab; i++) { +if (i ==0 || +is_core_symbol (src+i, info->sechdrs, info->hdr->e_shnum)) { + dst[ndst] = src[i]; + dst[ndst].st_name =bitmap_weight (info->strmap, + dst[ndst].st_name); + ++ndst; + } } mod->core_num_syms = ndst;
mm/vmscan.c +2 -0
@@ -3015,6 +3015,8 @@ static int kswapd(void *p) &balanced_classzone_idx); } } + + current->reclaim_state =NULL ;return 0 ; }
net/bluetooth/Kconfig +9 -28
@@ -6,7 +6,11 @@ menuconfig BT tristate "Bluetooth subsystem support" depends on NET && !S390 depends on RFKILL || !RFKILL + select CRC16 select CRYPTO + select CRYPTO_BLKCIPHER + select CRYPTO_AES + select CRYPTO_ECB help Bluetooth is low-cost, low-power, short-range wireless technology. It was designed as a replacement for cables and other short-range
@@ -15,10 +19,12 @@ menuconfig BT Bluetooth can be found at <http://www.bluetooth.com/>. Linux Bluetooth subsystem consist of several layers: - Bluetooth Core (HCI device and connection manager, scheduler) + Bluetooth Core + HCI device and connection manager, scheduler + SCO audio links + L2CAP (Logical Link Control and Adaptation Protocol) + SMP (Security Manager Protocol) on LE (Low Energy) links HCI Device drivers (Interface to the hardware) - SCO Module (SCO audio links) - L2CAP Module (Logical Link Control and Adaptation Protocol) RFCOMM Module (RFCOMM Protocol) BNEP Module (Bluetooth Network Encapsulation Protocol) CMTP Module (CAPI Message Transport Protocol)
@@ -33,31 +39,6 @@ menuconfig BT to Bluetooth kernel modules are provided in the BlueZ packages. For more information, see <http://www.bluez.org/>. -if BT != n - -config BT_L2CAP - bool "L2CAP protocol support" - select CRC16 - select CRYPTO - select CRYPTO_BLKCIPHER - select CRYPTO_AES - select CRYPTO_ECB - help - L2CAP (Logical Link Control and Adaptation Protocol) provides - connection oriented and connection-less data transport. L2CAP - support is required for most Bluetooth applications. - - Also included is support for SMP (Security Manager Protocol) which - is the security layer on top of LE (Low Energy) links. - -config BT_SCO - bool "SCO links support" - help - SCO link provides voice transport over Bluetooth. SCO support is - required for voice applications like Headset and Audio. - -endif - source "net/bluetooth/rfcomm/Kconfig" source "net/bluetooth/bnep/Kconfig"
net/bluetooth/Makefile +2 -3
@@ -8,6 +8,5 @@ obj-$(CONFIG_BT_BNEP) += bnep/ obj-$(CONFIG_BT_CMTP) += cmtp/ obj-$(CONFIG_BT_HIDP) += hidp/ -bluetooth-y := af_bluetooth.o hci_core.o hci_conn.o hci_event.o mgmt.o hci_sock.o hci_sysfs.o lib.o -bluetooth-$(CONFIG_BT_L2CAP) += l2cap_core.o l2cap_sock.o smp.o -bluetooth-$(CONFIG_BT_SCO) += sco.o +bluetooth-y := af_bluetooth.o hci_core.o hci_conn.o hci_event.o mgmt.o \ + hci_sock.o hci_sysfs.o l2cap_core.o l2cap_sock.o smp.o sco.o lib.o
net/bluetooth/bnep/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_BNEP tristate "BNEP protocol support" - depends on BT && BT_L2CAP + depends on BT select CRC32 help BNEP (Bluetooth Network Encapsulation Protocol) is Ethernet
net/bluetooth/cmtp/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_CMTP tristate "CMTP protocol support" - depends on BT && BT_L2CAP && ISDN_CAPI + depends on BT && ISDN_CAPI help CMTP (CAPI Message Transport Protocol) is a transport layer for CAPI messages. CMTP is required for the Bluetooth Common
net/bluetooth/hidp/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_HIDP tristate "HIDP protocol support" - depends on BT && BT_L2CAP && INPUT && HID_SUPPORT + depends on BT && INPUT && HID_SUPPORT select HID help HIDP (Human Interface Device Protocol) is a transport layer
net/bluetooth/rfcomm/Kconfig +1 -1
@@ -1,6 +1,6 @@ config BT_RFCOMM tristate "RFCOMM protocol support" - depends on BT && BT_L2CAP + depends on BT help RFCOMM provides connection oriented stream transport. RFCOMM support is required for Dialup Networking, OBEX and other Bluetooth
net/core/dev.c +1 -1
@@ -1633,7 +1633,7 @@ static inline int deliver_skb(struct sk_buff *skb,static inline bool skb_loop_sk (struct packet_type *ptype,struct sk_buff *skb) { -if (ptype->af_packet_priv ==NULL ) +if (!ptype->af_packet_priv || !skb->sk)return false;if (ptype->id_match)
net/core/rtnetlink.c +59 -19
185 lines not on this page · raw message
net/ipv4/tcp.c +3 -5
@@ -481,14 +481,12 @@ int tcp_ioctl(struct sock *sk, int cmd, unsigned long arg) !tp->urg_data || before(tp->urg_seq, tp->copied_seq) || !before(tp->urg_seq, tp->rcv_nxt)) { -struct sk_buff *skb; answ = tp->rcv_nxt - tp->copied_seq; -/* Subtract 1, if FIN is in queue. */ - skb =skb_peek_tail (&sk->sk_receive_queue); -if (answ && skb) - answ -=tcp_hdr (skb)->fin; +/* Subtract 1, if FIN was received */ +if (answ &&sock_flag (sk,SOCK_DONE )) + answ--; } else answ = tp->urg_seq - tp->copied_seq;release_sock (sk);
net/ipv4/tcp_illinois.c +5 -3
@@ -313,11 +313,13 @@ static void tcp_illinois_info(struct sock *sk, u32 ext, .tcpv_rttcnt = ca->cnt_rtt, .tcpv_minrtt = ca->base_rtt, }; -u64 t = ca->sum_rtt; -do_div (t, ca->cnt_rtt); - info.tcpv_rtt = t; +if (info.tcpv_rttcnt >0 ) { +u64 t = ca->sum_rtt; +do_div (t, info.tcpv_rttcnt); + info.tcpv_rtt = t; + }nla_put (skb,INET_DIAG_VEGASINFO ,sizeof (info), &info); } }
net/ipv6/ndisc.c +1 -2
@@ -606,7 +606,7 @@ static void ndisc_send_unsol_na(struct net_device *dev) {struct inet6_dev *idev;struct inet6_ifaddr *ifa; -struct in6_addr mcaddr; +struct in6_addr mcaddr =IN6ADDR_LINKLOCAL_ALLNODES_INIT ; idev =in6_dev_get (dev);if (!idev)
@@ -614,7 +614,6 @@ static void ndisc_send_unsol_na(struct net_device *dev)read_lock_bh (&idev->lock);list_for_each_entry (ifa, &idev->addr_list, if_list) { -addrconf_addr_solict_mult (&ifa->addr, &mcaddr); ndisc_send_na(dev, NULL, &mcaddr, &ifa->addr, /*router=*/ !!idev->cnf.forwarding, /*solicited=*/ false, /*override=*/ true,
net/ipv6/route.c +2 -2
@@ -185,7 +185,7 @@ static struct dst_ops ip6_dst_blackhole_ops = { };static const u32 ip6_template_metrics[RTAX_MAX ] = { - [RTAX_HOPLIMIT -1 ] =255 , + [RTAX_HOPLIMIT -1 ] =0 , };static struct rt6_info ip6_null_entry_template = {
@@ -1097,7 +1097,7 @@ struct dst_entry *icmp6_dst_alloc(struct net_device *dev,ipv6_addr_copy (&rt->rt6i_dst.addr, addr); rt->rt6i_dst.plen =128 ; rt->rt6i_idev = idev; -dst_metric_set (&rt->dst,RTAX_HOPLIMIT ,255 ); +dst_metric_set (&rt->dst,RTAX_HOPLIMIT ,0 );spin_lock_bh (&icmp6_dst_lock); rt->dst.next = icmp6_dst_gc_list;
net/l2tp/l2tp_eth.c +1 -0
@@ -269,6 +269,7 @@ static int l2tp_eth_create(struct net *net, u32 tunnel_id, u32 session_id, u32 p out_del_dev:free_netdev (dev); + spriv->dev =NULL ; out_del_session:l2tp_session_delete (session); out:
net/mac80211/ibss.c +1 -1
@@ -940,7 +940,7 @@ int ieee80211_ibss_join(struct ieee80211_sub_if_data *sdata, sdata->u.ibss.state =IEEE80211_IBSS_MLME_SEARCH ; sdata->u.ibss.ibss_join_req = jiffies; -memcpy (sdata->u.ibss.ssid, params->ssid,IEEE80211_MAX_SSID_LEN ); +memcpy (sdata->u.ibss.ssid, params->ssid, params->ssid_len); sdata->u.ibss.ssid_len = params->ssid_len;mutex_unlock (&sdata->u.ibss.mtx);
net/mac80211/rx.c +56 -15
138 lines not on this page · raw message
net/netlink/af_netlink.c +15 -4
@@ -137,6 +137,8 @@ static void netlink_destroy_callback(struct netlink_callback *cb);static DEFINE_RWLOCK (nl_table_lock);static atomic_t nl_table_users =ATOMIC_INIT (0 ); +#define nl_deref_protected (X ) rcu_dereference_protected(X, lockdep_is_held(&nl_table_lock)); +static ATOMIC_NOTIFIER_HEAD (netlink_chain);static u32 netlink_group_mask (u32 group)
@@ -331,6 +333,11 @@ netlink_update_listeners(struct sock *sk)struct hlist_node *node;unsigned long mask;unsigned int i; +struct listeners *listeners; + + listeners =nl_deref_protected (tbl->listeners); +if (!listeners) +return ;for (i =0 ; i <NLGRPLONGS (tbl->groups); i++) { mask =0 ;
@@ -338,7 +345,7 @@ netlink_update_listeners(struct sock *sk)if (i <NLGRPLONGS (nlk_sk (sk)->ngroups)) mask |=nlk_sk (sk)->groups[i]; } - tbl->listeners->masks[i] = mask; + listeners->masks[i] = mask; }/* this function is only called with the netlink table "grabbed", which * makes sure updates are visible before bind or setsockopt return. */
@@ -519,7 +526,11 @@ static int netlink_release(struct socket *sock)if (netlink_is_kernel (sk)) {BUG_ON (nl_table[sk->sk_protocol].registered ==0 );if (--nl_table[sk->sk_protocol].registered ==0 ) { -kfree (nl_table[sk->sk_protocol].listeners); +struct listeners *old; + + old =nl_deref_protected (nl_table[sk->sk_protocol].listeners); +RCU_INIT_POINTER (nl_table[sk->sk_protocol].listeners,NULL ); +kfree_rcu (old, rcu); nl_table[sk->sk_protocol].module =NULL ; nl_table[sk->sk_protocol].registered =0 ; }
@@ -950,7 +961,7 @@ int netlink_has_listeners(struct sock *sk, unsigned int group)rcu_read_lock (); listeners =rcu_dereference (nl_table[sk->sk_protocol].listeners); -if (group -1 < nl_table[sk->sk_protocol].groups) +if (listeners && group -1 < nl_table[sk->sk_protocol].groups) res =test_bit (group -1 , listeners->masks);rcu_read_unlock ();
@@ -1584,7 +1595,7 @@ int __netlink_change_ngroups(struct sock *sk, unsigned int groups) new =kzalloc (sizeof (*new) +NLGRPSZ (groups),GFP_ATOMIC );if (!new)return -ENOMEM ; - old =rcu_dereference_protected (tbl->listeners,1 ); + old =nl_deref_protected (tbl->listeners);memcpy (new->masks, old->masks,NLGRPSZ (tbl->groups));rcu_assign_pointer (tbl->listeners, new);
net/sctp/sm_sideeffect.c +2 -1
@@ -1604,8 +1604,9 @@ static int sctp_cmd_interpreter(sctp_event_t event_type, asoc->outqueue.outstanding_bytes; sackh.num_gap_ack_blocks =0 ; sackh.num_dup_tsns =0 ; + chunk->subh.sack_hdr = &sackh;sctp_add_cmd_sf (commands,SCTP_CMD_PROCESS_SACK , -SCTP_SACKH (&sackh)); +SCTP_CHUNK (chunk));break ;case SCTP_CMD_DISCARD_PACKET :
net/wireless/core.c +1 -2
@@ -548,8 +548,7 @@ int wiphy_register(struct wiphy *wiphy)for (i =0 ; i < sband->n_channels; i++) { sband->channels[i].orig_flags = sband->channels[i].flags; - sband->channels[i].orig_mag = - sband->channels[i].max_antenna_gain; + sband->channels[i].orig_mag =INT_MAX ; sband->channels[i].orig_mpwr = sband->channels[i].max_power; sband->channels[i].band = band;
net/wireless/util.c +8 -6
@@ -301,23 +301,21 @@ unsigned int ieee80211_get_hdrlen_from_skb(const struct sk_buff *skb) }EXPORT_SYMBOL (ieee80211_get_hdrlen_from_skb); -static int ieee80211_get_mesh_hdrlen (struct ieee80211s_hdr *meshhdr) +unsigned int ieee80211_get_mesh_hdrlen (struct ieee80211s_hdr *meshhdr) {int ae = meshhdr->flags &MESH_FLAGS_AE ; -/* 7.1.3.5a.2 */ +/* 802.11-2012, 8.2.4.7.3 */ switch (ae) { +default :case 0 :return 6 ;case MESH_FLAGS_AE_A4 :return 12 ;case MESH_FLAGS_AE_A5_A6 :return 18 ; -case (MESH_FLAGS_AE_A4 |MESH_FLAGS_AE_A5_A6 ): -return 24 ; -default : -return 6 ; } } +EXPORT_SYMBOL (ieee80211_get_mesh_hdrlen);int ieee80211_data_to_8023 (struct sk_buff *skb,const u8 *addr,enum nl80211_iftype iftype)
@@ -365,6 +363,8 @@ int ieee80211_data_to_8023(struct sk_buff *skb, const u8 *addr,/* make sure meshdr->flags is on the linear part */ if (!pskb_may_pull (skb, hdrlen +1 ))return -1 ; +if (meshdr->flags &MESH_FLAGS_AE_A4 ) +return -1 ;if (meshdr->flags &MESH_FLAGS_AE_A5_A6 ) { skb_copy_bits(skb, hdrlen + offsetof(struct ieee80211s_hdr, eaddr1),
@@ -389,6 +389,8 @@ int ieee80211_data_to_8023(struct sk_buff *skb, const u8 *addr,/* make sure meshdr->flags is on the linear part */ if (!pskb_may_pull (skb, hdrlen +1 ))return -1 ; +if (meshdr->flags &MESH_FLAGS_AE_A5_A6 ) +return -1 ;if (meshdr->flags &MESH_FLAGS_AE_A4 ) skb_copy_bits(skb, hdrlen + offsetof(struct ieee80211s_hdr, eaddr1),
sound/core/control.c +5 -0
@@ -86,6 +86,7 @@ static int snd_ctl_open(struct inode *inode, struct file *file)write_lock_irqsave (&card->ctl_files_rwlock, flags);list_add_tail (&ctl->list, &card->ctl_files);write_unlock_irqrestore (&card->ctl_files_rwlock, flags); +snd_card_unref (card);return 0 ; __error:
@@ -93,6 +94,8 @@ static int snd_ctl_open(struct inode *inode, struct file *file) __error2:snd_card_file_remove (card, file); __error1: +if (card) +snd_card_unref (card);return err; }
@@ -1433,6 +1436,8 @@ static ssize_t snd_ctl_read(struct file *file, char __user *buffer,spin_unlock_irq (&ctl->read_lock);schedule ();remove_wait_queue (&ctl->change_sleep, &wait); +if (ctl->card->shutdown) +return -ENODEV ;if (signal_pending (current))return -ERESTARTSYS ;spin_lock_irq (&ctl->read_lock);
sound/core/hwdep.c +11 -1
@@ -100,8 +100,10 @@ static int snd_hwdep_open(struct inode *inode, struct file * file)if (hw ==NULL )return -ENODEV ; -if (!try_module_get (hw->card->module)) +if (!try_module_get (hw->card->module)) { +snd_card_unref (hw->card);return -EFAULT ; + }init_waitqueue_entry (&wait, current);add_wait_queue (&hw->open_wait, &wait);
@@ -129,6 +131,10 @@ static int snd_hwdep_open(struct inode *inode, struct file * file)mutex_unlock (&hw->open_mutex);schedule ();mutex_lock (&hw->open_mutex); +if (hw->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
@@ -148,6 +154,7 @@ static int snd_hwdep_open(struct inode *inode, struct file * file)mutex_unlock (&hw->open_mutex);if (err <0 )module_put (hw->card->module); +snd_card_unref (hw->card);return err; }
@@ -459,12 +466,15 @@ static int snd_hwdep_dev_disconnect(struct snd_device *device)mutex_unlock (®ister_mutex);return -EINVAL ; } +mutex_lock (&hwdep->open_mutex); +wake_up (&hwdep->open_wait);#ifdef CONFIG_SND_OSSEMUL if (hwdep->ossreg)snd_unregister_oss_device (hwdep->oss_type, hwdep->card, hwdep->device);#endif snd_unregister_device (SNDRV_DEVICE_TYPE_HWDEP , hwdep->card, hwdep->device);list_del_init (&hwdep->list); +mutex_unlock (&hwdep->open_mutex);mutex_unlock (®ister_mutex);return 0 ; }
sound/core/init.c +30 -20
96 lines not on this page · raw message
sound/core/oss/mixer_oss.c +9 -2
@@ -52,14 +52,19 @@ static int snd_mixer_oss_open(struct inode *inode, struct file *file) SNDRV_OSS_DEVICE_TYPE_MIXER);if (card ==NULL )return -ENODEV ; -if (card->mixer_oss ==NULL ) +if (card->mixer_oss ==NULL ) { +snd_card_unref (card);return -ENODEV ; + } err =snd_card_file_add (card, file); -if (err <0 ) +if (err <0 ) { +snd_card_unref (card);return err; + } fmixer =kzalloc (sizeof (*fmixer),GFP_KERNEL );if (fmixer ==NULL ) {snd_card_file_remove (card, file); +snd_card_unref (card);return -ENOMEM ; } fmixer->card = card;
@@ -68,8 +73,10 @@ static int snd_mixer_oss_open(struct inode *inode, struct file *file)if (!try_module_get (card->module)) {kfree (fmixer);snd_card_file_remove (card, file); +snd_card_unref (card);return -EFAULT ; } +snd_card_unref (card);return 0 ; }
sound/core/oss/pcm_oss.c +7 -0
@@ -2441,6 +2441,10 @@ static int snd_pcm_oss_open(struct inode *inode, struct file *file)mutex_unlock (&pcm->open_mutex);schedule ();mutex_lock (&pcm->open_mutex); +if (pcm->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
@@ -2450,6 +2454,7 @@ static int snd_pcm_oss_open(struct inode *inode, struct file *file)mutex_unlock (&pcm->open_mutex);if (err <0 ) goto __error; +snd_card_unref (pcm->card);return err; __error:
@@ -2457,6 +2462,8 @@ static int snd_pcm_oss_open(struct inode *inode, struct file *file) __error2:snd_card_file_remove (pcm->card, file); __error1: +if (pcm) +snd_card_unref (pcm->card);return err; }
sound/core/pcm.c +11 -2
@@ -1046,11 +1046,19 @@ static int snd_pcm_dev_disconnect(struct snd_device *device)if (list_empty (&pcm->list)) goto unlock; +mutex_lock (&pcm->open_mutex); +wake_up (&pcm->open_wait);list_del_init (&pcm->list);for (cidx =0 ; cidx <2 ; cidx++) -for (substream = pcm->streams[cidx].substream; substream; substream = substream->next) -if (substream->runtime) +for (substream = pcm->streams[cidx].substream; substream; substream = substream->next) { +snd_pcm_stream_lock_irq (substream); +if (substream->runtime) { substream->runtime->status->state =SNDRV_PCM_STATE_DISCONNECTED ; +wake_up (&substream->runtime->sleep); +wake_up (&substream->runtime->tsleep); + } +snd_pcm_stream_unlock_irq (substream); + }list_for_each_entry (notify, &snd_pcm_notify_list, list) { notify->n_disconnect (pcm); }
@@ -1066,6 +1074,7 @@ static int snd_pcm_dev_disconnect(struct snd_device *device) }snd_unregister_device (devtype, pcm->card, pcm->device); } +mutex_unlock (&pcm->open_mutex); unlock:mutex_unlock (®ister_mutex);return 0 ;
sound/core/pcm_native.c +29 -6
@@ -369,6 +369,14 @@ static int period_to_usecs(struct snd_pcm_runtime *runtime)return usecs; } +static void snd_pcm_set_state (struct snd_pcm_substream *substream,int state) +{ +snd_pcm_stream_lock_irq (substream); +if (substream->runtime->status->state !=SNDRV_PCM_STATE_DISCONNECTED ) + substream->runtime->status->state = state; +snd_pcm_stream_unlock_irq (substream); +} +static int snd_pcm_hw_params (struct snd_pcm_substream *substream,struct snd_pcm_hw_params *params) {
@@ -452,7 +460,7 @@ static int snd_pcm_hw_params(struct snd_pcm_substream *substream, runtime->boundary *=2 ;snd_pcm_timer_resolution_change (substream); - runtime->status->state =SNDRV_PCM_STATE_SETUP ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_SETUP );if (pm_qos_request_active (&substream->latency_pm_qos_req))pm_qos_remove_request (&substream->latency_pm_qos_req);
@@ -464,7 +472,7 @@ static int snd_pcm_hw_params(struct snd_pcm_substream *substream,/* hardware might be unusable from this time, so we force application to retry to set the correct hardware parameter settings */ - runtime->status->state =SNDRV_PCM_STATE_OPEN ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_OPEN );if (substream->ops->hw_free !=NULL ) substream->ops->hw_free (substream);return err;
@@ -512,7 +520,7 @@ static int snd_pcm_hw_free(struct snd_pcm_substream *substream)return -EBADFD ;if (substream->ops->hw_free) result = substream->ops->hw_free (substream); - runtime->status->state =SNDRV_PCM_STATE_OPEN ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_OPEN );pm_qos_remove_request (&substream->latency_pm_qos_req);return result; }
@@ -1320,7 +1328,7 @@ static void snd_pcm_post_prepare(struct snd_pcm_substream *substream, int state) {struct snd_pcm_runtime *runtime = substream->runtime; runtime->control->appl_ptr = runtime->status->hw_ptr; - runtime->status->state =SNDRV_PCM_STATE_PREPARED ; +snd_pcm_set_state (substream,SNDRV_PCM_STATE_PREPARED ); }static struct action_ops snd_pcm_action_prepare = {
@@ -1500,6 +1508,10 @@ static int snd_pcm_drain(struct snd_pcm_substream *substream,down_read (&snd_pcm_link_rwsem);snd_pcm_stream_lock_irq (substream);remove_wait_queue (&to_check->sleep, &wait); +if (card->shutdown) { + result = -ENODEV ; +break ; + }if (tout ==0 ) {if (substream->runtime->status->state ==SNDRV_PCM_STATE_SUSPENDED ) result = -ESTRPIPE ;
@@ -1620,6 +1632,7 @@ static int snd_pcm_link(struct snd_pcm_substream *substream, int fd) _end:write_unlock_irq (&snd_pcm_link_rwlock);up_write (&snd_pcm_link_rwsem); +snd_card_unref (substream1->pcm->card);fput (file);return res; }
@@ -2092,7 +2105,10 @@ static int snd_pcm_playback_open(struct inode *inode, struct file *file)return err; pcm =snd_lookup_minor_data (iminor (inode),SNDRV_DEVICE_TYPE_PCM_PLAYBACK ); -return snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_PLAYBACK ); + err =snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_PLAYBACK ); +if (pcm) +snd_card_unref (pcm->card); +return err; }static int snd_pcm_capture_open (struct inode *inode,struct file *file)
@@ -2103,7 +2119,10 @@ static int snd_pcm_capture_open(struct inode *inode, struct file *file)return err; pcm =snd_lookup_minor_data (iminor (inode),SNDRV_DEVICE_TYPE_PCM_CAPTURE ); -return snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_CAPTURE ); + err =snd_pcm_open (file, pcm,SNDRV_PCM_STREAM_CAPTURE ); +if (pcm) +snd_card_unref (pcm->card); +return err; }static int snd_pcm_open (struct file *file,struct snd_pcm *pcm,int stream)
@@ -2140,6 +2159,10 @@ static int snd_pcm_open(struct file *file, struct snd_pcm *pcm, int stream)mutex_unlock (&pcm->open_mutex);schedule ();mutex_lock (&pcm->open_mutex); +if (pcm->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
sound/core/rawmidi.c +25 -1
@@ -379,8 +379,10 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file)if (rmidi ==NULL )return -ENODEV ; -if (!try_module_get (rmidi->card->module)) +if (!try_module_get (rmidi->card->module)) { +snd_card_unref (rmidi->card);return -ENXIO ; + }mutex_lock (&rmidi->open_mutex); card = rmidi->card;
@@ -422,6 +424,10 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file)mutex_unlock (&rmidi->open_mutex);schedule ();mutex_lock (&rmidi->open_mutex); +if (rmidi->card->shutdown) { + err = -ENODEV ; +break ; + }if (signal_pending (current)) { err = -ERESTARTSYS ;break ;
@@ -440,6 +446,7 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file)#endif file->private_data = rawmidi_file;mutex_unlock (&rmidi->open_mutex); +snd_card_unref (rmidi->card);return 0 ; __error:
@@ -447,6 +454,7 @@ static int snd_rawmidi_open(struct inode *inode, struct file *file) __error_card:mutex_unlock (&rmidi->open_mutex);module_put (rmidi->card->module); +snd_card_unref (rmidi->card);return err; }
@@ -991,6 +999,8 @@ static ssize_t snd_rawmidi_read(struct file *file, char __user *buf, size_t counspin_unlock_irq (&runtime->lock);schedule ();remove_wait_queue (&runtime->sleep, &wait); +if (rfile->rmidi->card->shutdown) +return -ENODEV ;if (signal_pending (current))return result >0 ? result : -ERESTARTSYS ;if (!runtime->avail)
@@ -1234,6 +1244,8 @@ static ssize_t snd_rawmidi_write(struct file *file, const char __user *buf,spin_unlock_irq (&runtime->lock); timeout =schedule_timeout (30 *HZ );remove_wait_queue (&runtime->sleep, &wait); +if (rfile->rmidi->card->shutdown) +return -ENODEV ;if (signal_pending (current))return result >0 ? result : -ERESTARTSYS ;if (!runtime->avail && !timeout)
@@ -1609,9 +1621,20 @@ static int snd_rawmidi_dev_register(struct snd_device *device)static int snd_rawmidi_dev_disconnect (struct snd_device *device) {struct snd_rawmidi *rmidi = device->device_data; +int dir;mutex_lock (®ister_mutex); +mutex_lock (&rmidi->open_mutex); +wake_up (&rmidi->open_wait);list_del_init (&rmidi->list); +for (dir =0 ; dir <2 ; dir++) { +struct snd_rawmidi_substream *s; +list_for_each_entry (s, &rmidi->streams[dir].substreams, list) { +if (s->runtime) +wake_up (&s->runtime->sleep); + } + } +#ifdef CONFIG_SND_OSSEMUL if (rmidi->ossreg) {if ((int )rmidi->device == midi_map[rmidi->card->number]) {
@@ -1626,6 +1649,7 @@ static int snd_rawmidi_dev_disconnect(struct snd_device *device) }#endif /* CONFIG_SND_OSSEMUL */ snd_unregister_device (SNDRV_DEVICE_TYPE_RAWMIDI , rmidi->card, rmidi->device); +mutex_unlock (&rmidi->open_mutex);mutex_unlock (®ister_mutex);return 0 ; }
sound/core/sound.c +9 -2
@@ -99,6 +99,10 @@ static void snd_request_other(int minor)* * Checks that a minor device with the specified type is registered, and returns * its user data pointer. +* +* This function increments the reference counter of the card instance +* if an associated instance with the given minor number and type is found. +* The caller must call snd_card_unref() appropriately later. */ void *snd_lookup_minor_data (unsigned int minor,int type) {
@@ -109,9 +113,11 @@ void *snd_lookup_minor_data(unsigned int minor, int type)return NULL ;mutex_lock (&sound_mutex); mreg = snd_minors[minor]; -if (mreg && mreg->type == type) +if (mreg && mreg->type == type) { private_data = mreg->private_data; -else +if (private_data && mreg->card_ptr) +atomic_inc (&mreg->card_ptr->refcount); + }else private_data =NULL ;mutex_unlock (&sound_mutex);return private_data;
@@ -275,6 +281,7 @@ int snd_register_device_for_dev(int type, struct snd_card *card, int dev, preg->device = dev; preg->f_ops = f_ops; preg->private_data = private_data; + preg->card_ptr = card;mutex_lock (&sound_mutex);#ifdef CONFIG_SND_DYNAMIC_MINORS minor =snd_find_free_minor (type);
sound/core/sound_oss.c +8 -2
@@ -40,6 +40,9 @@static struct snd_minor *snd_oss_minors[SNDRV_OSS_MINORS ];static DEFINE_MUTEX (sound_oss_mutex); +/* NOTE: This function increments the refcount of the associated card like +* snd_lookup_minor_data(); the caller must call snd_card_unref() appropriately +*/ void *snd_lookup_oss_minor_data (unsigned int minor,int type) {struct snd_minor *mreg;
@@ -49,9 +52,11 @@ void *snd_lookup_oss_minor_data(unsigned int minor, int type)return NULL ;mutex_lock (&sound_oss_mutex); mreg = snd_oss_minors[minor]; -if (mreg && mreg->type == type) +if (mreg && mreg->type == type) { private_data = mreg->private_data; -else +if (private_data && mreg->card_ptr) +atomic_inc (&mreg->card_ptr->refcount); + }else private_data =NULL ;mutex_unlock (&sound_oss_mutex);return private_data;
@@ -123,6 +128,7 @@ int snd_register_oss_device(int type, struct snd_card *card, int dev, preg->device = dev; preg->f_ops = f_ops; preg->private_data = private_data; + preg->card_ptr = card;mutex_lock (&sound_oss_mutex); snd_oss_minors[minor] = preg; minor_unit =SNDRV_MINOR_OSS_DEVICE (minor);
sound/pci/hda/patch_analog.c +1 -0
@@ -573,6 +573,7 @@ static int ad198x_build_pcms(struct hda_codec *codec)if (spec->multiout.dig_out_nid) { info++; codec->num_pcms++; + codec->spdif_status_reset =1 ; info->name ="AD198x Digital" ; info->pcm_type =HDA_PCM_TYPE_SPDIF ; info->stream[SNDRV_PCM_STREAM_PLAYBACK ] = ad198x_pcm_digital_playback;
sound/pci/hda/patch_cirrus.c +10 -6
@@ -93,8 +93,8 @@ enum {#define CS420X_VENDOR_NID 0x11#define CS_DIG_OUT1_PIN_NID 0x10#define CS_DIG_OUT2_PIN_NID 0x15 -#define CS_DMIC1_PIN_NID 0x12 -#define CS_DMIC2_PIN_NID 0x0e +#define CS_DMIC1_PIN_NID 0x0e +#define CS_DMIC2_PIN_NID 0x12/* coef indices */ #define IDX_SPDIF_STAT 0x0000
@@ -1088,14 +1088,18 @@ static void init_input(struct hda_codec *codec)cs_automic (codec); coef =0x000a ;/* ADC1/2 - Digital and Analog Soft Ramp */ +cs_vendor_coef_set (codec,IDX_ADC_CFG , coef); + + coef =cs_vendor_coef_get (codec,IDX_BEEP_CFG );if (is_active_pin (codec,CS_DMIC2_PIN_NID )) - coef |=0x0500 ;/* DMIC2 2 chan on, GPIO1 off */ + coef |=1 <<4 ;/* DMIC2 2 chan on, GPIO1 off */ if (is_active_pin (codec,CS_DMIC1_PIN_NID )) - coef |=0x1800 ;/* DMIC1 2 chan on, GPIO0 off + coef |=1 <<3 ;/* DMIC1 2 chan on, GPIO0 off * No effect if SPDIF_OUT2 is * selected in IDX_SPDIF_CTL. */ -cs_vendor_coef_set (codec,IDX_ADC_CFG , coef); + +cs_vendor_coef_set (codec,IDX_BEEP_CFG , coef); } }
@@ -1109,7 +1113,7 @@ static const struct hda_verb cs_coef_init_verbs[] = { | 0x0400 /* Disable Coefficient Auto increment */ )},/* Beep */ - {0x11, AC_VERB_SET_COEF_INDEX, IDX_DAC_CFG}, + {0x11, AC_VERB_SET_COEF_INDEX, IDX_BEEP_CFG}, {0x11, AC_VERB_SET_PROC_COEF, 0x0007}, /* Enable Beep thru DAC1/2/3 */ {} /* terminator */
sound/pci/hda/patch_realtek.c +2 -0
@@ -6039,6 +6039,7 @@ static const struct hda_codec_preset snd_hda_preset_realtek[] = { .patch = patch_alc662 }, { .id = 0x10ec0663, .name = "ALC663", .patch = patch_alc662 }, { .id = 0x10ec0665, .name = "ALC665", .patch = patch_alc662 }, + { .id = 0x10ec0668, .name = "ALC668", .patch = patch_alc662 }, { .id = 0x10ec0670, .name = "ALC670", .patch = patch_alc662 }, { .id = 0x10ec0680, .name = "ALC680", .patch = patch_alc680 }, { .id = 0x10ec0880, .name = "ALC880", .patch = patch_alc880 },
@@ -6056,6 +6057,7 @@ static const struct hda_codec_preset snd_hda_preset_realtek[] = { { .id = 0x10ec0889, .name = "ALC889", .patch = patch_alc882 }, { .id = 0x10ec0892, .name = "ALC892", .patch = patch_alc662 }, { .id = 0x10ec0899, .name = "ALC898", .patch = patch_alc882 }, + { .id = 0x10ec0900, .name = "ALC1150", .patch = patch_alc882 }, {}/* terminator */ };
sound/pci/hda/patch_via.c +18 -7
@@ -1856,11 +1856,11 @@ static int via_auto_fill_dac_nids(struct hda_codec *codec) {struct via_spec *spec = codec->spec;const struct auto_pin_cfg *cfg = &spec->autocfg; -int i, dac_num; +int i;hda_nid_t nid; + spec->multiout.num_dacs =0 ; spec->multiout.dac_nids = spec->private_dac_nids; - dac_num =0 ;for (i =0 ; i < cfg->line_outs; i++) {hda_nid_t dac =0 ; nid = cfg->line_out_pins[i];
@@ -1871,16 +1871,13 @@ static int via_auto_fill_dac_nids(struct hda_codec *codec)if (!i &&parse_output_path (codec, nid, dac,1 , &spec->out_mix_path)) dac = spec->out_mix_path.path[0 ]; -if (dac) { - spec->private_dac_nids[i] = dac; - dac_num++; - } +if (dac) + spec->private_dac_nids[spec->multiout.num_dacs++] = dac; }if (!spec->out_path[0 ].depth && spec->out_mix_path.depth) { spec->out_path[0 ] = spec->out_mix_path; spec->out_mix_path.depth =0 ; } - spec->multiout.num_dacs = dac_num;return 0 ; }
@@ -3689,6 +3686,18 @@ static void set_widgets_power_state_vt2002P(struct hda_codec *codec) AC_VERB_SET_POWER_STATE, AC_PWRST_D3); } +/* NIDs 0x24 and 0x33 on VT1802 have connections to non-existing NID 0x3e +* Replace this with mixer NID 0x1c +*/ +static void fix_vt1802_connections (struct hda_codec *codec) +{ +static hda_nid_t conn_24[] = {0x14 ,0x1c }; +static hda_nid_t conn_33[] = {0x1c }; + +snd_hda_override_conn_list (codec,0x24 ,ARRAY_SIZE (conn_24), conn_24); +snd_hda_override_conn_list (codec,0x33 ,ARRAY_SIZE (conn_33), conn_33); +} +/* patch for vt2002P */ static int patch_vt2002P (struct hda_codec *codec) {
@@ -3703,6 +3712,8 @@ static int patch_vt2002P(struct hda_codec *codec) spec->aa_mix_nid =0x21 ;override_mic_boost (codec,0x2b ,0 ,3 ,40 );override_mic_boost (codec,0x29 ,0 ,3 ,40 ); +if (spec->codec_type ==VT1802 ) +fix_vt1802_connections (codec);add_secret_dac_path (codec);/* automatic parse from the BIOS config */
sound/usb/card.c +8 -4
@@ -336,7 +336,7 @@ static int snd_usb_audio_create(struct usb_device *dev, int idx,return -ENOMEM ; } -mutex_init (&chip->shutdown_mutex); +init_rwsem (&chip->shutdown_rwsem); chip->index = idx; chip->dev = dev; chip->card = card;
@@ -556,7 +556,7 @@ static void snd_usb_audio_disconnect(struct usb_device *dev, card = chip->card;mutex_lock (®ister_mutex); -mutex_lock (&chip->shutdown_mutex); +down_write (&chip->shutdown_rwsem); chip->shutdown =1 ; chip->num_interfaces--;if (chip->num_interfaces <=0 ) {
@@ -574,11 +574,11 @@ static void snd_usb_audio_disconnect(struct usb_device *dev,snd_usb_mixer_disconnect (p); } usb_chip[chip->index] =NULL ; -mutex_unlock (&chip->shutdown_mutex); +up_write (&chip->shutdown_rwsem);mutex_unlock (®ister_mutex);snd_card_free_when_closed (card); }else { -mutex_unlock (&chip->shutdown_mutex); +up_write (&chip->shutdown_rwsem);mutex_unlock (®ister_mutex); } }
@@ -610,16 +610,20 @@ int snd_usb_autoresume(struct snd_usb_audio *chip) {int err = -ENODEV ; +down_read (&chip->shutdown_rwsem);if (!chip->shutdown && !chip->probing) err =usb_autopm_get_interface (chip->pm_intf); +up_read (&chip->shutdown_rwsem);return err; }void snd_usb_autosuspend (struct snd_usb_audio *chip) { +down_read (&chip->shutdown_rwsem);if (!chip->shutdown && !chip->probing)usb_autopm_put_interface (chip->pm_intf); +up_read (&chip->shutdown_rwsem); }static int usb_audio_suspend (struct usb_interface *intf,pm_message_t message)
sound/usb/card.h +1 -0
@@ -86,6 +86,7 @@ struct snd_usb_substream {struct snd_urb_ctx syncurb[SYNC_URBS ];/* sync urb table */ char *syncbuf;/* sync buffer for all sync URBs */ dma_addr_t sync_dma;/* DMA address of syncbuf */ +unsigned int speed;/* USB_SPEED_XXX */ u64 formats;/* format bitmasks (all or'ed) */ unsigned int num_formats;/* number of supported audio formats (list) */
sound/usb/endpoint.c +6 -3
@@ -148,8 +148,10 @@ void snd_usb_release_substream_urbs(struct snd_usb_substream *subs, int force)int i;/* stop urbs (to be sure) */ -deactivate_urbs (subs, force,1 ); -wait_clear_urbs (subs); +if (!subs->stream->chip->shutdown) { +deactivate_urbs (subs, force,1 ); +wait_clear_urbs (subs); + }for (i =0 ; i <MAX_URBS ; i++)release_urb_ctx (&subs->dataurb[i]);
@@ -895,7 +897,8 @@ void snd_usb_init_substream(struct snd_usb_stream *as, subs->dev = as->chip->dev; subs->txfr_quirk = as->chip->txfr_quirk; subs->ops = audio_urb_ops[stream]; -if (snd_usb_get_speed (subs->dev) >=USB_SPEED_HIGH ) + subs->speed =snd_usb_get_speed (subs->dev); +if (subs->speed >=USB_SPEED_HIGH ) subs->ops.prepare_sync = prepare_capture_sync_urb_hs;snd_usb_set_pcm_ops (as->pcm, stream);
sound/usb/mixer.c +43 -22
117 lines not on this page · raw message
sound/usb/mixer_quirks.c +33 -4
@@ -186,6 +186,11 @@ static int snd_audigy2nx_led_put(struct snd_kcontrol *kcontrol, struct snd_ctl_eif (value >1 )return -EINVAL ; changed = value != mixer->audigy2nx_leds[index]; +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) { + err = -ENODEV ; + goto out; + }if (mixer->chip->usb_id ==USB_ID (0x041e ,0x3042 )) err = snd_usb_ctl_msg(mixer->chip->dev, usb_sndctrlpipe(mixer->chip->dev, 0), 0x24,
@@ -202,6 +207,8 @@ static int snd_audigy2nx_led_put(struct snd_kcontrol *kcontrol, struct snd_ctl_eusb_sndctrlpipe (mixer->chip->dev,0 ),0x24 ,USB_DIR_OUT |USB_TYPE_VENDOR |USB_RECIP_OTHER , value, index + 2, NULL, 0); + out: +up_read (&mixer->chip->shutdown_rwsem);if (err <0 )return err; mixer->audigy2nx_leds[index] = value;
@@ -295,11 +302,16 @@ static void snd_audigy2nx_proc_read(struct snd_info_entry *entry,for (i =0 ; jacks[i].name; ++i) {snd_iprintf (buffer,"%s: " , jacks[i].name); - err =snd_usb_ctl_msg (mixer->chip->dev, +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) + err =0 ; +else + err =snd_usb_ctl_msg (mixer->chip->dev,usb_rcvctrlpipe (mixer->chip->dev,0 ),UAC_GET_MEM ,USB_DIR_IN |USB_TYPE_CLASS |USB_RECIP_INTERFACE ,0 , jacks[i].unitid <<8 , buf,3 ); +up_read (&mixer->chip->shutdown_rwsem);if (err ==3 && (buf[0 ] ==3 || buf[0 ] ==6 ))snd_iprintf (buffer,"%02x %02x\n" , buf[1 ], buf[2 ]);else
@@ -329,10 +341,15 @@ static int snd_xonar_u1_switch_put(struct snd_kcontrol *kcontrol,else new_status = old_status & ~0x02 ; changed = new_status != old_status; - err =snd_usb_ctl_msg (mixer->chip->dev, +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) + err = -ENODEV ; +else + err =snd_usb_ctl_msg (mixer->chip->dev,usb_sndctrlpipe (mixer->chip->dev,0 ),0x08 ,USB_DIR_OUT |USB_TYPE_VENDOR |USB_RECIP_OTHER ,50 ,0 , &new_status,1 ); +up_read (&mixer->chip->shutdown_rwsem);if (err <0 )return err; mixer->xonar_u1_status = new_status;
@@ -371,11 +388,17 @@ static int snd_nativeinstruments_control_get(struct snd_kcontrol *kcontrol,u8 bRequest = (kcontrol->private_value >>16 ) &0xff ;u16 wIndex = kcontrol->private_value &0xffff ;u8 tmp; +int ret; - int ret = usb_control_msg(dev, usb_rcvctrlpipe(dev, 0), bRequest, +down_read (&mixer->chip->shutdown_rwsem); +if (mixer->chip->shutdown) + ret = -ENODEV ; +else + ret = usb_control_msg(dev, usb_rcvctrlpipe(dev, 0), bRequest, USB_TYPE_VENDOR | USB_RECIP_DEVICE | USB_DIR_IN,
Lines of this file are not shown. View the raw message.
The rest of this diff is not shown. View the raw message.
Part of the diff is not shown here. View the raw message.