4.19.86-stable review
Greg Kroah-Hartman
maintainercover 4.19.86-stable review
This is the start of the stable review cycle for the 4.19.86 release. There are 220 patches in this series, all will be posted as a response to this one. If anyone has any issues with these being applied, please let me know.
Responses should be made by Sun, 24 Nov 2019 09:59:19 +0000. Anything received after that time might be too late.
The whole patch series can be found in one patch at:
https://www.kernel.org/pub/linux/kernel/v4.x/stable-review/patch-4.19.86-rc1.gz
or in the git tree and branch at:
git://git.kernel.org/pub/scm/linux/kernel/git/stable/linux-stable-rc.git linux-4.19.y
and the diffstat can be found below.
thanks,
greg k-h
-------------
Pseudo-Shortlog of commits:
Greg Kroah-Hartman <[email protected]>
Linux 4.19.86-rc1
Reinette Chatre <[email protected]>
x86/resctrl: Fix rdt_find_domain() return value and checks
Takeshi Saito <[email protected]>
mmc: tmio: fix SCC error handling to avoid false positive CRC error
Michael Ellerman <[email protected]>
powerpc/time: Fix clockevent_decrementer initalisation for PR KVM
Alan Mikhak <[email protected]>
tools: PCI: Fix broken pcitest compilation
Enric Balletbo i Serra <[email protected]>
PM / devfreq: Fix static checker warning in try_then_request_governor
Hans de Goede <[email protected]>
ACPI / LPSS: Use acpi_lpss_* instead of acpi_subsys_* functions for hibernate
Yuchung Cheng <[email protected]>
tcp: start receiver buffer autotuning sooner
Roger Quadros <[email protected]>
ARM: dts: omap5: Fix dual-role mode on Super-Speed port
Ido Schimmel <[email protected]>
mlxsw: spectrum_switchdev: Check notification relevance based on upper device
Huibin Hong <[email protected]>
spi: rockchip: initialize dma_slave_config properly
Felix Fietkau <[email protected]>
mac80211: minstrel: fix sampling/reporting of CCK rates in HT mode
Felix Fietkau <[email protected]>
mac80211: minstrel: fix CCK rate group streams value
Felix Fietkau <[email protected]>
mac80211: minstrel: fix using short preamble CCK rates on HT clients
zhong jiang <[email protected]>
misc: cxl: Fix possible null pointer dereference
Pablo Neira Ayuso <[email protected]>
netfilter: nft_compat: do not dump private area
Eric Dumazet <[email protected]>
net: sched: avoid writing on noop_qdisc
Petr Machata <[email protected]>
selftests: forwarding: Have lldpad_app_wait_set() wait for unknown, too
Kun Yi <[email protected]>
hwmon: (npcm-750-pwm-fan) Change initial pwm target to 255
Nicolin Chen <[email protected]>
hwmon: (ina3221) Fix INA3221_CONFIG_MODE macros
Thierry Reding <[email protected]>
hwmon: (pwm-fan) Silence error on probe deferral
Guenter Roeck <[email protected]>
hwmon: (nct6775) Fix names of DIMM temperature sources
Guenter Roeck <[email protected]>
hwmon: (k10temp) Support all Family 15h Model 6xh and Model 7xh processors
Colin Ian King <[email protected]>
scsi: arcmsr: clean up clang warning on extraneous parentheses
Linus Walleij <[email protected]>
pinctrl: gemini: Fix up TVC clock group
Colin Ian King <[email protected]>
orangefs: rate limit the client not running info message
Thomas Gleixner <[email protected]>
x86/mm: Do not warn about PCI BIOS W+X mappings
Timothy E Baldwin <[email protected]>
ARM: 8802/1: Call syscall_trace_exit even when system call skipped
Trent Piepho <[email protected]>
spi: spidev: Fix OF tree warning logic
Linus Walleij <[email protected]>
pinctrl: gemini: Mask and set properly
Hieu Tran Dang <[email protected]>
spi: fsl-lpspi: Prevent FIFO under/overrun by default
Marek Vasut <[email protected]>
gpio: syscon: Fix possible NULL ptr usage
Jesper Dangaard Brouer <[email protected]>
net: fix generic XDP to handle if eth header was mangled
Wenwen Wang <[email protected]>
bpf: btf: Fix a missing check bug
Bjorn Helgaas <[email protected]>
x86/kexec: Correct KEXEC_BACKUP_SRC_END off-by-one error
Zhoujie Wu <[email protected]>
lightnvm: pblk: consider max hw sectors supported for max_write_pgs
Wei Yongjun <[email protected]>
lightnvm: pblk: fix error handling of pblk_lines_init()
Javier González <[email protected]>
lightnvm: do no update csecs and sos on 1.2
Javier González <[email protected]>
lightnvm: pblk: guarantee mw_cunits on read buffer
Hans Holmberg <[email protected]>
lightnvm: pblk: fix write amplificiation calculation
Javier González <[email protected]>
lightnvm: pblk: guarantee emeta on line close
Matias Bjørling <[email protected]>
lightnvm: pblk: fix incorrect min_write_pgs
Matias Bjørling <[email protected]>
lightnvm: pblk: fix rqd.error return value in pblk_blk_erase_sync
Connor McAdams <[email protected]>
ALSA: hda/ca0132 - Fix input effect controls for desktop cards
Vikash Garodia <[email protected]>
media: venus: vdec: fix decoded data size
Colin Ian King <[email protected]>
media: cx231xx: fix potential sign-extension overflow on large shift
Tim Smith <[email protected]>
GFS2: Flush the GFS2 delete workqueue before stopping the kernel threads
Wenwen Wang <[email protected]>
media: isif: fix a NULL pointer dereference bug
He Zhe <[email protected]>
printk: Give error on attempt to set log buffer length to over 2G
Vignesh R <[email protected]>
mfd: ti_am335x_tscadc: Keep ADC interface on if child is wakeup capable
Nathan Chancellor <[email protected]>
backlight: lm3639: Unconditionally call led_classdev_unregister
Borislav Petkov <[email protected]>
proc/vmcore: Fix i386 build error of missing copy_oldmem_page_encrypted()
Vasily Gorbik <[email protected]>
s390/kasan: avoid user access code instrumentation
Vasily Gorbik <[email protected]>
s390/kasan: avoid instrumentation of early C code
Vasily Gorbik <[email protected]>
s390/kasan: avoid vdso instrumentation
Ludovic Barre <[email protected]>
mmc: mmci: expand startbiterr to irqmask and error check
Reinette Chatre <[email protected]>
x86/intel_rdt: CBM overlap should also check for overlap with CDP peer
Reinette Chatre <[email protected]>
x86/intel_rdt: Introduce utility to obtain CDP peer
Yogesh Gaur <[email protected]>
mtd: devices: m25p80: Make sure WRITE_EN is issued before each write
Nathan Chancellor <[email protected]>
mtd: spi-nor: cadence-quadspi: Use proper enum for dma_[un]map_single
Nathan Chancellor <[email protected]>
media: cx18: Don't check for address of video_dev
Sakari Ailus <[email protected]>
media: dw9807-vcm: Fix probe error handling
Rajmohan Mani <[email protected]>
media: dw9714: Fix error handling in probe function
Nathan Chancellor <[email protected]>
platform/x86: mlx-platform: Properly use mlxplat_mlxcpld_msn201x_items
Shenghui Wang <[email protected]>
bcache: recal cached_dev_sectors on detach
Shenghui Wang <[email protected]>
bcache: account size of buckets used in uuid write to ca->meta_sectors_written
Geert Uytterhoeven <[email protected]>
reset: Fix potential use-after-free in __of_reset_control_get()
Randy Dunlap <[email protected]>
fbdev: fix broken menu dependencies
Dan Carpenter <[email protected]>
fbdev: sbuslib: integer overflow in sbusfb_ioctl_helper()
Dan Carpenter <[email protected]>
fbdev: sbuslib: use checked version of put_user()
Sam Ravnborg <[email protected]>
atmel_lcdfb: support native-mode display-timings
Niklas Söderlund <[email protected]>
mmc: renesas_sdhi_internal_dmac: set scatter/gather max segment size
Masaharu Hayakawa <[email protected]>
mmc: tmio: Fix SCC error detection
Fabrizio Castro <[email protected]>
mmc: renesas_sdhi_internal_dmac: Whitelist r8a774a1
Andy Lutomirski <[email protected]>
x86/fsgsbase/64: Fix ptrace() to read the FS/GS base accurately
Björn Töpel <[email protected]>
xsk: proper AF_XDP socket teardown ordering
Sara Sharon <[email protected]>
iwlwifi: mvm: don't send keys when entering D3
Ronald Tschalär <[email protected]>
ACPI / SBS: Fix rare oops when removing modules
Li RongQing <[email protected]>
xfrm: use correct size to initialise sp->ovec
Radu Solea <[email protected]>
crypto: mxs-dcp - Fix AES issues
Radu Solea <[email protected]>
crypto: mxs-dcp - Fix SHA null hashes and output length
Wolfram Sang <[email protected]>
dmaengine: rcar-dmac: set scatter/gather max segment size
Borislav Petkov <[email protected]>
x86/olpc: Fix build error with CONFIG_MFD_CS5535=m
Lianbo Jiang <[email protected]>
kexec: Allocate decrypted control pages for kdump if SME is enabled
Sibi Sankar <[email protected]>
remoteproc: qcom: q6v5: Fix a race condition on fatal crash
Suman Anna <[email protected]>
remoteproc: Check for NULL firmwares in sysfs interface
Davide Caratti <[email protected]>
tc-testing: fix build of eBPF programs
Jian Shen <[email protected]>
net: hns3: Fix for rx vlan id handle to support Rev 0x21 hardware
Laurentiu Tudor <[email protected]>
soc: fsl: bman_portals: defer probe after bman's probe
Julian Sax <[email protected]>
Input: silead - try firmware reload after unsuccessful resume
Martin Kepplinger <[email protected]>
Input: st1232 - set INPUT_PROP_DIRECT property
Wolfram Sang <[email protected]>
i2c: zx2967: use core to detect 'no zero length' quirk
Wolfram Sang <[email protected]>
i2c: tegra: use core to detect 'no zero length' quirk
Wolfram Sang <[email protected]>
i2c: qup: use core to detect 'no zero length' quirk
Wolfram Sang <[email protected]>
i2c: omap: use core to detect 'no zero length' quirk
Bob Peterson <[email protected]>
gfs2: slow the deluge of io error messages
Hans Verkuil <[email protected]>
media: cec-gpio: select correct Signal Free Time
Hugues Fruchet <[email protected]>
media: ov5640: fix framerate update
Rami Rosen <[email protected]>
dmaengine: ioat: fix prototype of ioat_enumerate_channels
Olga Kornievskaia <[email protected]>
NFSv4.x: fix lock recovery during delegation recall
He Zhe <[email protected]>
printk: Correct wrong casting
Florian Fainelli <[email protected]>
i2c: brcmstb: Allow enabling the driver on DSL SoCs
Marek Szyprowski <[email protected]>
clk: samsung: Use clk_hw API for calling clk framework from clk notifiers
Joonyoung Shim <[email protected]>
clk: samsung: exynos5420: Define CLK_SECKEY gate clock only or Exynos5420
Marek Szyprowski <[email protected]>
clk: samsung: Use NOIRQ stage for Exynos5433 clocks suspend/resume
Sergey Matyukevich <[email protected]>
qtnfmac: drop error reports for out-of-bounds key indexes
Sergey Matyukevich <[email protected]>
qtnfmac: inform wireless core about supported extended capabilities
Sergey Matyukevich <[email protected]>
qtnfmac: pass sgi rate info flag to wireless core
Igor Mitsyanko <[email protected]>
qtnfmac: request userspace to do OBSS scanning if FW can not
Chung-Hsien Hsu <[email protected]>
brcmfmac: fix full timeout waiting for action frame on-channel tx
Chung-Hsien Hsu <[email protected]>
brcmfmac: reduce timeout for action frame scan
Borislav Petkov <[email protected]>
cpu/SMT: State SMT is disabled even with nosmt and without "=force"
Ricardo Ribalda Delgado <[email protected]>
mtd: physmap_of: Release resources on error
SolidHal <[email protected]>
usb: dwc2: disable power_down on rockchip devices
Johan Hovold <[email protected]>
USB: serial: cypress_m8: fix interrupt-out transfer length
Cameron Kaiser <[email protected]>
KVM: PPC: Book3S PR: Exiting split hack mode needs to fixup both PC and LR
Vasundhara Volam <[email protected]>
bnxt_en: return proper error when FW returns HWRM_ERR_CODE_RESOURCE_ACCESS_DENIED
Michael Pobega <[email protected]>
ALSA: hda/sigmatel - Disable automute for Elo VuPoint
Jacopo Mondi <[email protected]>
media: i2c: adv748x: Support probing a single output
Niklas Söderlund <[email protected]>
media: rcar-vin: fix redeclaration of symbol
Nathan Chancellor <[email protected]>
media: pxa_camera: Fix check for pdev->dev.of_node
Matthias Reichl <[email protected]>
media: rc: ir-rc6-decoder: enable toggle bit for Kathrein RCU-676 remote
Nathan Chancellor <[email protected]>
qed: Avoid implicit enum conversion in qed_ooo_submit_tx_buffers
Nathan Chancellor <[email protected]>
ata: ep93xx: Use proper enums for directions
Nicholas Piggin <[email protected]>
powerpc/64s/radix: Explicitly flush ERAT with local LPID invalidation
Anton Blanchard <[email protected]>
powerpc/time: Use clockevents_register_device(), fixing an issue with large decrementer
Dan Carpenter <[email protected]>
ASoC: qdsp6: q6asm-dai: checking NULL vs IS_ERR()
Rafael J. Wysocki <[email protected]>
cpuidle: menu: Fix wakeup statistics updates for polling state
Bob Moore <[email protected]>
ACPICA: Never run _REG on system_memory and system_IO
Viresh Kumar <[email protected]>
OPP: Return error on error from dev_pm_opp_get_opp_count()
Jordan Crouse <[email protected]>
msm/gpu/a6xx: Force of_dma_configure to setup DMA for GMU
Arun Kumar Neelakantam <[email protected]>
rpmsg: glink: smem: Support rx peak for size less than 4 bytes
Nathan Chancellor <[email protected]>
IB/mlx4: Avoid implicit enumerated type conversion
Lijun Ou <[email protected]>
RDMA/hns: Limit the size of extend sge of sq
Lijun Ou <[email protected]>
RDMA/hns: Bugfix for CM test
Lijun Ou <[email protected]>
RDMA/hns: Submit bad wr when post send wr exception
Lijun Ou <[email protected]>
RDMA/hns: Bugfix for reserved qp number
Zhu Yanjun <[email protected]>
IB/rxe: avoid srq memory leak
Wei Yongjun <[email protected]>
IB/mthca: Fix error return code in __mthca_init_one()
Radoslaw Tyl <[email protected]>
ixgbe: Fix crash with VFs and flow director on interface flap
Nathan Chancellor <[email protected]>
i40e: Use proper enum in i40e_ndo_set_vf_link_state
Radoslaw Tyl <[email protected]>
ixgbe: Fix ixgbe TX hangs with XDP_TX beyond queue limit
NeilBrown <[email protected]>
md: allow metadata updates while suspending an array - fix
Anirudh Venkataramanan <[email protected]>
ice: Fix forward to queue group logic
Sergei Shtylyov <[email protected]>
clocksource/drivers/sh_cmt: Fix clocksource width for 32-bit machines
Sergei Shtylyov <[email protected]>
clocksource/drivers/sh_cmt: Fixup for 64-bit machines
Gustavo Pimentel <[email protected]>
tools: PCI: Fix compilation warnings
Chen Yu <[email protected]>
PM / hibernate: Check the success of generating md5 digest before hibernation
Nathan Chancellor <[email protected]>
mtd: rawnand: sh_flctl: Use proper enum for flctl_dma_fifo0_transfer
Tudor Ambarus <[email protected]>
ARM: dts: at91: sama5d2_ptc_ek: fix bootloader env offsets
Tudor Ambarus <[email protected]>
ARM: dts: at91: at91sam9x5cm: fix addressable nand flash size
Tudor Ambarus <[email protected]>
ARM: dts: at91: sama5d4_xplained: fix addressable nand flash size
zhong jiang <[email protected]>
powerpc/xive: Move a dereference below a NULL test
Naveen N. Rao <[email protected]>
powerpc/pseries: Fix how we iterate over the DTL entries
Naveen N. Rao <[email protected]>
powerpc/pseries: Fix DTL buffer registration
Nathan Chancellor <[email protected]>
cxgb4: Use proper enum in IEEE_FAUX_SYNC
Nathan Chancellor <[email protected]>
cxgb4: Use proper enum in cxgb4_dcb_handle_fw_update
Dan Carpenter <[email protected]>
mei: samples: fix a signedness bug in amt_host_if_call()
Jon Derrick <[email protected]>
x86/PCI: Apply VMD's AERSID fixup generically
Chuck Lever <[email protected]>
sunrpc: Fix connect metrics
Nishanth Menon <[email protected]>
clk: keystone: Enable TISCI clocks if K3_ARCH
Gabriel Krisman Bertazi <[email protected]>
ext4: fix build error when DX_DEBUG is defined
Keyon Jie <[email protected]>
ALSA: hda: Fix mismatch for register mask and value in ext controller.
Nathan Chancellor <[email protected]>
dmaengine: timb_dma: Use proper enum in td_prep_slave_sg
Nathan Chancellor <[email protected]>
dmaengine: ep93xx: Return proper enum in ep93xx_dma_chan_direction
Sergey Senozhatsky <[email protected]>
printk: CON_PRINTBUFFER console registration is a bit racy
Petr Mladek <[email protected]>
printk: Do not miss new messages when replaying the log
Alexey Kardashevskiy <[email protected]>
KVM: PPC: Inform the userspace about TCE update failures
Guenter Roeck <[email protected]>
watchdog: w83627hf_wdt: Support NCT6796D, NCT6797D, NCT6798D
Romain Izard <[email protected]>
watchdog: sama5d4: fix timeout-sec usage
Wolfram Sang <[email protected]>
watchdog: renesas_wdt: stop when unregistering
Wolfram Sang <[email protected]>
watchdog: core: fix null pointer dereference when releasing cdev
Miquel Raynal <[email protected]>
irqchip/irq-mvebu-icu: Fix wrong private data retrieval
Andrew Zaborowski <[email protected]>
nl80211: Fix a GET_KEY reply attribute
Thinh Nguyen <[email protected]>
usb: dwc3: gadget: Check ENBLSLPM before sending ep command
Jia-Ju Bai <[email protected]>
usb: gadget: udc: fotg210-udc: Fix a sleep-in-atomic-context bug in fotg210_get_status()
Vakul Garg <[email protected]>
selftests/tls: Fix recv(MSG_PEEK) & splice() test cases
Simon Wunderlich <[email protected]>
ath9k: fix reporting calculated new FFT upper max
Vincent Donnefort <[email protected]>
PM / devfreq: stopping the governor before device_unregister()
Matthias Kaehlcke <[email protected]>
PM / devfreq: Fix handling of min/max_freq == 0
Enric Balletbo i Serra <[email protected]>
PM / devfreq: Fix devfreq_add_device() when drivers are built as modules.
Florian Fainelli <[email protected]>
ata: ahci_brcm: Allow using driver or DSL SoCs
Nathan Chancellor <[email protected]>
rtlwifi: btcoex: Use proper enumerated types for Wi-Fi only interface
Ben Greear <[email protected]>
ath10k: fix vdev-start timeout on error
Anshuman Khandual <[email protected]>
arm64/numa: Report correct memblock range for the dummy node
Suzuki K Poulose <[email protected]>
kvm: arm/arm64: Fix stage2_flush_memslot for 4 level page table
Zhen Lei <[email protected]>
iommu/arm-smmu-v3: Fix unexpected CMD_SYNC timeout
Robin Murphy <[email protected]>
iommu/io-pgtable-arm: Fix race handling in split_blk_unmap()
Felix Fietkau <[email protected]>
mt76: fix handling ps-poll frames
Felix Fietkau <[email protected]>
mt76x2: disable WLAN core before probe
Lorenzo Bianconi <[email protected]>
mt76x2: fix tx power configuration for VHT mcs 9
Dennis Dalessandro <[email protected]>
IB/hfi1: Ensure ucast_dlid access doesnt exceed bounds
Michael J. Ruhl <[email protected]>
IB/hfi1: Error path MAD response size is incorrect
Jaegeuk Kim <[email protected]>
f2fs: keep lazytime on remount
Hans de Goede <[email protected]>
ACPI / LPSS: Resume BYT/CHT I2C controllers from resume_noirq
Hans de Goede <[email protected]>
ACPI / LPSS: Make acpi_lpss_find_device() also find PCI devices
Trond Myklebust <[email protected]>
SUNRPC: Fix priority queue fairness
Yuchung Cheng <[email protected]>
tcp: up initial rmem to 128KB and SYN rwin to around 64KB
Chen-Yu Tsai <[email protected]>
ARM: dts: sun8i: h3: bpi-m2-plus: Fix address for external RGMII Ethernet PHY
Philipp Rossak <[email protected]>
ARM: dts: sun8i: h3-h5: ir register size should be the whole memory block
Jaegeuk Kim <[email protected]>
f2fs: return correct errno in f2fs_gc
Huazhong Tan <[email protected]>
net: hns3: Fix loss of coal configuration while doing reset
Yunsheng Lin <[email protected]>
net: hns3: Fix for netdev not up problem when setting mtu
H. Nikolaus Schaller <[email protected]>
ARM: dts: omap5: enable OTG role for DWC3 controller
Vignesh R <[email protected]>
ARM: dts: dra7: Enable workaround for errata i870 in PCIe host mode
YueHaibing <[email protected]>
net: xen-netback: fix return type of ndo_start_xmit function
YueHaibing <[email protected]>
net: ovs: fix return type of ndo_start_xmit function
Wang YanQing <[email protected]>
bpf, x32: Fix bug for BPF_JMP | {BPF_JSGT, BPF_JSLE, BPF_JSLT, BPF_JSGE}Luke Nelson <[email protected]>
bpf, x32: Fix bug with ALU64 {LSH, RSH, ARSH} BPF_K shift by 0
Luke Nelson <[email protected]>
bpf, x32: Fix bug with ALU64 {LSH, RSH, ARSH} BPF_X shift by 0
Wang YanQing <[email protected]>
bpf, x32: Fix bug for BPF_ALU64 | BPF_NEG
Daniel Vetter <[email protected]>
fbdev: Ditch fb_edid_add_monspecs
Pavel Tatashin <[email protected]>
arm64: uaccess: Ensure PAN is re-enabled after unhandled uaccess fault
David Hildenbrand <[email protected]>
mm/memory_hotplug: fix updating the node span
David Hildenbrand <[email protected]>
mm/memory_hotplug: don't access uninitialized memmaps in shrink_pgdat_span()
Matthew Wilcox (Oracle) <[email protected]>
idr: Fix idr_get_next race with idr_remove
Dan Carpenter <[email protected]>
net: cdc_ncm: Signedness bug in cdc_ncm_set_dgram_size()
Greg Kroah-Hartman <[email protected]>
Revert "OPP: Protect dev_list with opp_table lock"
Julia Lawall <[email protected]>
tee: optee: add missing of_node_put after of_device_is_available
Hsin-Yi Wang <[email protected]>
i2c: mediatek: modify threshold passed to i2c_get_dma_safe_msg_buf()
Leilk Liu <[email protected]>
spi: mediatek: use correct mata->xfer_len when in fifo transfer
-------------
Diffstat:
Makefile | 4 +- arch/arm/boot/dts/at91-sama5d2_ptc_ek.dts | 8 +- arch/arm/boot/dts/at91-sama5d4_xplained.dts | 2 +- arch/arm/boot/dts/at91sam9x5cm.dtsi | 2 +- arch/arm/boot/dts/dra7.dtsi | 2 + arch/arm/boot/dts/omap5-board-common.dtsi | 5 + arch/arm/boot/dts/sun8i-h3-bananapi-m2-plus.dts | 2 +- arch/arm/boot/dts/sunxi-h3-h5.dtsi | 2 +- arch/arm/kernel/entry-common.S | 9 +- arch/arm64/lib/clear_user.S | 1 + arch/arm64/lib/copy_from_user.S | 1 + arch/arm64/lib/copy_in_user.S | 1 + arch/arm64/lib/copy_to_user.S | 1 + arch/arm64/mm/numa.c | 2 +- arch/powerpc/kernel/time.c | 19 +- arch/powerpc/kvm/book3s.c | 3 + arch/powerpc/kvm/book3s_64_vio.c | 8 +- arch/powerpc/kvm/book3s_64_vio_hv.c | 6 +- arch/powerpc/mm/tlb-radix.c | 1 + arch/powerpc/platforms/pseries/dtl.c | 4 +- arch/powerpc/sysdev/xive/common.c | 7 +- arch/s390/boot/Makefile | 1 + arch/s390/boot/compressed/Makefile | 1 + arch/s390/kernel/Makefile | 2 + arch/s390/kernel/vdso32/Makefile | 3 +- arch/s390/kernel/vdso64/Makefile | 3 +- arch/s390/lib/Makefile | 4 + arch/x86/Kconfig | 3 +- arch/x86/include/asm/kexec.h | 2 +- arch/x86/kernel/cpu/intel_rdt.c | 2 +- arch/x86/kernel/cpu/intel_rdt_ctrlmondata.c | 2 +- arch/x86/kernel/cpu/intel_rdt_rdtgroup.c | 112 ++++- arch/x86/kernel/ptrace.c | 62 ++- arch/x86/mm/dump_pagetables.c | 35 +- arch/x86/net/bpf_jit_comp32.c | 524 ++++++++------------- arch/x86/pci/fixup.c | 12 +- arch/x86/power/hibernate_64.c | 11 +- drivers/acpi/acpi_lpss.c | 74 ++- drivers/acpi/acpica/acevents.h | 2 + drivers/acpi/acpica/aclocal.h | 2 +- drivers/acpi/acpica/evregion.c | 17 +- drivers/acpi/acpica/evrgnini.c | 6 +- drivers/acpi/acpica/evxfregn.c | 1 - drivers/acpi/osl.c | 1 + drivers/acpi/sbshc.c | 2 + drivers/ata/Kconfig | 3 +- drivers/ata/pata_ep93xx.c | 8 +- drivers/clk/Makefile | 1 + drivers/clk/keystone/Kconfig | 2 +- drivers/clk/samsung/clk-cpu.c | 6 +- drivers/clk/samsung/clk-cpu.h | 2 +- drivers/clk/samsung/clk-exynos5420.c | 3 +- drivers/clk/samsung/clk-exynos5433.c | 2 +- drivers/clocksource/sh_cmt.c | 78 ++- drivers/cpuidle/governors/menu.c | 10 + drivers/cpuidle/poll_state.c | 6 +- drivers/crypto/mxs-dcp.c | 80 +++- drivers/devfreq/devfreq.c | 104 +++- drivers/dma/ioat/init.c | 7 +- drivers/dma/sh/rcar-dmac.c | 3 + drivers/dma/timb_dma.c | 2 +- drivers/gpio/gpio-syscon.c | 2 +- drivers/gpu/drm/msm/adreno/a6xx_gmu.c | 2 +- drivers/hwmon/ina3221.c | 6 +- drivers/hwmon/k10temp.c | 5 +- drivers/hwmon/nct6775.c | 16 +- drivers/hwmon/npcm750-pwm-fan.c | 2 +- drivers/hwmon/pwm-fan.c | 8 +- drivers/i2c/busses/Kconfig | 7 +- drivers/i2c/busses/i2c-mt65xx.c | 8 +- drivers/i2c/busses/i2c-omap.c | 8 +- drivers/i2c/busses/i2c-qup.c | 14 +- drivers/i2c/busses/i2c-tegra.c | 4 +- drivers/i2c/busses/i2c-zx2967.c | 8 +- drivers/infiniband/hw/hfi1/mad.c | 4 +- drivers/infiniband/hw/hns/hns_roce_device.h | 2 + drivers/infiniband/hw/hns/hns_roce_hw_v2.c | 4 + drivers/infiniband/hw/hns/hns_roce_hw_v2.h | 2 + drivers/infiniband/hw/hns/hns_roce_qp.c | 29 +- drivers/infiniband/hw/mthca/mthca_main.c | 3 +- drivers/infiniband/sw/rxe/rxe_srq.c | 10 +- drivers/infiniband/ulp/opa_vnic/opa_vnic_encap.c | 3 +- drivers/input/touchscreen/silead.c | 13 + drivers/input/touchscreen/st1232.c | 1 + drivers/iommu/arm-smmu-v3.c | 8 +- drivers/iommu/io-pgtable-arm.c | 9 +- drivers/irqchip/irq-mvebu-icu.c | 2 +- drivers/lightnvm/pblk-core.c | 32 +- drivers/lightnvm/pblk-init.c | 10 +- drivers/lightnvm/pblk-sysfs.c | 3 +- drivers/md/bcache/super.c | 6 + drivers/md/md.c | 22 +- drivers/media/cec/cec-pin.c | 20 + drivers/media/i2c/adv748x/adv748x-core.c | 25 +- drivers/media/i2c/adv748x/adv748x-csi2.c | 18 +- drivers/media/i2c/adv748x/adv748x.h | 2 + drivers/media/i2c/dw9714.c | 3 +- drivers/media/i2c/dw9807-vcm.c | 3 +- drivers/media/i2c/ov5640.c | 7 +- drivers/media/pci/cx18/cx18-driver.c | 2 +- drivers/media/platform/davinci/isif.c | 3 +- drivers/media/platform/pxa_camera.c | 2 +- drivers/media/platform/qcom/venus/vdec.c | 3 +- drivers/media/platform/rcar-vin/rcar-core.c | 1 - drivers/media/rc/ir-rc6-decoder.c | 9 +- drivers/media/usb/cx231xx/cx231xx-video.c | 2 +- drivers/mfd/ti_am335x_tscadc.c | 13 + drivers/misc/cxl/guest.c | 2 - drivers/mmc/host/mmci.c | 27 +- drivers/mmc/host/mmci.h | 6 +- drivers/mmc/host/renesas_sdhi_internal_dmac.c | 9 + drivers/mmc/host/tmio_mmc_core.c | 5 +- drivers/mtd/devices/m25p80.c | 23 +- drivers/mtd/maps/physmap_of_core.c | 27 +- drivers/mtd/nand/raw/sh_flctl.c | 4 +- drivers/mtd/spi-nor/cadence-quadspi.c | 4 +- drivers/net/ethernet/broadcom/bnxt/bnxt_devlink.c | 6 +- drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.c | 4 +- drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.h | 2 +- drivers/net/ethernet/hisilicon/hns3/hns3_enet.c | 109 ++--- drivers/net/ethernet/hisilicon/hns3/hns3_enet.h | 2 + drivers/net/ethernet/intel/i40e/i40e_virtchnl_pf.c | 2 +- drivers/net/ethernet/intel/ice/ice_switch.c | 14 +- drivers/net/ethernet/intel/ixgbe/ixgbe_main.c | 24 +- .../ethernet/mellanox/mlxsw/spectrum_switchdev.c | 9 +- drivers/net/ethernet/qlogic/qed/qed_ll2.c | 13 +- drivers/net/usb/cdc_ncm.c | 2 +- drivers/net/wireless/ath/ath10k/core.h | 1 + drivers/net/wireless/ath/ath10k/mac.c | 2 +- drivers/net/wireless/ath/ath10k/wmi.c | 19 +- drivers/net/wireless/ath/ath10k/wmi.h | 8 +- drivers/net/wireless/ath/ath9k/common-spectral.c | 2 +- .../net/wireless/broadcom/brcm80211/brcmfmac/p2p.c | 26 +- .../net/wireless/broadcom/brcm80211/brcmfmac/p2p.h | 2 + drivers/net/wireless/intel/iwlwifi/mvm/d3.c | 4 +- drivers/net/wireless/mediatek/mt76/mac80211.c | 6 + .../wireless/mediatek/mt76/mt76x2_init_common.c | 4 + drivers/net/wireless/mediatek/mt76/mt76x2_pci.c | 1 + .../net/wireless/mediatek/mt76/mt76x2_phy_common.c | 4 +- drivers/net/wireless/quantenna/qtnfmac/cfg80211.c | 25 +- drivers/net/wireless/quantenna/qtnfmac/commands.c | 6 +- drivers/net/wireless/quantenna/qtnfmac/core.c | 16 +- drivers/net/wireless/quantenna/qtnfmac/core.h | 1 + drivers/net/wireless/quantenna/qtnfmac/qlink.h | 2 + .../realtek/rtlwifi/btcoexist/halbtcoutsrc.c | 6 +- drivers/net/xen-netback/interface.c | 3 +- drivers/nvme/host/lightnvm.c | 3 + drivers/opp/core.c | 23 +- drivers/opp/cpu.c | 2 - drivers/opp/opp.h | 2 +- drivers/pinctrl/pinctrl-gemini.c | 47 +- drivers/platform/x86/mlx-platform.c | 2 +- drivers/remoteproc/qcom_q6v5.c | 3 +- drivers/remoteproc/remoteproc_sysfs.c | 5 + drivers/reset/core.c | 15 +- drivers/rpmsg/qcom_glink_smem.c | 12 +- drivers/s390/char/Makefile | 1 + drivers/scsi/arcmsr/arcmsr_hba.c | 6 +- drivers/soc/fsl/qbman/bman_portal.c | 10 +- drivers/spi/spi-fsl-lpspi.c | 2 +- drivers/spi/spi-mt65xx.c | 4 +- drivers/spi/spi-rockchip.c | 3 + drivers/spi/spidev.c | 8 +- drivers/tee/optee/core.c | 4 +- drivers/usb/dwc2/params.c | 1 + drivers/usb/dwc3/gadget.c | 29 +- drivers/usb/gadget/udc/fotg210-udc.c | 2 +- drivers/usb/serial/cypress_m8.c | 2 +- drivers/video/backlight/lm3639_bl.c | 6 +- drivers/video/fbdev/Kconfig | 34 +- drivers/video/fbdev/atmel_lcdfb.c | 43 +- drivers/video/fbdev/core/fbmon.c | 96 ---- drivers/video/fbdev/core/modedb.c | 57 --- drivers/video/fbdev/sbuslib.c | 28 +- drivers/watchdog/renesas_wdt.c | 1 + drivers/watchdog/sama5d4_wdt.c | 6 +- drivers/watchdog/w83627hf_wdt.c | 8 +- drivers/watchdog/watchdog_dev.c | 10 +- fs/ext4/namei.c | 2 +- fs/f2fs/gc.c | 2 +- fs/f2fs/super.c | 1 + fs/gfs2/incore.h | 1 + fs/gfs2/log.c | 7 +- fs/gfs2/super.c | 2 +- fs/gfs2/util.c | 13 +- fs/nfs/delegation.c | 6 +- fs/orangefs/orangefs-sysfs.c | 2 +- fs/proc/vmcore.c | 10 + include/linux/cpuidle.h | 1 + include/linux/fb.h | 3 - include/linux/platform_data/dma-ep93xx.h | 2 +- include/linux/sunrpc/sched.h | 2 - include/rdma/ib_verbs.h | 2 +- kernel/bpf/btf.c | 3 + kernel/cpu.c | 1 + kernel/kexec_core.c | 6 + kernel/printk/printk.c | 42 +- lib/idr.c | 15 +- mm/memory_hotplug.c | 77 +-- net/core/dev.c | 14 + net/ipv4/tcp.c | 4 +- net/ipv4/tcp_input.c | 27 +- net/ipv4/tcp_output.c | 25 +- net/mac80211/rc80211_minstrel_ht.c | 20 +- net/netfilter/nft_compat.c | 24 +- net/openvswitch/vport-internal_dev.c | 5 +- net/sched/sch_generic.c | 14 +- net/sunrpc/sched.c | 109 +++-- net/sunrpc/xprt.c | 14 +- net/sunrpc/xprtrdma/transport.c | 6 +- net/sunrpc/xprtsock.c | 10 +- net/wireless/nl80211.c | 2 +- net/xdp/xdp_umem.c | 11 +- net/xdp/xsk.c | 13 +- net/xfrm/xfrm_input.c | 2 +- samples/mei/mei-amt-version.c | 2 +- sound/hda/ext/hdac_ext_controller.c | 22 +- sound/pci/hda/patch_ca0132.c | 8 +- sound/pci/hda/patch_sigmatel.c | 20 + sound/soc/qcom/qdsp6/q6asm-dai.c | 5 +- tools/pci/pcitest.c | 7 +- tools/testing/radix-tree/idr-test.c | 52 ++ tools/testing/selftests/net/forwarding/lib.sh | 2 +- tools/testing/selftests/net/tls.c | 20 +- tools/testing/selftests/tc-testing/bpf/Makefile | 29 ++ tools/testing/selftests/tc-testing/bpf/action.c | 23 + .../selftests/tc-testing/tc-tests/actions/bpf.json | 16 +- tools/testing/selftests/tc-testing/tdc_config.py | 4 +- virt/kvm/arm/mmu.c | 3 +- 229 files changed, 1885 insertions(+), 1392 deletions(-)
Greg Kroah-Hartman
maintainerPATCH 1/220 spi: mediatek: use correct mata->xfer_len when in fifo transfer
From: Leilk Liu <[email protected]>
commit a4d8f64f7267a88d4688f5c216926f5f6cafbae6 upstream.
when xfer_len is greater than 64 bytes and use fifo mode to transfer, the actual length from the third time is mata->xfer_len but not len in mtk_spi_interrupt().
---
 drivers/spi/spi-mt65xx.c |    4 ++--
 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/spi/spi-mt65xx.c +2 -2
@@ -522,11 +522,11 @@ static irqreturn_t mtk_spi_interrupt(int mdata->xfer_len =min (MTK_SPI_MAX_FIFO_SIZE , len);mtk_spi_setup_packet (master); - cnt = len /4 ; + cnt = mdata->xfer_len /4 ;iowrite32_rep (mdata->base +SPI_TX_DATA_REG , trans->tx_buf + mdata->num_xfered, cnt); - remainder = len %4 ; + remainder = mdata->xfer_len %4 ;if (remainder >0 ) { reg_val =0 ; memcpy(®_val,
Greg Kroah-Hartman
maintainerPATCH 2/220 i2c: mediatek: modify threshold passed to i2c_get_dma_safe_msg_buf()
In reply to Greg Kroah-HartmanFrom: Hsin-Yi Wang <[email protected]>
commit bc1a7f75c85e226e82f183d30d75c357f92b6029 upstream.
DMA with zero-length transfers doesn't make sense and this HW doesn't support them at all, so increase the threshold.
---
 drivers/i2c/busses/i2c-mt65xx.c |    8 ++++----
 1 file changed, 4 insertions(+), 4 deletions(-)
drivers/i2c/busses/i2c-mt65xx.c +4 -4
@@ -503,7 +503,7 @@ static int mtk_i2c_do_transfer(struct mtwritel (I2C_DMA_INT_FLAG_NONE , i2c->pdmabase +OFFSET_INT_FLAG );writel (I2C_DMA_CON_RX , i2c->pdmabase +OFFSET_CON ); - dma_rd_buf =i2c_get_dma_safe_msg_buf (msgs,0 ); + dma_rd_buf =i2c_get_dma_safe_msg_buf (msgs,1 );if (!dma_rd_buf)return -ENOMEM ;
@@ -526,7 +526,7 @@ static int mtk_i2c_do_transfer(struct mtwritel (I2C_DMA_INT_FLAG_NONE , i2c->pdmabase +OFFSET_INT_FLAG );writel (I2C_DMA_CON_TX , i2c->pdmabase +OFFSET_CON ); - dma_wr_buf =i2c_get_dma_safe_msg_buf (msgs,0 ); + dma_wr_buf =i2c_get_dma_safe_msg_buf (msgs,1 );if (!dma_wr_buf)return -ENOMEM ;
@@ -549,7 +549,7 @@ static int mtk_i2c_do_transfer(struct mtwritel (I2C_DMA_CLR_FLAG , i2c->pdmabase +OFFSET_INT_FLAG );writel (I2C_DMA_CLR_FLAG , i2c->pdmabase +OFFSET_CON ); - dma_wr_buf =i2c_get_dma_safe_msg_buf (msgs,0 ); + dma_wr_buf =i2c_get_dma_safe_msg_buf (msgs,1 );if (!dma_wr_buf)return -ENOMEM ;
@@ -561,7 +561,7 @@ static int mtk_i2c_do_transfer(struct mtreturn -ENOMEM ; } - dma_rd_buf =i2c_get_dma_safe_msg_buf ((msgs +1 ),0 ); + dma_rd_buf =i2c_get_dma_safe_msg_buf ((msgs +1 ),1 );if (!dma_rd_buf) {dma_unmap_single (i2c->dev, wpaddr, msgs->len,DMA_TO_DEVICE );
Greg Kroah-Hartman
maintainerPATCH 3/220 tee: optee: add missing of_node_put after of_device_is_available
In reply to Greg Kroah-HartmanFrom: Julia Lawall <[email protected]>
commit c7c0d8df0b94a67377555a550b8d66ee2ad2f4ed upstream.
Add an of_node_put when a tested device node is not available.
The semantic patch that fixes this problem is as follows
(http://coccinelle.lip6.fr):
// <smpl>
@@
identifier f;
local idexpression e;
expression x;
@@
e = f(...);
... when != of_node_put(e)
    when != x = e
    when != e = x
    when any
if (<+...of_device_is_available(e)...+>) {
... when != of_node_put(e)
(
return e;
|
+ of_node_put(e);
return ...;
)
}
// </smpl>
---
 drivers/tee/optee/core.c |    4 +++-
 1 file changed, 3 insertions(+), 1 deletion(-)
drivers/tee/optee/core.c +3 -1
@@ -696,8 +696,10 @@ static int __init optee_driver_init(voidreturn -ENODEV ; np =of_find_matching_node (fw_np, optee_match); -if (!np || !of_device_is_available (np)) +if (!np || !of_device_is_available (np)) { +of_node_put (np);return -ENODEV ; + } optee =optee_probe (np);of_node_put (np);
Greg Kroah-Hartman
maintainerPATCH 4/220 Revert "OPP: Protect dev_list with opp_table lock"
In reply to Greg Kroah-HartmanFrom: Greg Kroah-Hartman <[email protected]>
This reverts commit 4c64ce947cfa447993efe005cbaad7ba31a91612 which is commit 3d2556992a878a2210d3be498416aee39e0c32aa upstream.
Turns out to break the build on the odroid machines, so it needs to be reverted.
---
 drivers/opp/core.c |   21 ++-------------------
 drivers/opp/cpu.c  |    2 --
 drivers/opp/opp.h  |    2 +-
 3 files changed, 3 insertions(+), 22 deletions(-)
drivers/opp/core.c +2 -19
@@ -48,14 +48,9 @@ static struct opp_device *_find_opp_dev(static struct opp_table *_find_opp_table_unlocked (struct device *dev) {struct opp_table *opp_table; -bool found;list_for_each_entry (opp_table, &opp_tables, node) { -mutex_lock (&opp_table->lock); - found = !!_find_opp_dev (dev, opp_table); -mutex_unlock (&opp_table->lock); - -if (found) { +if (_find_opp_dev (dev, opp_table)) {_get_opp_table_kref (opp_table);return opp_table;
@@ -771,8 +766,6 @@ struct opp_device *_add_opp_dev(const st/* Initialize opp-dev */ opp_dev->dev = dev; - -mutex_lock (&opp_table->lock);list_add (&opp_dev->node, &opp_table->dev_list);/* Create debugfs entries for the opp_table */
@@ -780,7 +773,6 @@ struct opp_device *_add_opp_dev(const stif (ret)dev_err (dev,"%s: Failed to register opp debugfs (%d)\n" , __func__, ret); -mutex_unlock (&opp_table->lock);return opp_dev; }
@@ -799,7 +791,6 @@ static struct opp_table *_allocate_opp_tif (!opp_table)return NULL ; -mutex_init (&opp_table->lock);INIT_LIST_HEAD (&opp_table->dev_list); opp_dev =_add_opp_dev (dev, opp_table);
@@ -821,6 +812,7 @@ static struct opp_table *_allocate_opp_tBLOCKING_INIT_NOTIFIER_HEAD (&opp_table->head);INIT_LIST_HEAD (&opp_table->opp_list); +mutex_init (&opp_table->lock);kref_init (&opp_table->kref);/* Secure the device table modification */
@@ -862,10 +854,6 @@ static void _opp_table_kref_release(struif (!IS_ERR (opp_table->clk))clk_put (opp_table->clk); -/* -* No need to take opp_table->lock here as we are guaranteed that no -* references to the OPP table are taken at this point. -*/ opp_dev = list_first_entry(&opp_table->dev_list, struct opp_device, node);
@@ -1731,9 +1719,6 @@ void _dev_pm_opp_remove_table(struct opp {struct dev_pm_opp *opp, *tmp; -/* Protect dev_list */ -mutex_lock (&opp_table->lock); -/* Find if opp_table manages a single device */ if (list_is_singular (&opp_table->dev_list)) {/* Free static OPPs */
@@ -1751,8 +1736,6 @@ void _dev_pm_opp_remove_table(struct opp }else {_remove_opp_dev (_find_opp_dev (dev, opp_table), opp_table); } - -mutex_unlock (&opp_table->lock); }void _dev_pm_opp_find_and_remove_table (struct device *dev,bool remove_all)
drivers/opp/cpu.c +0 -2
@@ -222,10 +222,8 @@ int dev_pm_opp_get_sharing_cpus(struct dcpumask_clear (cpumask);if (opp_table->shared_opp ==OPP_TABLE_ACCESS_SHARED ) { -mutex_lock (&opp_table->lock);list_for_each_entry (opp_dev, &opp_table->dev_list, node)cpumask_set_cpu (opp_dev->dev->id, cpumask); -mutex_unlock (&opp_table->lock); }else {cpumask_set_cpu (cpu_dev->id, cpumask); }
drivers/opp/opp.h +1 -1
@@ -126,7 +126,7 @@ enum opp_table_access {* @dev_list: list of devices that share these OPPs * @opp_list: table of opps * @kref: for reference count of the table. -* @lock: mutex protecting the opp_list and dev_list. +* @lock: mutex protecting the opp_list. * @np: struct device_node pointer for opp's DT node. * @clock_latency_ns_max: Max clock latency in nanoseconds. * @shared_opp: OPP is shared between multiple devices.
Greg Kroah-Hartman
maintainerPATCH 5/220 net: cdc_ncm: Signedness bug in cdc_ncm_set_dgram_size()
In reply to Greg Kroah-HartmanFrom: Dan Carpenter <[email protected]>
commit a56dcc6b455830776899ce3686735f1172e12243 upstream.
This code is supposed to test for negative error codes and partial reads, but because sizeof() is size_t (unsigned) type then negative error codes are type promoted to high positive values and the condition doesn't work as expected.
---
 drivers/net/usb/cdc_ncm.c |    2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/net/usb/cdc_ncm.c +1 -1
@@ -579,7 +579,7 @@ static void cdc_ncm_set_dgram_size(struc err =usbnet_read_cmd (dev,USB_CDC_GET_MAX_DATAGRAM_SIZE ,USB_TYPE_CLASS |USB_DIR_IN |USB_RECIP_INTERFACE ,0 , iface_no, &max_datagram_size,sizeof (max_datagram_size)); -if (err <sizeof (max_datagram_size)) { +if (err !=sizeof (max_datagram_size)) {dev_dbg (&dev->intf->dev,"GET_MAX_DATAGRAM_SIZE failed\n" ); goto out; }
Greg Kroah-Hartman
maintainerPATCH 6/220 idr: Fix idr_get_next race with idr_remove
In reply to Greg Kroah-HartmanFrom: Matthew Wilcox (Oracle) <[email protected]>
commit 5c089fd0c73411f2170ab795c9ffc16718c7d007 upstream.
If the entry is deleted from the IDR between the call to radix_tree_iter_find() and rcu_dereference_raw(), idr_get_next() will return NULL, which will end the iteration prematurely. We should instead continue to the next entry in the IDR. This only happens if the iteration is protected by the RCU lock. Most IDR users use a spinlock or semaphore to exclude simultaneous modifications. It was noticed once the PID allocator was converted to use the IDR, as it uses the RCU lock, but there may be other users elsewhere in the kernel.
We can't use the normal pattern of calling radix_tree_deref_retry() (which catches both a retry entry in a leaf node and a node entry in the root) as the IDR supports storing entries which are unaligned, which will trigger an infinite loop if they are encountered. Instead, we have to explicitly check whether the entry is a retry entry.
---
 lib/idr.c                           |   15 +++++++++-
 tools/testing/radix-tree/idr-test.c |   52 ++++++++++++++++++++++++++++++++++++
 2 files changed, 65 insertions(+), 2 deletions(-)
lib/idr.c +13 -2
@@ -231,11 +231,22 @@ void *idr_get_next(struct idr *idr, int {struct radix_tree_iter iter;void __rcu **slot; +void *entry =NULL ;unsigned long base = idr->idr_base;unsigned long id = *nextid; id = (id < base) ?0 : id - base; - slot =radix_tree_iter_find (&idr->idr_rt, &iter, id); +radix_tree_for_each_slot (slot, &idr->idr_rt, &iter, id) { + entry =radix_tree_deref_slot (slot); +if (!entry) +continue ; +if (!radix_tree_deref_retry (entry)) +break ; +if (slot != (void *)&idr->idr_rt.rnode && + entry != (void *)RADIX_TREE_INTERNAL_NODE ) +break ; + slot =radix_tree_iter_retry (&iter); + }if (!slot)return NULL ; id = iter.index + base;
@@ -244,7 +255,7 @@ void *idr_get_next(struct idr *idr, intreturn NULL ; *nextid = id; -return rcu_dereference_raw (*slot); +return entry; }EXPORT_SYMBOL (idr_get_next);
tools/testing/radix-tree/idr-test.c +52 -0
64 lines not on this page · raw message
Greg Kroah-Hartman
maintainerPATCH 8/220 mm/memory_hotplug: fix updating the node span
In reply to Greg Kroah-HartmanFrom: David Hildenbrand <[email protected]>
commit 656d571193262a11c2daa4012e53e4d645bbce56 upstream.
We recently started updating the node span based on the zone span to avoid touching uninitialized memmaps.
Currently, we will always detect the node span to start at 0, meaning a node can easily span too many pages. pgdat_is_empty() will still work correctly if all zones span no pages. We should skip over all zones without spanned pages and properly handle the first detected zone that spans pages.
Unfortunately, in contrast to the zone span (/proc/zoneinfo), the node span cannot easily be inspected and tested. The node span gives no real guarantees when an architecture supports memory hotplug, meaning it can easily contain holes or span pages of different nodes.
The node span is not really used after init on architectures that support memory hotplug.
E.g., we use it in mm/memory_hotplug.c:try_offline_node() and in mm/kmemleak.c:kmemleak_scan(). These users seem to be fine.
---
 mm/memory_hotplug.c |    8 ++++++++
 1 file changed, 8 insertions(+)
mm/memory_hotplug.c +8 -0
@@ -448,6 +448,14 @@ static void update_pgdat_span(struct pgl zone->spanned_pages;/* No need to lock the zones, they can't change. */ +if (!zone->spanned_pages) +continue ; +if (!node_end_pfn) { + node_start_pfn = zone->zone_start_pfn; + node_end_pfn = zone_end_pfn; +continue ; + } +if (zone_end_pfn > node_end_pfn) node_end_pfn = zone_end_pfn;if (zone->zone_start_pfn < node_start_pfn)
Greg Kroah-Hartman
maintainerPATCH 9/220 arm64: uaccess: Ensure PAN is re-enabled after unhandled uaccess fault
In reply to Greg Kroah-HartmanFrom: Pavel Tatashin <[email protected]>
commit 94bb804e1e6f0a9a77acf20d7c70ea141c6c821e upstream.
A number of our uaccess routines ('__arch_clear_user()' and '__arch_copy_{in,from,to}_user()') fail to re-enable PAN if they encounter an unhandled fault whilst accessing userspace.
For CPUs implementing both hardware PAN and UAO, this bug has no effect when both extensions are in use by the kernel.
For CPUs implementing hardware PAN but not UAO, this means that a kernel using hardware PAN may execute portions of code with PAN inadvertently disabled, opening us up to potential security vulnerabilities that rely on userspace access from within the kernel which would usually be prevented by this mechanism. In other words, parts of the kernel run the same way as they would on a CPU without PAN implemented/emulated at all.
For CPUs not implementing hardware PAN and instead relying on software emulation via 'CONFIG_ARM64_SW_TTBR0_PAN=y', the impact is unfortunately much worse. Calling 'schedule()' with software PAN disabled means that the next task will execute in the kernel using the page-table and ASID of the previous process even after 'switch_mm()', since the actual hardware switch is deferred until return to userspace. At this point, or if there is a intermediate call to 'uaccess_enable()', the page-table and ASID of the new process are installed. Sadly, due to the changes introduced by KPTI, this is not an atomic operation and there is a very small window (two instructions) where the CPU is configured with the page-table of the old task and the ASID of the new task; a speculative access in this state is disastrous because it would corrupt the TLB entries for the new task with mappings from the previous address space.
As Pavel explains:
  | I was able to reproduce memory corruption problem on Broadcom's SoC
  | ARMv8-A like this:
  |
  | Enable software perf-events with PERF_SAMPLE_CALLCHAIN so userland's
  | stack is accessed and copied.
  |
  | The test program performed the following on every CPU and forking
  | many processes:
  |
  |	unsigned long *map = mmap(NULL, PAGE_SIZE, PROT_READ|PROT_WRITE,
  |				  MAP_SHARED | MAP_ANONYMOUS, -1, 0);
  |	map[0] = getpid();
  |	sched_yield();
  |	if (map[0] != getpid()) {
  |		fprintf(stderr, "Corruption detected!");
  |	}
  |	munmap(map, PAGE_SIZE);
  |
  | From time to time I was getting map[0] to contain pid for a
  | different process.
Ensure that PAN is re-enabled when returning after an unhandled user fault from our uaccess routines.
---
 arch/arm64/lib/clear_user.S     |    1 +
 arch/arm64/lib/copy_from_user.S |    1 +
 arch/arm64/lib/copy_in_user.S   |    1 +
 arch/arm64/lib/copy_to_user.S   |    1 +
 4 files changed, 4 insertions(+)
arch/arm64/lib/clear_user.S +1 -0
@@ -57,5 +57,6 @@ ENDPROC(__arch_clear_user)
 	.section .fixup,"ax"
 	.align	2
 9:	mov	x0, x2			// return the original size
+	uaccess_disable_not_uao x2, x3
 	ret
 	.previous
arch/arm64/lib/copy_from_user.S +1 -0
@@ -75,5 +75,6 @@ ENDPROC(__arch_copy_from_user)
 	.section .fixup,"ax"
 	.align	2
 9998:	sub	x0, end, dst			// bytes not copied
+	uaccess_disable_not_uao x3, x4
 	ret
 	.previous
arch/arm64/lib/copy_in_user.S +1 -0
@@ -77,5 +77,6 @@ ENDPROC(__arch_copy_in_user)
 	.section .fixup,"ax"
 	.align	2
 9998:	sub	x0, end, dst			// bytes not copied
+	uaccess_disable_not_uao x3, x4
 	ret
 	.previous
arch/arm64/lib/copy_to_user.S +1 -0
@@ -74,5 +74,6 @@ ENDPROC(__arch_copy_to_user)
 	.section .fixup,"ax"
 	.align	2
 9998:	sub	x0, end, dst			// bytes not copied
+	uaccess_disable_not_uao x3, x4
 	ret
 	.previous
Greg Kroah-Hartman
maintainerPATCH 10/220 fbdev: Ditch fb_edid_add_monspecs
In reply to Greg Kroah-HartmanFrom: Daniel Vetter <[email protected]>
commit 3b8720e63f4a1fc6f422a49ecbaa3b59c86d5aaf upstream.
It's dead code ever since
commit 34280340b1dc74c521e636f45cd728f9abf56ee2
Author: Geert Uytterhoeven <[email protected]>
Date:   Fri Dec 4 17:01:43 2015 +0100
fbdev: Remove unused SH-Mobile HDMI driver
Also with this gone we can remove the cea_modes db. This entire thing is massively incomplete anyway, compared to the CEA parsing that drm_edid.c does.
---
 drivers/video/fbdev/core/fbmon.c  |   96 --------------------------------------
 drivers/video/fbdev/core/modedb.c |   57 ----------------------
 include/linux/fb.h                |    3 -
 3 files changed, 156 deletions(-)
drivers/video/fbdev/core/fbmon.c +0 -96
@@ -997,98 +997,6 @@ void fb_edid_to_monspecs(unsigned char *DPRINTK ("========================================\n" ); } -/** -* fb_edid_add_monspecs() - add monitor video modes from E-EDID data -* @edid: 128 byte array with an E-EDID block -* @spacs: monitor specs to be extended -*/ -void fb_edid_add_monspecs (unsigned char *edid,struct fb_monspecs *specs) -{ -unsigned char *block; -struct fb_videomode *m; -int num =0 , i; -u8 svd[64 ], edt[(128 -4 ) /DETAILED_TIMING_DESCRIPTION_SIZE ]; -u8 pos =4 , svd_n =0 ; - -if (!edid) -return ; - -if (!edid_checksum (edid)) -return ; - -if (edid[0 ] !=0x2 || - edid[2 ] <4 || edid[2 ] >128 -DETAILED_TIMING_DESCRIPTION_SIZE ) -return ; - -DPRINTK (" Short Video Descriptors\n" ); - -while (pos < edid[2 ]) { -u8 len = edid[pos] &0x1f , type = (edid[pos] >>5 ) &7 ; -pr_debug ("Data block %u of %u bytes\n" , type, len); -if (type ==2 ) { -for (i = pos; i < pos + len; i++) { -u8 idx = edid[pos + i] &0x7f ; - svd[svd_n++] = idx; -pr_debug ("N%sative mode #%d\n" , - edid[pos + i] &0x80 ?"" :"on-n" , idx); - } - }else if (type ==3 && len >=3 ) { -/* Check Vendor Specific Data Block. For HDMI, -it is always 00-0C-03 for HDMI Licensing, LLC. */ -if (edid[pos +1 ] ==3 && edid[pos +2 ] ==0xc && - edid[pos +3 ] ==0 ) - specs->misc |=FB_MISC_HDMI ; - } - pos += len +1 ; - } - - block = edid + edid[2 ]; - -DPRINTK (" Extended Detailed Timings\n" ); - -for (i =0 ; i < (128 - edid[2 ]) /DETAILED_TIMING_DESCRIPTION_SIZE ; - i++, block +=DETAILED_TIMING_DESCRIPTION_SIZE ) -if (PIXEL_CLOCK !=0 ) - edt[num++] = block - edid; - -/* Yikes, EDID data is totally useless */ -if (!(num + svd_n)) -return ; - - m =kcalloc (specs->modedb_len + num + svd_n, -sizeof (struct fb_videomode ), -GFP_KERNEL ); - -if (!m) -return ; - -memcpy (m, specs->modedb, specs->modedb_len *sizeof (struct fb_videomode )); - -for (i = specs->modedb_len; i < specs->modedb_len + num; i++) { -get_detailed_timing (edid + edt[i - specs->modedb_len], &m[i]); -if (i == specs->modedb_len) - m[i].flag |=FB_MODE_IS_FIRST ; -pr_debug ("Adding %ux%u@%u\n" , m[i].xres, m[i].yres, m[i].refresh); - } - -for (i = specs->modedb_len + num; i < specs->modedb_len + num + svd_n; i++) { -int idx = svd[i - specs->modedb_len - num]; -if (!idx || idx >=ARRAY_SIZE (cea_modes)) { -pr_warn ("Reserved SVD code %d\n" , idx); - }else if (!cea_modes[idx].xres) { -pr_warn ("Unimplemented SVD code %d\n" , idx); - }else { -memcpy (&m[i], cea_modes + idx,sizeof (m[i])); -pr_debug ("Adding SVD #%d: %ux%u@%u\n" , idx, - m[i].xres, m[i].yres, m[i].refresh); - } - } - -kfree (specs->modedb); - specs->modedb = m; - specs->modedb_len = specs->modedb_len + num + svd_n; -} -/* * VESA Generalized Timing Formula (GTF) */
@@ -1498,9 +1406,6 @@ int fb_parse_edid(unsigned char *edid, svoid fb_edid_to_monspecs (unsigned char *edid,struct fb_monspecs *specs) { } -void fb_edid_add_monspecs (unsigned char *edid,struct fb_monspecs *specs) -{ -}void fb_destroy_modedb (struct fb_videomode *modedb) { }
@@ -1608,7 +1513,6 @@ EXPORT_SYMBOL(fb_firmware_edid);EXPORT_SYMBOL (fb_parse_edid);EXPORT_SYMBOL (fb_edid_to_monspecs); -EXPORT_SYMBOL (fb_edid_add_monspecs);EXPORT_SYMBOL (fb_get_mode);EXPORT_SYMBOL (fb_validate_mode);EXPORT_SYMBOL (fb_destroy_modedb);
drivers/video/fbdev/core/modedb.c +0 -57
63 lines not on this page · raw message
include/linux/fb.h +0 -3
@@ -736,8 +736,6 @@ extern int fb_parse_edid(unsigned char *extern const unsigned char *fb_firmware_edid (struct device *device);extern void fb_edid_to_monspecs (unsigned char *edid,struct fb_monspecs *specs); -extern void fb_edid_add_monspecs (unsigned char *edid, -struct fb_monspecs *specs);extern void fb_destroy_modedb (struct fb_videomode *modedb);extern int fb_find_mode_cvt (struct fb_videomode *mode,int margins,int rb);extern unsigned char *fb_ddc_read (struct i2c_adapter *adapter);
@@ -811,7 +809,6 @@ struct dmt_videomode {extern const char *fb_mode_option;extern const struct fb_videomode vesa_modes[]; -extern const struct fb_videomode cea_modes[65 ];extern const struct dmt_videomode dmt_modes[];struct fb_modelist {
Greg Kroah-Hartman
maintainerPATCH 11/220 bpf, x32: Fix bug for BPF_ALU64 | BPF_NEG
In reply to Greg Kroah-HartmanFrom: Wang YanQing <[email protected]>
commit b9aa0b35d878dff9ed19f94101fe353a4de00cc4 upstream.
The current implementation has two errors:
1: The second xor instruction will clear carry flag which
is necessary for following sbb instruction.
2: The select coding for sbb instruction is wrong, the coding
is "sbb dreg_hi,ecx", but what we need is "sbb ecx,dreg_hi".
This patch rewrites the implementation and fixes the errors.
This patch fixes below errors reported by bpf/test_verifier in x32 platform when the jit is enabled:
"
0: (b4) w1 = 4
1: (b4) w2 = 4
2: (1f) r2 -= r1
3: (4f) r2 |= r1
4: (87) r2 = -r2
5: (c7) r2 s>>= 63
6: (5f) r1 &= r2
7: (bf) r0 = r1
8: (95) exit
processed 9 insns (limit 131072), stack depth 0
0: (b4) w1 = 4
1: (b4) w2 = 4
2: (1f) r2 -= r1
3: (4f) r2 |= r1
4: (87) r2 = -r2
5: (c7) r2 s>>= 63
6: (5f) r1 &= r2
7: (bf) r0 = r1
8: (95) exit
processed 9 insns (limit 131072), stack depth 0
......
Summary: 1189 PASSED, 125 SKIPPED, 15 FAILED
"
---
 arch/x86/net/bpf_jit_comp32.c |   19 ++++++-------------
 1 file changed, 6 insertions(+), 13 deletions(-)
arch/x86/net/bpf_jit_comp32.c +6 -13
@@ -698,19 +698,12 @@ static inline void emit_ia32_neg64(const STACK_VAR(dst_hi)); } -/* xor ecx,ecx */ -EMIT2 (0x31 ,add_2reg (0xC0 ,IA32_ECX ,IA32_ECX )); -/* sub dreg_lo,ecx */ -EMIT2 (0x2B ,add_2reg (0xC0 , dreg_lo,IA32_ECX )); -/* mov dreg_lo,ecx */ -EMIT2 (0x89 ,add_2reg (0xC0 , dreg_lo,IA32_ECX )); - -/* xor ecx,ecx */ -EMIT2 (0x31 ,add_2reg (0xC0 ,IA32_ECX ,IA32_ECX )); -/* sbb dreg_hi,ecx */ -EMIT2 (0x19 ,add_2reg (0xC0 , dreg_hi,IA32_ECX )); -/* mov dreg_hi,ecx */ -EMIT2 (0x89 ,add_2reg (0xC0 , dreg_hi,IA32_ECX )); +/* neg dreg_lo */ +EMIT2 (0xF7 ,add_1reg (0xD8 , dreg_lo)); +/* adc dreg_hi,0x0 */ +EMIT3 (0x83 ,add_1reg (0xD0 , dreg_hi),0x00 ); +/* neg dreg_hi */ +EMIT2 (0xF7 ,add_1reg (0xD8 , dreg_hi));if (dstk) {/* mov dword ptr [ebp+off],dreg_lo */
Greg Kroah-Hartman
maintainerPATCH 12/220 bpf, x32: Fix bug with ALU64 {LSH, RSH, ARSH} BPF_X shift by 0
In reply to Greg Kroah-HartmanFrom: Luke Nelson <[email protected]>
commit 68a8357ec15bdce55266e9fba8b8b3b8143fa7d2 upstream.
The current x32 BPF JIT for shift operations is not correct when the shift amount in a register is 0. The expected behavior is a no-op, whereas the current implementation changes bits in the destination register.
The following example demonstrates the bug. The expected result of this program is 1, but the current JITed code returns 2.
r0 = 1
r1 = 1
r2 = 0
r1 <<= r2
if r1 == 1 goto end
r0 = 2
end:
exit
The bug is caused by an incorrect assumption by the JIT that a shift by 32 clear the register. On x32 however, shifts use the lower 5 bits of the source, making a shift by 32 equivalent to a shift by 0.
This patch fixes the bug using double-precision shifts, which also simplifies the code.
---
 arch/x86/net/bpf_jit_comp32.c |  221 ++++--------------------------------------
 1 file changed, 23 insertions(+), 198 deletions(-)
arch/x86/net/bpf_jit_comp32.c +23 -198
@@ -722,9 +722,6 @@ static inline void emit_ia32_lsh_r64(con {u8 *prog = *pprog;int cnt =0 ; -static int jmp_label1 =-1 ; -static int jmp_label2 =-1 ; -static int jmp_label3 =-1 ;u8 dreg_lo = dstk ?IA32_EAX : dst_lo;u8 dreg_hi = dstk ?IA32_EDX : dst_hi;
@@ -743,79 +740,23 @@ static inline void emit_ia32_lsh_r64(con/* mov ecx,src_lo */ EMIT2 (0x8B ,add_2reg (0xC0 , src_lo,IA32_ECX )); -/* cmp ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),32 ); -/* Jumps when >= 32 */ -if (is_imm8 (jmp_label (jmp_label1,2 ))) -EMIT2 (IA32_JAE ,jmp_label (jmp_label1,2 )); -else -EMIT2_off32 (0x0F ,IA32_JAE +0x10 ,jmp_label (jmp_label1,6 )); - -/* < 32 */ -/* shl dreg_hi,cl */ -EMIT2 (0xD3 ,add_1reg (0xE0 , dreg_hi)); -/* mov ebx,dreg_lo */ -EMIT2 (0x8B ,add_2reg (0xC0 , dreg_lo,IA32_EBX )); +/* shld dreg_hi,dreg_lo,cl */ +EMIT3 (0x0F ,0xA5 ,add_2reg (0xC0 , dreg_hi, dreg_lo));/* shl dreg_lo,cl */ EMIT2 (0xD3 ,add_1reg (0xE0 , dreg_lo)); -/* IA32_ECX = -IA32_ECX + 32 */ -/* neg ecx */ -EMIT2 (0xF7 ,add_1reg (0xD8 ,IA32_ECX )); -/* add ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xC0 ,IA32_ECX ),32 ); - -/* shr ebx,cl */ -EMIT2 (0xD3 ,add_1reg (0xE8 ,IA32_EBX )); -/* or dreg_hi,ebx */ -EMIT2 (0x09 ,add_2reg (0xC0 , dreg_hi,IA32_EBX )); - -/* goto out; */ -if (is_imm8 (jmp_label (jmp_label3,2 ))) -EMIT2 (0xEB ,jmp_label (jmp_label3,2 )); -else -EMIT1_off32 (0xE9 ,jmp_label (jmp_label3,5 )); +/* if ecx >= 32, mov dreg_lo into dreg_hi and clear dreg_lo */ -/* >= 32 */ -if (jmp_label1 ==-1 ) - jmp_label1 = cnt; - -/* cmp ecx,64 */ -EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),64 ); -/* Jumps when >= 64 */ -if (is_imm8 (jmp_label (jmp_label2,2 ))) -EMIT2 (IA32_JAE ,jmp_label (jmp_label2,2 )); -else -EMIT2_off32 (0x0F ,IA32_JAE +0x10 ,jmp_label (jmp_label2,6 )); +/* cmp ecx,32 */ +EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),32 ); +/* skip the next two instructions (4 bytes) when < 32 */ +EMIT2 (IA32_JB ,4 ); -/* >= 32 && < 64 */ -/* sub ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xE8 ,IA32_ECX ),32 ); -/* shl dreg_lo,cl */ -EMIT2 (0xD3 ,add_1reg (0xE0 , dreg_lo));/* mov dreg_hi,dreg_lo */ EMIT2 (0x89 ,add_2reg (0xC0 , dreg_hi, dreg_lo)); -/* xor dreg_lo,dreg_lo */ EMIT2 (0x33 ,add_2reg (0xC0 , dreg_lo, dreg_lo)); -/* goto out; */ -if (is_imm8 (jmp_label (jmp_label3,2 ))) -EMIT2 (0xEB ,jmp_label (jmp_label3,2 )); -else -EMIT1_off32 (0xE9 ,jmp_label (jmp_label3,5 )); - -/* >= 64 */ -if (jmp_label2 ==-1 ) - jmp_label2 = cnt; -/* xor dreg_lo,dreg_lo */ -EMIT2 (0x33 ,add_2reg (0xC0 , dreg_lo, dreg_lo)); -/* xor dreg_hi,dreg_hi */ -EMIT2 (0x33 ,add_2reg (0xC0 , dreg_hi, dreg_hi)); - -if (jmp_label3 ==-1 ) - jmp_label3 = cnt; -if (dstk) {/* mov dword ptr [ebp+off],dreg_lo */ EMIT3(0x89, add_2reg(0x40, IA32_EBP, dreg_lo),
@@ -834,9 +775,6 @@ static inline void emit_ia32_arsh_r64(co {u8 *prog = *pprog;int cnt =0 ; -static int jmp_label1 =-1 ; -static int jmp_label2 =-1 ; -static int jmp_label3 =-1 ;u8 dreg_lo = dstk ?IA32_EAX : dst_lo;u8 dreg_hi = dstk ?IA32_EDX : dst_hi;
@@ -855,79 +793,23 @@ static inline void emit_ia32_arsh_r64(co/* mov ecx,src_lo */ EMIT2 (0x8B ,add_2reg (0xC0 , src_lo,IA32_ECX )); -/* cmp ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),32 ); -/* Jumps when >= 32 */ -if (is_imm8 (jmp_label (jmp_label1,2 ))) -EMIT2 (IA32_JAE ,jmp_label (jmp_label1,2 )); -else -EMIT2_off32 (0x0F ,IA32_JAE +0x10 ,jmp_label (jmp_label1,6 )); - -/* < 32 */ -/* lshr dreg_lo,cl */ -EMIT2 (0xD3 ,add_1reg (0xE8 , dreg_lo)); -/* mov ebx,dreg_hi */ -EMIT2 (0x8B ,add_2reg (0xC0 , dreg_hi,IA32_EBX )); -/* ashr dreg_hi,cl */ +/* shrd dreg_lo,dreg_hi,cl */ +EMIT3 (0x0F ,0xAD ,add_2reg (0xC0 , dreg_lo, dreg_hi)); +/* sar dreg_hi,cl */ EMIT2 (0xD3 ,add_1reg (0xF8 , dreg_hi)); -/* IA32_ECX = -IA32_ECX + 32 */ -/* neg ecx */ -EMIT2 (0xF7 ,add_1reg (0xD8 ,IA32_ECX )); -/* add ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xC0 ,IA32_ECX ),32 ); - -/* shl ebx,cl */ -EMIT2 (0xD3 ,add_1reg (0xE0 ,IA32_EBX )); -/* or dreg_lo,ebx */ -EMIT2 (0x09 ,add_2reg (0xC0 , dreg_lo,IA32_EBX )); - -/* goto out; */ -if (is_imm8 (jmp_label (jmp_label3,2 ))) -EMIT2 (0xEB ,jmp_label (jmp_label3,2 )); -else -EMIT1_off32 (0xE9 ,jmp_label (jmp_label3,5 )); +/* if ecx >= 32, mov dreg_hi to dreg_lo and set/clear dreg_hi depending on sign */ -/* >= 32 */ -if (jmp_label1 ==-1 ) - jmp_label1 = cnt; - -/* cmp ecx,64 */ -EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),64 ); -/* Jumps when >= 64 */ -if (is_imm8 (jmp_label (jmp_label2,2 ))) -EMIT2 (IA32_JAE ,jmp_label (jmp_label2,2 )); -else -EMIT2_off32 (0x0F ,IA32_JAE +0x10 ,jmp_label (jmp_label2,6 )); +/* cmp ecx,32 */ +EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),32 ); +/* skip the next two instructions (5 bytes) when < 32 */ +EMIT2 (IA32_JB ,5 ); -/* >= 32 && < 64 */ -/* sub ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xE8 ,IA32_ECX ),32 ); -/* ashr dreg_hi,cl */ -EMIT2 (0xD3 ,add_1reg (0xF8 , dreg_hi));/* mov dreg_lo,dreg_hi */ EMIT2 (0x89 ,add_2reg (0xC0 , dreg_lo, dreg_hi)); - -/* ashr dreg_hi,imm8 */ +/* sar dreg_hi,31 */ EMIT3 (0xC1 ,add_1reg (0xF8 , dreg_hi),31 ); -/* goto out; */ -if (is_imm8 (jmp_label (jmp_label3,2 ))) -EMIT2 (0xEB ,jmp_label (jmp_label3,2 )); -else -EMIT1_off32 (0xE9 ,jmp_label (jmp_label3,5 )); - -/* >= 64 */ -if (jmp_label2 ==-1 ) - jmp_label2 = cnt; -/* ashr dreg_hi,imm8 */ -EMIT3 (0xC1 ,add_1reg (0xF8 , dreg_hi),31 ); -/* mov dreg_lo,dreg_hi */ -EMIT2 (0x89 ,add_2reg (0xC0 , dreg_lo, dreg_hi)); - -if (jmp_label3 ==-1 ) - jmp_label3 = cnt; -if (dstk) {/* mov dword ptr [ebp+off],dreg_lo */ EMIT3(0x89, add_2reg(0x40, IA32_EBP, dreg_lo),
@@ -946,9 +828,6 @@ static inline void emit_ia32_rsh_r64(con {u8 *prog = *pprog;int cnt =0 ; -static int jmp_label1 =-1 ; -static int jmp_label2 =-1 ; -static int jmp_label3 =-1 ;u8 dreg_lo = dstk ?IA32_EAX : dst_lo;u8 dreg_hi = dstk ?IA32_EDX : dst_hi;
@@ -967,77 +846,23 @@ static inline void emit_ia32_rsh_r64(con/* mov ecx,src_lo */ EMIT2 (0x8B ,add_2reg (0xC0 , src_lo,IA32_ECX )); -/* cmp ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),32 ); -/* Jumps when >= 32 */ -if (is_imm8 (jmp_label (jmp_label1,2 ))) -EMIT2 (IA32_JAE ,jmp_label (jmp_label1,2 )); -else -EMIT2_off32 (0x0F ,IA32_JAE +0x10 ,jmp_label (jmp_label1,6 )); - -/* < 32 */ -/* lshr dreg_lo,cl */ -EMIT2 (0xD3 ,add_1reg (0xE8 , dreg_lo)); -/* mov ebx,dreg_hi */ -EMIT2 (0x8B ,add_2reg (0xC0 , dreg_hi,IA32_EBX )); +/* shrd dreg_lo,dreg_hi,cl */ +EMIT3 (0x0F ,0xAD ,add_2reg (0xC0 , dreg_lo, dreg_hi));/* shr dreg_hi,cl */ EMIT2 (0xD3 ,add_1reg (0xE8 , dreg_hi)); -/* IA32_ECX = -IA32_ECX + 32 */ -/* neg ecx */ -EMIT2 (0xF7 ,add_1reg (0xD8 ,IA32_ECX )); -/* add ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xC0 ,IA32_ECX ),32 ); - -/* shl ebx,cl */ -EMIT2 (0xD3 ,add_1reg (0xE0 ,IA32_EBX )); -/* or dreg_lo,ebx */ -EMIT2 (0x09 ,add_2reg (0xC0 , dreg_lo,IA32_EBX )); - -/* goto out; */ -if (is_imm8 (jmp_label (jmp_label3,2 ))) -EMIT2 (0xEB ,jmp_label (jmp_label3,2 )); -else -EMIT1_off32 (0xE9 ,jmp_label (jmp_label3,5 )); +/* if ecx >= 32, mov dreg_hi to dreg_lo and clear dreg_hi */ -/* >= 32 */ -if (jmp_label1 ==-1 ) - jmp_label1 = cnt; -/* cmp ecx,64 */ -EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),64 ); -/* Jumps when >= 64 */ -if (is_imm8 (jmp_label (jmp_label2,2 ))) -EMIT2 (IA32_JAE ,jmp_label (jmp_label2,2 )); -else -EMIT2_off32 (0x0F ,IA32_JAE +0x10 ,jmp_label (jmp_label2,6 )); +/* cmp ecx,32 */ +EMIT3 (0x83 ,add_1reg (0xF8 ,IA32_ECX ),32 ); +/* skip the next two instructions (4 bytes) when < 32 */ +EMIT2 (IA32_JB ,4 ); -/* >= 32 && < 64 */ -/* sub ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xE8 ,IA32_ECX ),32 ); -/* shr dreg_hi,cl */ -EMIT2 (0xD3 ,add_1reg (0xE8 , dreg_hi));/* mov dreg_lo,dreg_hi */ EMIT2 (0x89 ,add_2reg (0xC0 , dreg_lo, dreg_hi));/* xor dreg_hi,dreg_hi */ EMIT2 (0x33 ,add_2reg (0xC0 , dreg_hi, dreg_hi)); -/* goto out; */ -if (is_imm8 (jmp_label (jmp_label3,2 ))) -EMIT2 (0xEB ,jmp_label (jmp_label3,2 )); -else -EMIT1_off32 (0xE9 ,jmp_label (jmp_label3,5 )); - -/* >= 64 */ -if (jmp_label2 ==-1 ) - jmp_label2 = cnt; -/* xor dreg_lo,dreg_lo */ -EMIT2 (0x33 ,add_2reg (0xC0 , dreg_lo, dreg_lo)); -/* xor dreg_hi,dreg_hi */ -EMIT2 (0x33 ,add_2reg (0xC0 , dreg_hi, dreg_hi)); - -if (jmp_label3 ==-1 ) - jmp_label3 = cnt; -if (dstk) {/* mov dword ptr [ebp+off],dreg_lo */ EMIT3(0x89, add_2reg(0x40, IA32_EBP, dreg_lo),
Greg Kroah-Hartman
maintainerPATCH 13/220 bpf, x32: Fix bug with ALU64 {LSH, RSH, ARSH} BPF_K shift by 0
In reply to Greg Kroah-HartmanFrom: Luke Nelson <[email protected]>
commit 6fa632e719eec4d1b1ebf3ddc0b2d667997b057b upstream.
The current x32 BPF JIT does not correctly compile shift operations when the immediate shift amount is 0. The expected behavior is for this to be a no-op.
The following program demonstrates the bug. The expexceted result is 1, but the current JITed code returns 2.
r0 = 1
r1 = 1
r1 <<= 0
if r1 == 1 goto end
r0 = 2
end:
exit
This patch simplifies the code and fixes the bug.
---
 arch/x86/net/bpf_jit_comp32.c |   63 ++++--------------------------------------
 1 file changed, 6 insertions(+), 57 deletions(-)
arch/x86/net/bpf_jit_comp32.c +6 -57
@@ -892,27 +892,10 @@ static inline void emit_ia32_lsh_i64(con }/* Do LSH operation */ if (val <32 ) { -/* shl dreg_hi,imm8 */ -EMIT3 (0xC1 ,add_1reg (0xE0 , dreg_hi), val); -/* mov ebx,dreg_lo */ -EMIT2 (0x8B ,add_2reg (0xC0 , dreg_lo,IA32_EBX )); +/* shld dreg_hi,dreg_lo,imm8 */ +EMIT4 (0x0F ,0xA4 ,add_2reg (0xC0 , dreg_hi, dreg_lo), val);/* shl dreg_lo,imm8 */ EMIT3 (0xC1 ,add_1reg (0xE0 , dreg_lo), val); - -/* IA32_ECX = 32 - val */ -/* mov ecx,val */ -EMIT2 (0xB1 , val); -/* movzx ecx,ecx */ -EMIT3 (0x0F ,0xB6 ,add_2reg (0xC0 ,IA32_ECX ,IA32_ECX )); -/* neg ecx */ -EMIT2 (0xF7 ,add_1reg (0xD8 ,IA32_ECX )); -/* add ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xC0 ,IA32_ECX ),32 ); - -/* shr ebx,cl */ -EMIT2 (0xD3 ,add_1reg (0xE8 ,IA32_EBX )); -/* or dreg_hi,ebx */ -EMIT2 (0x09 ,add_2reg (0xC0 , dreg_hi,IA32_EBX )); }else if (val >=32 && val <64 ) {u32 value = val -32 ;
@@ -958,27 +941,10 @@ static inline void emit_ia32_rsh_i64(con/* Do RSH operation */ if (val <32 ) { -/* shr dreg_lo,imm8 */ -EMIT3 (0xC1 ,add_1reg (0xE8 , dreg_lo), val); -/* mov ebx,dreg_hi */ -EMIT2 (0x8B ,add_2reg (0xC0 , dreg_hi,IA32_EBX )); +/* shrd dreg_lo,dreg_hi,imm8 */ +EMIT4 (0x0F ,0xAC ,add_2reg (0xC0 , dreg_lo, dreg_hi), val);/* shr dreg_hi,imm8 */ EMIT3 (0xC1 ,add_1reg (0xE8 , dreg_hi), val); - -/* IA32_ECX = 32 - val */ -/* mov ecx,val */ -EMIT2 (0xB1 , val); -/* movzx ecx,ecx */ -EMIT3 (0x0F ,0xB6 ,add_2reg (0xC0 ,IA32_ECX ,IA32_ECX )); -/* neg ecx */ -EMIT2 (0xF7 ,add_1reg (0xD8 ,IA32_ECX )); -/* add ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xC0 ,IA32_ECX ),32 ); - -/* shl ebx,cl */ -EMIT2 (0xD3 ,add_1reg (0xE0 ,IA32_EBX )); -/* or dreg_lo,ebx */ -EMIT2 (0x09 ,add_2reg (0xC0 , dreg_lo,IA32_EBX )); }else if (val >=32 && val <64 ) {u32 value = val -32 ;
@@ -1023,27 +989,10 @@ static inline void emit_ia32_arsh_i64(co }/* Do RSH operation */ if (val <32 ) { -/* shr dreg_lo,imm8 */ -EMIT3 (0xC1 ,add_1reg (0xE8 , dreg_lo), val); -/* mov ebx,dreg_hi */ -EMIT2 (0x8B ,add_2reg (0xC0 , dreg_hi,IA32_EBX )); +/* shrd dreg_lo,dreg_hi,imm8 */ +EMIT4 (0x0F ,0xAC ,add_2reg (0xC0 , dreg_lo, dreg_hi), val);/* ashr dreg_hi,imm8 */ EMIT3 (0xC1 ,add_1reg (0xF8 , dreg_hi), val); - -/* IA32_ECX = 32 - val */ -/* mov ecx,val */ -EMIT2 (0xB1 , val); -/* movzx ecx,ecx */ -EMIT3 (0x0F ,0xB6 ,add_2reg (0xC0 ,IA32_ECX ,IA32_ECX )); -/* neg ecx */ -EMIT2 (0xF7 ,add_1reg (0xD8 ,IA32_ECX )); -/* add ecx,32 */ -EMIT3 (0x83 ,add_1reg (0xC0 ,IA32_ECX ),32 ); - -/* shl ebx,cl */ -EMIT2 (0xD3 ,add_1reg (0xE0 ,IA32_EBX )); -/* or dreg_lo,ebx */ -EMIT2 (0x09 ,add_2reg (0xC0 , dreg_lo,IA32_EBX )); }else if (val >=32 && val <64 ) {u32 value = val -32 ;
Greg Kroah-Hartman
maintainerPATCH 14/220 bpf, x32: Fix bug for BPF_JMP | {BPF_JSGT, BPF_JSLE, BPF_JSLT, BPF_JSGE}
In reply to Greg Kroah-HartmanFrom: Wang YanQing <[email protected]>
commit 711aef1bbf88212a21f7103e88f397b47a528805 upstream.
The current method to compare 64-bit numbers for conditional jump is:
1) Compare the high 32-bit first.
2) If the high 32-bit isn't the same, then goto step 4.
3) Compare the low 32-bit.
4) Check the desired condition.
This method is right for unsigned comparison, but it is buggy for signed comparison, because it does signed comparison for low 32-bit too.
There is only one sign bit in 64-bit number, that is the MSB in the 64-bit number, it is wrong to treat low 32-bit as signed number and do the signed comparison for it.
This patch fixes the bug and adds a testcase in selftests/bpf for such bug.
---
 arch/x86/net/bpf_jit_comp32.c |  221 +++++++++++++++++++++++++++++++-----------
 1 file changed, 168 insertions(+), 53 deletions(-)
arch/x86/net/bpf_jit_comp32.c +168 -53
@@ -117,6 +117,8 @@ static bool is_simm32(s64 value)#define IA32_JLE 0x7E#define IA32_JG 0x7F +#define COND_JMP_OPCODE_INVALID (0xFF) +/* * Map eBPF registers to IA32 32bit registers or stack scratch space. *
@@ -1380,6 +1382,75 @@ static inline void emit_push_r64(const u *pprog = prog; } +static u8 get_cond_jmp_opcode (const u8 op,bool is_cmp_lo) +{ +u8 jmp_cond; + +/* Convert BPF opcode to x86 */ +switch (op) { +case BPF_JEQ : + jmp_cond =IA32_JE ; +break ; +case BPF_JSET : +case BPF_JNE : + jmp_cond =IA32_JNE ; +break ; +case BPF_JGT : +/* GT is unsigned '>', JA in x86 */ + jmp_cond =IA32_JA ; +break ; +case BPF_JLT : +/* LT is unsigned '<', JB in x86 */ + jmp_cond =IA32_JB ; +break ; +case BPF_JGE : +/* GE is unsigned '>=', JAE in x86 */ + jmp_cond =IA32_JAE ; +break ; +case BPF_JLE : +/* LE is unsigned '<=', JBE in x86 */ + jmp_cond =IA32_JBE ; +break ; +case BPF_JSGT : +if (!is_cmp_lo) +/* Signed '>', GT in x86 */ + jmp_cond =IA32_JG ; +else +/* GT is unsigned '>', JA in x86 */ + jmp_cond =IA32_JA ; +break ; +case BPF_JSLT : +if (!is_cmp_lo) +/* Signed '<', LT in x86 */ + jmp_cond =IA32_JL ; +else +/* LT is unsigned '<', JB in x86 */ + jmp_cond =IA32_JB ; +break ; +case BPF_JSGE : +if (!is_cmp_lo) +/* Signed '>=', GE in x86 */ + jmp_cond =IA32_JGE ; +else +/* GE is unsigned '>=', JAE in x86 */ + jmp_cond =IA32_JAE ; +break ; +case BPF_JSLE : +if (!is_cmp_lo) +/* Signed '<=', LE in x86 */ + jmp_cond =IA32_JLE ; +else +/* LE is unsigned '<=', JBE in x86 */ + jmp_cond =IA32_JBE ; +break ; +default :/* to silence GCC warning */ + jmp_cond =COND_JMP_OPCODE_INVALID ; +break ; + } + +return jmp_cond; +} +static int do_jit (struct bpf_prog *bpf_prog,int *addrs,u8 *image,int oldproglen,struct jit_context *ctx) {
@@ -1835,11 +1906,7 @@ static int do_jit(struct bpf_prog *bpf_pcase BPF_JMP |BPF_JGT |BPF_X :case BPF_JMP |BPF_JLT |BPF_X :case BPF_JMP |BPF_JGE |BPF_X : -case BPF_JMP |BPF_JLE |BPF_X : -case BPF_JMP |BPF_JSGT |BPF_X : -case BPF_JMP |BPF_JSLE |BPF_X : -case BPF_JMP |BPF_JSLT |BPF_X : -case BPF_JMP |BPF_JSGE |BPF_X : { +case BPF_JMP |BPF_JLE |BPF_X : {u8 dreg_lo = dstk ?IA32_EAX : dst_lo;u8 dreg_hi = dstk ?IA32_EDX : dst_hi;u8 sreg_lo = sstk ?IA32_ECX : src_lo;
@@ -1866,6 +1933,40 @@ static int do_jit(struct bpf_prog *bpf_pEMIT2 (0x39 ,add_2reg (0xC0 , dreg_lo, sreg_lo)); goto emit_cond_jmp; } +case BPF_JMP |BPF_JSGT |BPF_X : +case BPF_JMP |BPF_JSLE |BPF_X : +case BPF_JMP |BPF_JSLT |BPF_X : +case BPF_JMP |BPF_JSGE |BPF_X : { +u8 dreg_lo = dstk ?IA32_EAX : dst_lo; +u8 dreg_hi = dstk ?IA32_EDX : dst_hi; +u8 sreg_lo = sstk ?IA32_ECX : src_lo; +u8 sreg_hi = sstk ?IA32_EBX : src_hi; + +if (dstk) { +EMIT3 (0x8B ,add_2reg (0x40 ,IA32_EBP ,IA32_EAX ), +STACK_VAR (dst_lo)); +EMIT3 (0x8B , +add_2reg (0x40 ,IA32_EBP , +IA32_EDX ), +STACK_VAR (dst_hi)); + } + +if (sstk) { +EMIT3 (0x8B ,add_2reg (0x40 ,IA32_EBP ,IA32_ECX ), +STACK_VAR (src_lo)); +EMIT3 (0x8B , +add_2reg (0x40 ,IA32_EBP , +IA32_EBX ), +STACK_VAR (src_hi)); + } + +/* cmp dreg_hi,sreg_hi */ +EMIT2 (0x39 ,add_2reg (0xC0 , dreg_hi, sreg_hi)); +EMIT2 (IA32_JNE ,10 ); +/* cmp dreg_lo,sreg_lo */ +EMIT2 (0x39 ,add_2reg (0xC0 , dreg_lo, sreg_lo)); + goto emit_cond_jmp_signed; + }case BPF_JMP |BPF_JSET |BPF_X : {u8 dreg_lo = dstk ?IA32_EAX : dst_lo;u8 dreg_hi = dstk ?IA32_EDX : dst_hi;
@@ -1926,11 +2027,7 @@ static int do_jit(struct bpf_prog *bpf_pcase BPF_JMP |BPF_JGT |BPF_K :case BPF_JMP |BPF_JLT |BPF_K :case BPF_JMP |BPF_JGE |BPF_K : -case BPF_JMP |BPF_JLE |BPF_K : -case BPF_JMP |BPF_JSGT |BPF_K : -case BPF_JMP |BPF_JSLE |BPF_K : -case BPF_JMP |BPF_JSLT |BPF_K : -case BPF_JMP |BPF_JSGE |BPF_K : { +case BPF_JMP |BPF_JLE |BPF_K : {u32 hi;u8 dreg_lo = dstk ?IA32_EAX : dst_lo;u8 dreg_hi = dstk ?IA32_EDX : dst_hi;
@@ -1956,50 +2053,9 @@ static int do_jit(struct bpf_prog *bpf_p/* cmp dreg_lo,sreg_lo */ EMIT2 (0x39 ,add_2reg (0xC0 , dreg_lo, sreg_lo)); -emit_cond_jmp:/* Convert BPF opcode to x86 */ -switch (BPF_OP (code)) { -case BPF_JEQ : - jmp_cond =IA32_JE ; -break ; -case BPF_JSET : -case BPF_JNE : - jmp_cond =IA32_JNE ; -break ; -case BPF_JGT : -/* GT is unsigned '>', JA in x86 */ - jmp_cond =IA32_JA ; -break ; -case BPF_JLT : -/* LT is unsigned '<', JB in x86 */ - jmp_cond =IA32_JB ; -break ; -case BPF_JGE : -/* GE is unsigned '>=', JAE in x86 */ - jmp_cond =IA32_JAE ; -break ; -case BPF_JLE : -/* LE is unsigned '<=', JBE in x86 */ - jmp_cond =IA32_JBE ; -break ; -case BPF_JSGT : -/* Signed '>', GT in x86 */ - jmp_cond =IA32_JG ; -break ; -case BPF_JSLT : -/* Signed '<', LT in x86 */ - jmp_cond =IA32_JL ; -break ; -case BPF_JSGE : -/* Signed '>=', GE in x86 */ - jmp_cond =IA32_JGE ; -break ; -case BPF_JSLE : -/* Signed '<=', LE in x86 */ - jmp_cond =IA32_JLE ; -break ; -default :/* to silence GCC warning */ +emit_cond_jmp: jmp_cond =get_cond_jmp_opcode (BPF_OP (code), false); +if (jmp_cond ==COND_JMP_OPCODE_INVALID )return -EFAULT ; - } jmp_offset = addrs[i + insn->off] - addrs[i];if (is_imm8 (jmp_offset)) {EMIT2 (jmp_cond, jmp_offset);
@@ -2009,7 +2065,66 @@ emit_cond_jmp: /* Convert BPF opcode topr_err ("cond_jmp gen bug %llx\n" , jmp_offset);return -EFAULT ; } +break ; + } +case BPF_JMP |BPF_JSGT |BPF_K : +case BPF_JMP |BPF_JSLE |BPF_K : +case BPF_JMP |BPF_JSLT |BPF_K : +case BPF_JMP |BPF_JSGE |BPF_K : { +u8 dreg_lo = dstk ?IA32_EAX : dst_lo; +u8 dreg_hi = dstk ?IA32_EDX : dst_hi; +u8 sreg_lo =IA32_ECX ; +u8 sreg_hi =IA32_EBX ; +u32 hi; + +if (dstk) { +EMIT3 (0x8B ,add_2reg (0x40 ,IA32_EBP ,IA32_EAX ), +STACK_VAR (dst_lo)); +EMIT3 (0x8B , +add_2reg (0x40 ,IA32_EBP , +IA32_EDX ), +STACK_VAR (dst_hi)); + } + +/* mov ecx,imm32 */ +EMIT2_off32 (0xC7 ,add_1reg (0xC0 ,IA32_ECX ), imm32); + hi = imm32 & (1 <<31 ) ? (u32 )~0 :0 ; +/* mov ebx,imm32 */ +EMIT2_off32 (0xC7 ,add_1reg (0xC0 ,IA32_EBX ), hi); +/* cmp dreg_hi,sreg_hi */ +EMIT2 (0x39 ,add_2reg (0xC0 , dreg_hi, sreg_hi)); +EMIT2 (IA32_JNE ,10 ); +/* cmp dreg_lo,sreg_lo */ +EMIT2 (0x39 ,add_2reg (0xC0 , dreg_lo, sreg_lo)); + +/* +* For simplicity of branch offset computation, +* let's use fixed jump coding here. +*/ +emit_cond_jmp_signed:/* Check the condition for low 32-bit comparison */ + jmp_cond =get_cond_jmp_opcode (BPF_OP (code), true); +if (jmp_cond ==COND_JMP_OPCODE_INVALID ) +return -EFAULT ; + jmp_offset = addrs[i + insn->off] - addrs[i] +8 ; +if (is_simm32 (jmp_offset)) { +EMIT2_off32 (0x0F , jmp_cond +0x10 , jmp_offset); + }else { +pr_err ("cond_jmp gen bug %llx\n" , jmp_offset); +return -EFAULT ; + } +EMIT2 (0xEB ,6 ); +/* Check the condition for high 32-bit comparison */ + jmp_cond =get_cond_jmp_opcode (BPF_OP (code), false); +if (jmp_cond ==COND_JMP_OPCODE_INVALID ) +return -EFAULT ; + jmp_offset = addrs[i + insn->off] - addrs[i]; +if (is_simm32 (jmp_offset)) { +EMIT2_off32 (0x0F , jmp_cond +0x10 , jmp_offset); + }else { +pr_err ("cond_jmp gen bug %llx\n" , jmp_offset); +return -EFAULT ; + }break ; }case BPF_JMP |BPF_JA :
Greg Kroah-Hartman
maintainerPATCH 15/220 net: ovs: fix return type of ndo_start_xmit function
In reply to Greg Kroah-HartmanFrom: YueHaibing <[email protected]>
[ Upstream commit eddf11e18dff0e8671e06ce54e64cfc843303ab9 ]
The method ndo_start_xmit() is defined as returning an 'netdev_tx_t', which is a typedef for an enum type, so make sure the implementation in this driver has returns 'netdev_tx_t' value, and change the function return type to netdev_tx_t.
Found by coccinelle.
---
 net/openvswitch/vport-internal_dev.c | 5 +++--
 1 file changed, 3 insertions(+), 2 deletions(-)
net/openvswitch/vport-internal_dev.c +3 -2
@@ -43,7 +43,8 @@ static struct internal_dev *internal_dev_priv(struct net_device *netdev) }/* Called with rcu_read_lock_bh. */ -static int internal_dev_xmit (struct sk_buff *skb,struct net_device *netdev) +static netdev_tx_t +internal_dev_xmit (struct sk_buff *skb,struct net_device *netdev) {int len, err;
@@ -62,7 +63,7 @@ static int internal_dev_xmit(struct sk_buff *skb, struct net_device *netdev) }else { netdev->stats.tx_errors++; } -return 0 ; +return NETDEV_TX_OK ; }static int internal_dev_open (struct net_device *netdev)
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 16/220 net: xen-netback: fix return type of ndo_start_xmit function
In reply to Greg Kroah-HartmanFrom: YueHaibing <[email protected]>
[ Upstream commit a9ca7f17c6d240e269a24cbcd76abf9a940309dd ]
The method ndo_start_xmit() is defined as returning an 'netdev_tx_t', which is a typedef for an enum type, so make sure the implementation in this driver has returns 'netdev_tx_t' value, and change the function return type to netdev_tx_t.
Found by coccinelle.
---
 drivers/net/xen-netback/interface.c | 3 ++-
 1 file changed, 2 insertions(+), 1 deletion(-)
drivers/net/xen-netback/interface.c +2 -1
@@ -173,7 +173,8 @@ static u16 xenvif_select_queue(struct net_device *dev, struct sk_buff *skb, [skb_get_hash_raw (skb) % size]; } -static int xenvif_start_xmit (struct sk_buff *skb,struct net_device *dev) +static netdev_tx_t +xenvif_start_xmit (struct sk_buff *skb,struct net_device *dev) {struct xenvif *vif =netdev_priv (dev);struct xenvif_queue *queue =NULL ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 17/220 ARM: dts: dra7: Enable workaround for errata i870 in PCIe host mode
In reply to Greg Kroah-HartmanFrom: Vignesh R <[email protected]>
[ Upstream commit b830526f304764753fcb8b4a563a94080e982a6c ]
Add ti,syscon-unaligned-access property to PCIe RC nodes to set appropriate bits in CTRL_CORE_SMA_SW_7 register to enable workaround for errata i870.
---
 arch/arm/boot/dts/dra7.dtsi | 2 ++
 1 file changed, 2 insertions(+)
arch/arm/boot/dts/dra7.dtsi +2 -0
@@ -336,6 +336,7 @@ <0 0 0 2 &pcie1_intc 2>, <0 0 0 3 &pcie1_intc 3>, <0 0 0 4 &pcie1_intc 4>; + ti,syscon-unaligned-access = <&scm_conf1 0x14 1>; status = "disabled"; pcie1_intc: interrupt-controller { interrupt-controller;
@@ -387,6 +388,7 @@
 						<0 0 0 2 &pcie2_intc 2>,
 						<0 0 0 3 &pcie2_intc 3>,
 						<0 0 0 4 &pcie2_intc 4>;
+				ti,syscon-unaligned-access = <&scm_conf1 0x14 2>;
 				pcie2_intc: interrupt-controller {
 					interrupt-controller;
 					#address-cells = <0>;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 18/220 ARM: dts: omap5: enable OTG role for DWC3 controller
In reply to Greg Kroah-HartmanFrom: H. Nikolaus Schaller <[email protected]>
[ Upstream commit 656c1a65ab555ee5c7cd0d6aee8ab82ca3c1795f ]
Since SMPS10 and OTG cable detection extcon are described here, and work to enable OTG power when an OTG cable is plugged in, we can define OTG mode in the controller (which is disabled by default in omap5.dtsi).
Tested on OMAP5EVM and Pyra.
---
 arch/arm/boot/dts/omap5-board-common.dtsi | 4 ++++
 1 file changed, 4 insertions(+)
arch/arm/boot/dts/omap5-board-common.dtsi +4 -0
@@ -703,6 +703,10 @@ vbus-supply = <&smps10_out1_reg>; }; +&dwc3 { + dr_mode = "otg"; +}; + &mcspi1 { };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 19/220 net: hns3: Fix for netdev not up problem when setting mtu
In reply to Greg Kroah-HartmanFrom: Yunsheng Lin <[email protected]>
[ Upstream commit 93d8daf460183871a965dae339839d9e35d44309 ]
Currently hns3_nic_change_mtu will try to down the netdev before setting mtu, and it does not up the netdev when the setting fails, which causes netdev not up problem.
This patch fixes it by not returning when the setting fails.
---
 drivers/net/ethernet/hisilicon/hns3/hns3_enet.c | 8 +++-----
 1 file changed, 3 insertions(+), 5 deletions(-)
drivers/net/ethernet/hisilicon/hns3/hns3_enet.c +3 -5
@@ -1447,13 +1447,11 @@ static int hns3_nic_change_mtu(struct net_device *netdev, int new_mtu) } ret = h->ae_algo->ops->set_mtu (h, new_mtu); -if (ret) { +if (ret)netdev_err (netdev,"failed to change MTU in hardware %d\n" , ret); -return ret; - } - - netdev->mtu = new_mtu; +else + netdev->mtu = new_mtu;/* if the netdev was running earlier, bring it up again */ if (if_running &&hns3_nic_net_open (netdev))
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 20/220 net: hns3: Fix loss of coal configuration while doing reset
In reply to Greg Kroah-HartmanFrom: Huazhong Tan <[email protected]>
[ Upstream commit e4fd75022c24eb28cc1034e97e60cecc24f325f3 ]
The user's coal configuration will be lost after reset, so the tx_coal and rx_coal fields are added to the struct hns_nic_priv to save the coal configuration and used to restore the user's configuration after the reset is complete.
---
 .../net/ethernet/hisilicon/hns3/hns3_enet.c   | 71 +++++++++----------
 .../net/ethernet/hisilicon/hns3/hns3_enet.h   |  2 +
 2 files changed, 36 insertions(+), 37 deletions(-)
drivers/net/ethernet/hisilicon/hns3/hns3_enet.c +34 -37
@@ -195,8 +195,6 @@ void hns3_set_vector_coalesce_tx_gl(struct hns3_enet_tqp_vector *tqp_vector,static void hns3_vector_gl_rl_init (struct hns3_enet_tqp_vector *tqp_vector,struct hns3_nic_priv *priv) { -struct hnae3_handle *h = priv->ae_handle; -/* initialize the configuration for interrupt coalescing. * 1. GL (Interrupt Gap Limiter) * 2. RL (Interrupt Rate Limiter)
@@ -209,9 +207,6 @@ static void hns3_vector_gl_rl_init(struct hns3_enet_tqp_vector *tqp_vector, tqp_vector->tx_group.coal.int_gl =HNS3_INT_GL_50K ; tqp_vector->rx_group.coal.int_gl =HNS3_INT_GL_50K ; -/* Default: disable RL */ - h->kinfo.int_rl_setting =0 ; - tqp_vector->int_adapt_down =HNS3_INT_ADAPT_DOWN_START ; tqp_vector->rx_group.coal.flow_level =HNS3_FLOW_LOW ; tqp_vector->tx_group.coal.flow_level =HNS3_FLOW_LOW ;
@@ -3423,6 +3418,31 @@ int hns3_nic_reset_all_ring(struct hnae3_handle *h)return 0 ; } +static void hns3_store_coal (struct hns3_nic_priv *priv) +{ +/* ethtool only support setting and querying one coal +* configuation for now, so save the vector 0' coal +* configuation here in order to restore it. +*/ +memcpy (&priv->tx_coal, &priv->tqp_vector[0 ].tx_group.coal, +sizeof (struct hns3_enet_coalesce )); +memcpy (&priv->rx_coal, &priv->tqp_vector[0 ].rx_group.coal, +sizeof (struct hns3_enet_coalesce )); +} + +static void hns3_restore_coal (struct hns3_nic_priv *priv) +{ +u16 vector_num = priv->vector_num; +int i; + +for (i =0 ; i < vector_num; i++) { +memcpy (&priv->tqp_vector[i].tx_group.coal, &priv->tx_coal, +sizeof (struct hns3_enet_coalesce )); +memcpy (&priv->tqp_vector[i].rx_group.coal, &priv->rx_coal, +sizeof (struct hns3_enet_coalesce )); + } +} +static int hns3_reset_notify_down_enet (struct hnae3_handle *handle) {struct hnae3_knic_private_info *kinfo = &handle->kinfo;
@@ -3469,6 +3489,8 @@ static int hns3_reset_notify_init_enet(struct hnae3_handle *handle)/* Carrier off reporting is important to ethtool even BEFORE open */ netif_carrier_off (netdev); +hns3_restore_coal (priv); + ret =hns3_nic_init_vector_data (priv);if (ret)return ret;
@@ -3496,6 +3518,8 @@ static int hns3_reset_notify_uninit_enet(struct hnae3_handle *handle)return ret; } +hns3_store_coal (priv); + ret =hns3_uninit_all_ring (priv);if (ret)netdev_err (netdev,"uninit ring error\n" );
@@ -3530,24 +3554,7 @@ static int hns3_reset_notify(struct hnae3_handle *handle,return ret; } -static void hns3_restore_coal (struct hns3_nic_priv *priv, -struct hns3_enet_coalesce *tx, -struct hns3_enet_coalesce *rx) -{ -u16 vector_num = priv->vector_num; -int i; - -for (i =0 ; i < vector_num; i++) { -memcpy (&priv->tqp_vector[i].tx_group.coal, tx, -sizeof (struct hns3_enet_coalesce )); -memcpy (&priv->tqp_vector[i].rx_group.coal, rx, -sizeof (struct hns3_enet_coalesce )); - } -} - -static int hns3_modify_tqp_num (struct net_device *netdev,u16 new_tqp_num, -struct hns3_enet_coalesce *tx, -struct hns3_enet_coalesce *rx) +static int hns3_modify_tqp_num (struct net_device *netdev,u16 new_tqp_num) {struct hns3_nic_priv *priv =netdev_priv (netdev);struct hnae3_handle *h =hns3_get_handle (netdev);
@@ -3565,7 +3572,7 @@ static int hns3_modify_tqp_num(struct net_device *netdev, u16 new_tqp_num,if (ret) goto err_alloc_vector; -hns3_restore_coal (priv, tx, rx); +hns3_restore_coal (priv); ret =hns3_nic_init_vector_data (priv);if (ret)
@@ -3597,7 +3604,6 @@ int hns3_set_channels(struct net_device *netdev,struct hns3_nic_priv *priv =netdev_priv (netdev);struct hnae3_handle *h =hns3_get_handle (netdev);struct hnae3_knic_private_info *kinfo = &h->kinfo; -struct hns3_enet_coalesce tx_coal, rx_coal;bool if_running =netif_running (netdev);u32 new_tqp_num = ch->combined_count;u16 org_tqp_num;
@@ -3629,15 +3635,7 @@ int hns3_set_channels(struct net_device *netdev, goto open_netdev; } -/* Changing the tqp num may also change the vector num, -* ethtool only support setting and querying one coal -* configuation for now, so save the vector 0' coal -* configuation here in order to restore it. -*/ -memcpy (&tx_coal, &priv->tqp_vector[0 ].tx_group.coal, -sizeof (struct hns3_enet_coalesce )); -memcpy (&rx_coal, &priv->tqp_vector[0 ].rx_group.coal, -sizeof (struct hns3_enet_coalesce )); +hns3_store_coal (priv);hns3_nic_dealloc_vector_data (priv);
@@ -3645,10 +3643,9 @@ int hns3_set_channels(struct net_device *netdev,hns3_put_ring_config (priv); org_tqp_num = h->kinfo.num_tqps; - ret =hns3_modify_tqp_num (netdev, new_tqp_num, &tx_coal, &rx_coal); + ret =hns3_modify_tqp_num (netdev, new_tqp_num);if (ret) { - ret =hns3_modify_tqp_num (netdev, org_tqp_num, - &tx_coal, &rx_coal); + ret =hns3_modify_tqp_num (netdev, org_tqp_num);if (ret) {/* If revert to old tqp failed, fatal error occurred */ dev_err(&netdev->dev,
drivers/net/ethernet/hisilicon/hns3/hns3_enet.h +2 -0
@@ -541,6 +541,8 @@ struct hns3_nic_priv {/* Vxlan/Geneve information */ struct hns3_udp_tunnel udp_tnl[HNS3_UDP_TNL_MAX ];unsigned long active_vlans[BITS_TO_LONGS (VLAN_N_VID )]; +struct hns3_enet_coalesce tx_coal; +struct hns3_enet_coalesce rx_coal; };union l3_hdr_info {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 21/220 f2fs: return correct errno in f2fs_gc
In reply to Greg Kroah-HartmanFrom: Jaegeuk Kim <[email protected]>
[ Upstream commit 61f7725aa148ee870436a29d3a24d5c00ab7e9af ]
This fixes overriding error number in f2fs_gc.
---
 fs/f2fs/gc.c | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
fs/f2fs/gc.c +1 -1
@@ -1244,7 +1244,7 @@ int f2fs_gc(struct f2fs_sb_info *sbi, bool sync,put_gc_inode (&gc_list); -if (sync) +if (sync && !ret) ret = sec_freed ?0 : -EAGAIN ;return ret; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 22/220 ARM: dts: sun8i: h3-h5: ir register size should be the whole memory block
In reply to Greg Kroah-HartmanFrom: Philipp Rossak <[email protected]>
[ Upstream commit 6c700289a3e84d5d3f2a95cf27732a7f7fce105b ]
The size of the register should be the size of the whole memory block, not just the registers, that are needed.
---
 arch/arm/boot/dts/sunxi-h3-h5.dtsi | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
arch/arm/boot/dts/sunxi-h3-h5.dtsi +1 -1
@@ -816,7 +816,7 @@ clock-names = "apb", "ir"; resets = <&r_ccu RST_APB0_IR>; interrupts = <GIC_SPI 37 IRQ_TYPE_LEVEL_HIGH>; - reg = <0x01f02000 0x40>; + reg = <0x01f02000 0x400>; status = "disabled"; };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 23/220 ARM: dts: sun8i: h3: bpi-m2-plus: Fix address for external RGMII Ethernet PHY
In reply to Greg Kroah-HartmanFrom: Chen-Yu Tsai <[email protected]>
[ Upstream commit db9fd9d13e30fc67737ac9893a82e6b095e85a64 ]
The external RTL8211E RGMII Ethernet PHY is configured via external resistors to use the address 0x1. The 0x0 address is a broadcast address for this family of PHYs, and should not be used explicitly.
---
 arch/arm/boot/dts/sun8i-h3-bananapi-m2-plus.dts | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
arch/arm/boot/dts/sun8i-h3-bananapi-m2-plus.dts +1 -1
@@ -140,7 +140,7 @@ &external_mdio { ext_rgmii_phy: ethernet-phy@1 { compatible = "ethernet-phy-ieee802.3-c22"; - reg = <0>; + reg = <1>; }; };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 24/220 tcp: up initial rmem to 128KB and SYN rwin to around 64KB
In reply to Greg Kroah-HartmanFrom: Yuchung Cheng <[email protected]>
[ Upstream commit a337531b942bd8a03e7052444d7e36972aac2d92 ]
Previously TCP initial receive buffer is ~87KB by default and the initial receive window is ~29KB (20 MSS). This patch changes the two numbers to 128KB and ~64KB (rounding down to the multiples of MSS) respectively. The patch also simplifies the calculations s.t. the two numbers are directly controlled by sysctl tcp_rmem[1]:
1) Initial receiver buffer budget (sk_rcvbuf): while this should be configured via sysctl tcp_rmem[1], previously tcp_fixup_rcvbuf() always override and set a larger size when a new connection establishes.
2) Initial receive window in SYN: previously it is set to 20 packets if MSS <= 1460. The number 20 was based on the initial congestion window of 10: the receiver needs twice amount to avoid being limited by the receive window upon out-of-order delivery in the first window burst. But since this only applies if the receiving MSS <= 1460, connection using large MTU (e.g. to utilize receiver zero-copy) may be limited by the receive window.
With this patch TCP memory configuration is more straight-forward and more properly sized to modern high-speed networks by default. Several popular stacks have been announcing 64KB rwin in SYNs as well.
---
 net/ipv4/tcp.c        |  4 ++--
 net/ipv4/tcp_input.c  | 25 ++-----------------------
 net/ipv4/tcp_output.c | 25 ++++---------------------
 3 files changed, 8 insertions(+), 46 deletions(-)
net/ipv4/tcp.c +2 -2
@@ -3910,8 +3910,8 @@ void __init tcp_init(void) init_net.ipv4.sysctl_tcp_wmem[2 ] =max (64 *1024 , max_wshare); init_net.ipv4.sysctl_tcp_rmem[0 ] =SK_MEM_QUANTUM ; - init_net.ipv4.sysctl_tcp_rmem[1 ] =87380 ; - init_net.ipv4.sysctl_tcp_rmem[2 ] =max (87380 , max_rshare); + init_net.ipv4.sysctl_tcp_rmem[1 ] =131072 ; + init_net.ipv4.sysctl_tcp_rmem[2 ] =max (131072 , max_rshare);pr_info ("Hash tables configured (established %u bind %u)\n" , tcp_hashinfo.ehash_mask +1 , tcp_hashinfo.bhash_size);
net/ipv4/tcp_input.c +2 -23
@@ -426,26 +426,7 @@ static void tcp_grow_window(struct sock *sk, const struct sk_buff *skb) } } -/* 3. Tuning rcvbuf, when connection enters established state. */ -static void tcp_fixup_rcvbuf (struct sock *sk) -{ -u32 mss =tcp_sk (sk)->advmss; -int rcvmem; - - rcvmem =2 *SKB_TRUESIZE (mss +MAX_TCP_HEADER ) * -tcp_default_init_rwnd (mss); - -/* Dynamic Right Sizing (DRS) has 2 to 3 RTT latency -* Allow enough cushion so that sender is not limited by our window -*/ -if (sock_net (sk)->ipv4.sysctl_tcp_moderate_rcvbuf) - rcvmem <<=2 ; - -if (sk->sk_rcvbuf < rcvmem) - sk->sk_rcvbuf =min (rcvmem,sock_net (sk)->ipv4.sysctl_tcp_rmem[2 ]); -} - -/* 4. Try to fixup all. It is made immediately after connection enters +/* 3. Try to fixup all. It is made immediately after connection enters * established state. */ void tcp_init_buffer_space (struct sock *sk)
@@ -454,8 +435,6 @@ void tcp_init_buffer_space(struct sock *sk)struct tcp_sock *tp =tcp_sk (sk);int maxwin; -if (!(sk->sk_userlocks &SOCK_RCVBUF_LOCK )) -tcp_fixup_rcvbuf (sk);if (!(sk->sk_userlocks &SOCK_SNDBUF_LOCK ))tcp_sndbuf_expand (sk);
@@ -485,7 +464,7 @@ void tcp_init_buffer_space(struct sock *sk) tp->snd_cwnd_stamp = tcp_jiffies32; } -/* 5. Recalculate window clamp after socket hit its memory bounds. */ +/* 4. Recalculate window clamp after socket hit its memory bounds. */ static void tcp_clamp_window (struct sock *sk) {struct tcp_sock *tp =tcp_sk (sk);
net/ipv4/tcp_output.c +4 -21
@@ -179,21 +179,6 @@ static inline void tcp_event_ack_sent(struct sock *sk, unsigned int pkts,inet_csk_clear_xmit_timer (sk,ICSK_TIME_DACK ); } - -u32 tcp_default_init_rwnd (u32 mss) -{ -/* Initial receive window should be twice of TCP_INIT_CWND to -* enable proper sending of new unsent data during fast recovery -* (RFC 3517, Section 4, NextSeg() rule (2)). Further place a -* limit when mss is larger than 1460. -*/ -u32 init_rwnd =TCP_INIT_CWND *2 ; - -if (mss >1460 ) - init_rwnd =max ((1460 * init_rwnd) / mss,2U ); -return init_rwnd; -} -/* Determine a window scaling and initial window to offer. * Based on the assumption that the given amount of space * will be offered. Store the results in the tp structure.
@@ -228,7 +213,10 @@ void tcp_select_initial_window(const struct sock *sk, int __space, __u32 mss,if (sock_net (sk)->ipv4.sysctl_tcp_workaround_signed_windows) (*rcv_wnd) =min (space,MAX_TCP_WINDOW );else - (*rcv_wnd) = space; + (*rcv_wnd) =min_t (u32, space,U16_MAX ); + +if (init_rcv_wnd) + *rcv_wnd =min (*rcv_wnd, init_rcv_wnd * mss); (*rcv_wscale) =0 ;if (wscale_ok) {
@@ -241,11 +229,6 @@ void tcp_select_initial_window(const struct sock *sk, int __space, __u32 mss, (*rcv_wscale)++; } } - -if (!init_rcv_wnd)/* Use default unless specified otherwise */ - init_rcv_wnd =tcp_default_init_rwnd (mss); - *rcv_wnd =min (*rcv_wnd, init_rcv_wnd * mss); -/* Set the clamp no higher than max representable value */ (*window_clamp) =min_t (__u32,U16_MAX << (*rcv_wscale), *window_clamp); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 25/220 SUNRPC: Fix priority queue fairness
In reply to Greg Kroah-HartmanFrom: Trond Myklebust <[email protected]>
[ Upstream commit f42f7c283078ce3c1e8368b140e270755b1ae313 ]
Fix up the priority queue to not batch by owner, but by queue, so that we allow '1 << priority' elements to be dequeued before switching to the next priority queue.
The owner field is still used to wake up requests in round robin order by owner to avoid single processes hogging the RPC layer by loading the queues.
---
 include/linux/sunrpc/sched.h |   2 -
 net/sunrpc/sched.c           | 109 +++++++++++++++++------------------
 2 files changed, 54 insertions(+), 57 deletions(-)
include/linux/sunrpc/sched.h +0 -2
@@ -188,7 +188,6 @@ struct rpc_timer {struct rpc_wait_queue {spinlock_t lock;struct list_head tasks[RPC_NR_PRIORITY ];/* task queue for each priority level */ -pid_t owner;/* process id of last task serviced */ unsigned char maxpriority;/* maximum priority (0 if queue is not a priority queue) */ unsigned char priority;/* current priority */ unsigned char nr;/* # tasks remaining for cookie */
@@ -204,7 +203,6 @@ struct rpc_wait_queue {* from a single cookie. The aim is to improve * performance of NFS operations such as read/write. */ -#define RPC_BATCH_COUNT 16#define RPC_IS_PRIORITY (q) ((q)->maxpriority > 0)/*
net/sunrpc/sched.c +54 -55
170 lines not on this page · raw message
Signature · 1 line
2.20.1
Re: [PATCH 4.19 025/220] SUNRPC: Fix priority queue fairness
Quoted 12 lines · Greg Kroah-Hartman
From: Trond Myklebust <[email protected]>
[ Upstream commit
f42f7c283078ce3c1e8368b140e270755b1ae313]Fix up the priority queue to not batch by owner, but by queue, so that we allow '1 << priority' elements to be dequeued before switching to the next priority queue.
The owner field is still used to wake up requests in round robin order by owner to avoid single processes hogging the RPC layer by loading the queues.
Quoted 3 lines
 include/linux/sunrpc/sched.h |   2 -
 net/sunrpc/sched.c           | 109 +++++++++++++++++------------------
 2 files changed, 54 insertions(+), 57 deletions(-)
While this might improve things, it is not fixing a serious bug.
Plus, it is over limit for stable.
Best regards,
Pavel
Signature · 2 lines
(english) http://www.livejournal.com/~pavelmachek
(cesky, pictures) http://atrey.karlin.mff.cuni.cz/~pavel/picture/horses/blog.html
Greg Kroah-Hartman
maintainerPATCH 26/220 ACPI / LPSS: Make acpi_lpss_find_device() also find PCI devices
In reply to Greg Kroah-HartmanFrom: Hans de Goede <[email protected]>
[ Upstream commit 1e30124ac60abc41d74793900f8b4034f29bcb3d ]
On some Cherry Trail systems the GPU ACPI fwnode has power-resources which point to the PMIC, which is connected over one of the LPSS I2C controllers.
To get the suspend/resume ordering correct for this we need to be able to add device-links between the GPU and the I2c controller. The GPU is a PCI device, so this requires acpi_lpss_find_device() to also work on PCI devs.
---
 drivers/acpi/acpi_lpss.c | 9 ++++++++-
 1 file changed, 8 insertions(+), 1 deletion(-)
drivers/acpi/acpi_lpss.c +8 -1
@@ -16,6 +16,7 @@#include <linux/err.h> #include <linux/io.h> #include <linux/mutex.h> +#include <linux/pci.h> #include <linux/platform_device.h> #include <linux/platform_data/clk-lpss.h> #include <linux/platform_data/x86/pmc_atom.h>
@@ -512,12 +513,18 @@ static int match_hid_uid(struct device *dev, void *data)static struct device *acpi_lpss_find_device (const char *hid,const char *uid) { +struct device *dev; +struct hid_uid data = { .hid = hid, .uid = uid, }; -return bus_find_device (&platform_bus_type,NULL , &data, match_hid_uid); + dev =bus_find_device (&platform_bus_type,NULL , &data, match_hid_uid); +if (dev) +return dev; + +return bus_find_device (&pci_bus_type,NULL , &data, match_hid_uid); }static bool acpi_lpss_dep (struct acpi_device *adev,acpi_handle handle)
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 27/220 ACPI / LPSS: Resume BYT/CHT I2C controllers from resume_noirq
In reply to Greg Kroah-HartmanFrom: Hans de Goede <[email protected]>
[ Upstream commit 48402cee6889fb3fce58e95fea1471626286dc63 ]
On some Cherry Trail systems the GPU ACPI fwnode has power-resources which point to the PMIC, which is connected over a LPSS I2C controller.
We add a device-link to make sure that the I2C controller is resumed before the GPU is. But the pci-core changes the power-state of PCI devices from D3 to D0 at noirq time (to restore the PCI config registers) and before this commit we were bringing up the I2C controllers from a resume_early handler which runs later. More specifically the pm-core will first run all resume_noirq handlers in order and then all resume_early handlers.
So we must not only make sure that the handlers are run in the right order, but also that the resume of the I2C controller is done at noirq time.
The behavior before this commit, resuming the I2C controller from a resume_early handler leads to the following errors:
i2c_designware 808622C1:06: controller timed out
ACPI Error: AE_ERROR, Returned by Handler for [UserDefinedRegion] ACPI Error: Method parse/execution failed \_SB.P18W._ON, AE_ERROR video LNXVIDEO:00: Failed to change power state to D0
This commit changes the acpi_lpss.c code to resume the BYT/CHT I2C controllers at resume_noirq time fixing this.
---
 drivers/acpi/acpi_lpss.c | 61 +++++++++++++++++++++++++++++++++++++---
 1 file changed, 57 insertions(+), 4 deletions(-)
drivers/acpi/acpi_lpss.c +57 -4
@@ -84,6 +84,7 @@ struct lpss_device_desc {size_t prv_size_override;struct property_entry *properties;void (*setup)(struct lpss_private_data *pdata); +bool resume_from_noirq; };static const struct lpss_device_desc lpss_dma_desc = {
@@ -293,12 +294,14 @@ static const struct lpss_device_desc byt_i2c_dev_desc = { .flags = LPSS_CLK | LPSS_SAVE_CTX, .prv_offset = 0x800, .setup = byt_i2c_setup, + .resume_from_noirq = true, };static const struct lpss_device_desc bsw_i2c_dev_desc = { .flags =LPSS_CLK |LPSS_SAVE_CTX |LPSS_NO_D3_DELAY , .prv_offset =0x800 , .setup = byt_i2c_setup, + .resume_from_noirq = true, };static const struct lpss_device_desc bsw_spi_dev_desc = {
@@ -1031,7 +1034,7 @@ static int acpi_lpss_resume(struct device *dev) }#ifdef CONFIG_PM_SLEEP -static int acpi_lpss_suspend_late (struct device *dev) +static int acpi_lpss_do_suspend_late (struct device *dev) {int ret;
@@ -1042,12 +1045,62 @@ static int acpi_lpss_suspend_late(struct device *dev)return ret ? ret :acpi_lpss_suspend (dev,device_may_wakeup (dev)); } -static int acpi_lpss_resume_early (struct device *dev) +static int acpi_lpss_suspend_late (struct device *dev) +{ +struct lpss_private_data *pdata =acpi_driver_data (ACPI_COMPANION (dev)); + +if (pdata->dev_desc->resume_from_noirq) +return 0 ; + +return acpi_lpss_do_suspend_late (dev); +} + +static int acpi_lpss_suspend_noirq (struct device *dev) +{ +struct lpss_private_data *pdata =acpi_driver_data (ACPI_COMPANION (dev)); +int ret; + +if (pdata->dev_desc->resume_from_noirq) { + ret =acpi_lpss_do_suspend_late (dev); +if (ret) +return ret; + } + +return acpi_subsys_suspend_noirq (dev); +} + +static int acpi_lpss_do_resume_early (struct device *dev) {int ret =acpi_lpss_resume (dev);return ret ? ret :pm_generic_resume_early (dev); } + +static int acpi_lpss_resume_early (struct device *dev) +{ +struct lpss_private_data *pdata =acpi_driver_data (ACPI_COMPANION (dev)); + +if (pdata->dev_desc->resume_from_noirq) +return 0 ; + +return acpi_lpss_do_resume_early (dev); +} + +static int acpi_lpss_resume_noirq (struct device *dev) +{ +struct lpss_private_data *pdata =acpi_driver_data (ACPI_COMPANION (dev)); +int ret; + + ret =acpi_subsys_resume_noirq (dev); +if (ret) +return ret; + +if (!dev_pm_may_skip_resume (dev) && pdata->dev_desc->resume_from_noirq) + ret =acpi_lpss_do_resume_early (dev); + +return ret; +} +#endif /* CONFIG_PM_SLEEP */ static int acpi_lpss_runtime_suspend (struct device *dev)
@@ -1077,8 +1130,8 @@ static struct dev_pm_domain acpi_lpss_pm_domain = {
 		.complete = acpi_subsys_complete,
 		.suspend = acpi_subsys_suspend,
 		.suspend_late = acpi_lpss_suspend_late,
-		.suspend_noirq = acpi_subsys_suspend_noirq,
-		.resume_noirq = acpi_subsys_resume_noirq,
+		.suspend_noirq = acpi_lpss_suspend_noirq,
+		.resume_noirq = acpi_lpss_resume_noirq,
 		.resume_early = acpi_lpss_resume_early,
 		.freeze = acpi_subsys_freeze,
 		.freeze_late = acpi_subsys_freeze_late,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 28/220 f2fs: keep lazytime on remount
In reply to Greg Kroah-HartmanFrom: Jaegeuk Kim <[email protected]>
[ Upstream commit 095680f24f2673d860fd1d3d2f54f40f330b4c63 ]
This patch fixes losing lazytime when remounting f2fs.
---
 fs/f2fs/super.c | 1 +
 1 file changed, 1 insertion(+)
fs/f2fs/super.c +1 -0
@@ -1556,6 +1556,7 @@ static int f2fs_remount(struct super_block *sb, int *flags, char *data) (test_opt (sbi,POSIX_ACL ) ?SB_POSIXACL :0 );limit_reserve_root (sbi); + *flags = (*flags & ~SB_LAZYTIME ) | (sb->s_flags &SB_LAZYTIME );return 0 ; restore_gc:if (need_restart_gc) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 29/220 IB/hfi1: Error path MAD response size is incorrect
In reply to Greg Kroah-HartmanFrom: Michael J. Ruhl <[email protected]>
[ Upstream commit 935c84ac649a147e1aad2c48ee5c5a1a9176b2d0 ]
If a MAD packet has incorrect header information, the logic uses the reply path to report the error. The reply path expects *resp_len to be set prior to return. Unfortunately, *resp_len is set to 0 for this path. This causes an incorrect response packet.
Fix by ensuring that the *resp_len is defaulted to the incoming packet size (wc->bytes_len - sizeof(GRH)).
---
 drivers/infiniband/hw/hfi1/mad.c | 4 ++--
 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/infiniband/hw/hfi1/mad.c +2 -2
@@ -1,5 +1,5 @@/* -* Copyright(c) 2015-2017 Intel Corporation. +* Copyright(c) 2015-2018 Intel Corporation. * * This file is provided under a dual BSD/GPLv2 license. When using or * redistributing this file, you may do so under either license.
@@ -4829,7 +4829,7 @@ static int hfi1_process_opa_mad(struct ib_device *ibdev, int mad_flags,int ret;int pkey_idx;int local_mad =0 ; -u32 resp_len =0 ; +u32 resp_len = in_wc->byte_len -sizeof (*in_grh);struct hfi1_ibport *ibp =to_iport (ibdev, port); pkey_idx =hfi1_lookup_pkey_idx (ibp,LIM_MGMT_P_KEY );
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 30/220 IB/hfi1: Ensure ucast_dlid access doesnt exceed bounds
In reply to Greg Kroah-HartmanFrom: Dennis Dalessandro <[email protected]>
[ Upstream commit 3144533bf667c8e53bb20656b78295960073e57b ]
The dlid assignment made by looking into the u_ucast_dlid array does not do an explicit check for the size of the array. The code path to arrive at def_port, the index value is long and complicated so its best to just have an explicit check here.
---
 drivers/infiniband/ulp/opa_vnic/opa_vnic_encap.c | 3 ++-
 1 file changed, 2 insertions(+), 1 deletion(-)
drivers/infiniband/ulp/opa_vnic/opa_vnic_encap.c +2 -1
@@ -351,7 +351,8 @@ static uint32_t opa_vnic_get_dlid(struct opa_vnic_adapter *adapter,if (unlikely (!dlid))v_warn ("Null dlid in MAC address\n" ); }else if (def_port !=OPA_VNIC_INVALID_PORT ) { - dlid = info->vesw.u_ucast_dlid[def_port]; +if (def_port <OPA_VESW_MAX_NUM_DEF_PORT ) + dlid = info->vesw.u_ucast_dlid[def_port]; } }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 31/220 mt76x2: fix tx power configuration for VHT mcs 9
In reply to Greg Kroah-HartmanFrom: Lorenzo Bianconi <[email protected]>
[ Upstream commit 60b6645ef1a9239a02c70adeae136298395d145a ]
Fix tx power configuration for VHT 1SS/STBC mcs 9 since in MT_TX_PWR_CFG_{8,9} mcs 8,9 bits are GENMASK(21,16) and GENMASK(29,24) while GENMASK(15,6) are marked as reserved
---
 drivers/net/wireless/mediatek/mt76/mt76x2_phy_common.c | 4 ++--
 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/net/wireless/mediatek/mt76/mt76x2_phy_common.c +2 -2
@@ -232,9 +232,9 @@ void mt76x2_phy_set_txpower(struct mt76x2_dev *dev)mt76_wr (dev,MT_TX_PWR_CFG_7 ,mt76x2_tx_power_mask (t.ofdm[6 ], t.vht[8 ], t.ht[6 ], t.vht[8 ]));mt76_wr (dev,MT_TX_PWR_CFG_8 , -mt76x2_tx_power_mask (t.ht[14 ], t.vht[8 ], t.vht[8 ],0 )); +mt76x2_tx_power_mask (t.ht[14 ],0 , t.vht[8 ], t.vht[8 ]));mt76_wr (dev,MT_TX_PWR_CFG_9 , -mt76x2_tx_power_mask (t.ht[6 ], t.vht[8 ], t.vht[8 ],0 )); +mt76x2_tx_power_mask (t.ht[6 ],0 , t.vht[8 ], t.vht[8 ])); }EXPORT_SYMBOL_GPL (mt76x2_phy_set_txpower);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 32/220 mt76x2: disable WLAN core before probe
In reply to Greg Kroah-HartmanFrom: Felix Fietkau <[email protected]>
[ Upstream commit 62e04f8a31fcc375c978b7f83b4229a10c3e746d ]
If the WLAN core is still active during initialization, it might cause the MCU or DMA to hang. This can happen during soft reboot, so disable the core + clock early to avoid this issue.
---
 drivers/net/wireless/mediatek/mt76/mt76x2_init_common.c | 4 ++++
 drivers/net/wireless/mediatek/mt76/mt76x2_pci.c         | 1 +
 2 files changed, 5 insertions(+)
drivers/net/wireless/mediatek/mt76/mt76x2_init_common.c +4 -0
@@ -72,6 +72,9 @@ void mt76x2_reset_wlan(struct mt76x2_dev *dev, bool enable) {u32 val; +if (!enable) + goto out; + val =mt76_rr (dev,MT_WLAN_FUN_CTRL ); val &= ~MT_WLAN_FUN_CTRL_FRC_WL_ANT_SEL ;
@@ -87,6 +90,7 @@ void mt76x2_reset_wlan(struct mt76x2_dev *dev, bool enable)mt76_wr (dev,MT_WLAN_FUN_CTRL , val);udelay (20 ); +out:mt76x2_set_wlan_state (dev, enable); }EXPORT_SYMBOL_GPL (mt76x2_reset_wlan);
drivers/net/wireless/mediatek/mt76/mt76x2_pci.c +1 -0
@@ -53,6 +53,7 @@ mt76pci_probe(struct pci_dev *pdev, const struct pci_device_id *id)return -ENOMEM ;mt76_mmio_init (&dev->mt76,pcim_iomap_table (pdev)[0 ]); +mt76x2_reset_wlan (dev, false); dev->mt76.rev =mt76_rr (dev,MT_ASIC_VERSION );dev_info (dev->mt76.dev,"ASIC revision: %08x\n" , dev->mt76.rev);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 33/220 mt76: fix handling ps-poll frames
In reply to Greg Kroah-HartmanFrom: Felix Fietkau <[email protected]>
[ Upstream commit 36d910960fae3f9e74bedf3e0ef39ee26bdaa51f ]
Hardware station lookup for pspoll frames can fail, which makes the driver ignore ps-poll frames. Fix the resulting powersave issues by looking up the station for pspoll frames in software
---
 drivers/net/wireless/mediatek/mt76/mac80211.c | 6 ++++++
 1 file changed, 6 insertions(+)
drivers/net/wireless/mediatek/mt76/mac80211.c +6 -0
@@ -548,6 +548,12 @@ mt76_check_ps(struct mt76_dev *dev, struct sk_buff *skb)struct mt76_wcid *wcid = status->wcid;bool ps; +if (ieee80211_is_pspoll (hdr->frame_control) && !wcid) { + sta =ieee80211_find_sta_by_ifaddr (dev->hw, hdr->addr2,NULL ); +if (sta) + wcid = status->wcid = (struct mt76_wcid *) sta->drv_priv; + } +if (!wcid || !wcid->sta)return ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 34/220 iommu/io-pgtable-arm: Fix race handling in split_blk_unmap()
In reply to Greg Kroah-HartmanFrom: Robin Murphy <[email protected]>
[ Upstream commit 85c7a0f1ef624ef58173ef52ea77780257bdfe04 ]
In removing the pagetable-wide lock, we gained the possibility of the vanishingly unlikely case where we have a race between two concurrent unmappers splitting the same block entry. The logic to handle this is fairly straightforward - whoever loses the race frees their partial next-level table and instead dereferences the winner's newly-installed entry in order to fall back to a regular unmap, which intentionally echoes the pre-existing case of recursively splitting a 1GB block down to 4KB pages by installing a full table of 2MB blocks first.
Unfortunately, the chump who implemented that logic failed to update the condition check for that fallback, meaning that if said race occurs at the last level (where the loser's unmap_idx is valid) then the unmap won't actually happen. Fix that to properly account for both the race and recursive cases.
---
 drivers/iommu/io-pgtable-arm.c | 9 ++++-----
 1 file changed, 4 insertions(+), 5 deletions(-)
drivers/iommu/io-pgtable-arm.c +4 -5
@@ -574,13 +574,12 @@ static size_t arm_lpae_split_blk_unmap(struct arm_lpae_io_pgtable *data,return 0 ; tablep =iopte_deref (pte, data); + }else if (unmap_idx >=0 ) { +io_pgtable_tlb_add_flush (&data->iop, iova, size, size, true); +return size; } -if (unmap_idx <0 ) -return __arm_lpae_unmap (data, iova, size, lvl, tablep); - -io_pgtable_tlb_add_flush (&data->iop, iova, size, size, true); -return size; +return __arm_lpae_unmap (data, iova, size, lvl, tablep); } static size_t __arm_lpae_unmap(struct arm_lpae_io_pgtable *data,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 35/220 iommu/arm-smmu-v3: Fix unexpected CMD_SYNC timeout
In reply to Greg Kroah-HartmanFrom: Zhen Lei <[email protected]>
[ Upstream commit 0f02477d16980938a84aba8688a4e3a303306116 ]
The condition break condition of:
(int)(VAL - sync_idx) >= 0
in the __arm_smmu_sync_poll_msi() polling loop requires that sync_idx must be increased monotonically according to the sequence of the CMDs in the cmdq.
However, since the msidata is populated using atomic_inc_return_relaxed() before taking the command-queue spinlock, then the following scenario can occur:
CPU0 CPU1
msidata=0
msidata=1
insert cmd1
insert cmd0
smmu execute cmd1
smmu execute cmd0
			poll timeout, because msidata=1 is overridden by
			cmd0, that means VAL=0, sync_idx=1.
This is not a functional problem, since the caller will eventually either timeout or exit due to another CMD_SYNC, however it's clearly not what the code is supposed to be doing. Fix it, by incrementing the sequence count with the command-queue lock held, allowing us to drop the atomic operations altogether.
---
 drivers/iommu/arm-smmu-v3.c | 8 +++-----
 1 file changed, 3 insertions(+), 5 deletions(-)
drivers/iommu/arm-smmu-v3.c +3 -5
@@ -567,7 +567,7 @@ struct arm_smmu_device {int gerr_irq;int combined_irq; -atomic_t sync_nr; +u32 sync_nr;unsigned long ias;/* IPA */ unsigned long oas;/* PA */
@@ -964,14 +964,13 @@ static int __arm_smmu_cmdq_issue_sync_msi(struct arm_smmu_device *smmu)struct arm_smmu_cmdq_ent ent = { .opcode =CMDQ_OP_CMD_SYNC , .sync = { - .msidata =atomic_inc_return_relaxed (&smmu->sync_nr), .msiaddr =virt_to_phys (&smmu->sync_count), }, }; -arm_smmu_cmdq_build_cmd (cmd, &ent); -spin_lock_irqsave (&smmu->cmdq.lock, flags); + ent.sync.msidata = ++smmu->sync_nr; +arm_smmu_cmdq_build_cmd (cmd, &ent);arm_smmu_cmdq_insert_cmd (smmu, cmd);spin_unlock_irqrestore (&smmu->cmdq.lock, flags);
@@ -2196,7 +2195,6 @@ static int arm_smmu_init_structures(struct arm_smmu_device *smmu) {int ret; -atomic_set (&smmu->sync_nr,0 ); ret =arm_smmu_init_queues (smmu);if (ret)return ret;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 36/220 kvm: arm/arm64: Fix stage2_flush_memslot for 4 level page table
In reply to Greg Kroah-HartmanFrom: Suzuki K Poulose <[email protected]>
[ Upstream commit d2db7773ba864df6b4e19643dfc54838550d8049 ]
So far we have only supported 3 level page table with fixed IPA of 40bits, where PUD is folded. With 4 level page tables, we need to check if the PUD entry is valid or not. Fix stage2_flush_memslot() to do this check, before walking down the table.
---
 virt/kvm/arm/mmu.c | 3 ++-
 1 file changed, 2 insertions(+), 1 deletion(-)
virt/kvm/arm/mmu.c +2 -1
@@ -412,7 +412,8 @@ static void stage2_flush_memslot(struct kvm *kvm, pgd = kvm->arch.pgd +stage2_pgd_index (addr);do { next =stage2_pgd_addr_end (addr, end); -stage2_flush_puds (kvm, pgd, addr, next); +if (!stage2_pgd_none (*pgd)) +stage2_flush_puds (kvm, pgd, addr, next); }while (pgd++, addr = next, addr != end); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 37/220 arm64/numa: Report correct memblock range for the dummy node
In reply to Greg Kroah-HartmanFrom: Anshuman Khandual <[email protected]>
[ Upstream commit 77cfe950901e5c13aca2df6437a05f39dd9a929b ]
The dummy node ID is marked into all memory ranges on the system. So the dummy node really extends the entire memblock.memory. Hence report correct extent information for the dummy node using memblock range helper functions instead of the range [0LLU, PFN_PHYS(max_pfn) - 1)].
---
 arch/arm64/mm/numa.c | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
arch/arm64/mm/numa.c +1 -1
@@ -432,7 +432,7 @@ static int __init dummy_numa_init(void)if (numa_off)pr_info ("NUMA disabled\n" );/* Forced off on command line. */ pr_info ("Faking a node at [mem %#018Lx-%#018Lx]\n" , -0LLU ,PFN_PHYS (max_pfn) -1 ); +memblock_start_of_DRAM (),memblock_end_of_DRAM () -1 );for_each_memblock (memory, mblk) { ret =numa_add_memblk (0 , mblk->base, mblk->base + mblk->size);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 38/220 ath10k: fix vdev-start timeout on error
In reply to Greg Kroah-HartmanFrom: Ben Greear <[email protected]>
[ Upstream commit 833fd34d743c728afe6d127ef7bee67e7d9199a8 ]
The vdev-start-response message should cause the completion to fire, even in the error case. Otherwise, the user still gets no useful information and everything is blocked until the timeout period.
Add some warning text to print out the invalid status code to aid debugging, and propagate failure code.
---
 drivers/net/wireless/ath/ath10k/core.h |  1 +
 drivers/net/wireless/ath/ath10k/mac.c  |  2 +-
 drivers/net/wireless/ath/ath10k/wmi.c  | 19 ++++++++++++++++---
 drivers/net/wireless/ath/ath10k/wmi.h  |  8 +++++++-
 4 files changed, 25 insertions(+), 5 deletions(-)
drivers/net/wireless/ath/ath10k/core.h +1 -0
@@ -1003,6 +1003,7 @@ struct ath10k {struct completion install_key_done; +int last_wmi_vdev_start_status;struct completion vdev_setup_done;struct workqueue_struct *workqueue;
drivers/net/wireless/ath/ath10k/mac.c +1 -1
@@ -968,7 +968,7 @@ static inline int ath10k_vdev_setup_sync(struct ath10k *ar)if (time_left ==0 )return -ETIMEDOUT ; -return 0 ; +return ar->last_wmi_vdev_start_status; }static int ath10k_monitor_vdev_start (struct ath10k *ar,int vdev_id)
drivers/net/wireless/ath/ath10k/wmi.c +16 -3
@@ -3248,18 +3248,31 @@ void ath10k_wmi_event_vdev_start_resp(struct ath10k *ar, struct sk_buff *skb) {struct wmi_vdev_start_ev_arg arg = {};int ret; +u32 status;ath10k_dbg (ar,ATH10K_DBG_WMI ,"WMI_VDEV_START_RESP_EVENTID\n" ); + ar->last_wmi_vdev_start_status =0 ; + ret =ath10k_wmi_pull_vdev_start (ar, skb, &arg);if (ret) {ath10k_warn (ar,"failed to parse vdev start event: %d\n" , ret); -return ; + ar->last_wmi_vdev_start_status = ret; + goto out; } -if (WARN_ON (__le32_to_cpu (arg.status))) -return ; + status =__le32_to_cpu (arg.status); +if (WARN_ON_ONCE (status)) { +ath10k_warn (ar,"vdev-start-response reports status error: %d (%s)\n" , + status, (status ==WMI_VDEV_START_CHAN_INVALID ) ? +"chan-invalid" :"unknown" ); +/* Setup is done one way or another though, so we should still +* do the completion, so don't return here. +*/ + ar->last_wmi_vdev_start_status = -EINVAL ; + } +out:complete (&ar->vdev_setup_done); }
drivers/net/wireless/ath/ath10k/wmi.h +7 -1
@@ -6642,11 +6642,17 @@ struct wmi_ch_info_ev_arg {__le32 rx_frame_count; }; +/* From 10.4 firmware, not sure all have the same values. */ +enum wmi_vdev_start_status { +WMI_VDEV_START_OK =0 , +WMI_VDEV_START_CHAN_INVALID , +}; +struct wmi_vdev_start_ev_arg {__le32 vdev_id;__le32 req_id;__le32 resp_type;/* %WMI_VDEV_RESP_ */ -__le32 status; +__le32 status;/* See wmi_vdev_start_status enum above */ };struct wmi_peer_kick_ev_arg {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 39/220 rtlwifi: btcoex: Use proper enumerated types for Wi-Fi only interface
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 31138a827d1b3d6e4855bddb5a1e44e7b32309c0 ]
Clang warns when one enumerated type is implicitly converted to another.
drivers/net/wireless/realtek/rtlwifi/btcoexist/halbtcoutsrc.c:1327:34:
warning: implicit conversion from enumeration type 'enum btc_chip_interface' to different enumeration type 'enum wifionly_chip_interface' [-Wenum-conversion]
                wifionly_cfg->chip_interface = BTC_INTF_PCI;
~ ^~~~~~~~~~~~drivers/net/wireless/realtek/rtlwifi/btcoexist/halbtcoutsrc.c:1330:34:
warning: implicit conversion from enumeration type 'enum btc_chip_interface' to different enumeration type 'enum wifionly_chip_interface' [-Wenum-conversion]
                wifionly_cfg->chip_interface = BTC_INTF_USB;
~ ^~~~~~~~~~~~drivers/net/wireless/realtek/rtlwifi/btcoexist/halbtcoutsrc.c:1333:34:
warning: implicit conversion from enumeration type 'enum btc_chip_interface' to different enumeration type 'enum wifionly_chip_interface' [-Wenum-conversion]
                wifionly_cfg->chip_interface = BTC_INTF_UNKNOWN;
                                             ~ ^~~~~~~~~~~~~~~~
3 warnings generated.
Use the values from the correct enumerated type, wifionly_chip_interface.
BTC_INTF_UNKNOWN = WIFIONLY_INTF_UNKNOWN = 0BTC_INTF_PCI = WIFIONLY_INTF_PCI = 1BTC_INTF_USB = WIFIONLY_INTF_USB = 2
---
 .../net/wireless/realtek/rtlwifi/btcoexist/halbtcoutsrc.c   | 6 +++---
 1 file changed, 3 insertions(+), 3 deletions(-)
drivers/net/wireless/realtek/rtlwifi/btcoexist/halbtcoutsrc.c +3 -3
@@ -1324,13 +1324,13 @@ bool exhalbtc_initlize_variables_wifi_only(struct rtl_priv *rtlpriv)switch (rtlpriv->rtlhal.interface) {case INTF_PCI : - wifionly_cfg->chip_interface =BTC_INTF_PCI ; + wifionly_cfg->chip_interface =WIFIONLY_INTF_PCI ;break ;case INTF_USB : - wifionly_cfg->chip_interface =BTC_INTF_USB ; + wifionly_cfg->chip_interface =WIFIONLY_INTF_USB ;break ;default : - wifionly_cfg->chip_interface =BTC_INTF_UNKNOWN ; + wifionly_cfg->chip_interface =WIFIONLY_INTF_UNKNOWN ;break ; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 40/220 ata: ahci_brcm: Allow using driver or DSL SoCs
In reply to Greg Kroah-HartmanFrom: Florian Fainelli <[email protected]>
[ Upstream commit 7fb44929cb0e5cdcde143e1ca3ca57b5b8247db0 ]
The Broadcom STB AHCI controller is the same as the one found on DSL SoCs, so we will utilize the same driver on these systems as well.
---
 drivers/ata/Kconfig | 3 ++-
 1 file changed, 2 insertions(+), 1 deletion(-)
drivers/ata/Kconfig +2 -1
@@ -121,7 +121,8 @@ config SATA_AHCI_PLATFORM config AHCI_BRCM tristate "Broadcom AHCI SATA support" - depends on ARCH_BRCMSTB || BMIPS_GENERIC || ARCH_BCM_NSP + depends on ARCH_BRCMSTB || BMIPS_GENERIC || ARCH_BCM_NSP || \ + ARCH_BCM_63XX help This option enables support for the AHCI SATA3 controller found on Broadcom SoC's.
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 41/220 PM / devfreq: Fix devfreq_add_device() when drivers are built as modules.
In reply to Greg Kroah-HartmanFrom: Enric Balletbo i Serra <[email protected]>
[ Upstream commit 23c7b54ca1cd1797ef39169ab85e6d46f1c2d061 ]
When the devfreq driver and the governor driver are built as modules, the call to devfreq_add_device() or governor_store() fails because the governor driver is not loaded at the time the devfreq driver loads. The devfreq driver has a build dependency on the governor but also should have a runtime dependency. We need to make sure that the governor driver is loaded before the devfreq driver.
This patch fixes this bug by adding a try_then_request_governor() function. First tries to find the governor, and then, if it is not found, it requests the module and tries again.
---
 drivers/devfreq/devfreq.c | 53 ++++++++++++++++++++++++++++++++++++---
 1 file changed, 49 insertions(+), 4 deletions(-)
drivers/devfreq/devfreq.c +49 -4
@@ -11,6 +11,7 @@*/ #include <linux/kernel.h> +#include <linux/kmod.h> #include <linux/sched.h> #include <linux/errno.h> #include <linux/err.h>
@@ -221,6 +222,49 @@ static struct devfreq_governor *find_devfreq_governor(const char *name)return ERR_PTR (-ENODEV ); } +/** +* try_then_request_governor() - Try to find the governor and request the +* module if is not found. +* @name: name of the governor +* +* Search the list of devfreq governors and request the module and try again +* if is not found. This can happen when both drivers (the governor driver +* and the driver that call devfreq_add_device) are built as modules. +* devfreq_list_lock should be held by the caller. Returns the matched +* governor's pointer. +*/ +static struct devfreq_governor *try_then_request_governor (const char *name) +{ +struct devfreq_governor *governor; +int err =0 ; + +if (IS_ERR_OR_NULL (name)) { +pr_err ("DEVFREQ: %s: Invalid parameters\n" , __func__); +return ERR_PTR (-EINVAL ); + } +WARN (!mutex_is_locked (&devfreq_list_lock), +"devfreq_list_lock must be locked." ); + + governor =find_devfreq_governor (name); +if (IS_ERR (governor)) { +mutex_unlock (&devfreq_list_lock); + +if (!strncmp (name,DEVFREQ_GOV_SIMPLE_ONDEMAND , +DEVFREQ_NAME_LEN )) + err =request_module ("governor_%s" ,"simpleondemand" ); +else + err =request_module ("governor_%s" , name); +/* Restore previous state before return */ +mutex_lock (&devfreq_list_lock); +if (err) +return NULL ; + + governor =find_devfreq_governor (name); + } + +return governor; +} +static int devfreq_notify_transition (struct devfreq *devfreq,struct devfreq_freqs *freqs,unsigned int state) {
@@ -646,9 +690,8 @@ struct devfreq *devfreq_add_device(struct device *dev,mutex_unlock (&devfreq->lock);mutex_lock (&devfreq_list_lock); -list_add (&devfreq->node, &devfreq_list); - governor =find_devfreq_governor (devfreq->governor_name); + governor =try_then_request_governor (devfreq->governor_name);if (IS_ERR (governor)) {dev_err (dev,"%s: Unable to find governor for the device\n" , __func__);
@@ -664,12 +707,14 @@ struct devfreq *devfreq_add_device(struct device *dev, __func__); goto err_init; } + +list_add (&devfreq->node, &devfreq_list); +mutex_unlock (&devfreq_list_lock);return devfreq; err_init: -list_del (&devfreq->node);mutex_unlock (&devfreq_list_lock);device_unregister (&devfreq->dev);
@@ -991,7 +1036,7 @@ static ssize_t governor_store(struct device *dev, struct device_attribute *attr,return -EINVAL ;mutex_lock (&devfreq_list_lock); - governor =find_devfreq_governor (str_governor); + governor =try_then_request_governor (str_governor);if (IS_ERR (governor)) { ret =PTR_ERR (governor); goto out;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 42/220 PM / devfreq: Fix handling of min/max_freq == 0
In reply to Greg Kroah-HartmanFrom: Matthias Kaehlcke <[email protected]>
[ Upstream commit df5cf4a36178c5d4f2b8b9469cb2f722e64cd102 ]
Commit ab8f58ad72c4 ("PM / devfreq: Set min/max_freq when adding the devfreq device") initializes df->min/max_freq with the min/max OPP when the device is added. Later commit f1d981eaecf8 ("PM / devfreq: Use the available min/max frequency") adds df->scaling_min/max_freq and the following to the frequency adjustment code:
max_freq = MIN(devfreq->scaling_max_freq, devfreq->max_freq);
With the current handling of min/max_freq this is incorrect:
Even though df->max_freq is now initialized to a value != 0 user space can still set it to 0, in this case max_freq would be 0 instead of df->scaling_max_freq as intended. In consequence the frequency adjustment is not performed:
  if (max_freq && freq > max_freq) {
	freq = max_freq;
To fix this set df->min/max freq to the min/max OPP in max/max_freq_store, when the user passes a value of 0. This also prevents df->max_freq from being set below the min OPP when df->min_freq is 0, and similar for min_freq. Since it is now guaranteed that df->min/max_freq can't be 0 the checks for this case can be removed.
---
 drivers/devfreq/devfreq.c | 42 ++++++++++++++++++++++++++++-----------
 1 file changed, 30 insertions(+), 12 deletions(-)
drivers/devfreq/devfreq.c +30 -12
@@ -327,11 +327,11 @@ int update_devfreq(struct devfreq *devfreq) max_freq =MIN (devfreq->scaling_max_freq, devfreq->max_freq); min_freq =MAX (devfreq->scaling_min_freq, devfreq->min_freq); -if (min_freq && freq < min_freq) { +if (freq < min_freq) { freq = min_freq; flags &= ~DEVFREQ_FLAG_LEAST_UPPER_BOUND ;/* Use GLB */ } -if (max_freq && freq > max_freq) { +if (freq > max_freq) { freq = max_freq; flags |=DEVFREQ_FLAG_LEAST_UPPER_BOUND ;/* Use LUB */ }
@@ -1171,17 +1171,26 @@ static ssize_t min_freq_store(struct device *dev, struct device_attribute *attr,struct devfreq *df =to_devfreq (dev);unsigned long value;int ret; -unsigned long max; ret =sscanf (buf,"%lu" , &value);if (ret !=1 )return -EINVAL ;mutex_lock (&df->lock); - max = df->max_freq; -if (value && max && value > max) { - ret = -EINVAL ; - goto unlock; + +if (value) { +if (value > df->max_freq) { + ret = -EINVAL ; + goto unlock; + } + }else { +unsigned long *freq_table = df->profile->freq_table; + +/* Get minimum frequency according to sorting order */ +if (freq_table[0 ] < freq_table[df->profile->max_state -1 ]) + value = freq_table[0 ]; +else + value = freq_table[df->profile->max_state -1 ]; } df->min_freq = value;
@@ -1206,17 +1215,26 @@ static ssize_t max_freq_store(struct device *dev, struct device_attribute *attr,struct devfreq *df =to_devfreq (dev);unsigned long value;int ret; -unsigned long min; ret =sscanf (buf,"%lu" , &value);if (ret !=1 )return -EINVAL ;mutex_lock (&df->lock); - min = df->min_freq; -if (value && min && value < min) { - ret = -EINVAL ; - goto unlock; + +if (value) { +if (value < df->min_freq) { + ret = -EINVAL ; + goto unlock; + } + }else { +unsigned long *freq_table = df->profile->freq_table; + +/* Get maximum frequency according to sorting order */ +if (freq_table[0 ] < freq_table[df->profile->max_state -1 ]) + value = freq_table[df->profile->max_state -1 ]; +else + value = freq_table[0 ]; } df->max_freq = value;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 43/220 PM / devfreq: stopping the governor before device_unregister()
In reply to Greg Kroah-HartmanFrom: Vincent Donnefort <[email protected]>
[ Upstream commit 2f061fd0c2d852e32e03a903fccd810663c5c31e ]
device_release() is freeing the resources before calling the device specific release callback which is, in the case of devfreq, stopping the governor.
It is a problem as some governors are using the device resources. e.g. simpleondemand which is using the devfreq deferrable monitoring work. If it is not stopped before the resources are freed, it might lead to a use after free.
---
 drivers/devfreq/devfreq.c | 9 ++++-----
 1 file changed, 4 insertions(+), 5 deletions(-)
drivers/devfreq/devfreq.c +4 -5
@@ -578,10 +578,6 @@ static void devfreq_dev_release(struct device *dev)list_del (&devfreq->node);mutex_unlock (&devfreq_list_lock); -if (devfreq->governor) - devfreq->governor->event_handler (devfreq, -DEVFREQ_GOV_STOP ,NULL ); -if (devfreq->profile->exit) devfreq->profile->exit (devfreq->dev.parent);
@@ -717,7 +713,7 @@ struct devfreq *devfreq_add_device(struct device *dev, err_init:mutex_unlock (&devfreq_list_lock); -device_unregister (&devfreq->dev); +devfreq_remove_device (devfreq); devfreq =NULL ; err_dev:if (devfreq)
@@ -738,6 +734,9 @@ int devfreq_remove_device(struct devfreq *devfreq)if (!devfreq)return -EINVAL ; +if (devfreq->governor) + devfreq->governor->event_handler (devfreq, +DEVFREQ_GOV_STOP ,NULL );device_unregister (&devfreq->dev);return 0 ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 44/220 ath9k: fix reporting calculated new FFT upper max
In reply to Greg Kroah-HartmanFrom: Simon Wunderlich <[email protected]>
[ Upstream commit 4fb5837ac2bd46a85620b297002c704e9958f64d ]
Since the debug print code is outside of the loop, it shouldn't use the loop iterator anymore but instead print the found maximum index.
---
 drivers/net/wireless/ath/ath9k/common-spectral.c | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/net/wireless/ath/ath9k/common-spectral.c +1 -1
@@ -411,7 +411,7 @@ ath_cmn_process_ht20_40_fft(struct ath_rx_status *rs,ath_dbg (common,SPECTRAL_SCAN ,"Calculated new upper max 0x%X at %i\n" , - tmp_mag, i); + tmp_mag, fft_sample_40.upper_max_index); }else for (i = dc_pos; i <SPECTRAL_HT20_40_NUM_BINS ; i++) {if (fft_sample_40.data[i] == (upper_mag >> max_exp))
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 45/220 selftests/tls: Fix recv(MSG_PEEK) & splice() test cases
In reply to Greg Kroah-HartmanFrom: Vakul Garg <[email protected]>
[ Upstream commit 0ed3015c9964dab7a1693b3e40650f329c16691e ]
TLS test cases splice_from_pipe, send_and_splice & recv_peek_multiple_records expect to receive a given nummber of bytes and then compare them against the number of bytes which were sent. Therefore, system call recv() must not return before receiving the requested number of bytes, otherwise the subsequent memcmp() fails. This patch passes MSG_WAITALL flag to recv() so that it does not return prematurely before requested number of bytes are copied to receive buffer.
---
 tools/testing/selftests/net/tls.c | 20 ++++++++++----------
 1 file changed, 10 insertions(+), 10 deletions(-)
tools/testing/selftests/net/tls.c +10 -10
@@ -288,7 +288,7 @@ TEST_F(tls, splice_from_pipe)ASSERT_GE (pipe (p),0 );EXPECT_GE (write (p[1 ], mem_send, send_len),0 );EXPECT_GE (splice (p[0 ],NULL , self->fd,NULL , send_len,0 ),0 ); -EXPECT_GE (recv (self->cfd, mem_recv, send_len,0 ),0 ); +EXPECT_EQ (recv (self->cfd, mem_recv, send_len,MSG_WAITALL ), send_len);EXPECT_EQ (memcmp (mem_send, mem_recv, send_len),0 ); }
@@ -322,13 +322,13 @@ TEST_F(tls, send_and_splice)ASSERT_GE (pipe (p),0 );EXPECT_EQ (send (self->fd, test_str, send_len2,0 ), send_len2); -EXPECT_NE (recv (self->cfd, buf, send_len2,0 ),-1 ); +EXPECT_EQ (recv (self->cfd, buf, send_len2,MSG_WAITALL ), send_len2);EXPECT_EQ (memcmp (test_str, buf, send_len2),0 );EXPECT_GE (write (p[1 ], mem_send, send_len), send_len);EXPECT_GE (splice (p[0 ],NULL , self->fd,NULL , send_len,0 ), send_len); -EXPECT_GE (recv (self->cfd, mem_recv, send_len,0 ),0 ); +EXPECT_EQ (recv (self->cfd, mem_recv, send_len,MSG_WAITALL ), send_len);EXPECT_EQ (memcmp (mem_send, mem_recv, send_len),0 ); }
@@ -516,17 +516,17 @@ TEST_F(tls, recv_peek_multiple_records) len =strlen (test_str_second) +1 ;EXPECT_EQ (send (self->fd, test_str_second, len,0 ), len); - len =sizeof (buf); + len =strlen (test_str_first);memset (buf,0 , len); -EXPECT_NE (recv (self->cfd, buf, len,MSG_PEEK ),-1 ); +EXPECT_EQ (recv (self->cfd, buf, len,MSG_PEEK |MSG_WAITALL ), len);/* MSG_PEEK can only peek into the current record. */ - len =strlen (test_str_first) +1 ; + len =strlen (test_str_first);EXPECT_EQ (memcmp (test_str_first, buf, len),0 ); - len =sizeof (buf); + len =strlen (test_str) +1 ;memset (buf,0 , len); -EXPECT_NE (recv (self->cfd, buf, len,0 ),-1 ); +EXPECT_EQ (recv (self->cfd, buf, len,MSG_WAITALL ), len);/* Non-MSG_PEEK will advance strparser (and therefore record) * however.
@@ -543,9 +543,9 @@ TEST_F(tls, recv_peek_multiple_records) len =strlen (test_str_second) +1 ;EXPECT_EQ (send (self->fd, test_str_second, len,0 ), len); - len =sizeof (buf); + len =strlen (test_str) +1 ;memset (buf,0 , len); -EXPECT_NE (recv (self->cfd, buf, len,MSG_PEEK ),-1 ); +EXPECT_EQ (recv (self->cfd, buf, len,MSG_PEEK |MSG_WAITALL ), len); len =strlen (test_str) +1 ;EXPECT_EQ (memcmp (test_str, buf, len),0 );
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 46/220 usb: gadget: udc: fotg210-udc: Fix a sleep-in-atomic-context bug in fotg210_get_status()
In reply to Greg Kroah-HartmanFrom: Jia-Ju Bai <[email protected]>
[ Upstream commit 2337a77c1cc86bc4e504ecf3799f947659c86026 ]
The driver may sleep in an interrupt handler.
The function call path (from bottom to top) in Linux-4.17 is:
[FUNC] fotg210_ep_queue(GFP_KERNEL)drivers/usb/gadget/udc/fotg210-udc.c, 744:
fotg210_ep_queue in fotg210_get_status
drivers/usb/gadget/udc/fotg210-udc.c, 768:
fotg210_get_status in fotg210_setup_packetdrivers/usb/gadget/udc/fotg210-udc.c, 949:
fotg210_setup_packet in fotg210_irq (interrupt handler)
To fix this bug, GFP_KERNEL is replaced with GFP_ATOMIC. If possible, spin_unlock() and spin_lock() around fotg210_ep_queue() can be also removed.
This bug is found by my static analysis tool DSAC.
---
 drivers/usb/gadget/udc/fotg210-udc.c | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/usb/gadget/udc/fotg210-udc.c +1 -1
@@ -741,7 +741,7 @@ static void fotg210_get_status(struct fotg210_udc *fotg210, fotg210->ep0_req->length =2 ;spin_unlock (&fotg210->lock); -fotg210_ep_queue (fotg210->gadget.ep0, fotg210->ep0_req,GFP_KERNEL ); +fotg210_ep_queue (fotg210->gadget.ep0, fotg210->ep0_req,GFP_ATOMIC );spin_lock (&fotg210->lock); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 47/220 usb: dwc3: gadget: Check ENBLSLPM before sending ep command
In reply to Greg Kroah-HartmanFrom: Thinh Nguyen <[email protected]>
[ Upstream commit 87dd96111b0bb8e616fcbd74dbf4bb4182f2c596 ]
When operating in USB 2.0 speeds (HS/FS), if GUSB2PHYCFG.ENBLSLPM or GUSB2PHYCFG.SUSPHY is set, it must be cleared before issuing an endpoint command.
Current implementation only save and restore GUSB2PHYCFG.SUSPHY configuration. We must save and clear both GUSB2PHYCFG.ENBLSLPM and GUSB2PHYCFG.SUSPHY settings. Restore them after the command is completed.
DWC_usb3 3.30a and DWC_usb31 1.90a programming guide section 3.2.2
---
 drivers/usb/dwc3/gadget.c | 29 +++++++++++++++++++----------
 1 file changed, 19 insertions(+), 10 deletions(-)
drivers/usb/dwc3/gadget.c +19 -10
@@ -271,27 +271,36 @@ int dwc3_send_gadget_ep_cmd(struct dwc3_ep *dep, unsigned cmd,const struct usb_endpoint_descriptor *desc = dep->endpoint.desc;struct dwc3 *dwc = dep->dwc;u32 timeout =1000 ; +u32 saved_config =0 ;u32 reg;int cmd_status =0 ; -int susphy = false;int ret = -EINVAL ;/* -* Synopsys Databook 2.60a states, on section 6.3.2.5.[1-8], that if -* we're issuing an endpoint command, we must check if -* GUSB2PHYCFG.SUSPHY bit is set. If it is, then we need to clear it. +* When operating in USB 2.0 speeds (HS/FS), if GUSB2PHYCFG.ENBLSLPM or +* GUSB2PHYCFG.SUSPHY is set, it must be cleared before issuing an +* endpoint command. * -* We will also set SUSPHY bit to what it was before returning as stated -* by the same section on Synopsys databook. +* Save and clear both GUSB2PHYCFG.ENBLSLPM and GUSB2PHYCFG.SUSPHY +* settings. Restore them after the command is completed. +* +* DWC_usb3 3.30a and DWC_usb31 1.90a programming guide section 3.2.2 */ if (dwc->gadget.speed <=USB_SPEED_HIGH ) { reg =dwc3_readl (dwc->regs,DWC3_GUSB2PHYCFG (0 ));if (unlikely (reg &DWC3_GUSB2PHYCFG_SUSPHY )) { - susphy = true; + saved_config |=DWC3_GUSB2PHYCFG_SUSPHY ; reg &= ~DWC3_GUSB2PHYCFG_SUSPHY ; -dwc3_writel (dwc->regs,DWC3_GUSB2PHYCFG (0 ), reg); } + +if (reg &DWC3_GUSB2PHYCFG_ENBLSLPM ) { + saved_config |=DWC3_GUSB2PHYCFG_ENBLSLPM ; + reg &= ~DWC3_GUSB2PHYCFG_ENBLSLPM ; + } + +if (saved_config) +dwc3_writel (dwc->regs,DWC3_GUSB2PHYCFG (0 ), reg); }if (DWC3_DEPCMD_CMD (cmd) ==DWC3_DEPCMD_STARTTRANSFER ) {
@@ -380,9 +389,9 @@ int dwc3_send_gadget_ep_cmd(struct dwc3_ep *dep, unsigned cmd,dwc3_gadget_ep_get_transfer_index (dep); } -if (unlikely (susphy)) { +if (saved_config) { reg =dwc3_readl (dwc->regs,DWC3_GUSB2PHYCFG (0 )); - reg |=DWC3_GUSB2PHYCFG_SUSPHY ; + reg |= saved_config;dwc3_writel (dwc->regs,DWC3_GUSB2PHYCFG (0 ), reg); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 48/220 nl80211: Fix a GET_KEY reply attribute
In reply to Greg Kroah-HartmanFrom: Andrew Zaborowski <[email protected]>
[ Upstream commit efdfce7270de85a8706d1ea051bef3a7486809ff ]
Use the NL80211_KEY_IDX attribute inside the NL80211_ATTR_KEY in NL80211_CMD_GET_KEY responses to comply with nl80211_key_policy. This is unlikely to affect existing userspace.
---
 net/wireless/nl80211.c | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
net/wireless/nl80211.c +1 -1
@@ -3396,7 +3396,7 @@ static void get_key_callback(void *c, struct key_params *params) params->cipher))) goto nla_put_failure; -if (nla_put_u8 (cookie->msg,NL80211_ATTR_KEY_IDX , cookie->idx)) +if (nla_put_u8 (cookie->msg,NL80211_KEY_IDX , cookie->idx)) goto nla_put_failure;nla_nest_end (cookie->msg, key);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 49/220 irqchip/irq-mvebu-icu: Fix wrong private data retrieval
In reply to Greg Kroah-HartmanFrom: Miquel Raynal <[email protected]>
[ Upstream commit 2b4dab69dcca13c5be2ddaf1337ae4accd087de6 ]
The irq_domain structure has an host_data pointer that just stores private data. It is meant to not be touched by the IRQ core. However, when it comes to MSI, the MSI layer adds its own private data there with a structure that also has a host_data pointer.
Because this IRQ domain is an MSI domain, to access private data we should do a d->host_data->host_data, also wrapped as 'platform_msi_get_host_data()'.
This bug was lying there silently because the 'icu' structure retrieved this way was just called by dev_err(), only producing a '(NULL device *):' output on the console.
---
 drivers/irqchip/irq-mvebu-icu.c | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/irqchip/irq-mvebu-icu.c +1 -1
@@ -105,7 +105,7 @@ static int mvebu_icu_irq_domain_translate(struct irq_domain *d, struct irq_fwspec *fwspec, unsigned long *hwirq, unsigned int *type) { - struct mvebu_icu *icu = d->host_data; + struct mvebu_icu *icu = platform_msi_get_host_data(d);unsigned int icu_group;/* Check the count of the parameters in dt */
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 50/220 watchdog: core: fix null pointer dereference when releasing cdev
In reply to Greg Kroah-HartmanFrom: Wolfram Sang <[email protected]>
[ Upstream commit 953b9dd7725bad55a922a35e75bff7bebf7b9978 ]
watchdog_stop() calls watchdog_update_worker() which needs a valid wdd->wd_data pointer. So, when unregistering the cdev, clear the pointers after we call watchdog_stop(), not before.
---
 drivers/watchdog/watchdog_dev.c | 10 +++++-----
 1 file changed, 5 insertions(+), 5 deletions(-)
drivers/watchdog/watchdog_dev.c +5 -5
@@ -1019,16 +1019,16 @@ static void watchdog_cdev_unregister(struct watchdog_device *wdd) old_wd_data =NULL ; } -mutex_lock (&wd_data->lock); - wd_data->wdd =NULL ; - wdd->wd_data =NULL ; -mutex_unlock (&wd_data->lock); -if (watchdog_active (wdd) &&test_bit (WDOG_STOP_ON_UNREGISTER , &wdd->status)) {watchdog_stop (wdd); } +mutex_lock (&wd_data->lock); + wd_data->wdd =NULL ; + wdd->wd_data =NULL ; +mutex_unlock (&wd_data->lock); +hrtimer_cancel (&wd_data->timer);kthread_cancel_work_sync (&wd_data->work);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 51/220 watchdog: renesas_wdt: stop when unregistering
In reply to Greg Kroah-HartmanFrom: Wolfram Sang <[email protected]>
[ Upstream commit 14de99b44b34dbb9d0f64845b1cbb675e047767e ]
We want to go into a sane state when unregistering. Currently, it happens that the watchdog stops when unbinding because of RuntimePM stopping the core clock. When rebinding, the core clock gets reactivated and the watchdog fires even though it hasn't been opened by userspace yet. Strange scenario, yes, but sane state is much preferred anyhow.
---
 drivers/watchdog/renesas_wdt.c | 1 +
 1 file changed, 1 insertion(+)
drivers/watchdog/renesas_wdt.c +1 -0
@@ -239,6 +239,7 @@ static int rwdt_probe(struct platform_device *pdev)watchdog_set_drvdata (&priv->wdev, priv);watchdog_set_nowayout (&priv->wdev, nowayout);watchdog_set_restart_priority (&priv->wdev,0 ); +watchdog_stop_on_unregister (&priv->wdev);/* This overrides the default timeout only if DT configuration was found */ ret =watchdog_init_timeout (&priv->wdev,0 , &pdev->dev);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 52/220 watchdog: sama5d4: fix timeout-sec usage
In reply to Greg Kroah-HartmanFrom: Romain Izard <[email protected]>
[ Upstream commit 2e0432f8f8ad11b4bd208445360220efa5b37d82 ]
When using watchdog_init_timeout to update the default timeout value, an error means that there is no "timeout-sec" in the relevant device tree node.
This should not prevent binding of the driver to the device.
---
 drivers/watchdog/sama5d4_wdt.c | 6 +-----
 1 file changed, 1 insertion(+), 5 deletions(-)
drivers/watchdog/sama5d4_wdt.c +1 -5
@@ -247,11 +247,7 @@ static int sama5d4_wdt_probe(struct platform_device *pdev) } } - ret =watchdog_init_timeout (wdd, wdt_timeout, &pdev->dev); -if (ret) { -dev_err (&pdev->dev,"unable to set timeout value\n" ); -return ret; - } +watchdog_init_timeout (wdd, wdt_timeout, &pdev->dev); timeout =WDT_SEC2TICKS (wdd->timeout);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 53/220 watchdog: w83627hf_wdt: Support NCT6796D, NCT6797D, NCT6798D
In reply to Greg Kroah-HartmanFrom: Guenter Roeck <[email protected]>
[ Upstream commit 57cbf0e3a0fd48e5ad8f3884562e8dde4827c1c8 ]
The watchdog controller on NCT6796D, NCT6797D, and NCT6798D is compatible with the wtachdog controller on other Nuvoton chips.
---
 drivers/watchdog/w83627hf_wdt.c | 8 +++++++-
 1 file changed, 7 insertions(+), 1 deletion(-)
drivers/watchdog/w83627hf_wdt.c +7 -1
@@ -50,7 +50,7 @@ static int cr_wdt_csr; /* WDT control & status register */enum chips { w83627hf, w83627s, w83697hf, w83697ug, w83637hf, w83627thf, w83687thf, w83627ehf, w83627dhg, w83627uhg, w83667hg, w83627dhg_p, w83667hg_b, nct6775, nct6776, nct6779, nct6791, nct6792, nct6793, - nct6795, nct6102 }; + nct6795, nct6796, nct6102 };static int timeout;/* in seconds */ module_param (timeout, int,0 );
@@ -100,6 +100,7 @@ MODULE_PARM_DESC(early_disable, "Disable watchdog at boot time (default=0)");#define NCT6792_ID 0xc9#define NCT6793_ID 0xd1#define NCT6795_ID 0xd3 +#define NCT6796_ID 0xd4/* also NCT9697D, NCT9698D */ #define W83627HF_WDT_TIMEOUT 0xf6#define W83697HF_WDT_TIMEOUT 0xf4
@@ -209,6 +210,7 @@ static int w83627hf_init(struct watchdog_device *wdog, enum chips chip)case nct6792:case nct6793:case nct6795: +case nct6796:case nct6102:/* * These chips have a fixed WDTO# output pin (W83627UHG),
@@ -407,6 +409,9 @@ static int wdt_find(int addr)case NCT6795_ID : ret = nct6795;break ; +case NCT6796_ID : + ret = nct6796; +break ;case NCT6102_ID : ret = nct6102; cr_wdt_timeout =NCT6102D_WDT_TIMEOUT ;
@@ -450,6 +455,7 @@ static int __init wdt_init(void)"NCT6792" ,"NCT6793" ,"NCT6795" , +"NCT6796" , "NCT6102", };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 54/220 KVM: PPC: Inform the userspace about TCE update failures
In reply to Greg Kroah-HartmanFrom: Alexey Kardashevskiy <[email protected]>
[ Upstream commit f7960e299f13f069d6f3d4e157d91bfca2669677 ]
We return H_TOO_HARD from TCE update handlers when we think that the next handler (realmode -> virtual mode -> user mode) has a chance to handle the request; H_HARDWARE/H_CLOSED otherwise.
This changes the handlers to return H_TOO_HARD on every error giving the userspace an opportunity to handle any request or at least log them all.
---
 arch/powerpc/kvm/book3s_64_vio.c    | 8 ++++----
 arch/powerpc/kvm/book3s_64_vio_hv.c | 6 +++---
 2 files changed, 7 insertions(+), 7 deletions(-)
arch/powerpc/kvm/book3s_64_vio.c +4 -4
@@ -401,7 +401,7 @@ static long kvmppc_tce_iommu_do_unmap(struct kvm *kvm,long ret;if (WARN_ON_ONCE (iommu_tce_xchg (tbl, entry, &hpa, &dir))) -return H_HARDWARE ; +return H_TOO_HARD ;if (dir ==DMA_NONE )return H_SUCCESS ;
@@ -449,15 +449,15 @@ long kvmppc_tce_iommu_do_map(struct kvm *kvm, struct iommu_table *tbl,return H_TOO_HARD ;if (WARN_ON_ONCE (mm_iommu_ua_to_hpa (mem, ua, tbl->it_page_shift, &hpa))) -return H_HARDWARE ; +return H_TOO_HARD ;if (mm_iommu_mapped_inc (mem)) -return H_CLOSED ; +return H_TOO_HARD ; ret =iommu_tce_xchg (tbl, entry, &hpa, &dir);if (WARN_ON_ONCE (ret)) {mm_iommu_mapped_dec (mem); -return H_HARDWARE ; +return H_TOO_HARD ; }if (dir !=DMA_NONE )
arch/powerpc/kvm/book3s_64_vio_hv.c +3 -3
@@ -300,10 +300,10 @@ static long kvmppc_rm_tce_iommu_do_map(struct kvm *kvm, struct iommu_table *tbl,if (WARN_ON_ONCE_RM (mm_iommu_ua_to_hpa_rm (mem, ua, tbl->it_page_shift, &hpa))) -return H_HARDWARE ; +return H_TOO_HARD ;if (WARN_ON_ONCE_RM (mm_iommu_mapped_inc (mem))) -return H_CLOSED ; +return H_TOO_HARD ; ret =iommu_tce_xchg_rm (kvm->mm, tbl, entry, &hpa, &dir);if (ret) {
@@ -501,7 +501,7 @@ long kvmppc_rm_h_put_tce_indirect(struct kvm_vcpu *vcpu, rmap = (void *)vmalloc_to_phys (rmap);if (WARN_ON_ONCE_RM (!rmap)) -return H_HARDWARE ; +return H_TOO_HARD ;/* * Synchronize with the MMU notifier callbacks in
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 55/220 printk: Do not miss new messages when replaying the log
In reply to Greg Kroah-HartmanFrom: Petr Mladek <[email protected]>
[ Upstream commit f92b070f2dc89a8ff1a0cc8b608e20abef894c7d ]
The variable "exclusive_console" is used to reply all existing messages on a newly registered console. It is cleared when all messages are out.
The problem is that new messages might appear in the meantime. These are then visible only on the exclusive console.
The obvious solution is to clear "exclusive_console" after we replay all messages that were already proceed before we started the reply.
To: Steven Rostedt <[email protected]>
--- kernel/printk/printk.c | 13 +++++++++---- 1 file changed, 9 insertions(+), 4 deletions(-)
kernel/printk/printk.c +9 -4
@@ -423,6 +423,7 @@ static u32 log_next_idx;/* the next printk record to write to the console */ static u64 console_seq;static u32 console_idx; +static u64 exclusive_console_stop_seq;/* the next printk record to read after the last 'clear' command */ static u64 clear_seq;
@@ -2014,6 +2015,7 @@ static u64 syslog_seq;static u32 syslog_idx;static u64 console_seq;static u32 console_idx; +static u64 exclusive_console_stop_seq;static u64 log_first_seq;static u32 log_first_idx;static u64 log_next_seq;
@@ -2381,6 +2383,12 @@ void console_unlock(void) goto skip; } +/* Output to all consoles once old messages replayed. */ +if (unlikely (exclusive_console && + console_seq >= exclusive_console_stop_seq)) { + exclusive_console =NULL ; + } + len += msg_print_text(msg, console_msg_format & MSG_FORMAT_SYSLOG, text + len,
@@ -2423,10 +2431,6 @@ void console_unlock(void) console_locked =0 ; -/* Release the exclusive_console once it is used */ -if (unlikely (exclusive_console)) - exclusive_console =NULL ; -raw_spin_unlock (&logbuf_lock);up_console_sem ();
@@ -2711,6 +2715,7 @@ void register_console(struct console *newcon)* the already-registered consoles. */ exclusive_console = newcon; + exclusive_console_stop_seq = console_seq; }console_unlock ();console_sysfs_notify ();
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 56/220 printk: CON_PRINTBUFFER console registration is a bit racy
In reply to Greg Kroah-HartmanFrom: Sergey Senozhatsky <[email protected]>
[ Upstream commit 884e370ea88c109a3b982f4eb9ecd82510a3a1fe ]
CON_PRINTBUFFER console registration requires us to do several preparation steps:
- Rollback console_seq to replay logbuf messages which were already seen on other consoles;
- Set exclusive_console flag so console_unlock() will ->write() logbuf messages only to the exclusive_console driver.
The way we do it, however, is a bit racy
logbuf_lock_irqsave(flags); console_seq = syslog_seq; console_idx = syslog_idx; logbuf_unlock_irqrestore(flags); << preemption enabled << irqs enabled exclusive_console = newcon; console_unlock();
We rollback console_seq under logbuf_lock with IRQs disabled, but we set exclusive_console with local IRQs enabled and logbuf unlocked. If the system oops-es or panic-s before we set exclusive_console - and given that we have IRQs and preemption enabled there is such a possibility - we will re-play all logbuf messages to every registered console, which may be a bit annoying and time consuming.
Move exclusive_console assignment to the same IRQs-disabled and logbuf_lock-protected section where we rollback console_seq.
To: Steven Rostedt <[email protected]>
--- kernel/printk/printk.c | 6 +++++- 1 file changed, 5 insertions(+), 1 deletion(-)
kernel/printk/printk.c +5 -1
@@ -2708,14 +2708,18 @@ void register_console(struct console *newcon)logbuf_lock_irqsave (flags); console_seq = syslog_seq; console_idx = syslog_idx; -logbuf_unlock_irqrestore (flags);/* * We're about to replay the log buffer. Only do this to the * just-registered console to avoid excessive message spam to * the already-registered consoles. +* +* Set exclusive_console with disabled interrupts to reduce +* race window with eventual console_flush_on_panic() that +* ignores console_lock. */ exclusive_console = newcon; exclusive_console_stop_seq = console_seq; +logbuf_unlock_irqrestore (flags); }console_unlock ();console_sysfs_notify ();
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 57/220 dmaengine: ep93xx: Return proper enum in ep93xx_dma_chan_direction
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 9524d6b265f9b2b9a61fceb2ee2ce1c2a83e39ca ]
Clang warns when implicitly converting from one enumerated type to another. Avoid this by using the equivalent value from the expected type.
In file included from drivers/dma/ep93xx_dma.c:30:./include/linux/platform_data/dma-ep93xx.h:88:10: warning: implicit conversion from enumeration type 'enum dma_data_direction' to different enumeration type 'enum dma_transfer_direction' [-Wenum-conversion]
return DMA_NONE;
~~~~~~ ^~~~~~~~1 warning generated.
--- include/linux/platform_data/dma-ep93xx.h | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
include/linux/platform_data/dma-ep93xx.h +1 -1
@@ -85,7 +85,7 @@ static inline enum dma_transfer_direction ep93xx_dma_chan_direction(struct dma_chan *chan) {if (!ep93xx_dma_chan_is_m2p (chan)) -return DMA_NONE ; +return DMA_TRANS_NONE ;/* even channels are for TX, odd for RX */ return (chan->chan_id %2 ==0 ) ?DMA_MEM_TO_DEV :DMA_DEV_TO_MEM ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 58/220 dmaengine: timb_dma: Use proper enum in td_prep_slave_sg
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 5e621f5d538985f010035c6f3e28c22829d36db1 ]
Clang warns when implicitly converting from one enumerated type to another. Avoid this by using the equivalent value from the expected type.
drivers/dma/timb_dma.c:548:27: warning: implicit conversion from enumeration type 'enum dma_transfer_direction' to different enumeration type 'enum dma_data_direction' [-Wenum-conversion]
td_desc->desc_list_len, DMA_MEM_TO_DEV);
^~~~~~~~~~~~~~1 warning generated.
--- drivers/dma/timb_dma.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/dma/timb_dma.c +1 -1
@@ -545,7 +545,7 @@ static struct dma_async_tx_descriptor *td_prep_slave_sg(struct dma_chan *chan, }dma_sync_single_for_device (chan2dmadev (chan), td_desc->txd.phys, - td_desc->desc_list_len,DMA_MEM_TO_DEV ); + td_desc->desc_list_len,DMA_TO_DEVICE );return &td_desc->txd; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 59/220 ALSA: hda: Fix mismatch for register mask and value in ext controller.
In reply to Greg Kroah-HartmanFrom: Keyon Jie <[email protected]>
[ Upstream commit c32bf867cb6721d6ea04044d33f19c8bd81280c1 ]
E.g. for snd_hdac_ext_bus_link_power_up(), we should set mask to be AZX_MLCTL_SPA(it was 0), and AZX_MLCTL_SPA as value to power up it, here correct it and several similar mismatches.
--- sound/hda/ext/hdac_ext_controller.c | 22 ++++++++++++++-------- 1 file changed, 14 insertions(+), 8 deletions(-)
sound/hda/ext/hdac_ext_controller.c +14 -8
@@ -48,9 +48,11 @@ void snd_hdac_ext_bus_ppcap_enable(struct hdac_bus *bus, bool enable) }if (enable) -snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL ,0 ,AZX_PPCTL_GPROCEN ); +snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL , +AZX_PPCTL_GPROCEN ,AZX_PPCTL_GPROCEN );else -snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL ,AZX_PPCTL_GPROCEN ,0 ); +snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL , +AZX_PPCTL_GPROCEN ,0 ); }EXPORT_SYMBOL_GPL (snd_hdac_ext_bus_ppcap_enable);
@@ -68,9 +70,11 @@ void snd_hdac_ext_bus_ppcap_int_enable(struct hdac_bus *bus, bool enable) }if (enable) -snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL ,0 ,AZX_PPCTL_PIE ); +snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL , +AZX_PPCTL_PIE ,AZX_PPCTL_PIE );else -snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL ,AZX_PPCTL_PIE ,0 ); +snd_hdac_updatel (bus->ppcap,AZX_REG_PP_PPCTL , +AZX_PPCTL_PIE ,0 ); }EXPORT_SYMBOL_GPL (snd_hdac_ext_bus_ppcap_int_enable);
@@ -194,7 +198,8 @@ static int check_hdac_link_power_active(struct hdac_ext_link *link, bool enable)*/ int snd_hdac_ext_bus_link_power_up (struct hdac_ext_link *link) { -snd_hdac_updatel (link->ml_addr,AZX_REG_ML_LCTL ,0 ,AZX_MLCTL_SPA ); +snd_hdac_updatel (link->ml_addr,AZX_REG_ML_LCTL , +AZX_MLCTL_SPA ,AZX_MLCTL_SPA );return check_hdac_link_power_active (link, true); }
@@ -222,8 +227,8 @@ int snd_hdac_ext_bus_link_power_up_all(struct hdac_bus *bus)int ret;list_for_each_entry (hlink, &bus->hlink_list, list) { -snd_hdac_updatel (hlink->ml_addr, -AZX_REG_ML_LCTL ,0 ,AZX_MLCTL_SPA ); +snd_hdac_updatel (hlink->ml_addr,AZX_REG_ML_LCTL , +AZX_MLCTL_SPA ,AZX_MLCTL_SPA ); ret =check_hdac_link_power_active (hlink, true);if (ret <0 )return ret;
@@ -243,7 +248,8 @@ int snd_hdac_ext_bus_link_power_down_all(struct hdac_bus *bus)int ret;list_for_each_entry (hlink, &bus->hlink_list, list) { -snd_hdac_updatel (hlink->ml_addr,AZX_REG_ML_LCTL ,AZX_MLCTL_SPA ,0 ); +snd_hdac_updatel (hlink->ml_addr,AZX_REG_ML_LCTL , +AZX_MLCTL_SPA ,0 ); ret =check_hdac_link_power_active (hlink, false);if (ret <0 )return ret;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 60/220 ext4: fix build error when DX_DEBUG is defined
In reply to Greg Kroah-HartmanFrom: Gabriel Krisman Bertazi <[email protected]>
[ Upstream commit 799578ab16e86b074c184ec5abbda0bc698c7b0b ]
Enabling DX_DEBUG triggers the build error below. info is an attribute of the dxroot structure.
linux/fs/ext4/namei.c:2264:12: error: ‘info’ undeclared (first use in this function); did you mean ‘insl’?
info->indirect_levels));
--- fs/ext4/namei.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
fs/ext4/namei.c +1 -1
@@ -2284,7 +2284,7 @@ static int ext4_dx_add_entry(handle_t *handle, struct ext4_filename *fname, dxroot->info.indirect_levels +=1 ;dxtrace (printk (KERN_DEBUG "Creating %d level index...\n" , - info->indirect_levels)); + dxroot->info.indirect_levels)); err =ext4_handle_dirty_dx_node (handle, dir, frame->bh);if (err) goto journal_error;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 61/220 clk: keystone: Enable TISCI clocks if K3_ARCH
In reply to Greg Kroah-HartmanFrom: Nishanth Menon <[email protected]>
[ Upstream commit 2f149e6e14bcb5e581e49307b54aafcd6f74a74f ]
K3_ARCH uses TISCI for clocks as well. Enable the same for the driver support.
--- drivers/clk/Makefile | 1 + drivers/clk/keystone/Kconfig | 2 +- 2 files changed, 2 insertions(+), 1 deletion(-)
drivers/clk/Makefile +1 -0
@@ -73,6 +73,7 @@ obj-$(CONFIG_ARCH_HISI) += hisilicon/ obj-y += imgtec/ obj-$(CONFIG_ARCH_MXC) += imx/ obj-$(CONFIG_MACH_INGENIC) += ingenic/ +obj-$(CONFIG_ARCH_K3) += keystone/ obj-$(CONFIG_ARCH_KEYSTONE) += keystone/ obj-$(CONFIG_MACH_LOONGSON32) += loongson1/ obj-y += mediatek/
drivers/clk/keystone/Kconfig +1 -1
@@ -7,7 +7,7 @@ config COMMON_CLK_KEYSTONE config TI_SCI_CLK tristate "TI System Control Interface clock drivers" - depends on (ARCH_KEYSTONE || COMPILE_TEST) && OF + depends on (ARCH_KEYSTONE || ARCH_K3 || COMPILE_TEST) && OF depends on TI_SCI_PROTOCOL default ARCH_KEYSTONE ---help---
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 62/220 sunrpc: Fix connect metrics
In reply to Greg Kroah-HartmanFrom: Chuck Lever <[email protected]>
[ Upstream commit 3968a8a5310404c2f0b9e4d9f28cab13a12bc4fd ]
For TCP, the logic in xprt_connect_status is currently never invoked to record a successful connection. Commit 2a4919919a97 ("SUNRPC:
Return EAGAIN instead of ENOTCONN when waking up xprt->pending") changed the way TCP xprt's are awoken after a connect succeeds.
Instead, change connection-oriented transports to bump connect_count and compute connect_time the moment that XPRT_CONNECTED is set.
--- net/sunrpc/xprt.c | 14 ++++---------- net/sunrpc/xprtrdma/transport.c | 6 +++++- net/sunrpc/xprtsock.c | 10 ++++++---- 3 files changed, 15 insertions(+), 15 deletions(-)
net/sunrpc/xprt.c +4 -10
@@ -796,17 +796,11 @@ void xprt_connect(struct rpc_task *task)static void xprt_connect_status (struct rpc_task *task) { -struct rpc_xprt *xprt = task->tk_rqstp->rq_xprt; - -if (task->tk_status ==0 ) { - xprt->stat.connect_count++; - xprt->stat.connect_time += (long )jiffies - xprt->stat.connect_start; +switch (task->tk_status) { +case 0 :dprintk ("RPC: %5u xprt_connect_status: connection established\n" , task->tk_pid); -return ; - } - -switch (task->tk_status) { +break ;case -ECONNREFUSED :case -ECONNRESET :case -ECONNABORTED :
@@ -823,7 +817,7 @@ static void xprt_connect_status(struct rpc_task *task)default :dprintk ("RPC: %5u xprt_connect_status: error %d connecting to " "server %s\n" , task->tk_pid, -task->tk_status, - xprt->servername); + task->tk_rqstp->rq_xprt->servername); task->tk_status = -EIO ; } }
net/sunrpc/xprtrdma/transport.c +5 -1
@@ -242,8 +242,12 @@ rpcrdma_connect_worker(struct work_struct *work)spin_lock_bh (&xprt->transport_lock);if (ep->rep_connected >0 ) { -if (!xprt_test_and_set_connected (xprt)) +if (!xprt_test_and_set_connected (xprt)) { + xprt->stat.connect_count++; + xprt->stat.connect_time += (long )jiffies - + xprt->stat.connect_start;xprt_wake_pending_tasks (xprt,0 ); + } }else {if (xprt_test_and_clear_connected (xprt))xprt_wake_pending_tasks (xprt, -ENOTCONN );
net/sunrpc/xprtsock.c +6 -4
@@ -1611,6 +1611,9 @@ static void xs_tcp_state_change(struct sock *sk)clear_bit (XPRT_SOCK_CONNECTING , &transport->sock_state);xprt_clear_connecting (xprt); + xprt->stat.connect_count++; + xprt->stat.connect_time += (long )jiffies - + xprt->stat.connect_start;xprt_wake_pending_tasks (xprt, -EAGAIN ); }spin_unlock (&xprt->transport_lock);
@@ -2029,8 +2032,6 @@ static int xs_local_finish_connecting(struct rpc_xprt *xprt, }/* Tell the socket layer to start connecting... */ - xprt->stat.connect_count++; - xprt->stat.connect_start = jiffies;return kernel_connect (sock,xs_addr (xprt), xprt->addrlen,0 ); }
@@ -2062,6 +2063,9 @@ static int xs_local_setup_socket(struct sock_xprt *transport)case 0 :dprintk ("RPC: xprt %p connected to %s\n" , xprt, xprt->address_strings[RPC_DISPLAY_ADDR ]); + xprt->stat.connect_count++; + xprt->stat.connect_time += (long )jiffies - + xprt->stat.connect_start;xprt_set_connected (xprt);case -ENOBUFS :break ;
@@ -2387,8 +2391,6 @@ static int xs_tcp_finish_connecting(struct rpc_xprt *xprt, struct socket *sock)xs_set_memalloc (xprt);/* Tell the socket layer to start connecting... */ - xprt->stat.connect_count++; - xprt->stat.connect_start = jiffies;set_bit (XPRT_SOCK_CONNECTING , &transport->sock_state); ret =kernel_connect (sock,xs_addr (xprt), xprt->addrlen,O_NONBLOCK );switch (ret) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 63/220 x86/PCI: Apply VMDs AERSID fixup generically
In reply to Greg Kroah-HartmanFrom: Jon Derrick <[email protected]>
[ Upstream commit 4f475e8e0a6d4f5d430350d1f74f7e4899fb1692 ]
A root port Device ID changed between simulation and production. Rather than match Device IDs which may not be future-proof if left unmaintained, match all root ports which exist in a VMD domain.
--- arch/x86/pci/fixup.c | 12 +++--------- 1 file changed, 3 insertions(+), 9 deletions(-)
arch/x86/pci/fixup.c +3 -9
@@ -629,17 +629,11 @@ DECLARE_PCI_FIXUP_HEADER(PCI_VENDOR_ID_INTEL, 0x8c10, quirk_apple_mbp_poweroff);static void quirk_no_aersid (struct pci_dev *pdev) {/* VMD Domain */ -if (is_vmd (pdev->bus)) +if (is_vmd (pdev->bus) &&pci_is_root_bus (pdev->bus)) pdev->bus->bus_flags |=PCI_BUS_FLAGS_NO_AERSID ; } -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x2030 , quirk_no_aersid); -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x2031 , quirk_no_aersid); -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x2032 , quirk_no_aersid); -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x2033 , quirk_no_aersid); -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x334a , quirk_no_aersid); -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x334b , quirk_no_aersid); -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x334c , quirk_no_aersid); -DECLARE_PCI_FIXUP_EARLY (PCI_VENDOR_ID_INTEL ,0x334d , quirk_no_aersid); +DECLARE_PCI_FIXUP_CLASS_EARLY (PCI_VENDOR_ID_INTEL ,PCI_ANY_ID , +PCI_CLASS_BRIDGE_PCI ,8 , quirk_no_aersid);static void quirk_intel_th_dnv (struct pci_dev *dev) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 64/220 mei: samples: fix a signedness bug in amt_host_if_call()
In reply to Greg Kroah-HartmanFrom: Dan Carpenter <[email protected]>
[ Upstream commit 185647813cac080453cb73a2e034a8821049f2a7 ]
"out_buf_sz" needs to be signed for the error handling to work.
--- samples/mei/mei-amt-version.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
samples/mei/mei-amt-version.c +1 -1
@@ -370,7 +370,7 @@ static uint32_t amt_host_if_call(struct amt_host_if *acmd, unsigned int expected_sz) {uint32_t in_buf_sz; -uint32_t out_buf_sz; +ssize_t out_buf_sz;ssize_t written;uint32_t status;struct amt_host_if_resp_header *msg_hdr;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 65/220 cxgb4: Use proper enum in cxgb4_dcb_handle_fw_update
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 3b0b8f0d9a259f6a428af63e7a77547325f8e081 ]
Clang warns when one enumerated type is implicitly converted to another.
drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.c:303:7: warning: implicit conversion from enumeration type 'enum cxgb4_dcb_state' to different enumeration type 'enum cxgb4_dcb_state_input' [-Wenum-conversion]
? CXGB4_DCB_STATE_FW_ALLSYNCED
^~~~~~~~~~~~~~~~~~~~~~~~~~~~
drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.c:304:7: warning: implicit
conversion from enumeration type 'enum cxgb4_dcb_state' to different
enumeration type 'enum cxgb4_dcb_state_input' [-Wenum-conversion]
: CXGB4_DCB_STATE_FW_INCOMPLETE);
^~~~~~~~~~~~~~~~~~~~~~~~~~~~~2 warnings generated.
Use the equivalent value of the expected type to silence Clang while resulting in no functional change.
CXGB4_DCB_STATE_FW_INCOMPLETE = CXGB4_DCB_INPUT_FW_INCOMPLETE = 2 CXGB4_DCB_STATE_FW_ALLSYNCED = CXGB4_DCB_INPUT_FW_ALLSYNCED = 3
--- drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.c | 4 ++-- 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.c +2 -2
@@ -273,8 +273,8 @@ void cxgb4_dcb_handle_fw_update(struct adapter *adap,enum cxgb4_dcb_state_input input = ((pcmd->u.dcb.control.all_syncd_pkd &FW_PORT_CMD_ALL_SYNCD_F ) - ?CXGB4_DCB_STATE_FW_ALLSYNCED - :CXGB4_DCB_STATE_FW_INCOMPLETE ); + ?CXGB4_DCB_INPUT_FW_ALLSYNCED + :CXGB4_DCB_INPUT_FW_INCOMPLETE );if (dcb->dcb_version !=FW_PORT_DCB_VER_UNKNOWN ) { dcb_running_version = FW_PORT_CMD_DCB_VERSION_G(
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 66/220 cxgb4: Use proper enum in IEEE_FAUX_SYNC
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 258b6d141878530ba1f8fc44db683822389de914 ]
Clang warns when one enumerated type is implicitly converted to another.
drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.c:390:4: warning: implicit conversion from enumeration type 'enum cxgb4_dcb_state' to different enumeration type 'enum cxgb4_dcb_state_input' [-Wenum-conversion]
IEEE_FAUX_SYNC(dev, dcb);
^~~~~~~~~~~~~~~~~~~~~~~~
drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.h:70:10: note: expanded
from macro 'IEEE_FAUX_SYNC'
CXGB4_DCB_STATE_FW_ALLSYNCED);
^~~~~~~~~~~~~~~~~~~~~~~~~~~~Use the equivalent value of the expected type to silence Clang while resulting in no functional change.
CXGB4_DCB_STATE_FW_ALLSYNCED = CXGB4_DCB_INPUT_FW_ALLSYNCED = 3
--- drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.h | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/net/ethernet/chelsio/cxgb4/cxgb4_dcb.h +1 -1
@@ -67,7 +67,7 @@do { \if ((__dcb)->dcb_version ==FW_PORT_DCB_VER_IEEE ) \cxgb4_dcb_state_fsm ((__dev), \ -CXGB4_DCB_STATE_FW_ALLSYNCED ); \ +CXGB4_DCB_INPUT_FW_ALLSYNCED ); \ }while (0 )/* States we can be in for a port's Data Center Bridging.
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 67/220 powerpc/pseries: Fix DTL buffer registration
In reply to Greg Kroah-HartmanFrom: Naveen N. Rao <[email protected]>
[ Upstream commit db787af1b8a6b4be428ee2ea7d409dafcaa4a43c ]
When CONFIG_VIRT_CPU_ACCOUNTING_NATIVE is not set, we register the DTL buffer for a cpu when the associated file under powerpc/dtl in debugfs is opened. When doing so, we need to set the size of the buffer being registered in the second u32 word of the buffer. This needs to be in big endian, but we are not doing the conversion resulting in the below error showing up in dmesg:
dtl_start: DTL registration for cpu 0 (hw 0) failed with -4
Fix this in the obvious manner.
--- arch/powerpc/platforms/pseries/dtl.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
arch/powerpc/platforms/pseries/dtl.c +1 -1
@@ -149,7 +149,7 @@ static int dtl_start(struct dtl *dtl)/* Register our dtl buffer with the hypervisor. The HV expects the * buffer size to be passed in the second word of the buffer */ - ((u32 *)dtl->buf)[1 ] =DISPATCH_LOG_BYTES ; + ((u32 *)dtl->buf)[1 ] =cpu_to_be32 (DISPATCH_LOG_BYTES ); hwcpu =get_hard_smp_processor_id (dtl->cpu); addr =__pa (dtl->buf);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 68/220 powerpc/pseries: Fix how we iterate over the DTL entries
In reply to Greg Kroah-HartmanFrom: Naveen N. Rao <[email protected]>
[ Upstream commit 9258227e9dd1da8feddb07ad9702845546a581c9 ]
When CONFIG_VIRT_CPU_ACCOUNTING_NATIVE is not set, we look up dtl_idx in the lppaca to determine the number of entries in the buffer. Since lppaca is in big endian, we need to do an endian conversion before using this in our calculation to determine the number of entries in the buffer. Without this, we do not iterate over the existing entries in the DTL buffer properly.
--- arch/powerpc/platforms/pseries/dtl.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
arch/powerpc/platforms/pseries/dtl.c +1 -1
@@ -184,7 +184,7 @@ static void dtl_stop(struct dtl *dtl)static u64 dtl_current_index (struct dtl *dtl) { -return lppaca_of (dtl->cpu).dtl_idx; +return be64_to_cpu (lppaca_of (dtl->cpu).dtl_idx); }#endif /* CONFIG_VIRT_CPU_ACCOUNTING_NATIVE */
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 69/220 powerpc/xive: Move a dereference below a NULL test
In reply to Greg Kroah-HartmanFrom: zhong jiang <[email protected]>
[ Upstream commit cd5ff94577e004e0a4457e70d0ef3a030f4010b8 ]
Move the dereference of xc below the NULL test.
--- arch/powerpc/sysdev/xive/common.c | 7 ++++--- 1 file changed, 4 insertions(+), 3 deletions(-)
arch/powerpc/sysdev/xive/common.c +4 -3
@@ -1009,12 +1009,13 @@ static void xive_ipi_eoi(struct irq_data *d) {struct xive_cpu *xc =__this_cpu_read (xive_cpu); -DBG_VERBOSE ("IPI eoi: irq=%d [0x%lx] (HW IRQ 0x%x) pending=%02x\n" , - d->irq,irqd_to_hwirq (d), xc->hw_ipi, xc->pending_prio); -/* Handle possible race with unplug and drop stale IPIs */ if (!xc)return ; + +DBG_VERBOSE ("IPI eoi: irq=%d [0x%lx] (HW IRQ 0x%x) pending=%02x\n" , + d->irq,irqd_to_hwirq (d), xc->hw_ipi, xc->pending_prio); +xive_do_source_eoi (xc->hw_ipi, &xc->ipi_data);xive_do_queue_eoi (xc); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 70/220 ARM: dts: at91: sama5d4_xplained: fix addressable nand flash size
In reply to Greg Kroah-HartmanFrom: Tudor Ambarus <[email protected]>
[ Upstream commit df90fc64367ffdb6f1b5c0f0c4940d44832b0174 ]
sama5d4_xplained comes with a 4Gb NAND flash. Increase the rootfs size to match this limit.
--- arch/arm/boot/dts/at91-sama5d4_xplained.dts | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
arch/arm/boot/dts/at91-sama5d4_xplained.dts +1 -1
@@ -252,7 +252,7 @@ rootfs@800000 { label = "rootfs"; - reg = <0x800000 0x0f800000>; + reg = <0x800000 0x1f800000>; }; }; };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 71/220 ARM: dts: at91: at91sam9x5cm: fix addressable nand flash size
In reply to Greg Kroah-HartmanFrom: Tudor Ambarus <[email protected]>
[ Upstream commit 6f270d88a0c4a11725afd8fd2001ae408733afbf ]
at91sam9x5cm comes with a 2Gb NAND flash. Fix the rootfs size to match this limit.
--- arch/arm/boot/dts/at91sam9x5cm.dtsi | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
arch/arm/boot/dts/at91sam9x5cm.dtsi +1 -1
@@ -100,7 +100,7 @@ rootfs@800000 { label = "rootfs"; - reg = <0x800000 0x1f800000>; + reg = <0x800000 0x0f800000>; }; }; };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 72/220 ARM: dts: at91: sama5d2_ptc_ek: fix bootloader env offsets
In reply to Greg Kroah-HartmanFrom: Tudor Ambarus <[email protected]>
[ Upstream commit f602b4871c5f7ac01d37d8b285ca947ba7613065 ]
The offsets for the bootloader environment and its redundant partition were inverted. Fix the addresses to match our nand flash map available at:
http://www.at91.com/linux4sam/pub/Linux4SAM/SambaSubsections//demo_nandflash_map_lnx4sam5x.png
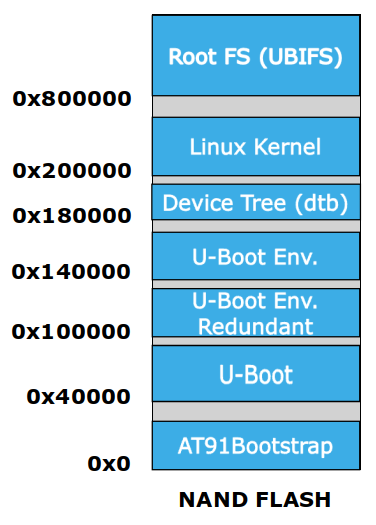
--- arch/arm/boot/dts/at91-sama5d2_ptc_ek.dts | 8 ++++---- 1 file changed, 4 insertions(+), 4 deletions(-)
arch/arm/boot/dts/at91-sama5d2_ptc_ek.dts +4 -4
@@ -92,13 +92,13 @@ reg = <0x40000 0xc0000>; }; - bootloaderenv@0x100000 { - label = "bootloader env"; + bootloaderenvred@0x100000 { + label = "bootloader env redundant"; reg = <0x100000 0x40000>; }; - bootloaderenvred@0x140000 { - label = "bootloader env redundant"; + bootloaderenv@0x140000 { + label = "bootloader env"; reg = <0x140000 0x40000>; };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 73/220 mtd: rawnand: sh_flctl: Use proper enum for flctl_dma_fifo0_transfer
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit e2bfa4ca23d9b5a7bdfcf21319fad9b59e38a05c ]
Clang warns when one enumerated type is converted implicitly to another:
drivers/mtd/nand/raw/sh_flctl.c:483:46: warning: implicit conversion from enumeration type 'enum dma_transfer_direction' to different enumeration type 'enum dma_data_direction' [-Wenum-conversion]
flctl_dma_fifo0_transfer(flctl, buf, rlen, DMA_DEV_TO_MEM) > 0) ~~~~~~~~~~~~~~~~~~~~~~~~^~~~~~~~~~~~~~drivers/mtd/nand/raw/sh_flctl.c:542:46: warning: implicit conversion from enumeration type 'enum dma_transfer_direction' to different enumeration type 'enum dma_data_direction' [-Wenum-conversion]
flctl_dma_fifo0_transfer(flctl, buf, rlen, DMA_MEM_TO_DEV) > 0) ~~~~~~~~~~~~~~~~~~~~~~~~^~~~~~~~~~~~~~
2 warnings generated.
Use the proper enums from dma_data_direction to satisfy Clang.
DMA_MEM_TO_DEV = DMA_TO_DEVICE = 1DMA_DEV_TO_MEM = DMA_FROM_DEVICE = 2
--- drivers/mtd/nand/raw/sh_flctl.c | 4 ++-- 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/mtd/nand/raw/sh_flctl.c +2 -2
@@ -480,7 +480,7 @@ static void read_fiforeg(struct sh_flctl *flctl, int rlen, int offset)/* initiate DMA transfer */ if (flctl->chan_fifo0_rx && rlen >=32 && -flctl_dma_fifo0_transfer (flctl, buf, rlen,DMA_DEV_TO_MEM ) >0 ) +flctl_dma_fifo0_transfer (flctl, buf, rlen,DMA_FROM_DEVICE ) >0 ) goto convert;/* DMA success */ /* do polling transfer */
@@ -539,7 +539,7 @@ static void write_ec_fiforeg(struct sh_flctl *flctl, int rlen,/* initiate DMA transfer */ if (flctl->chan_fifo0_tx && rlen >=32 && -flctl_dma_fifo0_transfer (flctl, buf, rlen,DMA_MEM_TO_DEV ) >0 ) +flctl_dma_fifo0_transfer (flctl, buf, rlen,DMA_TO_DEVICE ) >0 )return ;/* DMA success */ /* do polling transfer */
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 74/220 PM / hibernate: Check the success of generating md5 digest before hibernation
In reply to Greg Kroah-HartmanFrom: Chen Yu <[email protected]>
[ Upstream commit 749fa17093ff67b31dea864531a3698b6a95c26c ]
Currently if get_e820_md5() fails, then it will hibernate nevertheless. Actually the error code should be propagated to upper caller so that the hibernation could be aware of the result and terminates the process if md5 digest fails.
--- arch/x86/power/hibernate_64.c | 11 +++++------ 1 file changed, 5 insertions(+), 6 deletions(-)
arch/x86/power/hibernate_64.c +5 -6
@@ -266,9 +266,9 @@ static int get_e820_md5(struct e820_table *table, void *buf)return ret; } -static void hibernation_e820_save (void *buf) +static int hibernation_e820_save (void *buf) { -get_e820_md5 (e820_table_firmware, buf); +return get_e820_md5 (e820_table_firmware, buf); }static bool hibernation_e820_mismatch (void *buf)
@@ -288,8 +288,9 @@ static bool hibernation_e820_mismatch(void *buf) return memcmp(result, buf, MD5_DIGEST_SIZE) ? true : false; }#else -static void hibernation_e820_save (void *buf) +static int hibernation_e820_save (void *buf) { +return 0 ; }static bool hibernation_e820_mismatch (void *buf)
@@ -334,9 +335,7 @@ int arch_hibernation_header_save(void *addr, unsigned int max_size) rdr->magic =RESTORE_MAGIC ; -hibernation_e820_save (rdr->e820_digest); - -return 0 ; +return hibernation_e820_save (rdr->e820_digest); }/**
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 75/220 tools: PCI: Fix compilation warnings
In reply to Greg Kroah-HartmanFrom: Gustavo Pimentel <[email protected]>
[ Upstream commit fef31ecaaf2c5c54db85b35e893bf8abec96b93f ]
Current compilation produces the following warnings:
tools/pci/pcitest.c: In function 'run_test':tools/pci/pcitest.c:56:9: warning: unused variable 'time' [-Wunused-variable]
double time;
^~~~
tools/pci/pcitest.c:55:25: warning: unused variable 'end'
[-Wunused-variable]
struct timespec start, end;
^~~
tools/pci/pcitest.c:55:18: warning: unused variable 'start'
[-Wunused-variable]
struct timespec start, end;
^~~~~tools/pci/pcitest.c:146:1: warning: control reaches end of non-void function [-Wreturn-type]
}
^
Fix them:
- remove unused variables
- change function return from int to void, since it's not used
--- tools/pci/pcitest.c | 7 ++----- 1 file changed, 2 insertions(+), 5 deletions(-)
tools/pci/pcitest.c +2 -5
@@ -23,7 +23,6 @@#include <stdio.h> #include <stdlib.h> #include <sys/ioctl.h> -#include <time.h> #include <unistd.h> #include <linux/pcitest.h>
@@ -48,17 +47,15 @@ struct pci_test {unsigned long size; }; -static int run_test (struct pci_test *test) +static void run_test (struct pci_test *test) {long ret;int fd; -struct timespec start, end; -double time; fd =open (test->device,O_RDWR );if (fd <0 ) {perror ("can't open PCI Endpoint Test device" ); -return fd; +return ; }if (test->barnum >=0 && test->barnum <=5 ) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 76/220 clocksource/drivers/sh_cmt: Fixup for 64-bit machines
In reply to Greg Kroah-HartmanFrom: Sergei Shtylyov <[email protected]>
[ Upstream commit 22627c6f3ed3d9d0df13eec3c831b08f8186c38e ]
When trying to use CMT for clockevents on R-Car gen3 SoCs, I noticed that 'max_delta_ns' for the broadcast timer (CMT) was shown as 1000 in /proc/timer_list. It turned out that when calculating it, the driver did 1 << 32 (causing what I think was undefined behavior) resulting in a zero delta, later clamped to 1000 by cev_delta2ns(). The root cause turned out to be that the driver abused *unsigned long* for the CMT register values (which are 16/32-bit), so that the calculation of 'ch->max_match_value' in sh_cmt_setup_channel() used the wrong branch. Using more proper 'u32' instead fixed 'max_delta_ns' and even fixed the switching an active clocksource to CMT (which caused the system to turn non-interactive before).
--- drivers/clocksource/sh_cmt.c | 72 +++++++++++++++++------------------- 1 file changed, 33 insertions(+), 39 deletions(-)
drivers/clocksource/sh_cmt.c +33 -39
@@ -78,18 +78,17 @@ struct sh_cmt_info {unsigned int channels_mask;unsigned long width;/* 16 or 32 bit version of hardware block */ -unsigned long overflow_bit; -unsigned long clear_bits; +u32 overflow_bit; +u32 clear_bits;/* callbacks for CMSTR and CMCSR access */ -unsigned long (*read_control)(void __iomem *base,unsigned long offs); +u32 (*read_control)(void __iomem *base,unsigned long offs);void (*write_control)(void __iomem *base,unsigned long offs, -unsigned long value); +u32 value);/* callbacks for CMCNT and CMCOR access */ -unsigned long (*read_count)(void __iomem *base,unsigned long offs); -void (*write_count)(void __iomem *base,unsigned long offs, -unsigned long value); +u32 (*read_count)(void __iomem *base,unsigned long offs); +void (*write_count)(void __iomem *base,unsigned long offs,u32 value); };struct sh_cmt_channel {
@@ -103,9 +102,9 @@ struct sh_cmt_channel {unsigned int timer_bit;unsigned long flags; -unsigned long match_value; -unsigned long next_match_value; -unsigned long max_match_value; +u32 match_value; +u32 next_match_value; +u32 max_match_value;raw_spinlock_t lock;struct clock_event_device ced;struct clocksource cs;
@@ -160,24 +159,22 @@ struct sh_cmt_device {#define SH_CMT32_CMCSR_CKS_RCLK1 (7 << 0)#define SH_CMT32_CMCSR_CKS_MASK (7 << 0) -static unsigned long sh_cmt_read16 (void __iomem *base,unsigned long offs) +static u32 sh_cmt_read16 (void __iomem *base,unsigned long offs) {return ioread16 (base + (offs <<1 )); } -static unsigned long sh_cmt_read32 (void __iomem *base,unsigned long offs) +static u32 sh_cmt_read32 (void __iomem *base,unsigned long offs) {return ioread32 (base + (offs <<2 )); } -static void sh_cmt_write16 (void __iomem *base,unsigned long offs, -unsigned long value) +static void sh_cmt_write16 (void __iomem *base,unsigned long offs,u32 value) {iowrite16 (value, base + (offs <<1 )); } -static void sh_cmt_write32 (void __iomem *base,unsigned long offs, -unsigned long value) +static void sh_cmt_write32 (void __iomem *base,unsigned long offs,u32 value) {iowrite32 (value, base + (offs <<2 )); }
@@ -242,7 +239,7 @@ static const struct sh_cmt_info sh_cmt_info[] = {#define CMCNT 1/* channel register */ #define CMCOR 2/* channel register */ -static inline unsigned long sh_cmt_read_cmstr (struct sh_cmt_channel *ch) +static inline u32 sh_cmt_read_cmstr (struct sh_cmt_channel *ch) {if (ch->iostart)return ch->cmt->info->read_control (ch->iostart,0 );
@@ -250,8 +247,7 @@ static inline unsigned long sh_cmt_read_cmstr(struct sh_cmt_channel *ch)return ch->cmt->info->read_control (ch->cmt->mapbase,0 ); } -static inline void sh_cmt_write_cmstr (struct sh_cmt_channel *ch, -unsigned long value) +static inline void sh_cmt_write_cmstr (struct sh_cmt_channel *ch,u32 value) {if (ch->iostart) ch->cmt->info->write_control (ch->iostart,0 , value);
@@ -259,39 +255,35 @@ static inline void sh_cmt_write_cmstr(struct sh_cmt_channel *ch, ch->cmt->info->write_control (ch->cmt->mapbase,0 , value); } -static inline unsigned long sh_cmt_read_cmcsr (struct sh_cmt_channel *ch) +static inline u32 sh_cmt_read_cmcsr (struct sh_cmt_channel *ch) {return ch->cmt->info->read_control (ch->ioctrl,CMCSR ); } -static inline void sh_cmt_write_cmcsr (struct sh_cmt_channel *ch, -unsigned long value) +static inline void sh_cmt_write_cmcsr (struct sh_cmt_channel *ch,u32 value) { ch->cmt->info->write_control (ch->ioctrl,CMCSR , value); } -static inline unsigned long sh_cmt_read_cmcnt (struct sh_cmt_channel *ch) +static inline u32 sh_cmt_read_cmcnt (struct sh_cmt_channel *ch) {return ch->cmt->info->read_count (ch->ioctrl,CMCNT ); } -static inline void sh_cmt_write_cmcnt (struct sh_cmt_channel *ch, -unsigned long value) +static inline void sh_cmt_write_cmcnt (struct sh_cmt_channel *ch,u32 value) { ch->cmt->info->write_count (ch->ioctrl,CMCNT , value); } -static inline void sh_cmt_write_cmcor (struct sh_cmt_channel *ch, -unsigned long value) +static inline void sh_cmt_write_cmcor (struct sh_cmt_channel *ch,u32 value) { ch->cmt->info->write_count (ch->ioctrl,CMCOR , value); } -static unsigned long sh_cmt_get_counter (struct sh_cmt_channel *ch, -int *has_wrapped) +static u32 sh_cmt_get_counter (struct sh_cmt_channel *ch,u32 *has_wrapped) { -unsigned long v1, v2, v3; -int o1, o2; +u32 v1, v2, v3; +u32 o1, o2; o1 =sh_cmt_read_cmcsr (ch) & ch->cmt->info->overflow_bit;
@@ -311,7 +303,8 @@ static unsigned long sh_cmt_get_counter(struct sh_cmt_channel *ch,static void sh_cmt_start_stop_ch (struct sh_cmt_channel *ch,int start) { -unsigned long flags, value; +unsigned long flags; +u32 value;/* start stop register shared by multiple timer channels */ raw_spin_lock_irqsave (&ch->cmt->lock, flags);
@@ -418,11 +411,11 @@ static void sh_cmt_disable(struct sh_cmt_channel *ch)static void sh_cmt_clock_event_program_verify (struct sh_cmt_channel *ch,int absolute) { -unsigned long new_match; -unsigned long value = ch->next_match_value; -unsigned long delay =0 ; -unsigned long now =0 ; -int has_wrapped; +u32 value = ch->next_match_value; +u32 new_match; +u32 delay =0 ; +u32 now =0 ; +u32 has_wrapped; now =sh_cmt_get_counter (ch, &has_wrapped); ch->flags |=FLAG_REPROGRAM ;/* force reprogram */
@@ -619,9 +612,10 @@ static struct sh_cmt_channel *cs_to_sh_cmt(struct clocksource *cs)static u64 sh_cmt_clocksource_read (struct clocksource *cs) {struct sh_cmt_channel *ch =cs_to_sh_cmt (cs); -unsigned long flags, raw; +unsigned long flags;unsigned long value; -int has_wrapped; +u32 has_wrapped; +u32 raw;raw_spin_lock_irqsave (&ch->lock, flags); value = ch->total_cycles;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 77/220 clocksource/drivers/sh_cmt: Fix clocksource width for 32-bit machines
In reply to Greg Kroah-HartmanFrom: Sergei Shtylyov <[email protected]>
[ Upstream commit 37e7742c55ba856eaec7e35673ee370f36eb17f3 ]
The driver seems to abuse *unsigned long* not only for the (32-bit) register values but also for the 'sh_cmt_channel::total_cycles' which needs to always be 64-bit -- as a result, the clocksource's mask is needlessly clamped down to 32-bits on the 32-bit machines...
--- drivers/clocksource/sh_cmt.c | 6 +++--- 1 file changed, 3 insertions(+), 3 deletions(-)
drivers/clocksource/sh_cmt.c +3 -3
@@ -108,7 +108,7 @@ struct sh_cmt_channel {raw_spinlock_t lock;struct clock_event_device ced;struct clocksource cs; -unsigned long total_cycles; +u64 total_cycles;bool cs_enabled; };
@@ -613,8 +613,8 @@ static u64 sh_cmt_clocksource_read(struct clocksource *cs) {struct sh_cmt_channel *ch =cs_to_sh_cmt (cs);unsigned long flags; -unsigned long value;u32 has_wrapped; +u64 value;u32 raw;raw_spin_lock_irqsave (&ch->lock, flags);
@@ -688,7 +688,7 @@ static int sh_cmt_register_clocksource(struct sh_cmt_channel *ch, cs->disable = sh_cmt_clocksource_disable; cs->suspend = sh_cmt_clocksource_suspend; cs->resume = sh_cmt_clocksource_resume; - cs->mask =CLOCKSOURCE_MASK (sizeof (unsigned long ) *8 ); + cs->mask =CLOCKSOURCE_MASK (sizeof (u64) *8 ); cs->flags =CLOCK_SOURCE_IS_CONTINUOUS ; dev_info(&ch->cmt->pdev->dev, "ch%u: used as clock source\n",
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 78/220 ice: Fix forward to queue group logic
In reply to Greg Kroah-HartmanFrom: Anirudh Venkataramanan <[email protected]>
[ Upstream commit be8ff000bf83e658e63ab64cf4d2755abc5add5b ]
When adding a rule, queue region size needs to be provided as log base 2 of the number of queues in region. Fix that.
--- drivers/net/ethernet/intel/ice/ice_switch.c | 14 ++++++++++---- 1 file changed, 10 insertions(+), 4 deletions(-)
drivers/net/ethernet/intel/ice/ice_switch.c +10 -4
@@ -468,6 +468,7 @@ ice_fill_sw_rule(struct ice_hw *hw, struct ice_fltr_info *f_info,void *daddr =NULL ;u32 act =0 ;__be16 *off; +u8 q_rgn;if (opc == ice_aqc_opc_remove_sw_rules) { s_rule->pdata.lkup_tx_rx.act =0 ;
@@ -503,14 +504,19 @@ ice_fill_sw_rule(struct ice_hw *hw, struct ice_fltr_info *f_info, act |= (f_info->fwd_id.q_id <<ICE_SINGLE_ACT_Q_INDEX_S ) &ICE_SINGLE_ACT_Q_INDEX_M ;break ; +case ICE_DROP_PACKET : + act |=ICE_SINGLE_ACT_VSI_FORWARDING |ICE_SINGLE_ACT_DROP | +ICE_SINGLE_ACT_VALID_BIT ; +break ;case ICE_FWD_TO_QGRP : + q_rgn = f_info->qgrp_size >0 ? + (u8 )ilog2 (f_info->qgrp_size) :0 ; act |=ICE_SINGLE_ACT_TO_Q ; - act |= (f_info->qgrp_size <<ICE_SINGLE_ACT_Q_REGION_S ) & + act |= (f_info->fwd_id.q_id <<ICE_SINGLE_ACT_Q_INDEX_S ) & +ICE_SINGLE_ACT_Q_INDEX_M ; + act |= (q_rgn <<ICE_SINGLE_ACT_Q_REGION_S ) &ICE_SINGLE_ACT_Q_REGION_M ;break ; -case ICE_DROP_PACKET : - act |=ICE_SINGLE_ACT_VSI_FORWARDING |ICE_SINGLE_ACT_DROP ; -break ;default :return ; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 79/220 md: allow metadata updates while suspending an array - fix
In reply to Greg Kroah-HartmanFrom: NeilBrown <[email protected]>
[ Upstream commit 059421e041eb461fb2b3e81c9adaec18ef03ca3c ]
Commit 35bfc52187f6 ("md: allow metadata update while suspending.") added support for allowing md_check_recovery() to still perform metadata updates while the array is entering the 'suspended' state. This is needed to allow the processes of entering the state to complete.
Unfortunately, the patch doesn't really work. The test for "mddev->suspended" at the start of md_check_recovery() means that the function doesn't try to do anything at all while entering suspend.
This patch moves the code of updating the metadata while suspending to *before* the test on mddev->suspended.
--- drivers/md/md.c | 22 ++++++++++++---------- 1 file changed, 12 insertions(+), 10 deletions(-)
drivers/md/md.c +12 -10
@@ -8778,6 +8778,18 @@ static void md_start_sync(struct work_struct *ws)*/ void md_check_recovery (struct mddev *mddev) { +if (test_bit (MD_ALLOW_SB_UPDATE , &mddev->flags) && mddev->sb_flags) { +/* Write superblock - thread that called mddev_suspend() +* holds reconfig_mutex for us. +*/ +set_bit (MD_UPDATING_SB , &mddev->flags); +smp_mb__after_atomic (); +if (test_bit (MD_ALLOW_SB_UPDATE , &mddev->flags)) +md_update_sb (mddev,0 ); +clear_bit_unlock (MD_UPDATING_SB , &mddev->flags); +wake_up (&mddev->sb_wait); + } +if (mddev->suspended)return ;
@@ -8938,16 +8950,6 @@ void md_check_recovery(struct mddev *mddev) unlock:wake_up (&mddev->sb_wait);mddev_unlock (mddev); - }else if (test_bit (MD_ALLOW_SB_UPDATE , &mddev->flags) && mddev->sb_flags) { -/* Write superblock - thread that called mddev_suspend() -* holds reconfig_mutex for us. -*/ -set_bit (MD_UPDATING_SB , &mddev->flags); -smp_mb__after_atomic (); -if (test_bit (MD_ALLOW_SB_UPDATE , &mddev->flags)) -md_update_sb (mddev,0 ); -clear_bit_unlock (MD_UPDATING_SB , &mddev->flags); -wake_up (&mddev->sb_wait); } }EXPORT_SYMBOL (md_check_recovery);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 80/220 ixgbe: Fix ixgbe TX hangs with XDP_TX beyond queue limit
In reply to Greg Kroah-HartmanFrom: Radoslaw Tyl <[email protected]>
[ Upstream commit 8d7179b1e2d64b3493c0114916486fe92e6109a9 ]
We have Tx hang when number Tx and XDP queues are more than 64. In XDP always is MTQC == 0x0 (64TxQs). We need more space for Tx queues.
--- drivers/net/ethernet/intel/ixgbe/ixgbe_main.c | 14 ++++++++++---- 1 file changed, 10 insertions(+), 4 deletions(-)
drivers/net/ethernet/intel/ixgbe/ixgbe_main.c +10 -4
@@ -3582,12 +3582,18 @@ static void ixgbe_setup_mtqc(struct ixgbe_adapter *adapter)else mtqc |=IXGBE_MTQC_64VF ; }else { -if (tcs >4 ) +if (tcs >4 ) { mtqc =IXGBE_MTQC_RT_ENA |IXGBE_MTQC_8TC_8TQ ; -else if (tcs >1 ) + }else if (tcs >1 ) { mtqc =IXGBE_MTQC_RT_ENA |IXGBE_MTQC_4TC_4TQ ; -else - mtqc =IXGBE_MTQC_64Q_1PB ; + }else { +u8 max_txq = adapter->num_tx_queues + + adapter->num_xdp_queues; +if (max_txq >63 ) + mtqc =IXGBE_MTQC_RT_ENA |IXGBE_MTQC_4TC_4TQ ; +else + mtqc =IXGBE_MTQC_64Q_1PB ; + } }IXGBE_WRITE_REG (hw,IXGBE_MTQC , mtqc);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 81/220 i40e: Use proper enum in i40e_ndo_set_vf_link_state
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 43ade6ad18416b8fd5bb3c9e9789faa666527eec ]
Clang warns when one enumerated type is converted implicitly to another.
drivers/net/ethernet/intel/i40e/i40e_virtchnl_pf.c:4214:42: warning:
implicit conversion from enumeration type 'enum i40e_aq_link_speed' to different enumeration type 'enum virtchnl_link_speed'
[-Wenum-conversion]
pfe.event_data.link_event.link_speed = I40E_LINK_SPEED_40GB;
~ ^~~~~~~~~~~~~~~~~~~~1 warning generated.
Use the proper enum from virtchnl_link_speed, which has the same value as I40E_LINK_SPEED_40GB, VIRTCHNL_LINK_SPEED_40GB. This appears to be missed by commit ff3f4cc267f6 ("virtchnl: finish conversion to virtchnl interface").
--- drivers/net/ethernet/intel/i40e/i40e_virtchnl_pf.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/net/ethernet/intel/i40e/i40e_virtchnl_pf.c +1 -1
@@ -4211,7 +4211,7 @@ int i40e_ndo_set_vf_link_state(struct net_device *netdev, int vf_id, int link) vf->link_forced = true; vf->link_up = true; pfe.event_data.link_event.link_status = true; - pfe.event_data.link_event.link_speed =I40E_LINK_SPEED_40GB ; + pfe.event_data.link_event.link_speed =VIRTCHNL_LINK_SPEED_40GB ;break ;case IFLA_VF_LINK_STATE_DISABLE : vf->link_forced = true;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 82/220 ixgbe: Fix crash with VFs and flow director on interface flap
In reply to Greg Kroah-HartmanFrom: Radoslaw Tyl <[email protected]>
[ Upstream commit 5d826d209164b0752c883607be4cdbbcf7cab494 ]
This patch fix crash when we have restore flow director filters after reset adapter. In ixgbe_fdir_filter_restore() filter->action is outside of the rx_ring array, as it has a VF identifier in the upper 32 bits.
--- drivers/net/ethernet/intel/ixgbe/ixgbe_main.c | 10 ++++++++-- 1 file changed, 8 insertions(+), 2 deletions(-)
drivers/net/ethernet/intel/ixgbe/ixgbe_main.c +8 -2
@@ -5187,6 +5187,7 @@ static void ixgbe_fdir_filter_restore(struct ixgbe_adapter *adapter)struct ixgbe_hw *hw = &adapter->hw;struct hlist_node *node2;struct ixgbe_fdir_filter *filter; +u64 action;spin_lock (&adapter->fdir_perfect_lock);
@@ -5195,12 +5196,17 @@ static void ixgbe_fdir_filter_restore(struct ixgbe_adapter *adapter)hlist_for_each_entry_safe (filter, node2, &adapter->fdir_filter_list, fdir_node) { + action = filter->action; +if (action !=IXGBE_FDIR_DROP_QUEUE && action !=0 ) + action = + (action >>ETHTOOL_RX_FLOW_SPEC_RING_VF_OFF ) -1 ; +ixgbe_fdir_write_perfect_filter_82599 (hw, &filter->filter, filter->sw_idx, - (filter->action ==IXGBE_FDIR_DROP_QUEUE ) ? + (action ==IXGBE_FDIR_DROP_QUEUE ) ?IXGBE_FDIR_DROP_QUEUE : - adapter->rx_ring[filter->action]->reg_idx); + adapter->rx_ring[action]->reg_idx); }spin_unlock (&adapter->fdir_perfect_lock);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 83/220 IB/mthca: Fix error return code in __mthca_init_one()
In reply to Greg Kroah-HartmanFrom: Wei Yongjun <[email protected]>
[ Upstream commit 39f2495618c5e980d2873ea3f2d1877dd253e07a ]
Fix to return a negative error code from the mthca_cmd_init() error handling case instead of 0, as done elsewhere in this function.
--- drivers/infiniband/hw/mthca/mthca_main.c | 3 ++- 1 file changed, 2 insertions(+), 1 deletion(-)
drivers/infiniband/hw/mthca/mthca_main.c +2 -1
@@ -986,7 +986,8 @@ static int __mthca_init_one(struct pci_dev *pdev, int hca_type) goto err_free_dev; } -if (mthca_cmd_init (mdev)) { + err =mthca_cmd_init (mdev); +if (err) {mthca_err (mdev,"Failed to init command interface, aborting.\n" ); goto err_free_dev; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 84/220 IB/rxe: avoid srq memory leak
In reply to Greg Kroah-HartmanFrom: Zhu Yanjun <[email protected]>
[ Upstream commit aae0484e15f062ad2c2502e68e15dfb8b8f84608 ]
In rxe_queue_init, q and q->buf are allocated. In do_mmap_info, q->ip is allocated. When error occurs, rxe_srq_from_init and the later error handler do not free these allocated memories. This will make memory leak.
--- drivers/infiniband/sw/rxe/rxe_srq.c | 10 ++++++++-- 1 file changed, 8 insertions(+), 2 deletions(-)
drivers/infiniband/sw/rxe/rxe_srq.c +8 -2
@@ -31,6 +31,7 @@* SOFTWARE. */ +#include <linux/vmalloc.h> #include "rxe.h" #include "rxe_loc.h" #include "rxe_queue.h"
@@ -129,13 +130,18 @@ int rxe_srq_from_init(struct rxe_dev *rxe, struct rxe_srq *srq, err =do_mmap_info (rxe, uresp ? &uresp->mi :NULL , context, q->buf, q->buf_size, &q->ip); -if (err) +if (err) { +vfree (q->buf); +kfree (q);return err; + }if (uresp) {if (copy_to_user (&uresp->srq_num, &srq->srq_num, -sizeof (uresp->srq_num))) +sizeof (uresp->srq_num))) { +rxe_queue_cleanup (q);return -EFAULT ; + } }return 0 ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 85/220 RDMA/hns: Bugfix for reserved qp number
In reply to Greg Kroah-HartmanFrom: Lijun Ou <[email protected]>
[ Upstream commit 06ef0ee4b569101f3a07ce08335dbf29fd1404ef ]
It needs to include two special qps for every port. The hip08 have four ports and the all reserved qp numbers are eight.
--- drivers/infiniband/hw/hns/hns_roce_device.h | 1 + drivers/infiniband/hw/hns/hns_roce_hw_v2.c | 1 + drivers/infiniband/hw/hns/hns_roce_hw_v2.h | 1 + drivers/infiniband/hw/hns/hns_roce_qp.c | 10 ++++++++-- 4 files changed, 11 insertions(+), 2 deletions(-)
drivers/infiniband/hw/hns/hns_roce_device.h +1 -0
@@ -666,6 +666,7 @@ struct hns_roce_caps {u32 max_sq_inline;/* 32 */ u32 max_rq_sg;/* 2 */ int num_qps;/* 256k */ +int reserved_qps;u32 max_wqes;/* 16k */ u32 max_sq_desc_sz;/* 64 */ u32 max_rq_desc_sz;/* 64 */
drivers/infiniband/hw/hns/hns_roce_hw_v2.c +1 -0
@@ -1222,6 +1222,7 @@ static int hns_roce_v2_profile(struct hns_roce_dev *hr_dev) caps->reserved_mrws =1 ; caps->reserved_uars =0 ; caps->reserved_cqs =0 ; + caps->reserved_qps =HNS_ROCE_V2_RSV_QPS ; caps->qpc_ba_pg_sz =0 ; caps->qpc_buf_pg_sz =0 ;
drivers/infiniband/hw/hns/hns_roce_hw_v2.h +1 -0
@@ -78,6 +78,7 @@#define HNS_ROCE_INVALID_LKEY 0x100#define HNS_ROCE_CMQ_TX_TIMEOUT 30000#define HNS_ROCE_V2_UC_RC_SGE_NUM_IN_WQE 2 +#define HNS_ROCE_V2_RSV_QPS 8#define HNS_ROCE_CONTEXT_HOP_NUM 1#define HNS_ROCE_MTT_HOP_NUM 1
drivers/infiniband/hw/hns/hns_roce_qp.c +8 -2
@@ -1106,14 +1106,20 @@ int hns_roce_init_qp_table(struct hns_roce_dev *hr_dev) {struct hns_roce_qp_table *qp_table = &hr_dev->qp_table;int reserved_from_top =0 ; +int reserved_from_bot;int ret;spin_lock_init (&qp_table->lock);INIT_RADIX_TREE (&hr_dev->qp_table_tree,GFP_ATOMIC ); -/* A port include two SQP, six port total 12 */ +/* In hw v1, a port include two SQP, six ports total 12 */ +if (hr_dev->caps.max_sq_sg <=2 ) + reserved_from_bot =SQP_NUM ; +else + reserved_from_bot = hr_dev->caps.reserved_qps; + ret =hns_roce_bitmap_init (&qp_table->bitmap, hr_dev->caps.num_qps, - hr_dev->caps.num_qps -1 ,SQP_NUM , + hr_dev->caps.num_qps -1 , reserved_from_bot, reserved_from_top);if (ret) { dev_err(hr_dev->dev, "qp bitmap init failed!error=%d\n",
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 86/220 RDMA/hns: Submit bad wr when post send wr exception
In reply to Greg Kroah-HartmanFrom: Lijun Ou <[email protected]>
[ Upstream commit c80e066100b5fed722c8da67c1bd2312e7bcf129 ]
When user issues a RDMA read and enables sq inline, it needs to report a bad wr to user.
--- drivers/infiniband/hw/hns/hns_roce_hw_v2.c | 1 + 1 file changed, 1 insertion(+)
drivers/infiniband/hw/hns/hns_roce_hw_v2.c +1 -0
@@ -121,6 +121,7 @@ static int set_rwqe_data_seg(struct ib_qp *ibqp, const struct ib_send_wr *wr, }if (wr->opcode ==IB_WR_RDMA_READ ) { + *bad_wr = wr;dev_err (hr_dev->dev,"Not support inline data!\n" );return -EINVAL ; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 87/220 RDMA/hns: Bugfix for CM test
In reply to Greg Kroah-HartmanFrom: Lijun Ou <[email protected]>
[ Upstream commit 15fc056fba7b17b9abfbe80a12f188403fc949fb ]
It will print the warning when the MSB bit of SLID is not zero running cm_req_handler function that test CM. It needs to fixed zero when test RoCE device.
--- drivers/infiniband/hw/hns/hns_roce_hw_v2.c | 1 + 1 file changed, 1 insertion(+)
drivers/infiniband/hw/hns/hns_roce_hw_v2.c +1 -0
@@ -2268,6 +2268,7 @@ static int hns_roce_v2_poll_one(struct hns_roce_cq *hr_cq, wc->src_qp = (u8 )roce_get_field (cqe->byte_32,V2_CQE_BYTE_32_RMT_QPN_M ,V2_CQE_BYTE_32_RMT_QPN_S ); + wc->slid =0 ; wc->wc_flags |= (roce_get_bit (cqe->byte_32,V2_CQE_BYTE_32_GRH_S ) ?IB_WC_GRH :0 );
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 88/220 RDMA/hns: Limit the size of extend sge of sq
In reply to Greg Kroah-HartmanFrom: Lijun Ou <[email protected]>
[ Upstream commit 05ad5482a5904c416bcfd74afd7193e206e563ce ]
The hip08 split two hardware version. The version id are 0x20 and 0x21 according to the PCI revison. The max size of extend sge of sq is limited to 2M for 0x20 version and 8M for 0x21 version. It may be exceeded to 2M according to the algorithm that compute the product of wqe count and extend sge number of every wqe. But the product always less than 8M.
--- drivers/infiniband/hw/hns/hns_roce_device.h | 1 + drivers/infiniband/hw/hns/hns_roce_hw_v2.c | 1 + drivers/infiniband/hw/hns/hns_roce_hw_v2.h | 1 + drivers/infiniband/hw/hns/hns_roce_qp.c | 19 +++++++++++++++++++ 4 files changed, 22 insertions(+)
drivers/infiniband/hw/hns/hns_roce_device.h +1 -0
@@ -665,6 +665,7 @@ struct hns_roce_caps {u32 max_sq_sg;/* 2 */ u32 max_sq_inline;/* 32 */ u32 max_rq_sg;/* 2 */ +u32 max_extend_sg;int num_qps;/* 256k */ int reserved_qps;u32 max_wqes;/* 16k */
drivers/infiniband/hw/hns/hns_roce_hw_v2.c +1 -0
@@ -1194,6 +1194,7 @@ static int hns_roce_v2_profile(struct hns_roce_dev *hr_dev) caps->num_cqs =HNS_ROCE_V2_MAX_CQ_NUM ; caps->max_cqes =HNS_ROCE_V2_MAX_CQE_NUM ; caps->max_sq_sg =HNS_ROCE_V2_MAX_SQ_SGE_NUM ; + caps->max_extend_sg =HNS_ROCE_V2_MAX_EXTEND_SGE_NUM ; caps->max_rq_sg =HNS_ROCE_V2_MAX_RQ_SGE_NUM ; caps->max_sq_inline =HNS_ROCE_V2_MAX_SQ_INLINE ; caps->num_uars =HNS_ROCE_V2_UAR_NUM ;
drivers/infiniband/hw/hns/hns_roce_hw_v2.h +1 -0
@@ -50,6 +50,7 @@#define HNS_ROCE_V2_MAX_CQE_NUM 0x10000#define HNS_ROCE_V2_MAX_RQ_SGE_NUM 0x100#define HNS_ROCE_V2_MAX_SQ_SGE_NUM 0xff +#define HNS_ROCE_V2_MAX_EXTEND_SGE_NUM 0x200000#define HNS_ROCE_V2_MAX_SQ_INLINE 0x20#define HNS_ROCE_V2_UAR_NUM 256#define HNS_ROCE_V2_PHY_UAR_NUM 1
drivers/infiniband/hw/hns/hns_roce_qp.c +19 -0
@@ -31,6 +31,7 @@* SOFTWARE. */ +#include <linux/pci.h> #include <linux/platform_device.h> #include <rdma/ib_addr.h> #include <rdma/ib_umem.h>
@@ -372,6 +373,16 @@ static int hns_roce_set_user_sq_size(struct hns_roce_dev *hr_dev,if (hr_qp->sq.max_gs >2 ) hr_qp->sge.sge_cnt =roundup_pow_of_two (hr_qp->sq.wqe_cnt * (hr_qp->sq.max_gs -2 )); + +if ((hr_qp->sq.max_gs >2 ) && (hr_dev->pci_dev->revision ==0x20 )) { +if (hr_qp->sge.sge_cnt > hr_dev->caps.max_extend_sg) { +dev_err (hr_dev->dev, +"The extended sge cnt error! sge_cnt=%d\n" , + hr_qp->sge.sge_cnt); +return -EINVAL ; + } + } + hr_qp->sge.sge_shift =4 ;/* Get buf size, SQ and RQ are aligned to page_szie */
@@ -465,6 +476,14 @@ static int hns_roce_set_kernel_sq_size(struct hns_roce_dev *hr_dev, hr_qp->sge.sge_shift =4 ; } +if ((hr_qp->sq.max_gs >2 ) && hr_dev->pci_dev->revision ==0x20 ) { +if (hr_qp->sge.sge_cnt > hr_dev->caps.max_extend_sg) { +dev_err (dev,"The extended sge cnt error! sge_cnt=%d\n" , + hr_qp->sge.sge_cnt); +return -EINVAL ; + } + } +/* Get buf size, SQ and RQ are aligned to PAGE_SIZE */ page_size =1 << (hr_dev->caps.mtt_buf_pg_sz +PAGE_SHIFT ); hr_qp->sq.offset =0 ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 89/220 IB/mlx4: Avoid implicit enumerated type conversion
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit b56511c15713ba6c7572e77a41f7ddba9c1053ec ]
Clang warns when one enumerated type is implicitly converted to another.
drivers/infiniband/hw/mlx4/mad.c:1811:41: warning: implicit conversion from enumeration type 'enum mlx4_ib_qp_flags' to different enumeration type 'enum ib_qp_create_flags' [-Wenum-conversion]
qp_init_attr.init_attr.create_flags = MLX4_IB_SRIOV_TUNNEL_QP;
~ ^~~~~~~~~~~~~~~~~~~~~~~drivers/infiniband/hw/mlx4/mad.c:1819:41: warning: implicit conversion from enumeration type 'enum mlx4_ib_qp_flags' to different enumeration type 'enum ib_qp_create_flags' [-Wenum-conversion]
qp_init_attr.init_attr.create_flags = MLX4_IB_SRIOV_SQP;
~ ^~~~~~~~~~~~~~~~~The type mlx4_ib_qp_flags explicitly provides supplemental values to the type ib_qp_create_flags. Make that clear to Clang by changing the create_flags type to u32.
--- include/rdma/ib_verbs.h | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
include/rdma/ib_verbs.h +1 -1
@@ -1147,7 +1147,7 @@ struct ib_qp_init_attr {struct ib_qp_cap cap;enum ib_sig_type sq_sig_type;enum ib_qp_type qp_type; -enum ib_qp_create_flags create_flags; +u32 create_flags;/* * Only needed for special QP types, or when using the RW API.
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 90/220 rpmsg: glink: smem: Support rx peak for size less than 4 bytes
In reply to Greg Kroah-HartmanFrom: Arun Kumar Neelakantam <[email protected]>
[ Upstream commit 928002a5e9dab2ddc1a0fe3e00739e89be30dc6b ]
The current rx peak function fails to read the data if size is less than 4bytes.
Use memcpy_fromio to support data reads of size less than 4 bytes.
--- drivers/rpmsg/qcom_glink_smem.c | 12 ++++-------- 1 file changed, 4 insertions(+), 8 deletions(-)
drivers/rpmsg/qcom_glink_smem.c +4 -8
@@ -89,15 +89,11 @@ static void glink_smem_rx_peak(struct qcom_glink_pipe *np, tail -= pipe->native.length; len =min_t (size_t, count, pipe->native.length - tail); -if (len) { -__ioread32_copy (data, pipe->fifo + tail, - len /sizeof (u32)); - } +if (len) +memcpy_fromio (data, pipe->fifo + tail, len); -if (len != count) { -__ioread32_copy (data + len, pipe->fifo, - (count - len) /sizeof (u32)); - } +if (len != count) +memcpy_fromio (data + len, pipe->fifo, (count - len)); } static void glink_smem_rx_advance(struct qcom_glink_pipe *np,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 91/220 msm/gpu/a6xx: Force of_dma_configure to setup DMA for GMU
In reply to Greg Kroah-HartmanFrom: Jordan Crouse <[email protected]>
[ Upstream commit 32aa27e15c28d3898ed6f9b3c98f95f34a81eab2 ]
The point of the 'force_dma' parameter for of_dma_configure is to force the device to be set up even if DMA capability is not described by the firmware which is exactly the use case
we have for GMU - we need SMMU to get set up but we have no
other dma capabilities since memory is managed by the GPU driver. Currently we pass false so of_dma_configure() fails and subsequently GMU and GPU probe does as well.
--- drivers/gpu/drm/msm/adreno/a6xx_gmu.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/gpu/drm/msm/adreno/a6xx_gmu.c +1 -1
@@ -1140,7 +1140,7 @@ int a6xx_gmu_probe(struct a6xx_gpu *a6xx_gpu, struct device_node *node) gmu->dev = &pdev->dev; -of_dma_configure (gmu->dev, node, false); +of_dma_configure (gmu->dev, node, true);/* Fow now, don't do anything fancy until we get our feet under us */ gmu->idle_level =GMU_IDLE_STATE_ACTIVE ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 92/220 OPP: Return error on error from dev_pm_opp_get_opp_count()
In reply to Greg Kroah-HartmanFrom: Viresh Kumar <[email protected]>
[ Upstream commit 09f662f95306f3e3d47ab6842bc4b0bb868a80ad ]
Return error number instead of 0 on failures.
--- drivers/opp/core.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/opp/core.c +1 -1
@@ -313,7 +313,7 @@ int dev_pm_opp_get_opp_count(struct device *dev) count =PTR_ERR (opp_table);dev_dbg (dev,"%s: OPP table not found (%d)\n" , __func__, count); -return 0 ; +return count; } count =_get_opp_count (opp_table);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 93/220 ACPICA: Never run _REG on system_memory and system_IO
In reply to Greg Kroah-HartmanFrom: Bob Moore <[email protected]>
[ Upstream commit 8b1cafdcb4b75c5027c52f1e82b47ebe727ad7ed ]
These address spaces are defined by the ACPI spec to be "always available", and thus _REG should never be run on them. Provides compatibility with other ACPI implementations.
--- drivers/acpi/acpica/acevents.h | 2 ++ drivers/acpi/acpica/aclocal.h | 2 +- drivers/acpi/acpica/evregion.c | 17 +++++++++++++++-- drivers/acpi/acpica/evrgnini.c | 6 +----- drivers/acpi/acpica/evxfregn.c | 1 - 5 files changed, 19 insertions(+), 9 deletions(-)
drivers/acpi/acpica/acevents.h +2 -0
@@ -230,6 +230,8 @@ acpi_ev_default_region_setup(acpi_handle handle,acpi_status acpi_ev_initialize_region (union acpi_operand_object *region_obj); +u8 acpi_ev_is_pci_root_bridge (struct acpi_namespace_node *node); +/* * evsci - SCI (System Control Interrupt) handling/dispatch */
drivers/acpi/acpica/aclocal.h +1 -1
@@ -395,9 +395,9 @@ struct acpi_simple_repair_info {/* Info for running the _REG methods */ struct acpi_reg_walk_info { -acpi_adr_space_type space_id;u32 function;u32 reg_run_count; +acpi_adr_space_type space_id; };/*****************************************************************************
drivers/acpi/acpica/evregion.c +15 -2
@@ -653,6 +653,19 @@ acpi_ev_execute_reg_methods(struct acpi_namespace_node *node,ACPI_FUNCTION_TRACE (ev_execute_reg_methods); +/* +* These address spaces do not need a call to _REG, since the ACPI +* specification defines them as: "must always be accessible". Since +* they never change state (never become unavailable), no need to ever +* call _REG on them. Also, a data_table is not a "real" address space, +* so do not call _REG. September 2018. +*/ +if ((space_id ==ACPI_ADR_SPACE_SYSTEM_MEMORY ) || + (space_id ==ACPI_ADR_SPACE_SYSTEM_IO ) || + (space_id ==ACPI_ADR_SPACE_DATA_TABLE )) { + return_VOID; + } + info.space_id = space_id; info.function = function; info.reg_run_count =0 ;
@@ -714,8 +727,8 @@ acpi_ev_reg_run(acpi_handle obj_handle, }/* -* We only care about regions.and objects that are allowed to have address -* space handlers +* We only care about regions and objects that are allowed to have +* address space handlers */ if ((node->type !=ACPI_TYPE_REGION ) && (node != acpi_gbl_root_node)) {return (AE_OK );
drivers/acpi/acpica/evrgnini.c +1 -5
@@ -16,9 +16,6 @@#define _COMPONENT ACPI_EVENTSACPI_MODULE_NAME ("evrgnini" ) -/* Local prototypes */ -static u8 acpi_ev_is_pci_root_bridge (struct acpi_namespace_node *node); -/******************************************************************************* * * FUNCTION: acpi_ev_system_memory_region_setup
@@ -33,7 +30,6 @@ static u8 acpi_ev_is_pci_root_bridge(struct acpi_namespace_node *node);* DESCRIPTION: Setup a system_memory operation region * ******************************************************************************/ - acpi_status acpi_ev_system_memory_region_setup(acpi_handle handle, u32 function,
@@ -313,7 +309,7 @@ acpi_ev_pci_config_region_setup(acpi_handle handle,* ******************************************************************************/ -static u8 acpi_ev_is_pci_root_bridge (struct acpi_namespace_node *node) +u8 acpi_ev_is_pci_root_bridge (struct acpi_namespace_node *node) {acpi_status status;struct acpi_pnp_device_id *hid;
drivers/acpi/acpica/evxfregn.c +0 -1
@@ -193,7 +193,6 @@ acpi_remove_address_space_handler(acpi_handle device,*/ region_obj = handler_obj->address_space.region_list; - }/* Remove this Handler object from the list */
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 94/220 cpuidle: menu: Fix wakeup statistics updates for polling state
In reply to Greg Kroah-HartmanFrom: Rafael J. Wysocki <[email protected]>
[ Upstream commit 5f26bdceb9c0a5e6c696aa2899d077cd3ae93413 ]
If the CPU exits the "polling" state due to the time limit in the loop in poll_idle(), this is not a real wakeup and it just means that the "polling" state selection was not adequate. The governor mispredicted short idle duration, but had a more suitable state been selected, the CPU might have spent more time in it. In fact, there is no reason to expect that there would have been a wakeup event earlier than the next timer in that case.
Handling such cases as regular wakeups in menu_update() may cause the menu governor to make suboptimal decisions going forward, but ignoring them altogether would not be correct either, because every time menu_select() is invoked, it makes a separate new attempt to predict the idle duration taking distinct time to the closest timer event as input and the outcomes of all those attempts should be recorded.
For this reason, make menu_update() always assume that if the "polling" state was exited due to the time limit, the next proper wakeup event for the CPU would be the next timer event (not including the tick).
--- drivers/cpuidle/governors/menu.c | 10 ++++++++++ drivers/cpuidle/poll_state.c | 6 +++++- include/linux/cpuidle.h | 1 + 3 files changed, 16 insertions(+), 1 deletion(-)
drivers/cpuidle/governors/menu.c +10 -0
@@ -512,6 +512,16 @@ static void menu_update(struct cpuidle_driver *drv, struct cpuidle_device *dev)* duration predictor do a better job next time. */ measured_us =9 *MAX_INTERESTING /10 ; + }else if ((drv->states[last_idx].flags &CPUIDLE_FLAG_POLLING ) && + dev->poll_time_limit) { +/* +* The CPU exited the "polling" state due to a time limit, so +* the idle duration prediction leading to the selection of that +* state was inaccurate. If a better prediction had been made, +* the CPU might have been woken up from idle by the next timer. +* Assume that to be the case. +*/ + measured_us = data->next_timer_us; }else {/* measured value */ measured_us =cpuidle_get_last_residency (dev);
drivers/cpuidle/poll_state.c +5 -1
@@ -17,6 +17,8 @@ static int __cpuidle poll_idle(struct cpuidle_device *dev, {u64 time_start =local_clock (); + dev->poll_time_limit = false; +local_irq_enable ();if (!current_set_polling_and_test ()) {unsigned int loop_count =0 ;
@@ -27,8 +29,10 @@ static int __cpuidle poll_idle(struct cpuidle_device *dev,continue ; loop_count =0 ; -if (local_clock () - time_start >POLL_IDLE_TIME_LIMIT ) +if (local_clock () - time_start >POLL_IDLE_TIME_LIMIT ) { + dev->poll_time_limit = true;break ; + } } }current_clr_polling ();
include/linux/cpuidle.h +1 -0
@@ -81,6 +81,7 @@ struct cpuidle_device { unsigned int registered:1; unsigned int enabled:1; unsigned int use_deepest_state:1; + unsigned int poll_time_limit:1;unsigned int cpu;int last_residency;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 95/220 ASoC: qdsp6: q6asm-dai: checking NULL vs IS_ERR()
In reply to Greg Kroah-HartmanFrom: Dan Carpenter <[email protected]>
[ Upstream commit 8e9f7265eda9f3a662ca1ca47a69042a7840735b ]
The q6asm_audio_client_alloc() doesn't return NULL, it returns error pointers.
--- sound/soc/qcom/qdsp6/q6asm-dai.c | 5 +++-- 1 file changed, 3 insertions(+), 2 deletions(-)
sound/soc/qcom/qdsp6/q6asm-dai.c +3 -2
@@ -319,10 +319,11 @@ static int q6asm_dai_open(struct snd_pcm_substream *substream) prtd->audio_client =q6asm_audio_client_alloc (dev, (q6asm_cb )event_handler, prtd, stream_id,LEGACY_PCM_MODE ); -if (!prtd->audio_client) { +if (IS_ERR (prtd->audio_client)) {pr_info ("%s: Could not allocate memory\n" , __func__); + ret =PTR_ERR (prtd->audio_client);kfree (prtd); -return -ENOMEM ; +return ret; }if (substream->stream ==SNDRV_PCM_STREAM_PLAYBACK )
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 96/220 powerpc/time: Use clockevents_register_device(), fixing an issue with large decrementer
In reply to Greg Kroah-HartmanFrom: Anton Blanchard <[email protected]>
[ Upstream commit 8b78fdb045de60a4eb35460092bbd3cffa925353 ]
We currently cap the decrementer clockevent at 4 seconds, even on systems with large decrementer support. Fix this by converting the code to use clockevents_register_device() which calculates the upper bound based on the max_delta passed in.
--- arch/powerpc/kernel/time.c | 17 +++-------------- 1 file changed, 3 insertions(+), 14 deletions(-)
arch/powerpc/kernel/time.c +3 -14
@@ -984,10 +984,10 @@ static void register_decrementer_clockevent(int cpu) *dec = decrementer_clockevent; dec->cpumask =cpumask_of (cpu); +clockevents_config_and_register (dec, ppc_tb_freq,2 , decrementer_max); +printk_once (KERN_DEBUG "clockevent: %s mult[%x] shift[%d] cpu[%d]\n" , dec->name, dec->mult, dec->shift, cpu); - -clockevents_register_device (dec); }static void enable_large_decrementer (void )
@@ -1035,18 +1035,7 @@ static void __init set_decrementer_max(void)static void __init init_decrementer_clockevent (void ) { -int cpu =smp_processor_id (); - -clockevents_calc_mult_shift (&decrementer_clockevent, ppc_tb_freq,4 ); - - decrementer_clockevent.max_delta_ns = -clockevent_delta2ns (decrementer_max, &decrementer_clockevent); - decrementer_clockevent.max_delta_ticks = decrementer_max; - decrementer_clockevent.min_delta_ns = -clockevent_delta2ns (2 , &decrementer_clockevent); - decrementer_clockevent.min_delta_ticks =2 ; - -register_decrementer_clockevent (cpu); +register_decrementer_clockevent (smp_processor_id ()); }void secondary_cpu_time_init (void )
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 97/220 powerpc/64s/radix: Explicitly flush ERAT with local LPID invalidation
In reply to Greg Kroah-HartmanFrom: Nicholas Piggin <[email protected]>
[ Upstream commit 053c5a753e951c5dd1729af2cf4d8107f2e6e09b ]
Local radix TLB flush operations that operate on congruence classes have explicit ERAT flushes for POWER9. The process scoped LPID flush did not have a flush, so add it.
--- arch/powerpc/mm/tlb-radix.c | 1 + 1 file changed, 1 insertion(+)
arch/powerpc/mm/tlb-radix.c +1 -0
@@ -429,6 +429,7 @@ static inline void _tlbiel_lpid_guest(unsigned long lpid, unsigned long ric)__tlbiel_lpid_guest (lpid, set,RIC_FLUSH_TLB ); asmvolatile ("ptesync" : : :"memory" ); + asm volatile(PPC_INVALIDATE_ERAT : : :"memory"); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 98/220 ata: ep93xx: Use proper enums for directions
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 6adde4a36f1b6a562a1057fbb1065007851050e7 ]
Clang warns when one enumerated type is implicitly converted to another.
drivers/ata/pata_ep93xx.c:662:36: warning: implicit conversion from enumeration type 'enum dma_data_direction' to different enumeration type 'enum dma_transfer_direction' [-Wenum-conversion]
drv_data->dma_rx_data.direction = DMA_FROM_DEVICE;
~ ^~~~~~~~~~~~~~~
drivers/ata/pata_ep93xx.c:670:36: warning: implicit conversion from
enumeration type 'enum dma_data_direction' to different enumeration type
'enum dma_transfer_direction' [-Wenum-conversion]
drv_data->dma_tx_data.direction = DMA_TO_DEVICE;
~ ^~~~~~~~~~~~~
drivers/ata/pata_ep93xx.c:681:19: warning: implicit conversion from
enumeration type 'enum dma_data_direction' to different enumeration type
'enum dma_transfer_direction' [-Wenum-conversion]
conf.direction = DMA_FROM_DEVICE;
~ ^~~~~~~~~~~~~~~
drivers/ata/pata_ep93xx.c:692:19: warning: implicit conversion from
enumeration type 'enum dma_data_direction' to different enumeration type
'enum dma_transfer_direction' [-Wenum-conversion]
conf.direction = DMA_TO_DEVICE;
~ ^~~~~~~~~~~~~Use the equivalent valued enums from the expected type so that Clang no longer warns about a conversion.
DMA_TO_DEVICE = DMA_MEM_TO_DEV = 1DMA_FROM_DEVICE = DMA_DEV_TO_MEM = 2
--- drivers/ata/pata_ep93xx.c | 8 ++++---- 1 file changed, 4 insertions(+), 4 deletions(-)
drivers/ata/pata_ep93xx.c +4 -4
@@ -659,7 +659,7 @@ static void ep93xx_pata_dma_init(struct ep93xx_pata_data *drv_data)* start of new transfer. */ drv_data->dma_rx_data.port =EP93XX_DMA_IDE ; - drv_data->dma_rx_data.direction =DMA_FROM_DEVICE ; + drv_data->dma_rx_data.direction =DMA_DEV_TO_MEM ; drv_data->dma_rx_data.name ="ep93xx-pata-rx" ; drv_data->dma_rx_channel =dma_request_channel (mask, ep93xx_pata_dma_filter, &drv_data->dma_rx_data);
@@ -667,7 +667,7 @@ static void ep93xx_pata_dma_init(struct ep93xx_pata_data *drv_data)return ; drv_data->dma_tx_data.port =EP93XX_DMA_IDE ; - drv_data->dma_tx_data.direction =DMA_TO_DEVICE ; + drv_data->dma_tx_data.direction =DMA_MEM_TO_DEV ; drv_data->dma_tx_data.name ="ep93xx-pata-tx" ; drv_data->dma_tx_channel =dma_request_channel (mask, ep93xx_pata_dma_filter, &drv_data->dma_tx_data);
@@ -678,7 +678,7 @@ static void ep93xx_pata_dma_init(struct ep93xx_pata_data *drv_data)/* Configure receive channel direction and source address */ memset (&conf,0 ,sizeof (conf)); - conf.direction =DMA_FROM_DEVICE ; + conf.direction =DMA_DEV_TO_MEM ; conf.src_addr = drv_data->udma_in_phys; conf.src_addr_width =DMA_SLAVE_BUSWIDTH_4_BYTES ;if (dmaengine_slave_config (drv_data->dma_rx_channel, &conf)) {
@@ -689,7 +689,7 @@ static void ep93xx_pata_dma_init(struct ep93xx_pata_data *drv_data)/* Configure transmit channel direction and destination address */ memset (&conf,0 ,sizeof (conf)); - conf.direction =DMA_TO_DEVICE ; + conf.direction =DMA_MEM_TO_DEV ; conf.dst_addr = drv_data->udma_out_phys; conf.dst_addr_width =DMA_SLAVE_BUSWIDTH_4_BYTES ;if (dmaengine_slave_config (drv_data->dma_tx_channel, &conf)) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 99/220 qed: Avoid implicit enum conversion in qed_ooo_submit_tx_buffers
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 8fa74e3c49204bdf788d99ef71840490cccc210d ]
Clang warns when one enumerated type is implicitly converted to another.
drivers/net/ethernet/qlogic/qed/qed_ll2.c:799:32: warning: implicit conversion from enumeration type 'enum core_tx_dest' to different enumeration type 'enum qed_ll2_tx_dest' [-Wenum-conversion]
tx_pkt.tx_dest = p_ll2_conn->tx_dest;
~ ~~~~~~~~~~~~^~~~~~~1 warning generated.
Fix this by using a switch statement to convert between the enumerated values since they are not 1 to 1, which matches how the rest of the driver handles this conversion.
--- drivers/net/ethernet/qlogic/qed/qed_ll2.c | 13 ++++++++++++- 1 file changed, 12 insertions(+), 1 deletion(-)
drivers/net/ethernet/qlogic/qed/qed_ll2.c +12 -1
@@ -796,7 +796,18 @@ qed_ooo_submit_tx_buffers(struct qed_hwfn *p_hwfn, tx_pkt.vlan = p_buffer->vlan; tx_pkt.bd_flags = bd_flags; tx_pkt.l4_hdr_offset_w = l4_hdr_offset_w; - tx_pkt.tx_dest = p_ll2_conn->tx_dest; +switch (p_ll2_conn->tx_dest) { +case CORE_TX_DEST_NW : + tx_pkt.tx_dest =QED_LL2_TX_DEST_NW ; +break ; +case CORE_TX_DEST_LB : + tx_pkt.tx_dest =QED_LL2_TX_DEST_LB ; +break ; +case CORE_TX_DEST_DROP : +default : + tx_pkt.tx_dest =QED_LL2_TX_DEST_DROP ; +break ; + } tx_pkt.first_frag = first_frag; tx_pkt.first_frag_len = p_buffer->packet_length; tx_pkt.cookie = p_buffer;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 100/220 media: rc: ir-rc6-decoder: enable toggle bit for Kathrein RCU-676 remote
In reply to Greg Kroah-HartmanFrom: Matthias Reichl <[email protected]>
[ Upstream commit 85e4af0a7ae2f146769b7475ae531bf8a3f3afb4 ]
The Kathrein RCU-676 remote uses the 32-bit rc6 protocol and toggles bit 15 (0x8000) on repeated button presses, like MCE remotes.
Add it's customer code 0x80460000 to the 32-bit rc6 toggle handling code to get proper scancodes and toggle reports.
--- drivers/media/rc/ir-rc6-decoder.c | 9 +++++++-- 1 file changed, 7 insertions(+), 2 deletions(-)
drivers/media/rc/ir-rc6-decoder.c +7 -2
@@ -40,6 +40,7 @@#define RC6_6A_MCE_TOGGLE_MASK 0x8000/* for the body bits */ #define RC6_6A_LCC_MASK 0xffff0000/* RC6-6A-32 long customer code mask */ #define RC6_6A_MCE_CC 0x800f0000/* MCE customer code */ +#define RC6_6A_KATHREIN_CC 0x80460000/* Kathrein RCU-676 customer code */ #ifndef CHAR_BIT #define CHAR_BIT 8/* Normally in <limits.h> */ #endif
@@ -242,13 +243,17 @@ static int ir_rc6_decode(struct rc_dev *dev, struct ir_raw_event ev) toggle =0 ;break ;case 32 : -if ((scancode &RC6_6A_LCC_MASK ) ==RC6_6A_MCE_CC ) { +switch (scancode &RC6_6A_LCC_MASK ) { +case RC6_6A_MCE_CC : +case RC6_6A_KATHREIN_CC : protocol =RC_PROTO_RC6_MCE ; toggle = !!(scancode &RC6_6A_MCE_TOGGLE_MASK ); scancode &= ~RC6_6A_MCE_TOGGLE_MASK ; - }else { +break ; +default : protocol =RC_PROTO_RC6_6A_32 ; toggle =0 ; +break ; }break ;default :
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 101/220 media: pxa_camera: Fix check for pdev->dev.of_node
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 44d7f1a77d8c84f8e42789b5475b74ae0e6d4758 ]
Clang warns that the address of a pointer will always evaluated as true in a boolean context.
drivers/media/platform/pxa_camera.c:2400:17: warning: address of 'pdev->dev.of_node' will always evaluate to 'true' [-Wpointer-bool-conversion]
if (&pdev->dev.of_node && !pcdev->pdata) {
~~~~~~~~~~^~~~~~~ ~~1 warning generated.
Judging from the rest of the kernel, it seems like this was an error and just the value of of_node should be checked rather than the address.
--- drivers/media/platform/pxa_camera.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/media/platform/pxa_camera.c +1 -1
@@ -2397,7 +2397,7 @@ static int pxa_camera_probe(struct platform_device *pdev) pcdev->res = res; pcdev->pdata = pdev->dev.platform_data; -if (&pdev->dev.of_node && !pcdev->pdata) { +if (pdev->dev.of_node && !pcdev->pdata) { err =pxa_camera_pdata_from_dt (&pdev->dev, pcdev, &pcdev->asd); }else { pcdev->platform_flags = pcdev->pdata->flags;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 102/220 media: rcar-vin: fix redeclaration of symbol
In reply to Greg Kroah-HartmanFrom: Niklas Söderlund <[email protected]>
[ Upstream commit 4e673ed4e2bfac00b3c3043a84e007874c17c84d ]
When adding support for parallel subdev for Gen3 it was missed that the symbol 'i' in rvin_group_link_notify() was already declared, remove the dupe as it's only used as a loop variable this have no functional change. This fixes warning:
rcar-core.c:117:52: originally declared here rcar-core.c:173:30: warning: symbol 'i' shadows an earlier one
--- drivers/media/platform/rcar-vin/rcar-core.c | 1 - 1 file changed, 1 deletion(-)
drivers/media/platform/rcar-vin/rcar-core.c +0 -1
@@ -174,7 +174,6 @@ static int rvin_group_link_notify(struct media_link *link, u32 flags,if (csi_id == -ENODEV ) {struct v4l2_subdev *sd; -unsigned int i;/* * Make sure the source entity subdevice is registered as
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 103/220 media: i2c: adv748x: Support probing a single output
In reply to Greg Kroah-HartmanFrom: Jacopo Mondi <[email protected]>
[ Upstream commit eccf442ce156ec2b4e06b1239d5fdcb0c732f63f ]
Currently the adv748x driver will fail to probe unless both of its output endpoints (TXA and TXB) are connected.
Make the driver support probing provided that there is at least one input, and one output connected and protect the clean-up function from accessing un-initialized fields.
Following patches will fix other uses of un-initialized TXs in the driver, such as power management functions.
--- drivers/media/i2c/adv748x/adv748x-core.c | 25 +++++++++++++++++++++--- drivers/media/i2c/adv748x/adv748x-csi2.c | 18 ++++++----------- drivers/media/i2c/adv748x/adv748x.h | 2 ++ 3 files changed, 30 insertions(+), 15 deletions(-)
drivers/media/i2c/adv748x/adv748x-core.c +22 -3
@@ -569,7 +569,8 @@ static int adv748x_parse_dt(struct adv748x_state *state) {struct device_node *ep_np =NULL ;struct of_endpoint ep; -bool found = false; +bool out_found = false; +bool in_found = false;for_each_endpoint_of_node (state->dev->of_node, ep_np) {of_graph_parse_endpoint (ep_np, &ep);
@@ -592,10 +593,17 @@ static int adv748x_parse_dt(struct adv748x_state *state)of_node_get (ep_np); state->endpoints[ep.port] = ep_np; - found = true; +/* +* At least one input endpoint and one output endpoint shall +* be defined. +*/ +if (ep.port <ADV748X_PORT_TXA ) + in_found = true; +else + out_found = true; } -return found ?0 : -ENODEV ; +return in_found && out_found ?0 : -ENODEV ; }static void adv748x_dt_cleanup (struct adv748x_state *state)
@@ -627,6 +635,17 @@ static int adv748x_probe(struct i2c_client *client, state->i2c_clients[ADV748X_PAGE_IO ] = client;i2c_set_clientdata (client, state); +/* +* We can not use container_of to get back to the state with two TXs; +* Initialize the TXs's fields unconditionally on the endpoint +* presence to access them later. +*/ + state->txa.state = state->txb.state = state; + state->txa.page =ADV748X_PAGE_TXA ; + state->txb.page =ADV748X_PAGE_TXB ; + state->txa.port =ADV748X_PORT_TXA ; + state->txb.port =ADV748X_PORT_TXB ; +/* Discover and process ports declared by the Device tree endpoints */ ret =adv748x_parse_dt (state);if (ret) {
drivers/media/i2c/adv748x/adv748x-csi2.c +6 -12
@@ -266,19 +266,10 @@ static int adv748x_csi2_init_controls(struct adv748x_csi2 *tx)int adv748x_csi2_init (struct adv748x_state *state,struct adv748x_csi2 *tx) { -struct device_node *ep;int ret; -/* We can not use container_of to get back to the state with two TXs */ - tx->state = state; - tx->page =is_txa (tx) ?ADV748X_PAGE_TXA :ADV748X_PAGE_TXB ; - - ep = state->endpoints[is_txa (tx) ?ADV748X_PORT_TXA :ADV748X_PORT_TXB ]; -if (!ep) { -adv_err (state,"No endpoint found for %s\n" , -is_txa (tx) ?"txa" :"txb" ); -return -ENODEV ; - } +if (!is_tx_enabled (tx)) +return 0 ;/* Initialise the virtual channel */ adv748x_csi2_set_virtual_channel (tx,0 );
@@ -288,7 +279,7 @@ int adv748x_csi2_init(struct adv748x_state *state, struct adv748x_csi2 *tx) is_txa(tx) ? "txa" : "txb");/* Ensure that matching is based upon the endpoint fwnodes */ - tx->sd.fwnode =of_fwnode_handle (ep); + tx->sd.fwnode =of_fwnode_handle (state->endpoints[tx->port]);/* Register internal ops for incremental subdev registration */ tx->sd.internal_ops = &adv748x_csi2_internal_ops;
@@ -321,6 +312,9 @@ int adv748x_csi2_init(struct adv748x_state *state, struct adv748x_csi2 *tx)void adv748x_csi2_cleanup (struct adv748x_csi2 *tx) { +if (!is_tx_enabled (tx)) +return ; +v4l2_async_unregister_subdev (&tx->sd);media_entity_cleanup (&tx->sd.entity);v4l2_ctrl_handler_free (&tx->ctrl_hdl);
drivers/media/i2c/adv748x/adv748x.h +2 -0
@@ -82,6 +82,7 @@ struct adv748x_csi2 {struct adv748x_state *state;struct v4l2_mbus_framefmt format;unsigned int page; +unsigned int port;struct media_pad pads[ADV748X_CSI2_NR_PADS ];struct v4l2_ctrl_handler ctrl_hdl;
@@ -91,6 +92,7 @@ struct adv748x_csi2 {#define notifier_to_csi2 (n) container_of(n, struct adv748x_csi2, notifier)#define adv748x_sd_to_csi2 (sd) container_of(sd, struct adv748x_csi2, sd) +#define is_tx_enabled (_tx) ((_tx)->state->endpoints[(_tx)->port] != NULL)enum adv748x_hdmi_pads {ADV748X_HDMI_SINK ,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 104/220 ALSA: hda/sigmatel - Disable automute for Elo VuPoint
In reply to Greg Kroah-HartmanFrom: Michael Pobega <[email protected]>
[ Upstream commit d153135e93a50cdb6f1b52e238909e9965b56056 ]
The Elo VuPoint 15MX has two headphone jacks of which neither work by default. Disabling automute allows ALSA to work normally with the speakers & left headphone jack.
Future pin configuration changes may be required in the future to get the right headphone jack working in tandem.
--- sound/pci/hda/patch_sigmatel.c | 20 ++++++++++++++++++++ 1 file changed, 20 insertions(+)
sound/pci/hda/patch_sigmatel.c +20 -0
@@ -77,6 +77,7 @@ enum {STAC_DELL_M6_BOTH ,STAC_DELL_EQ ,STAC_ALIENWARE_M17X , +STAC_ELO_VUPOINT_15MX ,STAC_92HD89XX_HP_FRONT_JACK ,STAC_92HD89XX_HP_Z1_G2_RIGHT_MIC_JACK , STAC_92HD73XX_ASUS_MOBO,
@@ -1879,6 +1880,18 @@ static void stac92hd73xx_fixup_no_jd(struct hda_codec *codec, codec->no_jack_detect =1 ; } + +static void stac92hd73xx_disable_automute (struct hda_codec *codec, +const struct hda_fixup *fix,int action) +{ +struct sigmatel_spec *spec = codec->spec; + +if (action !=HDA_FIXUP_ACT_PRE_PROBE ) +return ; + + spec->gen.suppress_auto_mute =1 ; +} +static const struct hda_fixup stac92hd73xx_fixups[] = { [STAC_92HD73XX_REF ] = { .type =HDA_FIXUP_FUNC ,
@@ -1904,6 +1917,10 @@ static const struct hda_fixup stac92hd73xx_fixups[] = { .type = HDA_FIXUP_FUNC, .v.func = stac92hd73xx_fixup_alienware_m17x, }, + [STAC_ELO_VUPOINT_15MX] = { + .type = HDA_FIXUP_FUNC, + .v.func = stac92hd73xx_disable_automute, + }, [STAC_92HD73XX_INTEL] = { .type = HDA_FIXUP_PINS, .v.pins = intel_dg45id_pin_configs,
@@ -1942,6 +1959,7 @@ static const struct hda_model_fixup stac92hd73xx_models[] = { { .id = STAC_DELL_M6_BOTH, .name = "dell-m6" }, { .id = STAC_DELL_EQ, .name = "dell-eq" }, { .id = STAC_ALIENWARE_M17X, .name = "alienware" }, + { .id = STAC_ELO_VUPOINT_15MX, .name = "elo-vupoint-15mx" }, { .id = STAC_92HD73XX_ASUS_MOBO, .name = "asus-mobo" }, {} };
@@ -1991,6 +2009,8 @@ static const struct snd_pci_quirk stac92hd73xx_fixup_tbl[] = { "Alienware M17x", STAC_ALIENWARE_M17X),SND_PCI_QUIRK (PCI_VENDOR_ID_DELL ,0x0490 ,"Alienware M17x R3" ,STAC_DELL_EQ ), +SND_PCI_QUIRK (0x1059 ,0x1011 , +"ELO VuPoint 15MX" ,STAC_ELO_VUPOINT_15MX ),SND_PCI_QUIRK (PCI_VENDOR_ID_HP ,0x1927 ,"HP Z1 G2" ,STAC_92HD89XX_HP_Z1_G2_RIGHT_MIC_JACK ), SND_PCI_QUIRK(PCI_VENDOR_ID_HP, 0x2b17,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 105/220 bnxt_en: return proper error when FW returns HWRM_ERR_CODE_RESOURCE_ACCESS_DENIED
In reply to Greg Kroah-HartmanFrom: Vasundhara Volam <[email protected]>
[ Upstream commit 3a1d52a54a6a4030b294e5f5732f0bfbae0e3815 ]
Return proper error code when Firmware returns HWRM_ERR_CODE_RESOURCE_ACCESS_DENIED for HWRM_NVM_GET/SET_VARIABLE commands.
--- drivers/net/ethernet/broadcom/bnxt/bnxt_devlink.c | 6 +++++- 1 file changed, 5 insertions(+), 1 deletion(-)
drivers/net/ethernet/broadcom/bnxt/bnxt_devlink.c +5 -1
@@ -78,8 +78,12 @@ static int bnxt_hwrm_nvm_req(struct bnxt *bp, u32 param_id, void *msg,memcpy (buf, data_addr, bytesize);dma_free_coherent (&bp->pdev->dev, bytesize, data_addr, data_dma_addr); -if (rc) +if (rc ==HWRM_ERR_CODE_RESOURCE_ACCESS_DENIED ) { +netdev_err (bp->dev,"PF does not have admin privileges to modify NVM config\n" ); +return -EACCES ; + }else if (rc) {return -EIO ; + }return 0 ; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 106/220 KVM: PPC: Book3S PR: Exiting split hack mode needs to fixup both PC and LR
In reply to Greg Kroah-HartmanFrom: Cameron Kaiser <[email protected]>
[ Upstream commit 1006284c5e411872333967b1970c2ca46a9e225f ]
When an OS (currently only classic Mac OS) is running in KVM-PR and makes a linked jump from code with split hack addressing enabled into code that does not, LR is not correctly updated and reflects the previously munged PC.
To fix this, this patch undoes the address munge when exiting split hack mode so that code relying on LR being a proper address will now execute. This does not affect OS X or other operating systems running on KVM-PR.
--- arch/powerpc/kvm/book3s.c | 3 +++ 1 file changed, 3 insertions(+)
arch/powerpc/kvm/book3s.c +3 -0
@@ -78,8 +78,11 @@ void kvmppc_unfixup_split_real(struct kvm_vcpu *vcpu) {if (vcpu->arch.hflags &BOOK3S_HFLAG_SPLIT_HACK ) {ulong pc =kvmppc_get_pc (vcpu); +ulong lr =kvmppc_get_lr (vcpu);if ((pc &SPLIT_HACK_MASK ) ==SPLIT_HACK_OFFS )kvmppc_set_pc (vcpu, pc & ~SPLIT_HACK_MASK ); +if ((lr &SPLIT_HACK_MASK ) ==SPLIT_HACK_OFFS ) +kvmppc_set_lr (vcpu, lr & ~SPLIT_HACK_MASK ); vcpu->arch.hflags &= ~BOOK3S_HFLAG_SPLIT_HACK ; } }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 107/220 USB: serial: cypress_m8: fix interrupt-out transfer length
In reply to Greg Kroah-HartmanFrom: Johan Hovold <[email protected]>
[ Upstream commit 56445eef55cb5904096fed7a73cf87b755dfffc7 ]
Fix interrupt-out transfer length which was being set to the transfer-buffer length rather than the size of the outgoing packet.
Note that no slab data was leaked as the whole transfer buffer is always cleared before each transfer.
--- drivers/usb/serial/cypress_m8.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/usb/serial/cypress_m8.c +1 -1
@@ -769,7 +769,7 @@ static void cypress_send(struct usb_serial_port *port)usb_fill_int_urb (port->interrupt_out_urb, port->serial->dev,usb_sndintpipe (port->serial->dev, port->interrupt_out_endpointAddress), - port->interrupt_out_buffer, port->interrupt_out_size, + port->interrupt_out_buffer, actual_size, cypress_write_int_callback, port, priv->write_urb_interval); result =usb_submit_urb (port->interrupt_out_urb,GFP_ATOMIC );if (result) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 108/220 usb: dwc2: disable power_down on rockchip devices
In reply to Greg Kroah-HartmanFrom: SolidHal <[email protected]>
[ Upstream commit c216765d3a1defda5e7e2dabd878f99f0cd2ebf2 ]
The bug would let the usb controller enter partial power down, which was formally known as hibernate, upon boot if nothing was plugged in to the port. Partial power down couldn't be exited properly, so any usb devices plugged in after boot would not be usable.
Before the name change, params.hibernation was false by default, so _dwc2_hcd_suspend() would skip entering hibernation. With the rename, _dwc2_hcd_suspend() was changed to use params.power_down to decide whether or not to enter partial power down.
Since params.power_down is non-zero by default, it needs to be set to 0 for rockchip devices to restore functionality.
This bug was reported in the linux-usb thread:
REGRESSION: usb: dwc2: USB device not seen after boot
The commit that caused this regression is:6d23ee9caa6790aea047f9aca7f3c03cb8d96eb6
--- drivers/usb/dwc2/params.c | 1 + 1 file changed, 1 insertion(+)
drivers/usb/dwc2/params.c +1 -0
@@ -88,6 +88,7 @@ static void dwc2_set_rk_params(struct dwc2_hsotg *hsotg) p->host_perio_tx_fifo_size =256 ; p->ahbcfg =GAHBCFG_HBSTLEN_INCR16 <<GAHBCFG_HBSTLEN_SHIFT ; + p->power_down =0 ; }static void dwc2_set_ltq_params (struct dwc2_hsotg *hsotg)
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 109/220 mtd: physmap_of: Release resources on error
In reply to Greg Kroah-HartmanFrom: Ricardo Ribalda Delgado <[email protected]>
[ Upstream commit ef0de747f7ad179c7698a5b0e28db05f18ecbf57 ]
During probe, if there was an error the memory region and the memory map were not properly released.This can lead a system unusable if deferred probe is in use.
Replace mem_request and map with devm_ioremap_resource
--- drivers/mtd/maps/physmap_of_core.c | 27 +++++---------------------- 1 file changed, 5 insertions(+), 22 deletions(-)
drivers/mtd/maps/physmap_of_core.c +5 -22
@@ -31,7 +31,6 @@struct of_flash_list {struct mtd_info *mtd;struct map_info map; -struct resource *res; };struct of_flash {
@@ -56,18 +55,10 @@ static int of_flash_remove(struct platform_device *dev)mtd_concat_destroy (info->cmtd); } -for (i =0 ; i < info->list_size; i++) { +for (i =0 ; i < info->list_size; i++)if (info->list[i].mtd)map_destroy (info->list[i].mtd); -if (info->list[i].map.virt) -iounmap (info->list[i].map.virt); - -if (info->list[i].res) { -release_resource (info->list[i].res); -kfree (info->list[i].res); - } - }return 0 ; }
@@ -215,10 +206,11 @@ static int of_flash_probe(struct platform_device *dev) err = -EBUSY ; res_size =resource_size (&res); - info->list[i].res =request_mem_region (res.start, res_size, -dev_name (&dev->dev)); -if (!info->list[i].res) + info->list[i].map.virt =devm_ioremap_resource (&dev->dev, &res); +if (IS_ERR (info->list[i].map.virt)) { + err =PTR_ERR (info->list[i].map.virt); goto err_out; + } err = -ENXIO ; width =of_get_property (dp,"bank-width" ,NULL );
@@ -246,15 +238,6 @@ static int of_flash_probe(struct platform_device *dev)if (err) goto err_out; - err = -ENOMEM ; - info->list[i].map.virt =ioremap (info->list[i].map.phys, - info->list[i].map.size); -if (!info->list[i].map.virt) { -dev_err (&dev->dev,"Failed to ioremap() flash" -" region\n" ); - goto err_out; - } -simple_map_init (&info->list[i].map);/*
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 110/220 cpu/SMT: State SMT is disabled even with nosmt and without "=force"
In reply to Greg Kroah-HartmanFrom: Borislav Petkov <[email protected]>
[ Upstream commit d0e7d14455d41163126afecd0fcce935463cc512 ]
When booting with "nosmt=force" a message is issued into dmesg to confirm that SMT has been force-disabled but such a message is not issued when only "nosmt" is on the kernel command line.
Fix that.
--- kernel/cpu.c | 1 + 1 file changed, 1 insertion(+)
kernel/cpu.c +1 -0
@@ -375,6 +375,7 @@ void __init cpu_smt_disable(bool force)pr_info ("SMT: Force disabled\n" ); cpu_smt_control =CPU_SMT_FORCE_DISABLED ; }else { +pr_info ("SMT: disabled\n" ); cpu_smt_control =CPU_SMT_DISABLED ; } }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 111/220 brcmfmac: reduce timeout for action frame scan
In reply to Greg Kroah-HartmanFrom: Chung-Hsien Hsu <[email protected]>
[ Upstream commit edb6d6885bef82d1eac432dbeca9fbf4ec349d7e ]
Finding a common channel to send an action frame out is required for some action types. Since a loop with several scan retry is used to find the channel, a short wait time could be considered for each attempt. This patch reduces the wait time from 1500 to 450 msec for each action frame scan.
This patch fixes the WFA p2p certification 5.1.20 failure caused by the long action frame send time.
--- drivers/net/wireless/broadcom/brcm80211/brcmfmac/p2p.c | 9 ++++----- 1 file changed, 4 insertions(+), 5 deletions(-)
drivers/net/wireless/broadcom/brcm80211/brcmfmac/p2p.c +4 -5
@@ -74,7 +74,7 @@#define P2P_AF_MAX_WAIT_TIME msecs_to_jiffies(2000)#define P2P_INVALID_CHANNEL -1#define P2P_CHANNEL_SYNC_RETRY 5 -#define P2P_AF_FRM_SCAN_MAX_WAIT msecs_to_jiffies(1500) +#define P2P_AF_FRM_SCAN_MAX_WAIT msecs_to_jiffies(450)#define P2P_DEFAULT_SLEEP_TIME_VSDB 200/* WiFi P2P Public Action Frame OUI Subtypes */
@@ -1134,7 +1134,6 @@ static s32 brcmf_p2p_af_searching_channel(struct brcmf_p2p_info *p2p) {struct afx_hdl *afx_hdl = &p2p->afx_hdl;struct brcmf_cfg80211_vif *pri_vif; -unsigned long duration;s32 retry;brcmf_dbg (TRACE ,"Enter\n" );
@@ -1150,7 +1149,6 @@ static s32 brcmf_p2p_af_searching_channel(struct brcmf_p2p_info *p2p)* pending action frame tx is cancelled. */ retry =0 ; - duration =msecs_to_jiffies (P2P_AF_FRM_SCAN_MAX_WAIT );while ((retry <P2P_CHANNEL_SYNC_RETRY ) && (afx_hdl->peer_chan ==P2P_INVALID_CHANNEL )) { afx_hdl->is_listen = false;
@@ -1158,7 +1156,8 @@ static s32 brcmf_p2p_af_searching_channel(struct brcmf_p2p_info *p2p) retry);/* search peer on peer's listen channel */ schedule_work (&afx_hdl->afx_work); -wait_for_completion_timeout (&afx_hdl->act_frm_scan, duration); +wait_for_completion_timeout (&afx_hdl->act_frm_scan, +P2P_AF_FRM_SCAN_MAX_WAIT );if ((afx_hdl->peer_chan !=P2P_INVALID_CHANNEL ) || (!test_bit (BRCMF_P2P_STATUS_FINDING_COMMON_CHANNEL , &p2p->status)))
@@ -1171,7 +1170,7 @@ static s32 brcmf_p2p_af_searching_channel(struct brcmf_p2p_info *p2p) afx_hdl->is_listen = true;schedule_work (&afx_hdl->afx_work);wait_for_completion_timeout (&afx_hdl->act_frm_scan, - duration); +P2P_AF_FRM_SCAN_MAX_WAIT ); } if ((afx_hdl->peer_chan != P2P_INVALID_CHANNEL) || (!test_bit(BRCMF_P2P_STATUS_FINDING_COMMON_CHANNEL,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 112/220 brcmfmac: fix full timeout waiting for action frame on-channel tx
In reply to Greg Kroah-HartmanFrom: Chung-Hsien Hsu <[email protected]>
[ Upstream commit fbf07000960d9c8a13fdc17c6de0230d681c7543 ]
The driver sends an action frame down and waits for a completion signal triggered by the received BRCMF_E_ACTION_FRAME_OFF_CHAN_COMPLETE event to continue the process. However, the action frame could be transmitted either on the current channel or on an off channel. For the on-channel case, only BRCMF_E_ACTION_FRAME_COMPLETE event will be received when the frame is transmitted, which make the driver always wait a full timeout duration. This patch has the completion signal be triggered by receiving the BRCMF_E_ACTION_FRAME_COMPLETE event for the on-channel case.
This change fixes WFA p2p certification 5.1.19 failure.
--- .../wireless/broadcom/brcm80211/brcmfmac/p2p.c | 17 +++++++++++++++-- .../wireless/broadcom/brcm80211/brcmfmac/p2p.h | 2 ++ 2 files changed, 17 insertions(+), 2 deletions(-)
drivers/net/wireless/broadcom/brcm80211/brcmfmac/p2p.c +15 -2
@@ -1457,10 +1457,12 @@ int brcmf_p2p_notify_action_tx_complete(struct brcmf_if *ifp,return 0 ;if (e->event_code ==BRCMF_E_ACTION_FRAME_COMPLETE ) { -if (e->status ==BRCMF_E_STATUS_SUCCESS ) +if (e->status ==BRCMF_E_STATUS_SUCCESS ) {set_bit (BRCMF_P2P_STATUS_ACTION_TX_COMPLETED , &p2p->status); -else { +if (!p2p->wait_for_offchan_complete) +complete (&p2p->send_af_done); + }else {set_bit (BRCMF_P2P_STATUS_ACTION_TX_NOACK , &p2p->status);/* If there is no ack, we don't need to wait for * WLC_E_ACTION_FRAME_OFFCHAN_COMPLETE event
@@ -1511,6 +1513,17 @@ static s32 brcmf_p2p_tx_action_frame(struct brcmf_p2p_info *p2p, p2p->af_sent_channel =le32_to_cpu (af_params->channel); p2p->af_tx_sent_jiffies = jiffies; +if (test_bit (BRCMF_P2P_STATUS_DISCOVER_LISTEN , &p2p->status) && + p2p->af_sent_channel == +ieee80211_frequency_to_channel (p2p->remain_on_channel.center_freq)) + p2p->wait_for_offchan_complete = false; +else + p2p->wait_for_offchan_complete = true; + +brcmf_dbg (TRACE ,"Waiting for %s tx completion event\n" , + (p2p->wait_for_offchan_complete) ? +"off-channel" :"on-channel" ); + timeout =wait_for_completion_timeout (&p2p->send_af_done,P2P_AF_MAX_WAIT_TIME );
drivers/net/wireless/broadcom/brcm80211/brcmfmac/p2p.h +2 -0
@@ -124,6 +124,7 @@ struct afx_hdl {* @gon_req_action: about to send go negotiation requets frame. * @block_gon_req_tx: drop tx go negotiation requets frame. * @p2pdev_dynamically: is p2p device if created by module param or supplicant. +* @wait_for_offchan_complete: wait for off-channel tx completion event. */ struct brcmf_p2p_info {struct brcmf_cfg80211_info *cfg;
@@ -144,6 +145,7 @@ struct brcmf_p2p_info {bool gon_req_action;bool block_gon_req_tx;bool p2pdev_dynamically; +bool wait_for_offchan_complete; };s32 brcmf_p2p_attach (struct brcmf_cfg80211_info *cfg,bool p2pdev_forced);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 113/220 qtnfmac: request userspace to do OBSS scanning if FW can not
In reply to Greg Kroah-HartmanFrom: Igor Mitsyanko <[email protected]>
[ Upstream commit 92246b126ebf66ab1fec9d631df78d7c675b66db ]
In case firmware reports that it can not do OBSS scanning for 40MHz 2.4GHz channels itself, tell userpsace to do that instead by setting NL80211_FEATURE_NEED_OBSS_SCAN flag.
--- drivers/net/wireless/quantenna/qtnfmac/cfg80211.c | 3 +++ drivers/net/wireless/quantenna/qtnfmac/qlink.h | 2 ++ 2 files changed, 5 insertions(+)
drivers/net/wireless/quantenna/qtnfmac/cfg80211.c +3 -0
@@ -1109,6 +1109,9 @@ int qtnf_wiphy_register(struct qtnf_hw_info *hw_info, struct qtnf_wmac *mac)if (hw_info->hw_capab &QLINK_HW_CAPAB_SCAN_RANDOM_MAC_ADDR ) wiphy->features |=NL80211_FEATURE_SCAN_RANDOM_MAC_ADDR ; +if (!(hw_info->hw_capab &QLINK_HW_CAPAB_OBSS_SCAN )) + wiphy->features |=NL80211_FEATURE_NEED_OBSS_SCAN ; +#ifdef CONFIG_PM if (macinfo->wowlan) wiphy->wowlan = macinfo->wowlan;
drivers/net/wireless/quantenna/qtnfmac/qlink.h +2 -0
@@ -71,6 +71,7 @@ struct qlink_msg_header {* @QLINK_HW_CAPAB_DFS_OFFLOAD: device implements DFS offload functionality * @QLINK_HW_CAPAB_SCAN_RANDOM_MAC_ADDR: device supports MAC Address * Randomization in probe requests. +* @QLINK_HW_CAPAB_OBSS_SCAN: device can perform OBSS scanning. */ enum qlink_hw_capab {QLINK_HW_CAPAB_REG_UPDATE =BIT (0 ),
@@ -78,6 +79,7 @@ enum qlink_hw_capab {QLINK_HW_CAPAB_DFS_OFFLOAD =BIT (2 ),QLINK_HW_CAPAB_SCAN_RANDOM_MAC_ADDR =BIT (3 ),QLINK_HW_CAPAB_PWR_MGMT =BIT (4 ), + QLINK_HW_CAPAB_OBSS_SCAN = BIT(5), }; enum qlink_iface_type {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 114/220 qtnfmac: pass sgi rate info flag to wireless core
In reply to Greg Kroah-HartmanFrom: Sergey Matyukevich <[email protected]>
[ Upstream commit d5657b709e2a92a0e581109010765d1d485580df ]
SGI should be passed to wireless core as a part of rate structure. Otherwise wireless core performs incorrect rate calculation when SGI is enabled in hardware but not reported to host.
--- drivers/net/wireless/quantenna/qtnfmac/commands.c | 3 +++ 1 file changed, 3 insertions(+)
drivers/net/wireless/quantenna/qtnfmac/commands.c +3 -0
@@ -544,6 +544,9 @@ qtnf_sta_info_parse_rate(struct rate_info *rate_dst, rate_dst->flags |=RATE_INFO_FLAGS_MCS ; else if (rate_src->flags & QLINK_STA_INFO_RATE_FLAG_VHT_MCS) rate_dst->flags |= RATE_INFO_FLAGS_VHT_MCS; + +if (rate_src->flags &QLINK_STA_INFO_RATE_FLAG_SHORT_GI ) + rate_dst->flags |=RATE_INFO_FLAGS_SHORT_GI ; } static void
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 115/220 qtnfmac: inform wireless core about supported extended capabilities
In reply to Greg Kroah-HartmanFrom: Sergey Matyukevich <[email protected]>
[ Upstream commit ab1c64a1d349cc7f1090a60ce85a53298e3d371d ]
Driver retrieves information about supported extended capabilities from wireless card. However this information is not propagated further to Linux wireless core. Fix this by setting extended capabilities fields of wiphy structure.
--- .../net/wireless/quantenna/qtnfmac/cfg80211.c | 9 +++++++++ .../net/wireless/quantenna/qtnfmac/commands.c | 3 +-- drivers/net/wireless/quantenna/qtnfmac/core.c | 16 ++++++++++++++-- drivers/net/wireless/quantenna/qtnfmac/core.h | 1 + 4 files changed, 25 insertions(+), 4 deletions(-)
drivers/net/wireless/quantenna/qtnfmac/cfg80211.c +9 -0
@@ -1126,6 +1126,15 @@ int qtnf_wiphy_register(struct qtnf_hw_info *hw_info, struct qtnf_wmac *mac) wiphy->regulatory_flags |=REGULATORY_WIPHY_SELF_MANAGED ; } +if (mac->macinfo.extended_capabilities_len) { + wiphy->extended_capabilities = + mac->macinfo.extended_capabilities; + wiphy->extended_capabilities_mask = + mac->macinfo.extended_capabilities_mask; + wiphy->extended_capabilities_len = + mac->macinfo.extended_capabilities_len; + } +strlcpy (wiphy->fw_version, hw_info->fw_version,sizeof (wiphy->fw_version)); wiphy->hw_version = hw_info->hw_version;
drivers/net/wireless/quantenna/qtnfmac/commands.c +1 -2
@@ -1356,8 +1356,7 @@ static int qtnf_parse_variable_mac_info(struct qtnf_wmac *mac, ext_capa_mask =NULL ; } -kfree (mac->macinfo.extended_capabilities); -kfree (mac->macinfo.extended_capabilities_mask); +qtnf_mac_ext_caps_free (mac); mac->macinfo.extended_capabilities = ext_capa; mac->macinfo.extended_capabilities_mask = ext_capa_mask; mac->macinfo.extended_capabilities_len = ext_capa_len;
drivers/net/wireless/quantenna/qtnfmac/core.c +14 -2
@@ -304,6 +304,19 @@ void qtnf_mac_iface_comb_free(struct qtnf_wmac *mac) } } +void qtnf_mac_ext_caps_free (struct qtnf_wmac *mac) +{ +if (mac->macinfo.extended_capabilities_len) { +kfree (mac->macinfo.extended_capabilities); + mac->macinfo.extended_capabilities =NULL ; + +kfree (mac->macinfo.extended_capabilities_mask); + mac->macinfo.extended_capabilities_mask =NULL ; + + mac->macinfo.extended_capabilities_len =0 ; + } +} +static void qtnf_vif_reset_handler (struct work_struct *work) { struct qtnf_vif *vif = container_of(work, struct qtnf_vif, reset_work);
@@ -493,8 +506,7 @@ static void qtnf_core_mac_detach(struct qtnf_bus *bus, unsigned int macid) }qtnf_mac_iface_comb_free (mac); -kfree (mac->macinfo.extended_capabilities); -kfree (mac->macinfo.extended_capabilities_mask); +qtnf_mac_ext_caps_free (mac);kfree (mac->macinfo.wowlan);wiphy_free (wiphy); bus->mac[macid] =NULL ;
drivers/net/wireless/quantenna/qtnfmac/core.h +1 -0
@@ -151,6 +151,7 @@ struct qtnf_hw_info {struct qtnf_vif *qtnf_mac_get_free_vif (struct qtnf_wmac *mac);struct qtnf_vif *qtnf_mac_get_base_vif (struct qtnf_wmac *mac);void qtnf_mac_iface_comb_free (struct qtnf_wmac *mac); +void qtnf_mac_ext_caps_free (struct qtnf_wmac *mac);struct wiphy *qtnf_wiphy_allocate (struct qtnf_bus *bus);int qtnf_core_net_attach (struct qtnf_wmac *mac,struct qtnf_vif *priv,const char *name,unsigned char name_assign_type);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 116/220 qtnfmac: drop error reports for out-of-bounds key indexes
In reply to Greg Kroah-HartmanFrom: Sergey Matyukevich <[email protected]>
[ Upstream commit 35da3fe63b8647ce3cc52fccdf186a60710815fb ]
On disconnect wireless core attempts to remove all the supported keys. Following cfg80211_ops conventions, firmware returns -ENOENT code for the out-of-bound key indexes. This is a normal behavior, so no need to report errors for this case.
--- drivers/net/wireless/quantenna/qtnfmac/cfg80211.c | 13 ++++++++++--- 1 file changed, 10 insertions(+), 3 deletions(-)
drivers/net/wireless/quantenna/qtnfmac/cfg80211.c +10 -3
@@ -521,9 +521,16 @@ static int qtnf_del_key(struct wiphy *wiphy, struct net_device *dev,int ret; ret =qtnf_cmd_send_del_key (vif, key_index, pairwise, mac_addr); -if (ret) -pr_err ("VIF%u.%u: failed to delete key: idx=%u pw=%u\n" , - vif->mac->macid, vif->vifid, key_index, pairwise); +if (ret) { +if (ret == -ENOENT ) { +pr_debug ("VIF%u.%u: key index %d out of bounds\n" , + vif->mac->macid, vif->vifid, key_index); + }else { +pr_err ("VIF%u.%u: failed to delete key: idx=%u pw=%u\n" , + vif->mac->macid, vif->vifid, + key_index, pairwise); + } + }return ret; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 117/220 clk: samsung: Use NOIRQ stage for Exynos5433 clocks suspend/resume
In reply to Greg Kroah-HartmanFrom: Marek Szyprowski <[email protected]>
[ Upstream commit 70da9ee80228e6d98fd68e3c1db124c4461d283c ]
SoC clock drivers should suspend after every other drivers in the system, which are using clocks and resume before them. The last stage for calling suspend device callbacks is NOIRQ stage and there exists driver, which use that state (dwmmc-exynos), so Exynos5433 clocks driver should also use it. During the same stage, clocks driver will be always suspended after its clients as a direct result of proper device probe order (deferred probe reorders the suspend call sequence).
--- drivers/clk/samsung/clk-exynos5433.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/clk/samsung/clk-exynos5433.c +1 -1
@@ -5630,7 +5630,7 @@ static const struct of_device_id exynos5433_cmu_of_match[] = {static const struct dev_pm_ops exynos5433_cmu_pm_ops = { SET_RUNTIME_PM_OPS(exynos5433_cmu_suspend, exynos5433_cmu_resume, NULL) -SET_LATE_SYSTEM_SLEEP_PM_OPS (pm_runtime_force_suspend, +SET_NOIRQ_SYSTEM_SLEEP_PM_OPS (pm_runtime_force_suspend, pm_runtime_force_resume) };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 118/220 clk: samsung: exynos5420: Define CLK_SECKEY gate clock only or Exynos5420
In reply to Greg Kroah-HartmanFrom: Joonyoung Shim <[email protected]>
[ Upstream commit d32dd2a1a0f80edad158c9a1ba5f47650d9504a0 ]
The bit of GATE_BUS_PERIS1 for CLK_SECKEY is just reserved on exynos5422/5800, not exynos5420. Define gate clk for exynos5420 to handle the bit only on exynos5420.
--- drivers/clk/samsung/clk-exynos5420.c | 3 +-- 1 file changed, 1 insertion(+), 2 deletions(-)
drivers/clk/samsung/clk-exynos5420.c +1 -2
@@ -634,6 +634,7 @@ static const struct samsung_div_clock exynos5420_div_clks[] __initconst = { };static const struct samsung_gate_clock exynos5420_gate_clks[]__initconst = { +GATE (CLK_SECKEY ,"seckey" ,"aclk66_psgen" ,GATE_BUS_PERIS1 ,1 ,0 ,0 ),GATE (CLK_MAU_EPLL ,"mau_epll" ,"mout_mau_epll_clk" ,SRC_MASK_TOP7 ,20 ,CLK_SET_RATE_PARENT ,0 ), };
@@ -1163,8 +1164,6 @@ static const struct samsung_gate_clock exynos5x_gate_clks[] __initconst = {GATE (CLK_TMU ,"tmu" ,"aclk66_psgen" ,GATE_IP_PERIS ,21 ,0 ,0 ),GATE (CLK_TMU_GPU ,"tmu_gpu" ,"aclk66_psgen" ,GATE_IP_PERIS ,22 ,0 ,0 ), -GATE (CLK_SECKEY ,"seckey" ,"aclk66_psgen" ,GATE_BUS_PERIS1 ,1 ,0 ,0 ), -/* GEN Block */ GATE (CLK_ROTATOR ,"rotator" ,"mout_user_aclk266" ,GATE_IP_GEN ,1 ,0 ,0 ), GATE(CLK_JPEG, "jpeg", "aclk300_jpeg", GATE_IP_GEN, 2, 0, 0),
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 119/220 clk: samsung: Use clk_hw API for calling clk framework from clk notifiers
In reply to Greg Kroah-HartmanFrom: Marek Szyprowski <[email protected]>
[ Upstream commit 1da220e3a5d22fccda0bc8542997abc1d1741268 ]
clk_notifier_register() documentation states, that the provided notifier callbacks associated with the notifier must not re-enter into the clk framework by calling any top-level clk APIs. Fix this by replacing clk_get_rate() calls with clk_hw_get_rate(), which is safe in this context.
--- drivers/clk/samsung/clk-cpu.c | 6 +++--- drivers/clk/samsung/clk-cpu.h | 2 +- 2 files changed, 4 insertions(+), 4 deletions(-)
drivers/clk/samsung/clk-cpu.c +3 -3
@@ -152,7 +152,7 @@ static int exynos_cpuclk_pre_rate_change(struct clk_notifier_data *ndata, struct exynos_cpuclk *cpuclk, void __iomem *base) { const struct exynos_cpuclk_cfg_data *cfg_data = cpuclk->cfg; -unsigned long alt_prate =clk_get_rate (cpuclk->alt_parent); +unsigned long alt_prate =clk_hw_get_rate (cpuclk->alt_parent);unsigned long alt_div =0 , alt_div_mask =DIV_MASK ;unsigned long div0, div1 =0 , mux_reg;unsigned long flags;
@@ -280,7 +280,7 @@ static int exynos5433_cpuclk_pre_rate_change(struct clk_notifier_data *ndata, struct exynos_cpuclk *cpuclk, void __iomem *base) { const struct exynos_cpuclk_cfg_data *cfg_data = cpuclk->cfg; -unsigned long alt_prate =clk_get_rate (cpuclk->alt_parent); +unsigned long alt_prate =clk_hw_get_rate (cpuclk->alt_parent);unsigned long alt_div =0 , alt_div_mask =DIV_MASK ;unsigned long div0, div1 =0 , mux_reg;unsigned long flags;
@@ -432,7 +432,7 @@ int __init exynos_register_cpu_clock(struct samsung_clk_provider *ctx,else cpuclk->clk_nb.notifier_call = exynos_cpuclk_notifier_cb; - cpuclk->alt_parent =__clk_lookup (alt_parent); + cpuclk->alt_parent =__clk_get_hw (__clk_lookup (alt_parent));if (!cpuclk->alt_parent) {pr_err ("%s: could not lookup alternate parent %s\n" , __func__, alt_parent);
drivers/clk/samsung/clk-cpu.h +1 -1
@@ -49,7 +49,7 @@ struct exynos_cpuclk_cfg_data {*/ struct exynos_cpuclk {struct clk_hw hw; -struct clk *alt_parent; +struct clk_hw *alt_parent;void __iomem *ctrl_base;spinlock_t *lock;const struct exynos_cpuclk_cfg_data *cfg;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 120/220 i2c: brcmstb: Allow enabling the driver on DSL SoCs
In reply to Greg Kroah-HartmanFrom: Florian Fainelli <[email protected]>
[ Upstream commit e1eba2ea54a2de0e4c58d87270d25706bb77b844 ]
ARCH_BCM_63XX which is used by ARM-based DSL SoCs from Broadcom uses the same controller, make it possible to select the STB driver and update the Kconfig and help text a bit.
--- drivers/i2c/busses/Kconfig | 7 ++++--- 1 file changed, 4 insertions(+), 3 deletions(-)
drivers/i2c/busses/Kconfig +4 -3
@@ -433,12 +433,13 @@ config I2C_BCM_KONA If you do not need KONA I2C interface, say N. config I2C_BRCMSTB - tristate "BRCM Settop I2C controller" - depends on ARCH_BRCMSTB || BMIPS_GENERIC || COMPILE_TEST + tristate "BRCM Settop/DSL I2C controller" + depends on ARCH_BRCMSTB || BMIPS_GENERIC || ARCH_BCM_63XX || \ + COMPILE_TEST default y help If you say yes to this option, support will be included for the - I2C interface on the Broadcom Settop SoCs. + I2C interface on the Broadcom Settop/DSL SoCs. If you do not need I2C interface, say N.
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 121/220 printk: Correct wrong casting
In reply to Greg Kroah-HartmanFrom: He Zhe <[email protected]>
[ Upstream commit 51a72ab7372d85c96104e58036f1b49ba11e5d2b ]
log_first_seq and console_seq are 64-bit unsigned integers. Correct a wrong casting that might cut off the output.
--- kernel/printk/printk.c | 5 +++-- 1 file changed, 3 insertions(+), 2 deletions(-)
kernel/printk/printk.c +3 -2
@@ -2358,8 +2358,9 @@ void console_unlock(void)printk_safe_enter_irqsave (flags);raw_spin_lock (&logbuf_lock);if (console_seq < log_first_seq) { - len =sprintf (text,"** %u printk messages dropped **\n" , - (unsigned )(log_first_seq - console_seq)); + len =sprintf (text, +"** %llu printk messages dropped **\n" , + log_first_seq - console_seq);/* messages are gone, move to first one */ console_seq = log_first_seq;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 122/220 NFSv4.x: fix lock recovery during delegation recall
In reply to Greg Kroah-HartmanFrom: Olga Kornievskaia <[email protected]>
[ Upstream commit 44f411c353bf6d98d5a34f8f1b8605d43b2e50b8 ]
Running "./nfstest_delegation --runtest recall26" uncovers that client doesn't recover the lock when we have an appending open, where the initial open got a write delegation.
Instead of checking for the passed in open context against the file lock's open context. Check that the state is the same.
--- fs/nfs/delegation.c | 6 +++--- 1 file changed, 3 insertions(+), 3 deletions(-)
fs/nfs/delegation.c +3 -3
@@ -103,7 +103,7 @@ int nfs4_check_delegation(struct inode *inode, fmode_t flags)return nfs4_do_check_delegation (inode, flags, false); } -static int nfs_delegation_claim_locks (struct nfs_open_context *ctx,struct nfs4_state *state,const nfs4_stateid *stateid) +static int nfs_delegation_claim_locks (struct nfs4_state *state,const nfs4_stateid *stateid) {struct inode *inode = state->inode;struct file_lock *fl;
@@ -118,7 +118,7 @@ static int nfs_delegation_claim_locks(struct nfs_open_context *ctx, struct nfs4_spin_lock (&flctx->flc_lock); restart:list_for_each_entry (fl, list, fl_list) { -if (nfs_file_open_context (fl->fl_file) != ctx) +if (nfs_file_open_context (fl->fl_file)->state != state)continue ;spin_unlock (&flctx->flc_lock); status =nfs4_lock_delegation_recall (fl, state, stateid);
@@ -165,7 +165,7 @@ static int nfs_delegation_claim_opens(struct inode *inode, seq =raw_seqcount_begin (&sp->so_reclaim_seqcount); err =nfs4_open_delegation_recall (ctx, state, stateid);if (!err) - err =nfs_delegation_claim_locks (ctx, state, stateid); + err =nfs_delegation_claim_locks (state, stateid);if (!err &&read_seqcount_retry (&sp->so_reclaim_seqcount, seq)) err = -EAGAIN ;mutex_unlock (&sp->so_delegreturn_mutex);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 123/220 dmaengine: ioat: fix prototype of ioat_enumerate_channels
In reply to Greg Kroah-HartmanFrom: Rami Rosen <[email protected]>
[ Upstream commit f4d34aa8c887a8a2d23ef546da0efa10e3f77241 ]
--- drivers/dma/ioat/init.c | 7 +++---- 1 file changed, 3 insertions(+), 4 deletions(-)
drivers/dma/ioat/init.c +3 -4
@@ -129,7 +129,7 @@ static void ioat_init_channel(struct ioatdma_device *ioat_dma, struct ioatdma_chan *ioat_chan, int idx);static void ioat_intr_quirk (struct ioatdma_device *ioat_dma); -static int ioat_enumerate_channels (struct ioatdma_device *ioat_dma); +static void ioat_enumerate_channels (struct ioatdma_device *ioat_dma);static int ioat3_dma_self_test (struct ioatdma_device *ioat_dma);static int ioat_dca_enabled =1 ;
@@ -575,7 +575,7 @@ static void ioat_dma_remove(struct ioatdma_device *ioat_dma)* ioat_enumerate_channels - find and initialize the device's channels * @ioat_dma: the ioat dma device to be enumerated */ -static int ioat_enumerate_channels (struct ioatdma_device *ioat_dma) +static void ioat_enumerate_channels (struct ioatdma_device *ioat_dma) {struct ioatdma_chan *ioat_chan;struct device *dev = &ioat_dma->pdev->dev;
@@ -594,7 +594,7 @@ static int ioat_enumerate_channels(struct ioatdma_device *ioat_dma) xfercap_log =readb (ioat_dma->reg_base +IOAT_XFERCAP_OFFSET ); xfercap_log &=0x1f ;/* bits [4:0] valid */ if (xfercap_log ==0 ) -return 0 ; +return ;dev_dbg (dev,"%s: xfercap = %d\n" , __func__,1 << xfercap_log);for (i =0 ; i < dma->chancnt; i++) {
@@ -611,7 +611,6 @@ static int ioat_enumerate_channels(struct ioatdma_device *ioat_dma) } } dma->chancnt = i; -return i; }/**
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 124/220 media: ov5640: fix framerate update
In reply to Greg Kroah-HartmanFrom: Hugues Fruchet <[email protected]>
[ Upstream commit 0929983e49c81c1d413702cd9b83bb06c4a2555c ]
Changing framerate right before streamon had no effect, the new framerate value was taken into account only at next streamon, fix this.
--- drivers/media/i2c/ov5640.c | 7 ++++--- 1 file changed, 4 insertions(+), 3 deletions(-)
drivers/media/i2c/ov5640.c +4 -3
@@ -2572,8 +2572,6 @@ static int ov5640_s_frame_interval(struct v4l2_subdev *sd,if (frame_rate <0 ) frame_rate =OV5640_15_FPS ; - sensor->current_fr = frame_rate; - sensor->frame_interval = fi->interval; mode =ov5640_find_mode (sensor, frame_rate, mode->hact, mode->vact, true);if (!mode) {
@@ -2581,7 +2579,10 @@ static int ov5640_s_frame_interval(struct v4l2_subdev *sd, goto out; } -if (mode != sensor->current_mode) { +if (mode != sensor->current_mode || + frame_rate != sensor->current_fr) { + sensor->current_fr = frame_rate; + sensor->frame_interval = fi->interval; sensor->current_mode = mode; sensor->pending_mode_change = true; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 125/220 media: cec-gpio: select correct Signal Free Time
In reply to Greg Kroah-HartmanFrom: Hans Verkuil <[email protected]>
[ Upstream commit c439d5c1e13dbf66cff53455432f21d4d0536c51 ]
If a receive is in progress or starts before the transmit has a chance, then lower the Signal Free Time of the upcoming transmit to no more than CEC_SIGNAL_FREE_TIME_NEW_INITIATOR.
This is per the specification requirements.
--- drivers/media/cec/cec-pin.c | 20 ++++++++++++++++++++ 1 file changed, 20 insertions(+)
drivers/media/cec/cec-pin.c +20 -0
@@ -936,6 +936,17 @@ static enum hrtimer_restart cec_pin_timer(struct hrtimer *timer)/* Start bit, switch to receive state */ pin->ts = ts; pin->state =CEC_ST_RX_START_BIT_LOW ; +/* +* If a transmit is pending, then that transmit should +* use a signal free time of no more than +* CEC_SIGNAL_FREE_TIME_NEW_INITIATOR since it will +* have a new initiator due to the receive that is now +* starting. +*/ +if (pin->tx_msg.len && pin->tx_signal_free_time > +CEC_SIGNAL_FREE_TIME_NEW_INITIATOR ) + pin->tx_signal_free_time = +CEC_SIGNAL_FREE_TIME_NEW_INITIATOR ;break ; }if (ktime_to_ns (pin->ts) ==0 )
@@ -1158,6 +1169,15 @@ static int cec_pin_adap_transmit(struct cec_adapter *adap, u8 attempts, {struct cec_pin *pin = adap->pin; +/* +* If a receive is in progress, then this transmit should use +* a signal free time of max CEC_SIGNAL_FREE_TIME_NEW_INITIATOR +* since when it starts transmitting it will have a new initiator. +*/ +if (pin->state !=CEC_ST_IDLE && + signal_free_time >CEC_SIGNAL_FREE_TIME_NEW_INITIATOR ) + signal_free_time =CEC_SIGNAL_FREE_TIME_NEW_INITIATOR ; + pin->tx_signal_free_time = signal_free_time; pin->tx_extra_bytes =0 ; pin->tx_msg = *msg;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 126/220 gfs2: slow the deluge of io error messages
In reply to Greg Kroah-HartmanFrom: Bob Peterson <[email protected]>
[ Upstream commit b524abcc01483b2ac093cc6a8a2a7375558d2b64 ]
When an io error is hit, it calls gfs2_io_error_bh_i for every journal buffer it can't write. Since we changed gfs2_io_error_bh_i recently to withdraw later in the cycle, it sends a flood of errors to the console. This patch checks for the file system already being withdrawn, and if so, doesn't send more messages. It doesn't stop the flood of messages, but it slows it down and keeps it more reasonable.
--- fs/gfs2/incore.h | 1 + fs/gfs2/log.c | 7 +++++-- fs/gfs2/util.c | 13 +++++++------ 3 files changed, 13 insertions(+), 8 deletions(-)
fs/gfs2/incore.h +1 -0
@@ -623,6 +623,7 @@ enum {SDF_RORECOVERY =7 ,/* read only recovery */ SDF_SKIP_DLM_UNLOCK =8 ,SDF_FORCE_AIL_FLUSH =9 , + SDF_AIL1_IO_ERROR = 10, }; enum gfs2_freeze_state {
fs/gfs2/log.c +5 -2
@@ -108,7 +108,9 @@ __acquires(&sdp->sd_ail_lock)gfs2_assert (sdp, bd->bd_tr == tr);if (!buffer_busy (bh)) { -if (!buffer_uptodate (bh)) { +if (!buffer_uptodate (bh) && + !test_and_set_bit (SDF_AIL1_IO_ERROR , + &sdp->sd_flags)) {gfs2_io_error_bh (sdp, bh); *withdraw = true; }
@@ -206,7 +208,8 @@ static void gfs2_ail1_empty_one(struct gfs2_sbd *sdp, struct gfs2_trans *tr,gfs2_assert (sdp, bd->bd_tr == tr);if (buffer_busy (bh))continue ; -if (!buffer_uptodate (bh)) { +if (!buffer_uptodate (bh) && + !test_and_set_bit (SDF_AIL1_IO_ERROR , &sdp->sd_flags)) {gfs2_io_error_bh (sdp, bh); *withdraw = true; }
fs/gfs2/util.c +7 -6
@@ -256,12 +256,13 @@ void gfs2_io_error_bh_i(struct gfs2_sbd *sdp, struct buffer_head *bh, const char *function, char *file, unsigned int line, bool withdraw) { - fs_err(sdp, - "fatal: I/O error\n" - " block = %llu\n" -" function = %s, file = %s, line = %u\n" , - (unsigned long long )bh->b_blocknr, - function, file, line); + if (!test_bit(SDF_SHUTDOWN, &sdp->sd_flags)) + fs_err(sdp, + "fatal: I/O error\n" + " block = %llu\n" +" function = %s, file = %s, line = %u\n" , + (unsigned long long )bh->b_blocknr, + function, file, line);if (withdraw)gfs2_lm_withdraw (sdp,NULL ); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 127/220 i2c: omap: use core to detect no zero length quirk
In reply to Greg Kroah-HartmanFrom: Wolfram Sang <[email protected]>
[ Upstream commit f37b2bb6ac3e6ebf855d9d4f05cc6932a8e5b463 ]
And don't reimplement in the driver.
--- drivers/i2c/busses/i2c-omap.c | 8 +++++--- 1 file changed, 5 insertions(+), 3 deletions(-)
drivers/i2c/busses/i2c-omap.c +5 -3
@@ -661,9 +661,6 @@ static int omap_i2c_xfer_msg(struct i2c_adapter *adap,dev_dbg (omap->dev,"addr: 0x%04x, len: %d, flags: 0x%x, stop: %d\n" , msg->addr, msg->len, msg->flags, stop); -if (msg->len ==0 ) -return -EINVAL ; - omap->receiver = !!(msg->flags &I2C_M_RD );omap_i2c_resize_fifo (omap, msg->len, omap->receiver);
@@ -1179,6 +1176,10 @@ static const struct i2c_algorithm omap_i2c_algo = { .functionality = omap_i2c_func, }; +static const struct i2c_adapter_quirks omap_i2c_quirks = { + .flags =I2C_AQ_NO_ZERO_LEN , +}; +#ifdef CONFIG_OF static struct omap_i2c_bus_platform_data omap2420_pdata = { .rev = OMAP_I2C_IP_VERSION_1,
@@ -1453,6 +1454,7 @@ omap_i2c_probe(struct platform_device *pdev) adap->class =I2C_CLASS_DEPRECATED ;strlcpy (adap->name,"OMAP I2C adapter" ,sizeof (adap->name)); adap->algo = &omap_i2c_algo; + adap->quirks = &omap_i2c_quirks; adap->dev.parent = &pdev->dev; adap->dev.of_node = pdev->dev.of_node; adap->bus_recovery_info = &omap_i2c_bus_recovery_info;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 128/220 i2c: qup: use core to detect no zero length quirk
In reply to Greg Kroah-HartmanFrom: Wolfram Sang <[email protected]>
[ Upstream commit de82bb431855580ad659bfed3e858bd9dd12efd0 ]
And don't reimplement in the driver.
--- drivers/i2c/busses/i2c-qup.c | 14 ++++++-------- 1 file changed, 6 insertions(+), 8 deletions(-)
drivers/i2c/busses/i2c-qup.c +6 -8
@@ -1088,11 +1088,6 @@ static int qup_i2c_xfer(struct i2c_adapter *adap,writel (I2C_MINI_CORE |I2C_N_VAL , qup->base +QUP_CONFIG );for (idx =0 ; idx < num; idx++) { -if (msgs[idx].len ==0 ) { - ret = -EINVAL ; - goto out; - } -if (qup_i2c_poll_state_i2c_master (qup)) { ret = -EIO ; goto out;
@@ -1520,9 +1515,6 @@ qup_i2c_determine_mode_v2(struct qup_i2c_dev *qup,/* All i2c_msgs should be transferred using either dma or cpu */ for (idx =0 ; idx < num; idx++) { -if (msgs[idx].len ==0 ) -return -EINVAL ; -if (msgs[idx].flags &I2C_M_RD ) max_rx_len = max_t(unsigned int, max_rx_len, msgs[idx].len);
@@ -1636,9 +1628,14 @@ static const struct i2c_algorithm qup_i2c_algo_v2 = {* which limits the possible read to 256 (QUP_READ_LIMIT) bytes. */ static const struct i2c_adapter_quirks qup_i2c_quirks = { + .flags =I2C_AQ_NO_ZERO_LEN , .max_read_len =QUP_READ_LIMIT , }; +static const struct i2c_adapter_quirks qup_i2c_quirks_v2 = { + .flags =I2C_AQ_NO_ZERO_LEN , +}; +static void qup_i2c_enable_clocks (struct qup_i2c_dev *qup) {clk_prepare_enable (qup->clk);
@@ -1701,6 +1698,7 @@ static int qup_i2c_probe(struct platform_device *pdev) is_qup_v1 = true; }else { qup->adap.algo = &qup_i2c_algo_v2; + qup->adap.quirks = &qup_i2c_quirks_v2; is_qup_v1 = false;if (acpi_match_device (qup_i2c_acpi_match, qup->dev)) goto nodma;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 129/220 i2c: tegra: use core to detect no zero length quirk
In reply to Greg Kroah-HartmanFrom: Wolfram Sang <[email protected]>
[ Upstream commit c96c0f2683804b710531e7b754dcd02b5ded6d4a ]
And don't reimplement in the driver.
--- drivers/i2c/busses/i2c-tegra.c | 4 +--- 1 file changed, 1 insertion(+), 3 deletions(-)
drivers/i2c/busses/i2c-tegra.c +1 -3
@@ -684,9 +684,6 @@ static int tegra_i2c_xfer_msg(struct tegra_i2c_dev *i2c_dev,tegra_i2c_flush_fifos (i2c_dev); -if (msg->len ==0 ) -return -EINVAL ; - i2c_dev->msg_buf = msg->buf; i2c_dev->msg_buf_remaining = msg->len; i2c_dev->msg_err =I2C_ERR_NONE ;
@@ -831,6 +828,7 @@ static const struct i2c_algorithm tegra_i2c_algo = {/* payload size is only 12 bit */ static const struct i2c_adapter_quirks tegra_i2c_quirks = { + .flags =I2C_AQ_NO_ZERO_LEN , .max_read_len =4096 , .max_write_len =4096 -12 , };
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 130/220 i2c: zx2967: use core to detect no zero length quirk
In reply to Greg Kroah-HartmanFrom: Wolfram Sang <[email protected]>
[ Upstream commit e2115ace4196bcd2126446fb874bcfc90cba79be ]
And don't reimplement in the driver.
--- drivers/i2c/busses/i2c-zx2967.c | 8 +++++--- 1 file changed, 5 insertions(+), 3 deletions(-)
drivers/i2c/busses/i2c-zx2967.c +5 -3
@@ -281,9 +281,6 @@ static int zx2967_i2c_xfer_msg(struct zx2967_i2c *i2c,int ret;int i; -if (msg->len ==0 ) -return -EINVAL ; -zx2967_i2c_flush_fifos (i2c); i2c->cur_trans = msg->buf;
@@ -498,6 +495,10 @@ static const struct i2c_algorithm zx2967_i2c_algo = { .functionality = zx2967_i2c_func, }; +static const struct i2c_adapter_quirks zx2967_i2c_quirks = { + .flags =I2C_AQ_NO_ZERO_LEN , +}; +static const struct of_device_id zx2967_i2c_of_match[] = { { .compatible ="zte,zx296718-i2c" , }, { },
@@ -568,6 +569,7 @@ static int zx2967_i2c_probe(struct platform_device *pdev)strlcpy (i2c->adap.name,"zx2967 i2c adapter" ,sizeof (i2c->adap.name)); i2c->adap.algo = &zx2967_i2c_algo; + i2c->adap.quirks = &zx2967_i2c_quirks; i2c->adap.nr = pdev->id; i2c->adap.dev.parent = &pdev->dev; i2c->adap.dev.of_node = pdev->dev.of_node;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 131/220 Input: st1232 - set INPUT_PROP_DIRECT property
In reply to Greg Kroah-HartmanFrom: Martin Kepplinger <[email protected]>
[ Upstream commit 20bbb312079494a406c10c90932e3c80837c9d94 ]
This is how userspace checks for touchscreen devices most reliably.
--- drivers/input/touchscreen/st1232.c | 1 + 1 file changed, 1 insertion(+)
drivers/input/touchscreen/st1232.c +1 -0
@@ -195,6 +195,7 @@ static int st1232_ts_probe(struct i2c_client *client, input_dev->id.bustype =BUS_I2C ; input_dev->dev.parent = &client->dev; +__set_bit (INPUT_PROP_DIRECT , input_dev->propbit);__set_bit (EV_SYN , input_dev->evbit);__set_bit (EV_KEY , input_dev->evbit);__set_bit (EV_ABS , input_dev->evbit);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 132/220 Input: silead - try firmware reload after unsuccessful resume
In reply to Greg Kroah-HartmanFrom: Julian Sax <[email protected]>
[ Upstream commit dde27443211062e841806feaf690674b7c3a599f ]
A certain silead controller (Chip ID: 0x56810000) loses its firmware after suspend, causing the resume to fail. This patch tries to load the firmware, should a resume error occur and retries the resuming.
--- drivers/input/touchscreen/silead.c | 13 +++++++++++++ 1 file changed, 13 insertions(+)
drivers/input/touchscreen/silead.c +13 -0
@@ -558,20 +558,33 @@ static int __maybe_unused silead_ts_suspend(struct device *dev)static int __maybe_unused silead_ts_resume (struct device *dev) {struct i2c_client *client =to_i2c_client (dev); +bool second_try = false;int error, status;silead_ts_set_power (client,SILEAD_POWER_ON ); + retry: error =silead_ts_reset (client);if (error)return error; +if (second_try) { + error =silead_ts_load_fw (client); +if (error) +return error; + } + error =silead_ts_startup (client);if (error)return error; status =silead_ts_get_status (client);if (status !=SILEAD_STATUS_OK ) { +if (!second_try) { + second_try = true; +dev_dbg (dev,"Reloading firmware after unsuccessful resume\n" ); + goto retry; + }dev_err (dev,"Resume error, status: 0x%02x\n" , status);return -ENODEV ; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 133/220 soc: fsl: bman_portals: defer probe after bmans probe
In reply to Greg Kroah-HartmanFrom: Laurentiu Tudor <[email protected]>
[ Upstream commit e0940b34c40e95d1879691d2474d182c57aae0de ]
A crash in bman portal probing could not be triggered (as is the case with qman portals) but it does make calls [1] into the bman driver so lets make sure the bman portal probing happens after bman's.
[1] bman_p_irqsource_add() (in bman) called by:
init_pcfg() called by:
bman_portal_probe()
--- drivers/soc/fsl/qbman/bman_portal.c | 10 +++++++++- 1 file changed, 9 insertions(+), 1 deletion(-)
drivers/soc/fsl/qbman/bman_portal.c +9 -1
@@ -91,7 +91,15 @@ static int bman_portal_probe(struct platform_device *pdev)struct device_node *node = dev->of_node;struct bm_portal_config *pcfg;struct resource *addr_phys[2 ]; -int irq, cpu; +int irq, cpu, err; + + err =bman_is_probed (); +if (!err) +return -EPROBE_DEFER ; +if (err <0 ) { +dev_err (&pdev->dev,"failing probe due to bman probe error\n" ); +return -ENODEV ; + } pcfg =devm_kmalloc (dev,sizeof (*pcfg),GFP_KERNEL );if (!pcfg)
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 134/220 net: hns3: Fix for rx vlan id handle to support Rev 0x21 hardware
In reply to Greg Kroah-HartmanFrom: Jian Shen <[email protected]>
[ Upstream commit 701a6d6ac78c76083ddb7c6581fdbedd95093e11 ]
In revision 0x20, we use vlan id != 0 to check whether a vlan tag has been offloaded, so vlan id 0 is not supported.
In revision 0x21, rx buffer descriptor adds two bits to indicate whether one or more vlan tags have been offloaded, so vlan id 0 is valid now.
This patch seperates the handle for vlan id 0, add vlan id 0 support for revision 0x21.
--- .../net/ethernet/hisilicon/hns3/hns3_enet.c | 30 ++++++++----------- 1 file changed, 13 insertions(+), 17 deletions(-)
drivers/net/ethernet/hisilicon/hns3/hns3_enet.c +13 -17
@@ -2124,18 +2124,18 @@ static void hns3_rx_skb(struct hns3_enet_ring *ring, struct sk_buff *skb)napi_gro_receive (&ring->tqp_vector->napi, skb); } -static u16 hns3_parse_vlan_tag (struct hns3_enet_ring *ring, -struct hns3_desc *desc,u32 l234info) +static bool hns3_parse_vlan_tag (struct hns3_enet_ring *ring, +struct hns3_desc *desc,u32 l234info, +u16 *vlan_tag) {struct pci_dev *pdev = ring->tqp->handle->pdev; -u16 vlan_tag;if (pdev->revision ==0x20 ) { - vlan_tag =le16_to_cpu (desc->rx.ot_vlan_tag); -if (!(vlan_tag &VLAN_VID_MASK )) - vlan_tag =le16_to_cpu (desc->rx.vlan_tag); + *vlan_tag =le16_to_cpu (desc->rx.ot_vlan_tag); +if (!(*vlan_tag &VLAN_VID_MASK )) + *vlan_tag =le16_to_cpu (desc->rx.vlan_tag); -return vlan_tag; +return (*vlan_tag !=0 ); }#define HNS3_STRP_OUTER_VLAN 0x1
@@ -2144,17 +2144,14 @@ static u16 hns3_parse_vlan_tag(struct hns3_enet_ring *ring,switch (hnae3_get_field (l234info,HNS3_RXD_STRP_TAGP_M ,HNS3_RXD_STRP_TAGP_S )) {case HNS3_STRP_OUTER_VLAN : - vlan_tag =le16_to_cpu (desc->rx.ot_vlan_tag); -break ; + *vlan_tag =le16_to_cpu (desc->rx.ot_vlan_tag); +return true;case HNS3_STRP_INNER_VLAN : - vlan_tag =le16_to_cpu (desc->rx.vlan_tag); -break ; + *vlan_tag =le16_to_cpu (desc->rx.vlan_tag); +return true;default : - vlan_tag =0 ; -break ; +return false; } - -return vlan_tag; } static int hns3_handle_rx_bd(struct hns3_enet_ring *ring,
@@ -2256,8 +2253,7 @@ static int hns3_handle_rx_bd(struct hns3_enet_ring *ring,if (netdev->features &NETIF_F_HW_VLAN_CTAG_RX ) {u16 vlan_tag; - vlan_tag =hns3_parse_vlan_tag (ring, desc, l234info); -if (vlan_tag &VLAN_VID_MASK ) +if (hns3_parse_vlan_tag (ring, desc, l234info, &vlan_tag))__vlan_hwaccel_put_tag (skb,htons (ETH_P_8021Q ), vlan_tag);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 135/220 tc-testing: fix build of eBPF programs
In reply to Greg Kroah-HartmanFrom: Davide Caratti <[email protected]>
[ Upstream commit cf5eafbfa586d030f9321cee516b91d089e38280 ]
rely on uAPI headers in the current kernel tree, rather than requiring the correct version installed on the test system. While at it, group all sections in a single binary and test the 'section' parameter.
--- .../testing/selftests/tc-testing/bpf/Makefile | 29 +++++++++++++++++++ .../testing/selftests/tc-testing/bpf/action.c | 23 +++++++++++++++ .../tc-testing/tc-tests/actions/bpf.json | 16 +++++----- .../selftests/tc-testing/tdc_config.py | 4 ++- 4 files changed, 63 insertions(+), 9 deletions(-) create mode 100644 tools/testing/selftests/tc-testing/bpf/Makefile create mode 100644 tools/testing/selftests/tc-testing/bpf/action.c
tools/testing/selftests/tc-testing/bpf/Makefile new file +29 -0
@@ -0,0 +1,29 @@ +# SPDX-License-Identifier: GPL-2.0 + +APIDIR := ../../../../include/uapi +TEST_GEN_FILES = action.o + +top_srcdir = ../../../../.. +include ../../lib.mk + +CLANG ?= clang +LLC ?= llc +PROBE := $(shell $(LLC) -march=bpf -mcpu=probe -filetype=null /dev/null 2>&1) + +ifeq ($(PROBE),) + CPU ?= probe +else + CPU ?= generic +endif + +CLANG_SYS_INCLUDES := $(shell $(CLANG) -v -E - </dev/null 2>&1 \ + | sed -n '/<...> search starts here:/,/End of search list./{ s| \(/.*\)|-idirafter \1|p }') + +CLANG_FLAGS = -I. -I$(APIDIR) \ + $(CLANG_SYS_INCLUDES) \ + -Wno-compare-distinct-pointer-types + +$(OUTPUT)/%.o: %.c + $(CLANG) $(CLANG_FLAGS) \ + -O2 -target bpf -emit-llvm -c $< -o - | \ + $(LLC) -march=bpf -mcpu=$(CPU) $(LLC_FLAGS) -filetype=obj -o $@
tools/testing/selftests/tc-testing/bpf/action.c new file +23 -0
@@ -0,0 +1,23 @@ +/* SPDX-License-Identifier: GPL-2.0 +* Copyright (c) 2018 Davide Caratti, Red Hat inc. +* +* This program is free software; you can redistribute it and/or +* modify it under the terms of version 2 of the GNU General Public +* License as published by the Free Software Foundation. +*/ + +#include <linux/bpf.h> +#include <linux/pkt_cls.h> + +__attribute__((section ("action-ok" ),used))int action_ok (struct __sk_buff *s) +{ +return TC_ACT_OK ; +} + +__attribute__((section ("action-ko" ),used))int action_ko (struct __sk_buff *s) +{ + s->data =0x0 ; +return TC_ACT_OK ; +} + +char _license[] __attribute__((section("license"),used)) = "GPL";
tools/testing/selftests/tc-testing/tc-tests/actions/bpf.json +8 -8
@@ -55,7 +55,7 @@ "bpf" ], "setup": [ - "printf '#include <linux/bpf.h>\nchar l[] __attribute__((section(\"license\"),used))=\"GPL\"; __attribute__((section(\"action\"),used)) int m(struct __sk_buff *s) { return 2; }' | clang -O2 -x c -c - -target bpf -o _b.o", + "make -C bpf", [ "$TC action flush action bpf", 0,
@@ -63,14 +63,14 @@ 255 ] ], - "cmdUnderTest": "$TC action add action bpf object-file _b.o index 667", + "cmdUnderTest": "$TC action add action bpf object-file $EBPFDIR/action.o section action-ok index 667", "expExitCode": "0", "verifyCmd": "$TC action get action bpf index 667", - "matchPattern": "action order [0-9]*: bpf _b.o:\\[action\\] id [0-9]* tag 3b185187f1855c4c( jited)? default-action pipe.*index 667 ref", + "matchPattern": "action order [0-9]*: bpf action.o:\\[action-ok\\] id [0-9]* tag [0-9a-f]{16}( jited)? default-action pipe.*index 667 ref", "matchCount": "1", "teardown": [ "$TC action flush action bpf", - "rm -f _b.o" + "make -C bpf clean" ] }, {
@@ -81,7 +81,7 @@ "bpf" ], "setup": [ - "printf '#include <linux/bpf.h>\nchar l[] __attribute__((section(\"license\"),used))=\"GPL\"; __attribute__((section(\"action\"),used)) int m(struct __sk_buff *s) { s->data = 0x0; return 2; }' | clang -O2 -x c -c - -target bpf -o _c.o", + "make -C bpf", [ "$TC action flush action bpf", 0,
@@ -89,10 +89,10 @@ 255 ] ], - "cmdUnderTest": "$TC action add action bpf object-file _c.o index 667", + "cmdUnderTest": "$TC action add action bpf object-file $EBPFDIR/action.o section action-ko index 667", "expExitCode": "255", "verifyCmd": "$TC action get action bpf index 667", - "matchPattern": "action order [0-9]*: bpf _c.o:\\[action\\] id [0-9].*index 667 ref", + "matchPattern": "action order [0-9]*: bpf action.o:\\[action-ko\\] id [0-9].*index 667 ref", "matchCount": "0", "teardown": [ [
@@ -101,7 +101,7 @@ 1, 255 ], - "rm -f _c.o" + "make -C bpf clean" ] }, {
tools/testing/selftests/tc-testing/tdc_config.py +3 -1
@@ -16,7 +16,9 @@ NAMES = { 'DEV2': '', 'BATCH_FILE': './batch.txt', # Name of the namespace to use - 'NS': 'tcut' + 'NS': 'tcut', + # Directory containing eBPF test programs + 'EBPFDIR': './bpf' }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 136/220 remoteproc: Check for NULL firmwares in sysfs interface
In reply to Greg Kroah-HartmanFrom: Suman Anna <[email protected]>
[ Upstream commit faeadbb64094757150a8c2a3175ca418dbdd472c ]
The remoteproc framework provides a sysfs file 'firmware' for modifying the firmware image name from userspace. Add an additional check to ensure NULL firmwares are errored out right away, rather than getting a delayed error while requesting a firmware during the start of a remoteproc later on.
--- drivers/remoteproc/remoteproc_sysfs.c | 5 +++++ 1 file changed, 5 insertions(+)
drivers/remoteproc/remoteproc_sysfs.c +5 -0
@@ -48,6 +48,11 @@ static ssize_t firmware_store(struct device *dev, } len =strcspn (buf,"\n" ); +if (!len) { +dev_err (dev,"can't provide a NULL firmware\n" ); + err = -EINVAL ; + goto out; + } p =kstrndup (buf, len,GFP_KERNEL );if (!p) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 137/220 remoteproc: qcom: q6v5: Fix a race condition on fatal crash
In reply to Greg Kroah-HartmanFrom: Sibi Sankar <[email protected]>
[ Upstream commit d3ae96c0e6b042a883927493351b2af6ee05e92c ]
Currently with GLINK_SSR enabled each fatal crash results in servicing a crash from wdog as well. This is due to a race that occurs in setting the running flag in the shutdown path. Fix this by moving the running flag to the end of fatal interrupt handler.
Crash Logs:
qcom-q6v5-pil 4080000.remoteproc: fatal error without message remoteproc remoteproc0: crash detected in 4080000.remoteproc: type fatal
error
remoteproc remoteproc0: handling crash #1 in 4080000.remoteproc remoteproc remoteproc0: recovering 4080000.remoteproc qcom-q6v5-pil 4080000.remoteproc: watchdog without message remoteproc remoteproc0: crash detected in 4080000.remoteproc: type watchdog remoteproc:glink-edge: intent request timed outqcom_glink_ssr remoteproc:glink-edge.glink_ssr.-1.-1: failed to send
cleanup messageqcom_glink_ssr remoteproc:glink-edge.glink_ssr.-1.-1: timeout waiting
for cleanup done message
qcom-q6v5-pil 4080000.remoteproc: timed out on wait qcom-q6v5-pil 4080000.remoteproc: port failed halt
remoteproc remoteproc0: stopped remote processor 4080000.remoteproc qcom-q6v5-pil 4080000.remoteproc: MBA booted, loading mpss remoteproc remoteproc0: remote processor 4080000.remoteproc is now up remoteproc remoteproc0: handling crash #2 in 4080000.remoteproc remoteproc remoteproc0: recovering 4080000.remoteproc qcom-q6v5-pil 4080000.remoteproc: port failed halt
remoteproc remoteproc0: stopped remote processor 4080000.remoteproc qcom-q6v5-pil 4080000.remoteproc: MBA booted, loading mpss remoteproc remoteproc0: remote processor 4080000.remoteproc is now up
--- drivers/remoteproc/qcom_q6v5.c | 3 +-- 1 file changed, 1 insertion(+), 2 deletions(-)
drivers/remoteproc/qcom_q6v5.c +1 -2
@@ -84,6 +84,7 @@ static irqreturn_t q6v5_fatal_interrupt(int irq, void *data)else dev_err (q6v5->dev,"fatal error without message\n" ); + q6v5->running = false;rproc_report_crash (q6v5->rproc,RPROC_FATAL_ERROR );return IRQ_HANDLED ;
@@ -150,8 +151,6 @@ int qcom_q6v5_request_stop(struct qcom_q6v5 *q6v5) {int ret; - q6v5->running = false; -qcom_smem_state_update_bits (q6v5->state,BIT (q6v5->stop_bit),BIT (q6v5->stop_bit));
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 138/220 kexec: Allocate decrypted control pages for kdump if SME is enabled
In reply to Greg Kroah-HartmanFrom: Lianbo Jiang <[email protected]>
[ Upstream commit 9cf38d5559e813cccdba8b44c82cc46ba48d0896 ]
When SME is enabled in the first kernel, it needs to allocate decrypted pages for kdump because when the kdump kernel boots, these pages need to be accessed decrypted in the initial boot stage, before SME is enabled.
[ bp: clean up text. ]
--- kernel/kexec_core.c | 6 ++++++ 1 file changed, 6 insertions(+)
kernel/kexec_core.c +6 -0
@@ -473,6 +473,10 @@ static struct page *kimage_alloc_crash_control_pages(struct kimage *image, } } +/* Ensure that these pages are decrypted if SME is enabled. */ +if (pages) +arch_kexec_post_alloc_pages (page_address (pages),1 << order,0 ); +return pages; }
@@ -869,6 +873,7 @@ static int kimage_load_crash_segment(struct kimage *image, result = -ENOMEM ; goto out; } +arch_kexec_post_alloc_pages (page_address (page),1 ,0 ); ptr =kmap (page); ptr += maddr & ~PAGE_MASK ; mchunk = min_t(size_t, mbytes,
@@ -886,6 +891,7 @@ static int kimage_load_crash_segment(struct kimage *image, result =copy_from_user (ptr, buf, uchunk);kexec_flush_icache_page (page);kunmap (page); +arch_kexec_pre_free_pages (page_address (page),1 );if (result) { result = -EFAULT ; goto out;
Signature · 9 lines
2.20.1 _______________________________________________ kexec mailing list [email protected] http://lists.infradead.org/mailman/listinfo/kexec
Greg Kroah-Hartman
maintainerPATCH 139/220 x86/olpc: Fix build error with CONFIG_MFD_CS5535=m
In reply to Greg Kroah-HartmanFrom: Borislav Petkov <[email protected]>
[ Upstream commit fa112cf1e8bc693d5a666b1c479a2859c8b6e0f1 ]
When building a 32-bit config which has the above MFD item as module but OLPC_XO1_PM is enabled =y - which is bool, btw - the kernel fails building with:
ld: arch/x86/platform/olpc/olpc-xo1-pm.o: in function `xo1_pm_remove':
/home/boris/kernel/linux/arch/x86/platform/olpc/olpc-xo1-pm.c:159: undefined reference to `mfd_cell_disable'
ld: arch/x86/platform/olpc/olpc-xo1-pm.o: in function `xo1_pm_probe':
/home/boris/kernel/linux/arch/x86/platform/olpc/olpc-xo1-pm.c:133: undefined reference to `mfd_cell_enable'
make: *** [Makefile:1030: vmlinux] Error 1
Force MFD_CS5535 to y if OLPC_XO1_PM is enabled.
--- arch/x86/Kconfig | 3 +-- 1 file changed, 1 insertion(+), 2 deletions(-)
arch/x86/Kconfig +1 -2
@@ -2771,8 +2771,7 @@ config OLPC config OLPC_XO1_PM bool "OLPC XO-1 Power Management" - depends on OLPC && MFD_CS5535 && PM_SLEEP - select MFD_CORE + depends on OLPC && MFD_CS5535=y && PM_SLEEP ---help--- Add support for poweroff and suspend of the OLPC XO-1 laptop.
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 140/220 dmaengine: rcar-dmac: set scatter/gather max segment size
In reply to Greg Kroah-HartmanFrom: Wolfram Sang <[email protected]>
[ Upstream commit 97d49c59e219acac576e16293a6b8cb99302f62f ]
Fix warning when running with CONFIG_DMA_API_DEBUG_SG=y by allocating a device_dma_parameters structure and filling in the max segment size.
--- drivers/dma/sh/rcar-dmac.c | 3 +++ 1 file changed, 3 insertions(+)
drivers/dma/sh/rcar-dmac.c +3 -0
@@ -198,6 +198,7 @@ struct rcar_dmac {struct dma_device engine;struct device *dev;void __iomem *iomem; +struct device_dma_parameters parms;unsigned int n_channels;struct rcar_dmac_chan *channels;
@@ -1814,6 +1815,8 @@ static int rcar_dmac_probe(struct platform_device *pdev) dmac->dev = &pdev->dev;platform_set_drvdata (pdev, dmac); + dmac->dev->dma_parms = &dmac->parms; +dma_set_max_seg_size (dmac->dev,RCAR_DMATCR_MASK );dma_set_mask_and_coherent (dmac->dev,DMA_BIT_MASK (40 )); ret =rcar_dmac_parse_of (&pdev->dev, dmac);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 141/220 crypto: mxs-dcp - Fix SHA null hashes and output length
In reply to Greg Kroah-HartmanFrom: Radu Solea <[email protected]>
[ Upstream commit c709eebaf5c5faa8a0f140355f9cfe67e8f7afb1 ]
DCP writes at least 32 bytes in the output buffer instead of hash length as documented. Add intermediate buffer to prevent write out of bounds.
When requested to produce null hashes DCP fails to produce valid output. Add software workaround to bypass hardware and return valid output.
--- drivers/crypto/mxs-dcp.c | 47 +++++++++++++++++++++++++++++++--------- 1 file changed, 37 insertions(+), 10 deletions(-)
drivers/crypto/mxs-dcp.c +37 -10
@@ -28,9 +28,24 @@#define DCP_MAX_CHANS 4#define DCP_BUF_SZ PAGE_SIZE +#define DCP_SHA_PAY_SZ 64#define DCP_ALIGNMENT 64 +/* +* Null hashes to align with hw behavior on imx6sl and ull +* these are flipped for consistency with hw output +*/ +const uint8_t sha1_null_hash[] = +"\x09\x07\xd8\xaf\x90\x18\x60\x95\xef\xbf" +"\x55\x32\x0d\x4b\x6b\x5e\xee\xa3\x39\xda" ; + +const uint8_t sha256_null_hash[] = +"\x55\xb8\x52\x78\x1b\x99\x95\xa4" +"\x4c\x93\x9b\x64\xe4\x41\xae\x27" +"\x24\xb9\x6f\x99\xc8\xf4\xfb\x9a" +"\x14\x1c\xfc\x98\x42\xc4\xb0\xe3" ; +/* DCP DMA descriptor. */ struct dcp_dma_desc {uint32_t next_cmd_addr;
@@ -48,6 +63,7 @@ struct dcp_coherent_block {uint8_t aes_in_buf[DCP_BUF_SZ ];uint8_t aes_out_buf[DCP_BUF_SZ ];uint8_t sha_in_buf[DCP_BUF_SZ ]; +uint8_t sha_out_buf[DCP_SHA_PAY_SZ ];uint8_t aes_key[2 *AES_KEYSIZE_128 ];
@@ -513,8 +529,6 @@ static int mxs_dcp_run_sha(struct ahash_request *req)struct crypto_ahash *tfm =crypto_ahash_reqtfm (req);struct dcp_async_ctx *actx =crypto_ahash_ctx (tfm);struct dcp_sha_req_ctx *rctx =ahash_request_ctx (req); -struct hash_alg_common *halg =crypto_hash_alg_common (tfm); -struct dcp_dma_desc *desc = &sdcp->coh->desc[actx->chan];dma_addr_t digest_phys =0 ;
@@ -536,10 +550,23 @@ static int mxs_dcp_run_sha(struct ahash_request *req) desc->payload =0 ; desc->status =0 ; +/* +* Align driver with hw behavior when generating null hashes +*/ +if (rctx->init && rctx->fini && desc->size ==0 ) { +struct hash_alg_common *halg =crypto_hash_alg_common (tfm); +const uint8_t *sha_buf = + (actx->alg ==MXS_DCP_CONTROL1_HASH_SELECT_SHA1 ) ? + sha1_null_hash : sha256_null_hash; +memcpy (sdcp->coh->sha_out_buf, sha_buf, halg->digestsize); + ret =0 ; + goto done_run; + } +/* Set HASH_TERM bit for last transfer block. */ if (rctx->fini) { - digest_phys =dma_map_single (sdcp->dev, req->result, - halg->digestsize,DMA_FROM_DEVICE ); + digest_phys =dma_map_single (sdcp->dev, sdcp->coh->sha_out_buf, +DCP_SHA_PAY_SZ ,DMA_FROM_DEVICE ); desc->control0 |=MXS_DCP_CONTROL0_HASH_TERM ; desc->payload = digest_phys; }
@@ -547,9 +574,10 @@ static int mxs_dcp_run_sha(struct ahash_request *req) ret =mxs_dcp_start_dma (actx);if (rctx->fini) -dma_unmap_single (sdcp->dev, digest_phys, halg->digestsize, +dma_unmap_single (sdcp->dev, digest_phys,DCP_SHA_PAY_SZ ,DMA_FROM_DEVICE ); +done_run:dma_unmap_single (sdcp->dev, buf_phys,DCP_BUF_SZ ,DMA_TO_DEVICE );return ret;
@@ -567,6 +595,7 @@ static int dcp_sha_req_to_buf(struct crypto_async_request *arq)const int nents =sg_nents (req->src);uint8_t *in_buf = sdcp->coh->sha_in_buf; +uint8_t *out_buf = sdcp->coh->sha_out_buf;uint8_t *src_buf;
@@ -621,11 +650,9 @@ static int dcp_sha_req_to_buf(struct crypto_async_request *arq) actx->fill =0 ; -/* For some reason, the result is flipped. */ -for (i =0 ; i < halg->digestsize /2 ; i++) { -swap (req->result[i], - req->result[halg->digestsize - i -1 ]); - } +/* For some reason the result is flipped */ +for (i =0 ; i < halg->digestsize; i++) + req->result[i] = out_buf[halg->digestsize - i -1 ]; }return 0 ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 142/220 crypto: mxs-dcp - Fix AES issues
In reply to Greg Kroah-HartmanFrom: Radu Solea <[email protected]>
[ Upstream commit fadd7a6e616b89c7f4f7bfa7b824f290bab32c3c ]
The DCP driver does not obey cryptlen, when doing android CTS this results in passing to hardware input stream lengths which are not multiple of block size.
Add a check to prevent future erroneous stream lengths from reaching the hardware and adjust the scatterlist walking code to obey cryptlen.
Also properly copy-out the IV for chaining.
--- drivers/crypto/mxs-dcp.c | 33 +++++++++++++++++++++++++++++++-- 1 file changed, 31 insertions(+), 2 deletions(-)
drivers/crypto/mxs-dcp.c +31 -2
@@ -225,6 +225,12 @@ static int mxs_dcp_run_aes(struct dcp_async_ctx *actx,dma_addr_t dst_phys =dma_map_single (sdcp->dev, sdcp->coh->aes_out_buf,DCP_BUF_SZ ,DMA_FROM_DEVICE ); +if (actx->fill %AES_BLOCK_SIZE ) { +dev_err (sdcp->dev,"Invalid block size!\n" ); + ret = -EINVAL ; + goto aes_done_run; + } +/* Fill in the DMA descriptor. */ desc->control0 =MXS_DCP_CONTROL0_DECR_SEMAPHORE | MXS_DCP_CONTROL0_INTERRUPT |
@@ -254,6 +260,7 @@ static int mxs_dcp_run_aes(struct dcp_async_ctx *actx, ret =mxs_dcp_start_dma (actx); +aes_done_run:dma_unmap_single (sdcp->dev, key_phys,2 *AES_KEYSIZE_128 ,DMA_TO_DEVICE );dma_unmap_single (sdcp->dev, src_phys,DCP_BUF_SZ ,DMA_TO_DEVICE );
@@ -280,13 +287,15 @@ static int mxs_dcp_aes_block_crypt(struct crypto_async_request *arq)uint8_t *out_tmp, *src_buf, *dst_buf =NULL ;uint32_t dst_off =0 ; +uint32_t last_out_len =0 ;uint8_t *key = sdcp->coh->aes_key;int ret =0 ;int split =0 ; -unsigned int i, len, clen, rem =0 ; +unsigned int i, len, clen, rem =0 , tlen =0 ;int init =0 ; +bool limit_hit = false; actx->fill =0 ;
@@ -305,6 +314,11 @@ static int mxs_dcp_aes_block_crypt(struct crypto_async_request *arq)for_each_sg (req->src, src, nents, i) { src_buf =sg_virt (src); len =sg_dma_len (src); + tlen += len; + limit_hit = tlen > req->nbytes; + +if (limit_hit) + len = req->nbytes - (tlen - len); do { if (actx->fill + len > out_off)
@@ -321,13 +335,15 @@ static int mxs_dcp_aes_block_crypt(struct crypto_async_request *arq)* If we filled the buffer or this is the last SG, * submit the buffer. */ -if (actx->fill == out_off ||sg_is_last (src)) { +if (actx->fill == out_off ||sg_is_last (src) || + limit_hit) { ret =mxs_dcp_run_aes (actx, req, init);if (ret)return ret; init =0 ; out_tmp = out_buf; + last_out_len = actx->fill;while (dst && actx->fill) {if (!split) { dst_buf =sg_virt (dst);
@@ -350,6 +366,19 @@ static int mxs_dcp_aes_block_crypt(struct crypto_async_request *arq) } } }while (len); + +if (limit_hit) +break ; + } + +/* Copy the IV for CBC for chaining */ +if (!rctx->ecb) { +if (rctx->enc) +memcpy (req->info, out_buf+(last_out_len-AES_BLOCK_SIZE ), +AES_BLOCK_SIZE ); +else +memcpy (req->info, in_buf+(last_out_len-AES_BLOCK_SIZE ), +AES_BLOCK_SIZE ); }return ret;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 143/220 xfrm: use correct size to initialise sp->ovec
In reply to Greg Kroah-HartmanFrom: Li RongQing <[email protected]>
[ Upstream commit f1193e915748291fb205a908db33bd3debece6e2 ]
This place should want to initialize array, not a element, so it should be sizeof(array) instead of sizeof(element)
but now this array only has one element, so no error in this condition that XFRM_MAX_OFFLOAD_DEPTH is 1
--- net/xfrm/xfrm_input.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
net/xfrm/xfrm_input.c +1 -1
@@ -131,7 +131,7 @@ struct sec_path *secpath_dup(struct sec_path *src) sp->len =0 ; sp->olen =0 ; -memset (sp->ovec,0 ,sizeof (sp->ovec[XFRM_MAX_OFFLOAD_DEPTH ])); +memset (sp->ovec,0 ,sizeof (sp->ovec));if (src) {int i;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 144/220 ACPI / SBS: Fix rare oops when removing modules
In reply to Greg Kroah-HartmanFrom: Ronald Tschalär <[email protected]>
[ Upstream commit 757c968c442397f1249bb775a7c8c03842e3e0c7 ]
There was a small race when removing the sbshc module where smbus_alarm() had queued acpi_smbus_callback() for deferred execution but it hadn't been run yet, so that when it did run hc had been freed and the module unloaded, resulting in an invalid paging request.
A similar race existed when removing the sbs module with regards to acpi_sbs_callback() (which is called from acpi_smbus_callback()).
We therefore need to ensure no callbacks are pending or executing before the cleanups are done and the modules are removed.
--- drivers/acpi/osl.c | 1 + drivers/acpi/sbshc.c | 2 ++ 2 files changed, 3 insertions(+)
drivers/acpi/osl.c +1 -0
@@ -1132,6 +1132,7 @@ void acpi_os_wait_events_complete(void)flush_workqueue (kacpid_wq);flush_workqueue (kacpi_notify_wq); } +EXPORT_SYMBOL (acpi_os_wait_events_complete);struct acpi_hp_work {struct work_struct work;
drivers/acpi/sbshc.c +2 -0
@@ -196,6 +196,7 @@ int acpi_smbus_unregister_callback(struct acpi_smb_hc *hc) hc->callback =NULL ; hc->context =NULL ;mutex_unlock (&hc->lock); +acpi_os_wait_events_complete ();return 0 ; }
@@ -292,6 +293,7 @@ static int acpi_smbus_hc_remove(struct acpi_device *device) hc =acpi_driver_data (device);acpi_ec_remove_query_handler (hc->ec, hc->query_bit); +acpi_os_wait_events_complete ();kfree (hc); device->driver_data =NULL ;return 0 ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 145/220 iwlwifi: mvm: dont send keys when entering D3
In reply to Greg Kroah-HartmanFrom: Sara Sharon <[email protected]>
[ Upstream commit 8c7fd6a365eb5b2647b2c01918730d0a485b9f85 ]
In the past, we needed to program the keys when entering D3. This was since we replaced the image. However, now that there is a single image, this is no longer needed. Note that RSC is sent separately in a new command. This solves issues with newer devices that support PN offload. Since driver re-sent the keys, the PN got zeroed and the receiver dropped the next packets, until PN caught up again.
--- drivers/net/wireless/intel/iwlwifi/mvm/d3.c | 4 +++- 1 file changed, 3 insertions(+), 1 deletion(-)
drivers/net/wireless/intel/iwlwifi/mvm/d3.c +3 -1
@@ -731,8 +731,10 @@ int iwl_mvm_wowlan_config_key_params(struct iwl_mvm *mvm, {struct iwl_wowlan_kek_kck_material_cmd kek_kck_cmd = {};struct iwl_wowlan_tkip_params_cmd tkip_cmd = {}; +bool unified =fw_has_capa (&mvm->fw->ucode_capa, +IWL_UCODE_TLV_CAPA_CNSLDTD_D3_D0_IMG );struct wowlan_key_data key_data = { - .configure_keys = !d0i3, + .configure_keys = !d0i3 && !unified, .use_rsc_tsc = false, .tkip = &tkip_cmd, .use_tkip = false,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 146/220 xsk: proper AF_XDP socket teardown ordering
In reply to Greg Kroah-HartmanFrom: Björn Töpel <[email protected]>
[ Upstream commit 541d7fdd7694560404c502f64298a90ffe017e6b ]
The AF_XDP socket struct can exist in three different, implicit
states: setup, bound and released. Setup is prior the socket has been bound to a device. Bound is when the socket is active for receive and send. Released is when the process/userspace side of the socket is released, but the sock object is still lingering, e.g. when there is a reference to the socket in an XSKMAP after process termination.
The Rx fast-path code uses the "dev" member of struct xdp_sock to check whether a socket is bound or relased, and the Tx code uses the struct xdp_umem "xsk_list" member in conjunction with "dev" to determine the state of a socket.
However, the transition from bound to released did not tear the socket down in correct order.
On the Rx side "dev" was cleared after synchronize_net() making the synchronization useless. On the Tx side, the internal queues were destroyed prior removing them from the "xsk_list".
This commit corrects the cleanup order, and by doing so xdp_del_sk_umem() can be simplified and one synchronize_net() can be removed.
--- net/xdp/xdp_umem.c | 11 +++-------- net/xdp/xsk.c | 13 ++++++++----- 2 files changed, 11 insertions(+), 13 deletions(-)
net/xdp/xdp_umem.c +3 -8
@@ -32,14 +32,9 @@ void xdp_del_sk_umem(struct xdp_umem *umem, struct xdp_sock *xs) {unsigned long flags; -if (xs->dev) { -spin_lock_irqsave (&umem->xsk_list_lock, flags); -list_del_rcu (&xs->list); -spin_unlock_irqrestore (&umem->xsk_list_lock, flags); - -if (umem->zc) -synchronize_net (); - } +spin_lock_irqsave (&umem->xsk_list_lock, flags); +list_del_rcu (&xs->list); +spin_unlock_irqrestore (&umem->xsk_list_lock, flags); }int xdp_umem_query (struct net_device *dev,u16 queue_id)
net/xdp/xsk.c +8 -5
@@ -343,12 +343,18 @@ static int xsk_release(struct socket *sock)local_bh_enable ();if (xs->dev) { +struct net_device *dev = xs->dev; +/* Wait for driver to stop using the xdp socket. */ -synchronize_net (); -dev_put (xs->dev); +xdp_del_sk_umem (xs->umem, xs); xs->dev =NULL ; +synchronize_net (); +dev_put (dev); } +xskq_destroy (xs->rx); +xskq_destroy (xs->tx); +sock_orphan (sk); sock->sk =NULL ;
@@ -707,9 +713,6 @@ static void xsk_destruct(struct sock *sk)if (!sock_flag (sk,SOCK_DEAD ))return ; -xskq_destroy (xs->rx); -xskq_destroy (xs->tx); -xdp_del_sk_umem (xs->umem, xs);xdp_put_umem (xs->umem);sk_refcnt_debug_dec (sk);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 147/220 x86/fsgsbase/64: Fix ptrace() to read the FS/GS base accurately
In reply to Greg Kroah-HartmanFrom: Andy Lutomirski <[email protected]>
[ Upstream commit 07e1d88adaaeab247b300926f78cc3f950dbeda3 ]
On 64-bit kernels ptrace can read the FS/GS base using the register access APIs (PTRACE_PEEKUSER, etc.) or PTRACE_ARCH_PRCTL.
Make both of these mechanisms return the actual FS/GS base.
This will improve debuggability by providing the correct information to ptracer such as GDB.
[ chang: Rebased and revised patch description. ]
[ mingo: Revised the changelog some more. ]
--- arch/x86/kernel/ptrace.c | 62 +++++++++++++++++++++++++++++++++------- 1 file changed, 52 insertions(+), 10 deletions(-)
arch/x86/kernel/ptrace.c +52 -10
@@ -40,6 +40,7 @@#include <asm/hw_breakpoint.h> #include <asm/traps.h> #include <asm/syscall.h> +#include <asm/mmu_context.h> #include "tls.h"
@@ -343,6 +344,49 @@ static int set_segment_reg(struct task_struct *task,return 0 ; } +static unsigned long task_seg_base (struct task_struct *task, +unsigned short selector) +{ +unsigned short idx = selector >>3 ; +unsigned long base; + +if (likely ((selector &SEGMENT_TI_MASK ) ==0 )) { +if (unlikely (idx >=GDT_ENTRIES )) +return 0 ; + +/* +* There are no user segments in the GDT with nonzero bases +* other than the TLS segments. +*/ +if (idx <GDT_ENTRY_TLS_MIN || idx >GDT_ENTRY_TLS_MAX ) +return 0 ; + + idx -=GDT_ENTRY_TLS_MIN ; + base =get_desc_base (&task->thread.tls_array[idx]); + }else { +#ifdef CONFIG_MODIFY_LDT_SYSCALL +struct ldt_struct *ldt; + +/* +* If performance here mattered, we could protect the LDT +* with RCU. This is a slow path, though, so we can just +* take the mutex. +*/ +mutex_lock (&task->mm->context.lock); + ldt = task->mm->context.ldt; +if (unlikely (idx >= ldt->nr_entries)) + base =0 ; +else + base =get_desc_base (ldt->entries + idx); +mutex_unlock (&task->mm->context.lock); +#else + base =0 ; +#endif + } + +return base; +} +#endif /* CONFIG_X86_32 */ static unsigned long get_flags (struct task_struct *task)
@@ -436,18 +480,16 @@ static unsigned long getreg(struct task_struct *task, unsigned long offset)#ifdef CONFIG_X86_64 case offsetof(struct user_regs_struct , fs_base): { -/* -* XXX: This will not behave as expected if called on -* current or if fsindex != 0. -*/ -return task->thread.fsbase; +if (task->thread.fsindex ==0 ) +return task->thread.fsbase; +else +return task_seg_base (task, task->thread.fsindex); }case offsetof(struct user_regs_struct , gs_base): { -/* -* XXX: This will not behave as expected if called on -* current or if fsindex != 0. -*/ -return task->thread.gsbase; +if (task->thread.gsindex ==0 ) +return task->thread.gsbase; +else +return task_seg_base (task, task->thread.gsindex); }#endif }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 148/220 mmc: renesas_sdhi_internal_dmac: Whitelist r8a774a1
In reply to Greg Kroah-HartmanFrom: Fabrizio Castro <[email protected]>
[ Upstream commit 2e1501a8bdd49eaa0e967c0ad00e9dcd68d0b30f ]
We need r8a774a1 to be whitelisted for SDHI to work on the RZ/G2M, but we don't care about the revision of the SoC, so just whitelist the generic part number.
--- drivers/mmc/host/renesas_sdhi_internal_dmac.c | 1 + 1 file changed, 1 insertion(+)
drivers/mmc/host/renesas_sdhi_internal_dmac.c +1 -0
@@ -298,6 +298,7 @@ static const struct soc_device_attribute gen3_soc_whitelist[] = { { .soc_id = "r8a7796", .revision = "ES1.0", .data = (void *)BIT(SDHI_INTERNAL_DMAC_ONE_RX_ONLY) }, /* generic ones */ + { .soc_id = "r8a774a1" }, { .soc_id = "r8a7795" }, { .soc_id = "r8a7796" }, { .soc_id = "r8a77965" },
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 149/220 mmc: tmio: Fix SCC error detection
In reply to Greg Kroah-HartmanFrom: Masaharu Hayakawa <[email protected]>
[ Upstream commit b85fb0a1c8aeaaa40d08945d51a6656b512173f0 ]
SDR104, HS200 and HS400 need to check for SCC error. If SCC error is detected, retuning is necessary.
--- drivers/mmc/host/tmio_mmc_core.c | 4 ++-- 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/mmc/host/tmio_mmc_core.c +2 -2
@@ -926,8 +926,8 @@ static void tmio_mmc_finish_request(struct tmio_mmc_host *host)if (mrq->cmd->error || (mrq->data && mrq->data->error))tmio_mmc_abort_dma (host); -if (host->check_scc_error) - host->check_scc_error (host); +if (host->check_scc_error && host->check_scc_error (host)) + mrq->cmd->error = -EILSEQ ;/* If SET_BLOCK_COUNT, continue with main command */ if (host->mrq && !mrq->cmd->error) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 150/220 mmc: renesas_sdhi_internal_dmac: set scatter/gather max segment size
In reply to Greg Kroah-HartmanFrom: Niklas Söderlund <[email protected]>
[ Upstream commit 54541815b43f4e49c82628bf28bbb31d86d2f58a ]
Fix warning when running with CONFIG_DMA_API_DEBUG_SG=y by allocating a device_dma_parameters structure and filling in the max segment size. The size used is the result of a discussion with Renesas hardware engineers and unfortunately not found in the datasheet.
renesas_sdhi_internal_dmac ee140000.sd: DMA-API: mapping sg segment longer than device claims to support [len=126976] [max=65536]
[wsa: simplified some logic after validating intended dma_parms life cycle
and added comment]
--- drivers/mmc/host/renesas_sdhi_internal_dmac.c | 8 ++++++++ 1 file changed, 8 insertions(+)
drivers/mmc/host/renesas_sdhi_internal_dmac.c +8 -0
@@ -310,12 +310,20 @@ static const struct soc_device_attribute gen3_soc_whitelist[] = {static int renesas_sdhi_internal_dmac_probe (struct platform_device *pdev) {const struct soc_device_attribute *soc =soc_device_match (gen3_soc_whitelist); +struct device *dev = &pdev->dev;if (!soc)return -ENODEV ; global_flags |= (unsigned long )soc->data; + dev->dma_parms =devm_kzalloc (dev,sizeof (*dev->dma_parms),GFP_KERNEL ); +if (!dev->dma_parms) +return -ENOMEM ; + +/* value is max of SD_SECCNT. Confirmed by HW engineers */ +dma_set_max_seg_size (dev,0xffffffff ); +return renesas_sdhi_probe (pdev, &renesas_sdhi_internal_dmac_dma_ops); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 151/220 atmel_lcdfb: support native-mode display-timings
In reply to Greg Kroah-HartmanFrom: Sam Ravnborg <[email protected]>
[ Upstream commit 60e5e48dba72c6b59a7a9c7686ba320766913368 ]
When a device tree set a display-timing using native-mode then according to the bindings doc this should:
native-mode:
The native mode for the display, in case multiple modes are provided.
When omitted, assume the first node is the native.
The atmel_lcdfb used the last timing subnode and did not respect the timing mode specified with native-mode.
Introduce use of of_get_videomode() which allowed
a nice simplification of the code while also
added support for native-mode.
As a nice side-effect this fixes a memory leak where the data used for timings and the display_np was not freed.
--- drivers/video/fbdev/atmel_lcdfb.c | 43 +++++++------------------------ 1 file changed, 9 insertions(+), 34 deletions(-)
drivers/video/fbdev/atmel_lcdfb.c +9 -34
@@ -22,6 +22,7 @@#include <linux/module.h> #include <linux/of.h> #include <linux/of_device.h> +#include <video/of_videomode.h> #include <video/of_display_timing.h> #include <linux/regulator/consumer.h> #include <video/videomode.h>
@@ -1028,11 +1029,11 @@ static int atmel_lcdfb_of_init(struct atmel_lcdfb_info *sinfo)struct device *dev = &sinfo->pdev->dev;struct device_node *np =dev->of_node;struct device_node *display_np; -struct device_node *timings_np; -struct display_timings *timings;struct atmel_lcdfb_power_ctrl_gpio *og;bool is_gpio_power = false; +struct fb_videomode fb_vm;struct gpio_desc *gpiod; +struct videomode vm;int ret = -ENOENT ;int i;
@@ -1105,44 +1106,18 @@ static int atmel_lcdfb_of_init(struct atmel_lcdfb_info *sinfo) pdata->lcdcon_is_backlight =of_property_read_bool (display_np,"atmel,lcdcon-backlight" ); pdata->lcdcon_pol_negative =of_property_read_bool (display_np,"atmel,lcdcon-backlight-inverted" ); - timings =of_get_display_timings (display_np); -if (!timings) { -dev_err (dev,"failed to get display timings\n" ); - ret = -EINVAL ; + ret =of_get_videomode (display_np, &vm,OF_USE_NATIVE_MODE ); +if (ret) { +dev_err (dev,"failed to get videomode from DT\n" ); goto put_display_node; } - timings_np =of_get_child_by_name (display_np,"display-timings" ); -if (!timings_np) { -dev_err (dev,"failed to find display-timings node\n" ); - ret = -ENODEV ; + ret =fb_videomode_from_videomode (&vm, &fb_vm); +if (ret <0 ) goto put_display_node; - } -for (i =0 ; i <of_get_child_count (timings_np); i++) { -struct videomode vm; -struct fb_videomode fb_vm; - - ret =videomode_from_timings (timings, &vm, i); -if (ret <0 ) - goto put_timings_node; - ret =fb_videomode_from_videomode (&vm, &fb_vm); -if (ret <0 ) - goto put_timings_node; - -fb_add_videomode (&fb_vm, &info->modelist); - } - -/* -* FIXME: Make sure we are not referencing any fields in display_np -* and timings_np and drop our references to them before returning to -* avoid leaking the nodes on probe deferral and driver unbind. -*/ - -return 0 ; +fb_add_videomode (&fb_vm, &info->modelist); -put_timings_node: -of_node_put (timings_np); put_display_node:of_node_put (display_np);return ret;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 152/220 fbdev: sbuslib: use checked version of put_user()
In reply to Greg Kroah-HartmanFrom: Dan Carpenter <[email protected]>
[ Upstream commit d8bad911e5e55e228d59c0606ff7e6b8131ca7bf ]
I'm not sure why the code assumes that only the first put_user() needs an access_ok() check. I have made all the put_user() and get_user() calls checked.
--- drivers/video/fbdev/sbuslib.c | 26 +++++++++++++------------- 1 file changed, 13 insertions(+), 13 deletions(-)
drivers/video/fbdev/sbuslib.c +13 -13
@@ -106,11 +106,11 @@ int sbusfb_ioctl_helper(unsigned long cmd, unsigned long arg,struct fbtype __user *f = (struct fbtype __user *) arg;if (put_user (type, &f->fb_type) || -__put_user (info->var.yres, &f->fb_height) || -__put_user (info->var.xres, &f->fb_width) || -__put_user (fb_depth, &f->fb_depth) || -__put_user (0 , &f->fb_cmsize) || -__put_user (fb_size, &f->fb_cmsize)) +put_user (info->var.yres, &f->fb_height) || +put_user (info->var.xres, &f->fb_width) || +put_user (fb_depth, &f->fb_depth) || +put_user (0 , &f->fb_cmsize) || +put_user (fb_size, &f->fb_cmsize))return -EFAULT ;return 0 ; }
@@ -125,10 +125,10 @@ int sbusfb_ioctl_helper(unsigned long cmd, unsigned long arg,unsigned int index, count, i;if (get_user (index, &c->index) || -__get_user (count, &c->count) || -__get_user (ured, &c->red) || -__get_user (ugreen, &c->green) || -__get_user (ublue, &c->blue)) +get_user (count, &c->count) || +get_user (ured, &c->red) || +get_user (ugreen, &c->green) || +get_user (ublue, &c->blue))return -EFAULT ; cmap.len =1 ;
@@ -165,10 +165,10 @@ int sbusfb_ioctl_helper(unsigned long cmd, unsigned long arg,u8 red, green, blue;if (get_user (index, &c->index) || -__get_user (count, &c->count) || -__get_user (ured, &c->red) || -__get_user (ugreen, &c->green) || -__get_user (ublue, &c->blue)) +get_user (count, &c->count) || +get_user (ured, &c->red) || +get_user (ugreen, &c->green) || +get_user (ublue, &c->blue))return -EFAULT ;if (index + count > cmap->len)
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 153/220 fbdev: sbuslib: integer overflow in sbusfb_ioctl_helper()
In reply to Greg Kroah-HartmanFrom: Dan Carpenter <[email protected]>
[ Upstream commit e5017716adb8aa5c01c52386c1b7470101ffe9c5 ]
The "index + count" addition can overflow. Both come directly from the user. This bug leads to an information leak.
--- drivers/video/fbdev/sbuslib.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/video/fbdev/sbuslib.c +1 -1
@@ -171,7 +171,7 @@ int sbusfb_ioctl_helper(unsigned long cmd, unsigned long arg, get_user(ublue, &c->blue))return -EFAULT ; -if (index + count > cmap->len) +if (index > cmap->len || count > cmap->len - index)return -EINVAL ;for (i =0 ; i < count; i++) {
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 154/220 fbdev: fix broken menu dependencies
In reply to Greg Kroah-HartmanFrom: Randy Dunlap <[email protected]>
[ Upstream commit aae3394ef0ef90cf00a21133357448385f13a5d4 ]
The framebuffer options and devices menu is unintentionally split or broken because some items in it do not depend on FB (including several under omap and mmp).
Fix this by moving FB_CMDLINE, FB_NOTIFY, and FB_CLPS711X_OLD to just before the FB Kconfig symbol definition and by moving the omap, omap2, and mmp menus to last, following FB_SM712.
Also, the FB_VIA dependencies are duplicated by both being inside an "if FB_VIA/endif" block and "depends on FB_VIA", so drop the "depends on FB_VIA" lines since they are redundant.
--- drivers/video/fbdev/Kconfig | 34 ++++++++++++++++------------------ 1 file changed, 16 insertions(+), 18 deletions(-)
drivers/video/fbdev/Kconfig +16 -18
@@ -2,6 +2,18 @@ # fbdev configuration # +config FB_CMDLINE + bool + +config FB_NOTIFY + bool + +config FB_CLPS711X_OLD + tristate + select FB_CFB_FILLRECT + select FB_CFB_COPYAREA + select FB_CFB_IMAGEBLIT + menuconfig FB tristate "Support for frame buffer devices" select FB_CMDLINE
@@ -54,12 +66,6 @@ config FIRMWARE_EDID combination with certain motherboards and monitors are known to suffer from this problem. -config FB_CMDLINE - bool - -config FB_NOTIFY - bool - config FB_DDC tristate depends on FB
@@ -329,12 +335,6 @@ config FB_ACORN hardware found in Acorn RISC PCs and other ARM-based machines. If unsure, say N. -config FB_CLPS711X_OLD - tristate - select FB_CFB_FILLRECT - select FB_CFB_COPYAREA - select FB_CFB_IMAGEBLIT - config FB_CLPS711X tristate "CLPS711X LCD support" depends on FB && (ARCH_CLPS711X || COMPILE_TEST)
@@ -1456,7 +1456,6 @@ if FB_VIA config FB_VIA_DIRECT_PROCFS bool "direct hardware access via procfs (DEPRECATED)(DANGEROUS)" - depends on FB_VIA default n help Allow direct hardware access to some output registers via procfs.
@@ -1466,7 +1465,6 @@ config FB_VIA_DIRECT_PROCFS config FB_VIA_X_COMPATIBILITY bool "X server compatibility" - depends on FB_VIA default n help This option reduces the functionality (power saving, ...) of the
@@ -2308,10 +2306,6 @@ config FB_SIMPLE Configuration re: surface address, size, and format must be provided through device tree, or plain old platform data. -source "drivers/video/fbdev/omap/Kconfig" -source "drivers/video/fbdev/omap2/Kconfig" -source "drivers/video/fbdev/mmp/Kconfig" - config FB_SSD1307 tristate "Solomon SSD1307 framebuffer support" depends on FB && I2C
@@ -2341,3 +2335,7 @@ config FB_SM712 This driver is also available as a module. The module will be called sm712fb. If you want to compile it as a module, say M here and read <file:Documentation/kbuild/modules.txt>. + +source "drivers/video/fbdev/omap/Kconfig" +source "drivers/video/fbdev/omap2/Kconfig" +source "drivers/video/fbdev/mmp/Kconfig"
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 155/220 reset: Fix potential use-after-free in __of_reset_control_get()
In reply to Greg Kroah-HartmanFrom: Geert Uytterhoeven <[email protected]>
[ Upstream commit b790c8ea5593d6dc3580adfad8e117eeb56af874 ]
Calling of_node_put() decreases the reference count of a device tree object, and may free some data.
However, the of_phandle_args structure embedding it is passed to reset_controller_dev.of_xlate() after that, so it may still be accessed.
Move the call to of_node_put() down to fix this.
--- drivers/reset/core.c | 15 ++++++++------- 1 file changed, 8 insertions(+), 7 deletions(-)
drivers/reset/core.c +8 -7
@@ -496,28 +496,29 @@ struct reset_control *__of_reset_control_get(struct device_node *node,break ; } } -of_node_put (args.np);if (!rcdev) { -mutex_unlock (&reset_list_mutex); -return ERR_PTR (-EPROBE_DEFER ); + rstc =ERR_PTR (-EPROBE_DEFER ); + goto out; }if (WARN_ON (args.args_count != rcdev->of_reset_n_cells)) { -mutex_unlock (&reset_list_mutex); -return ERR_PTR (-EINVAL ); + rstc =ERR_PTR (-EINVAL ); + goto out; } rstc_id = rcdev->of_xlate (rcdev, &args);if (rstc_id <0 ) { -mutex_unlock (&reset_list_mutex); -return ERR_PTR (rstc_id); + rstc =ERR_PTR (rstc_id); + goto out; }/* reset_list_mutex also protects the rcdev's reset_control list */ rstc =__reset_control_get_internal (rcdev, rstc_id, shared); +out:mutex_unlock (&reset_list_mutex); +of_node_put (args.np);return rstc; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 156/220 bcache: account size of buckets used in uuid write to ca->meta_sectors_written
In reply to Greg Kroah-HartmanFrom: Shenghui Wang <[email protected]>
[ Upstream commit 7a55948d38eb9b274cbbdd56dc1dd4b96ebfbe04 ]
UUIDs are considered as metadata. __uuid_write should add the number of buckets (in sectors) written to disk to ca->meta_sectors_written. Currently only 1 bucket is used in uuid write.
Steps to test:
1) create a fresh backing device and a fresh cache device separately. The backing device didn't attach to any cache set.
2) cd /sys/block/<cache device>/bcache
cat metadata_written // record the output value
cat bucket_size
3) attach the backing device to cache set
4) cat metadata_written
The output value is almost the same as the value in step 2 before the change.
After the change, the value is bigger about 1 bucket size.
--- drivers/md/bcache/super.c | 5 +++++ 1 file changed, 5 insertions(+)
drivers/md/bcache/super.c +5 -0
@@ -418,6 +418,7 @@ static int __uuid_write(struct cache_set *c) {BKEY_PADDED (key) k;struct closure cl; +struct cache *ca;closure_init_stack (&cl);lockdep_assert_held (&bch_register_lock);
@@ -429,6 +430,10 @@ static int __uuid_write(struct cache_set *c)uuid_io (c,REQ_OP_WRITE ,0 , &k.key, &cl);closure_sync (&cl); +/* Only one bucket used for uuid write */ + ca =PTR_CACHE (c, &k.key,0 ); +atomic_long_add (ca->sb.bucket_size, &ca->meta_sectors_written); +bkey_copy (&c->uuid_bucket, &k.key);bkey_put (c, &k.key);return 0 ;
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 157/220 bcache: recal cached_dev_sectors on detach
In reply to Greg Kroah-HartmanFrom: Shenghui Wang <[email protected]>
[ Upstream commit 46010141da6677b81cc77f9b47f8ac62bd1cbfd3 ]
Recal cached_dev_sectors on cached_dev detached, as recal done on cached_dev attached.
Update the cached_dev_sectors before bcache_device_detach called as bcache_device_detach will set bcache_device->c to NULL.
--- drivers/md/bcache/super.c | 1 + 1 file changed, 1 insertion(+)
drivers/md/bcache/super.c +1 -0
@@ -1009,6 +1009,7 @@ static void cached_dev_detach_finish(struct work_struct *w)bch_write_bdev_super (dc, &cl);closure_sync (&cl); +calc_cached_dev_sectors (dc->disk.c);bcache_device_detach (&dc->disk);list_move (&dc->list, &uncached_devices);
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 158/220 platform/x86: mlx-platform: Properly use mlxplat_mlxcpld_msn201x_items
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 8289c4b6f2e53750de78bd38cecb6bce4d7a988c ]
Clang warns that mlxplat_mlxcpld_msn201x_items is not going to be emitted in the final assembly because it's only used in ARRAY_SIZE right now, which is a compile time evaluation since the array's size is known.
drivers/platform/x86/mlx-platform.c:555:32: warning: variable 'mlxplat_mlxcpld_msn201x_items' is not needed and will not be emitted [-Wunneeded-internal-declaration]
static struct mlxreg_core_item mlxplat_mlxcpld_msn201x_items[] = {
^1 warning generated.
It appears this was a copy and paste mistake from when this item was first added. Use the definition in mlxplat_mlxcpld_msn201x_data so that Clang no longer warns.
--- drivers/platform/x86/mlx-platform.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/platform/x86/mlx-platform.c +1 -1
@@ -575,7 +575,7 @@ static struct mlxreg_core_item mlxplat_mlxcpld_msn201x_items[] = {static struct mlxreg_core_hotplug_platform_data mlxplat_mlxcpld_msn201x_data = { - .items = mlxplat_mlxcpld_msn21xx_items, + .items = mlxplat_mlxcpld_msn201x_items, .counter =ARRAY_SIZE (mlxplat_mlxcpld_msn201x_items), .cell =MLXPLAT_CPLD_LPC_REG_AGGR_OFFSET , .mask =MLXPLAT_CPLD_AGGR_MASK_DEF ,
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 159/220 media: dw9714: Fix error handling in probe function
In reply to Greg Kroah-HartmanFrom: Rajmohan Mani <[email protected]>
[ Upstream commit f9a0b14240a2d0bd196d35e8aac73df6eabd6382 ]
Fixed the case where v4l2_async_unregister_subdev() is called unnecessarily in the error handling path in probe function.
--- drivers/media/i2c/dw9714.c | 3 ++- 1 file changed, 2 insertions(+), 1 deletion(-)
drivers/media/i2c/dw9714.c +2 -1
@@ -169,7 +169,8 @@ static int dw9714_probe(struct i2c_client *client)return 0 ; err_cleanup: -dw9714_subdev_cleanup (dw9714_dev); +v4l2_ctrl_handler_free (&dw9714_dev->ctrls_vcm); +media_entity_cleanup (&dw9714_dev->sd.entity);dev_err (&client->dev,"Probe failed: %d\n" , rval);return rval; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 160/220 media: dw9807-vcm: Fix probe error handling
In reply to Greg Kroah-HartmanFrom: Sakari Ailus <[email protected]>
[ Upstream commit 9e5b5081fa117ae34eca94b63b1cb6d43dc28f10 ]
v4l2_async_unregister_subdev() may not be called without v4l2_async_register_subdev() being called first. Fix this.
--- drivers/media/i2c/dw9807-vcm.c | 3 ++- 1 file changed, 2 insertions(+), 1 deletion(-)
drivers/media/i2c/dw9807-vcm.c +2 -1
@@ -218,7 +218,8 @@ static int dw9807_probe(struct i2c_client *client)return 0 ; err_cleanup: -dw9807_subdev_cleanup (dw9807_dev); +v4l2_ctrl_handler_free (&dw9807_dev->ctrls_vcm); +media_entity_cleanup (&dw9807_dev->sd.entity);return rval; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 161/220 media: cx18: Dont check for address of video_dev
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit eb1ca9a428fdc3f98be4898f6cd8bcb803878619 ]
Clang warns that the address of a pointer will always evaluated as true in a boolean context.
drivers/media/pci/cx18/cx18-driver.c:1255:23: warning: address of 'cx->streams[i].video_dev' will always evaluate to 'true' [-Wpointer-bool-conversion]
if (&cx->streams[i].video_dev)
~~ ~~~~~~~~~~~~~~~^~~~~~~~~1 warning generated.
Check whether v4l2_dev is null, not the address, so that the statement doesn't fire all the time. This check has been present since 2009, introduced by commit 21a278b85d3c ("V4L/DVB (11619): cx18: Simplify the work handler for outgoing mailbox commands")
--- drivers/media/pci/cx18/cx18-driver.c | 2 +- 1 file changed, 1 insertion(+), 1 deletion(-)
drivers/media/pci/cx18/cx18-driver.c +1 -1
@@ -1252,7 +1252,7 @@ static void cx18_cancel_out_work_orders(struct cx18 *cx) {int i;for (i =0 ; i <CX18_MAX_STREAMS ; i++) -if (&cx->streams[i].video_dev) +if (cx->streams[i].video_dev.v4l2_dev)cancel_work_sync (&cx->streams[i].out_work_order); }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 162/220 mtd: spi-nor: cadence-quadspi: Use proper enum for dma_[un]map_single
In reply to Greg Kroah-HartmanFrom: Nathan Chancellor <[email protected]>
[ Upstream commit 900f5e0d8c9edc5dacc57873d22aee2ae699a8e1 ]
Clang warns when one enumerated type is converted implicitly to another.
drivers/mtd/spi-nor/cadence-quadspi.c:962:47: warning: implicit conversion from enumeration type 'enum dma_transfer_direction' to different enumeration type 'enum dma_data_direction' [-Wenum-conversion]
dma_dst = dma_map_single(nor->dev, buf, len, DMA_DEV_TO_MEM);
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~^~~~~~~~~~~~~~~
./include/linux/dma-mapping.h:428:66: note: expanded from macro
'dma_map_single'
~~~~~~~~~~~~~~~~~~~~ ^
drivers/mtd/spi-nor/cadence-quadspi.c:997:43: warning: implicit
conversion from enumeration type 'enum dma_transfer_direction' to
different enumeration type 'enum dma_data_direction' [-Wenum-conversion]
dma_unmap_single(nor->dev, dma_dst, len, DMA_DEV_TO_MEM);
~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~^~~~~~~~~~~~~~~
./include/linux/dma-mapping.h:429:70: note: expanded from macro
'dma_unmap_single'
~~~~~~~~~~~~~~~~~~~~~~ ^2 warnings generated.
Use the proper enums from dma_data_direction to satisfy Clang.
DMA_FROM_DEVICE = DMA_DEV_TO_MEM = 2
--- drivers/mtd/spi-nor/cadence-quadspi.c | 4 ++-- 1 file changed, 2 insertions(+), 2 deletions(-)
drivers/mtd/spi-nor/cadence-quadspi.c +2 -2
@@ -972,7 +972,7 @@ static int cqspi_direct_read_execute(struct spi_nor *nor, u_char *buf,return 0 ; } - dma_dst =dma_map_single (nor->dev, buf, len,DMA_DEV_TO_MEM ); + dma_dst =dma_map_single (nor->dev, buf, len,DMA_FROM_DEVICE );if (dma_mapping_error (nor->dev, dma_dst)) {dev_err (nor->dev,"dma mapping failed\n" );return -ENOMEM ;
@@ -1007,7 +1007,7 @@ static int cqspi_direct_read_execute(struct spi_nor *nor, u_char *buf, } err_unmap: -dma_unmap_single (nor->dev, dma_dst, len,DMA_DEV_TO_MEM ); +dma_unmap_single (nor->dev, dma_dst, len,DMA_FROM_DEVICE );return ret; }
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 163/220 mtd: devices: m25p80: Make sure WRITE_EN is issued before each write
In reply to Greg Kroah-HartmanFrom: Yogesh Gaur <[email protected]>
[ Upstream commit 3baa8ec88c2feb902328e59a4dcf0f0aaab7d2ff ]
Some SPI controllers can't write nor->page_size bytes in a single step because their TX FIFO is too small, but when that happens we should make sure a WRITE_EN command before each write access and READ_SR command after each write access is issued.
The core is already taking care of that, so all we have to do here is return the actual number of bytes that were written during the spi_mem_exec_op() operation.
--- drivers/mtd/devices/m25p80.c | 23 ++++++++--------------- 1 file changed, 8 insertions(+), 15 deletions(-)
drivers/mtd/devices/m25p80.c +8 -15
@@ -90,7 +90,6 @@ static ssize_t m25p80_write(struct spi_nor *nor, loff_t to, size_t len,SPI_MEM_OP_ADDR (nor->addr_width, to,1 ),SPI_MEM_OP_NO_DUMMY , SPI_MEM_OP_DATA_OUT(len, buf, 1)); -size_t remaining = len;int ret;/* get transfer protocols. */
@@ -101,22 +100,16 @@ static ssize_t m25p80_write(struct spi_nor *nor, loff_t to, size_t len,if (nor->program_opcode ==SPINOR_OP_AAI_WP && nor->sst_write_second) op.addr.nbytes =0 ; -while (remaining) { - op.data.nbytes = remaining <UINT_MAX ? remaining :UINT_MAX ; - ret =spi_mem_adjust_op_size (flash->spimem, &op); -if (ret) -return ret; - - ret =spi_mem_exec_op (flash->spimem, &op); -if (ret) -return ret; + ret =spi_mem_adjust_op_size (flash->spimem, &op); +if (ret) +return ret; + op.data.nbytes = len < op.data.nbytes ? len : op.data.nbytes; - op.addr.val += op.data.nbytes; - remaining -= op.data.nbytes; - op.data.buf.out += op.data.nbytes; - } + ret =spi_mem_exec_op (flash->spimem, &op); +if (ret) +return ret; -return len; +return op.data.nbytes; }/*
Signature · 1 line
2.20.1
Greg Kroah-Hartman
maintainerPATCH 164/220 x86/intel_rdt: Introduce utility to obtain CDP peer
In reply to Greg Kroah-HartmanFrom: Reinette Chatre <[email protected]>
[ Upstream commit 521348b011d64cf3febb10b64ba5b472681bef94 ]
Introduce a utility that, when provided with a RDT resource and an instance of this RDT resource (a RDT domain), would return pointers to the RDT resource and RDT domain that share the same hardware. This is specific to the CDP resources that share the same hardware.
For example, if a pointer to the RDT_RESOURCE_L2DATA resource (struct rdt_resource) and a pointer to an instance of this resource (struct rdt_domain) is provided, then it will return a pointer to the RDT_RESOURCE_L2CODE resource as well as the specific instance that shares the same hardware as the provided rdt_domain.
This utility is created in support of the "exclusive" resource group mode where overlap of resource allocation between resource groups need to be avoided. The overlap test need to consider not just the matching resources, but also the resources that share the same hardware.
Temporarily mark it as unused in support of patch testing to avoid compile warnings until it is used.
--- arch/x86/kernel/cpu/intel_rdt_rdtgroup.c | 72 ++++++++++++++++++++++++ 1 file changed, 72 insertions(+)
arch/x86/kernel/cpu/intel_rdt_rdtgroup.c +72 -0
@@ -964,6 +964,78 @@ static int rdtgroup_mode_show(struct kernfs_open_file *of,return 0 ; } +/** +* rdt_cdp_peer_get - Retrieve CDP peer if it exists +* @r: RDT resource to which RDT domain @d belongs +* @d: Cache instance for which a CDP peer is requested +* @r_cdp: RDT resource that shares hardware with @r (RDT resource peer) +* Used to return the result. +* @d_cdp: RDT domain that shares hardware with @d (RDT domain peer) +* Used to return the result. +* +* RDT resources are managed independently and by extension the RDT domains +* (RDT resource instances) are managed independently also. The Code and +* Data Prioritization (CDP) RDT resources, while managed independently, +* could refer to the same underlying hardware. For example, +* RDT_RESOURCE_L2CODE and RDT_RESOURCE_L2DATA both refer to the L2 cache. +* +* When provided with an RDT resource @r and an instance of that RDT +* resource @d rdt_cdp_peer_get() will return if there is a peer RDT +* resource and the exact instance that shares the same hardware. +* +* Return: 0 if a CDP peer was found, <0 on error or if no CDP peer exists. +* If a CDP peer was found, @r_cdp will point to the peer RDT resource +* and @d_cdp will point to the peer RDT domain. +*/ +static int __attribute__((unused))rdt_cdp_peer_get (struct rdt_resource *r, +struct rdt_domain *d, +struct rdt_resource **r_cdp, +struct rdt_domain **d_cdp) +{ +struct rdt_resource *_r_cdp =NULL ; +struct rdt_domain *_d_cdp =NULL ; +int ret =0 ; + +switch (r->rid) { +case RDT_RESOURCE_L3DATA : + _r_cdp = &rdt_resources_all[RDT_RESOURCE_L3CODE ]; +break ; +case RDT_RESOURCE_L3CODE : + _r_cdp = &rdt_resources_all[RDT_RESOURCE_L3DATA ]; +break ; +case RDT_RESOURCE_L2DATA : + _r_cdp = &rdt_resources_all[RDT_RESOURCE_L2CODE ]; +break ; +case RDT_RESOURCE_L2CODE : + _r_cdp = &rdt_resources_all[RDT_RESOURCE_L2DATA ]; +break ; +default : + ret = -ENOENT ; + goto out; + } + +/* +* When a new CPU comes online and CDP is enabled then the new +* RDT domains (if any) associated with both CDP RDT resources +* are added in the same CPU online routine while the +* rdtgroup_mutex is held. It should thus not happen for one +* RDT domain to exist and be associated with its RDT CDP +* resource but there is no RDT domain associated with the +* peer RDT CDP resource. Hence the WARN. +*/ + _d_cdp =rdt_find_domain (_r_cdp, d->id,NULL ); +if (WARN_ON (!_d_cdp)) { + _r_cdp =NULL ; + ret = -EINVAL ; + } + +out: + *r_cdp = _r_cdp; + *d_cdp = _d_cdp; + +return ret; +} +/** * rdtgroup_cbm_overlaps - Does CBM for intended closid overlap with other * @r: Resource to which domain instance @d belongs.
Signature · 1 line
2.20.1