postrouting and mac address
Hi!
I have a router linux and I need to filter packets in postrouting chain using source mac address. But... in postrouting chain, what is source mac address? mac address of effective source of the packet or router interface mac address ?
Thanks in advance,
Fabio
Quoted 8 lines · Fabio Marcone
Hi!
I have a router linux and I need to filter packets in postrouting chain using source mac address. But... in postrouting chain, what is source mac address? mac address of effective source of the packet or router interface mac address ?Thanks in advance,
Fabio
Hi Fabio,
I don't think you can filter packets in postrouting. The only tables available in POSTROUTING are mangle and nat.
To filter packets in a router, I think you have to do it in the FORWARD chain.
see: http://jengelh.medozas.de/images/nf-packet-flow.png
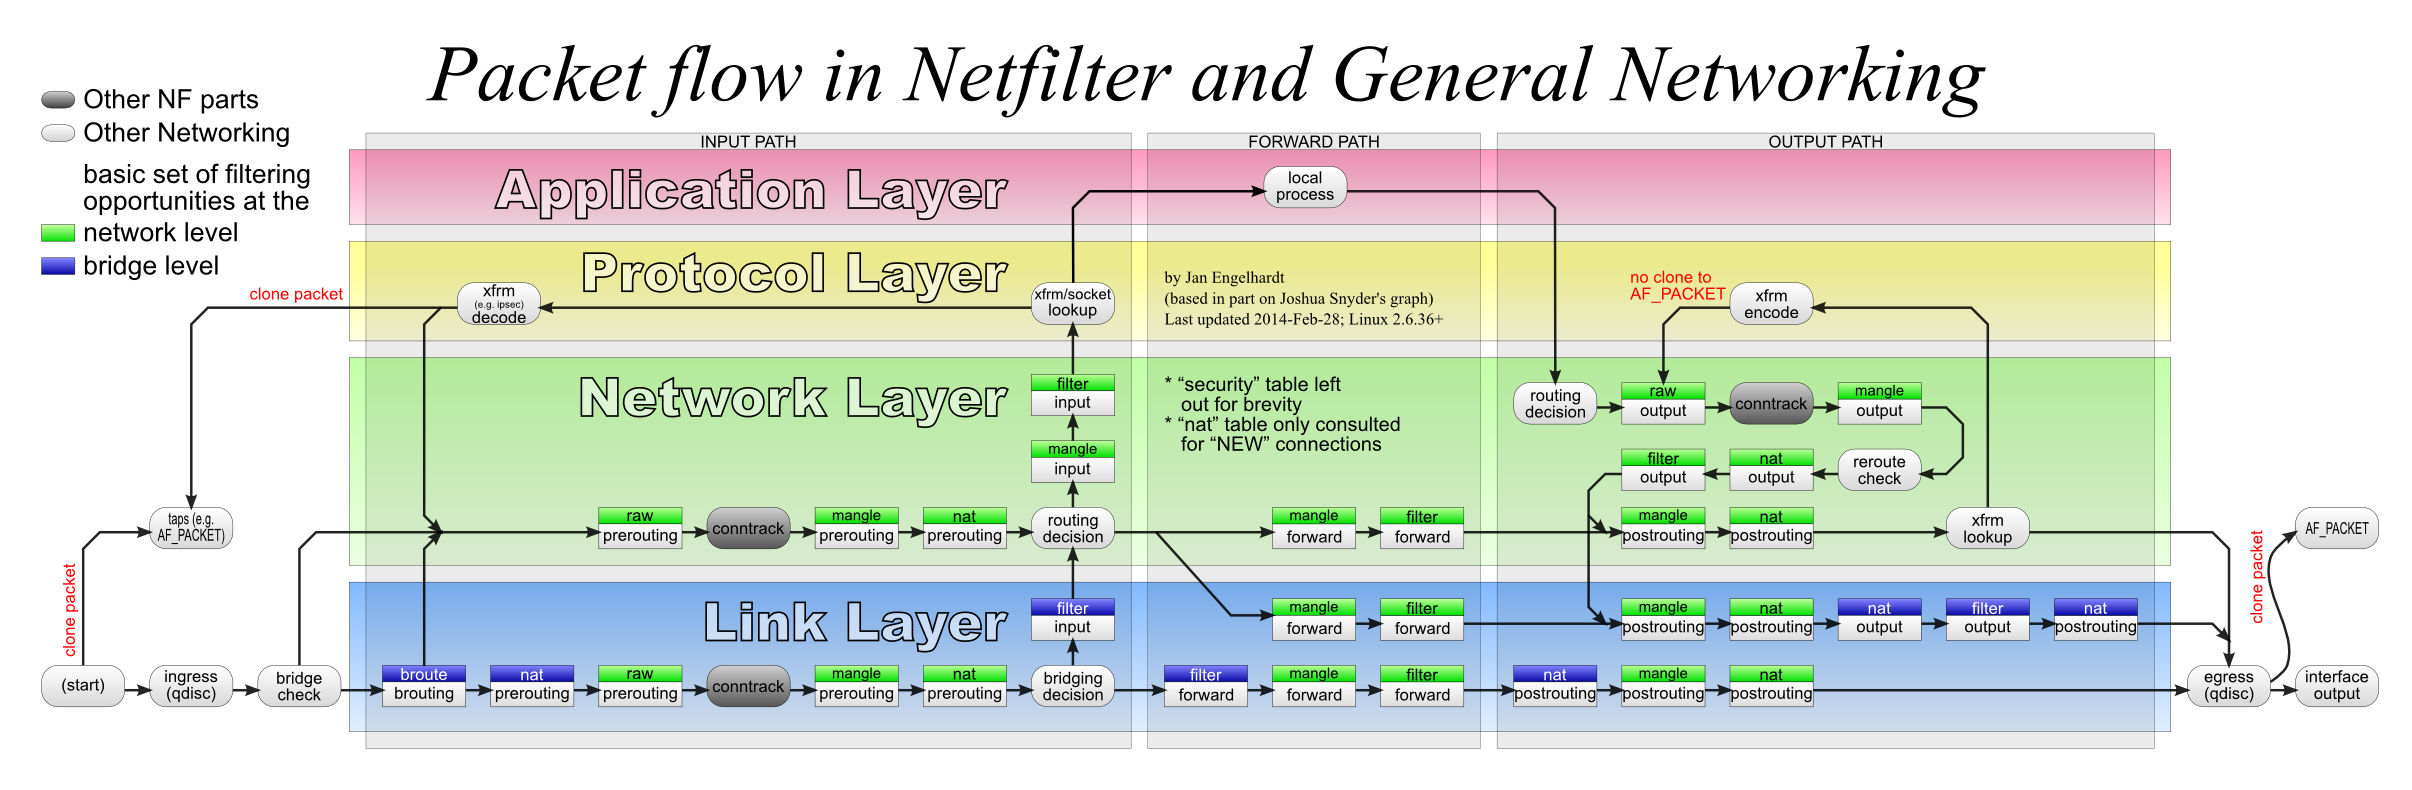
Julien
Signature · 2 lines
julien
http://jve.linuxwall.info/blog
Hi!
there was a misunderstanding: "filter" I mean "recognize". I don't want to drop packets in postrouting, I know it is impossible, but I need to recognize in postrouting packet of a certain source (by mac address, not by ip).
I don't know when packets source mac address is modified by router.
Thanks,
Fabio
Quoted 13 lines
Hi Fabio,
I don't think you can filter packets in postrouting. The only tables available in POSTROUTING are mangle and nat.
To filter packets in a router, I think you have to do it in the FORWARD chain.
see: http://jengelh.medozas.de/images/nf-packet-flow.png
Julien
I tried to add this debug rule:
iptables -t mangle -A POSTROUTING -o eth0 -m mac --mac-source 00:e0:7d:ec:96:1b -j LOG --log-prefix "POST_MAC "
but I got this error:ip_tables: mac match: bad hook_mask 0x10/0x7
so I can't recognize packets by mac source in postrouting chain, isn't it?
Fabio
Quoted 7 lines · Fabio Marcone
Hi!
there was a misunderstanding: "filter" I mean "recognize". I don't want to drop packets in postrouting, I know it is impossible, but I need to recognize in postrouting packet of a certain source (by mac address, not by ip).I don't know when packets source mac address is modified by router.
Thanks,
Fabio
Hello,
Fabio Marcone a écrit :
Quoted 2 lines
Hi!
there was a misunderstanding: "filter" I mean "recognize". I don't want to drop packets in postrouting, I know it is impossible,
It is possible (DROP exists in all tables), but should not be done.
Quoted 1 line
but I need to recognize in postrouting packet of a certain source (by mac address, not by ip).
Can't you MARK packets in earlier chains (PREROUTING or FORWARD) and use the mark in POSTROUTING ?
Quoted 3 lines
It is possible (DROP exists in all tables), but should not be done.
I know that drop is only in INPUT, FORWARD and OUTPUT chain...
Quoted 1 line
Can't you MARK packets in earlier chains (PREROUTING or FORWARD) and use the mark in POSTROUTING ?
perhaps it is the only solution but I would to recognize packets in POSTROUTING to send them in a IMQ virtual interface.
Fabio
Fabio Marcone Ãrta:
Quoted 1 line
perhaps it is the only solution but I would to recognize packets in POSTROUTING to send them in a IMQ virtual interface.
Or maybe you can tell us what you really want...
I mean: What is the purpose of logging by mac in the POSTROUTING chain?
Swifty
Fabio Marcone a écrit :
Quoted 3 lines
Quoted 2 lines
It is possible (DROP exists in all tables), but should not be done.
I know that drop is only in INPUT, FORWARD and OUTPUT chain...
This is not quite correct. DROP is available in all tables and chains. However the "orthodoxy" is to do filtering only in the 'filter' table.
Quoted 3 lines
Quoted 1 line
Can't you MARK packets in earlier chains (PREROUTING or FORWARD) and use the mark in POSTROUTING ?
perhaps it is the only solution but I would to recognize packets in POSTROUTING to send them in a IMQ virtual interface.
What is the problem in using a mark to do this ?